The term "ku delegate" typically refers to the delegation mechanisms, representative structures, or user permissions associated with institutional platforms like the University of Kansas (KU) or specific technical workflows bearing the "KU" prefix. In administrative and enterprise environments, delegation protocols allow authorized users to assign administrative rights, proxy voting capabilities, or system access permissions to other qualified individuals, ensuring operational continuity and adherence to institutional governance standards.
Introduction to Delegation Frameworks
Institutional efficiency depends heavily on clear chains of command, temporary role assignments, and structured permissions management. When an institutional stakeholder—whether a faculty member, department head, or system administrator—needs to step away from active duties or distribute workload, a formal delegation mechanism ensures that workflow bottlenecks do not occur.
Within large educational and enterprise ecosystems, the concept of a delegate spans multiple domains. It can refer to academic representation within faculty senate bodies, proxy voting rights during institutional elections, or digital access delegation within enterprise resource planning (ERP) systems. Understanding how these frameworks operate requires examining the underlying prerequisites, technical setup procedures, governance rules, and common pitfalls associated with delegated authority.
Core Purpose and Scope of Institutional Delegation
Delegation is not merely a convenience; it is a formal administrative process governed by institutional policy. The primary objective is to maintain operational continuity without compromising security, accountability, or compliance standards.
Administrative Continuity
In academic institutions, administrative tasks such as approving requisitions, signing off on grade adjustments, or reviewing travel authorizations must happen within strict windows. If a primary approver is on leave, research sabbatical, or traveling, a designated delegate steps in to execute these tasks. This prevents delays that could affect student progression, vendor payments, or grant compliance.
Academic and Governance Representation
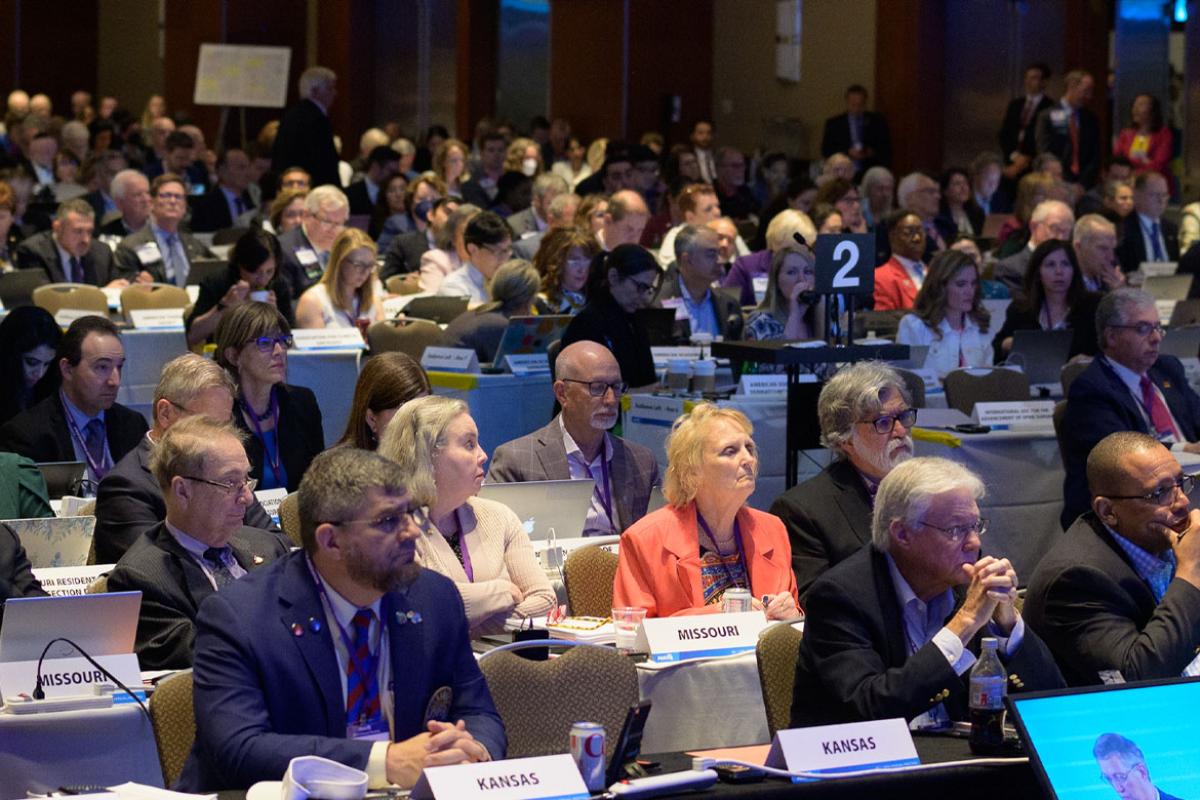
Beyond administrative approvals, delegation frequently appears in governance contexts. Faculty senates and university councils often permit elected representatives to send a proxy delegate to meetings when the primary member cannot attend. These delegates may carry voting privileges depending on the specific bylaws of the governing body, ensuring that every department or constituency maintains a voice in institutional decisions.
Digital System Access
In modern IT infrastructures, system-level delegation allows a user to grant another user specific permissions within a software application. Rather than sharing login credentials—a severe security violation—the system allows structured delegation where actions performed by the delegate are logged under their own credentials while acting on behalf of the principal.
Prerequisites and Eligibility Requirements
Before establishing a delegation relationship within an institutional framework, specific administrative and technical criteria must be met. These requirements safeguard the integrity of institutional data and financial resources.
Role-Based Eligibility
Not every user can act as a delegate. Institutions typically enforce strict role-based access control (RBAC) hierarchies. For financial approvals, a delegate often must hold a comparable or authorized job classification. For academic representation, the delegate must be a recognized member of the specific faculty or department being represented.
Authorization and Documentation
Formal delegation often requires documented approval from a department chair, dean, or system administrator. Casual or verbal agreements are insufficient for system-level or financial delegations. Institutions maintain audit trails that record who authorized the delegation, the exact scope of the transferred permissions, and the expiration date of the arrangement.
Technical Prerequisites
Users must have active, authenticated accounts within the institution's directory services (such as Active Directory or Shibboleth single sign-on) before they can be assigned as delegates. Multi-factor authentication (MFA) is universally required to protect both the principal's account security and the delegate's access level.
Step-by-Step Implementation Workflow
Setting up a delegate involves a precise sequence of actions designed to ensure accountability and minimize security risks. While specific interfaces vary depending on the platform or software module in use, the general workflow remains consistent.
- Audit Current Permissions: The principal must review their current responsibilities and determine precisely which tasks need to be delegated (e.g., travel expense approvals vs. student advising sign-offs).
- Identify a Qualified Delegate: Select an individual within the organization who possesses the necessary training, clearance, and availability to handle the delegated tasks.
- Initiate the Delegation Request: Navigate to the administrative portal, ERP module, or governance settings menu where delegation management is hosted.
- Define Scope and Duration: Specify the exact start date, end date, and specific task categories assigned to the delegate. Open-ended or permanent delegations are heavily restricted or prohibited in financial systems.
- Submit and Verify: Submit the request through the workflow engine. Verify that the designated delegate receives notification and that their dashboard reflects the newly acquired permissions.
| Delegation Type | Typical Duration | Approval Required | Primary Use Case |
|---|---|---|---|
| Financial Approvals | 1 to 90 days | Department Head / Finance Office | Sabbaticals, extended leave, heavy workload management |
| System Access Proxy | Task-specific | IT Administrator | Technical troubleshooting, automated workflow handoffs |
| Governance Proxy | Single meeting/session | Committee Chair / Secretary | Faculty senate votes, council attendance |
| Academic Advising | Academic term | Registrar / Department Lead | Faculty absence, structured student support handoff |
Ongoing Management and Compliance
Once a delegation is active, both the principal and the delegate share responsibilities regarding compliance and security. Institutions audit these relationships regularly to prevent unauthorized access accumulation.
Monitoring and Auditing
Internal audit departments periodically review active delegations to ensure they comply with institutional policies. Principals receive automated reminders regarding active delegations and are expected to revoke access immediately if circumstances change or if the delegate completes their assignment early.
Handling Conflicts of Interest
Delegates must avoid conflicts of interest, particularly in financial and procurement workflows. A delegate cannot approve their own expenses, travel, or requisitions, even if granted broad authority over a principal's account. System-level segregation of duties (SoD) controls typically block such transactions automatically.
Troubleshooting Common Delegation Issues
Users frequently encounter technical or administrative hurdles when establishing or utilizing delegated authority. Understanding these issues helps prevent workflow disruptions.
Permission Mismatches
If a delegate cannot view specific items in their queue, the root cause is often an incomplete role assignment or a mismatch between the principal's department code and the delegate's security profile. Resolving this requires contacting the central IT help desk or the institutional software administrator to verify user group mappings.
Expired Credentials or Access Locks
When a delegate's primary account experiences password expiration or security lockouts, all delegated functions are temporarily suspended. Ensuring that both accounts remain in good standing is essential for uninterrupted operations.
Failure to Receive Notifications
Delegates often miss pending tasks because notification routing defaults to the principal or fails due to outdated email preferences within the enterprise application. Delegates should manually check their assigned task queues within the portal rather than relying solely on email alerts.
Frequently Asked Questions
What is the difference between a permanent transfer of authority and a temporary delegate?
A permanent transfer involves a formal restructuring of job duties and organizational charts, whereas a temporary delegate acts on behalf of a principal for a finite period while retaining their primary role and responsibilities.
Can a delegate further delegate their authority to someone else?
No. Sub-delegation is strictly prohibited across almost all institutional and enterprise systems to maintain a clear audit trail and prevent unauthorized access proliferation.
What happens to pending approvals if a delegation period expires?
Pending approvals that remain unaddressed when a delegation expires typically return to the principal's queue or require reassignment to a new active delegate, depending on the system's workflow configuration.
How are security risks mitigated during delegation?
Institutions mitigate risks by enforcing time limits, requiring multi-factor authentication, restricting delegations to specific task categories, and maintaining comprehensive audit logs of every action performed by the delegate.
Who should I contact if my delegation setup fails?
Users should contact their institutional IT service desk, enterprise system support team, or department administrative manager for assistance with role provisioning and workflow errors.
Conclusion and Next Actions
Effective management of institutional delegation ensures that academic and administrative operations proceed smoothly without compromising security or compliance. Stakeholders seeking to establish a delegate should review their institution's specific governance guidelines, consult with their department administrator, and utilize official administrative portals to initiate time-bound, task-specific delegation requests. Regular audits of active permissions will maintain organizational integrity and protect institutional resources.