A safer lookup refers to the systematic practice of searching for information, verifying data, or executing queries across digital platforms while minimizing cybersecurity risks, privacy exposure, and the threat of malicious redirection. By utilizing trusted verification protocols, encrypted communication channels, and strict authentication mechanisms, users can insulate themselves against phishing vectors, malicious data harvesting, and fraudulent search engine optimization tactics that aim to intercept routine queries.
Understanding the Mechanics of Modern Information Retrieval
The architecture of contemporary search engines and lookup portals is designed for speed and convenience, yet these very design priorities create significant vulnerabilities. When users initiate a lookup—whether for customer support numbers, software downloads, corporate registries, or personal directory records—they often rely on standard, open-ended search mechanisms. These public discovery channels are frequently targeted by threat actors who employ deceptive optimization techniques to manipulate search engine result pages.
By pushing malicious or spoofed domains to the top of result listings, attackers intercept unsuspecting users seeking legitimate organizational interfaces. This phenomenon, often described as malvertising or search engine poisoning, transforms routine information gathering into a high-risk vector for credential theft, malware deployment, and financial fraud.
To counteract these vulnerabilities, implementing a safer lookup framework requires shifting away from passive reliance on top-tier search engine results. Users must adopt an active verification posture, moving from open web queries to direct navigation, authenticated application programming interfaces (APIs), and cryptographically secure repositories. This shift changes the lookup paradigm from trust-upon-receipt to zero-trust verification, ensuring that the data retrieved originates from an authentic source and has not been altered in transit.
- Traditional Search Query (Vulnerable to SEO poisoning, phishing, and malvertising)
- Safer Lookup Framework (Direct navigation, API verification, SSL/TLS validation)
- Authenticated Endpoint (Guaranteed data integrity and source trust)
Core Principles of Secure Digital Investigations
Executing a truly secure and reliable query demands adherence to foundational cybersecurity principles. Whether conducting routine background verifications, corporate due diligence, or technical troubleshooting, adhering to these rules mitigates operational risks.
1. Source Isolation and Sandboxing
When investigating unfamiliar domains, suspicious IP addresses, or unverified file hashes, running queries directly from a primary operating system or personal workstation exposes local networks to compromise. Safer lookup procedures dictate the use of isolated environments, such as dedicated virtual machines, disposable cloud instances, or secure remote browser isolation (RBI) tools. This ensures that any drive-by download, malicious script execution, or exploit kit triggered by the lookup remains quarantined away from production assets.
2. Transport Layer Security and Protocol Verification
Data in transit remains vulnerable to interception and tampering if proper encryption standards are absent. Every lookup action must utilize modern Transport Layer Security (TLS) implementations, specifically TLS 1.3, to guarantee confidentiality and integrity. Users should independently inspect digital certificates, check certificate authorities, and verify that domain names match institutional registries exactly, avoiding typosquatted variations designed to mimic legitimate authorities.
3. Metadata Minimization and Privacy Preservation
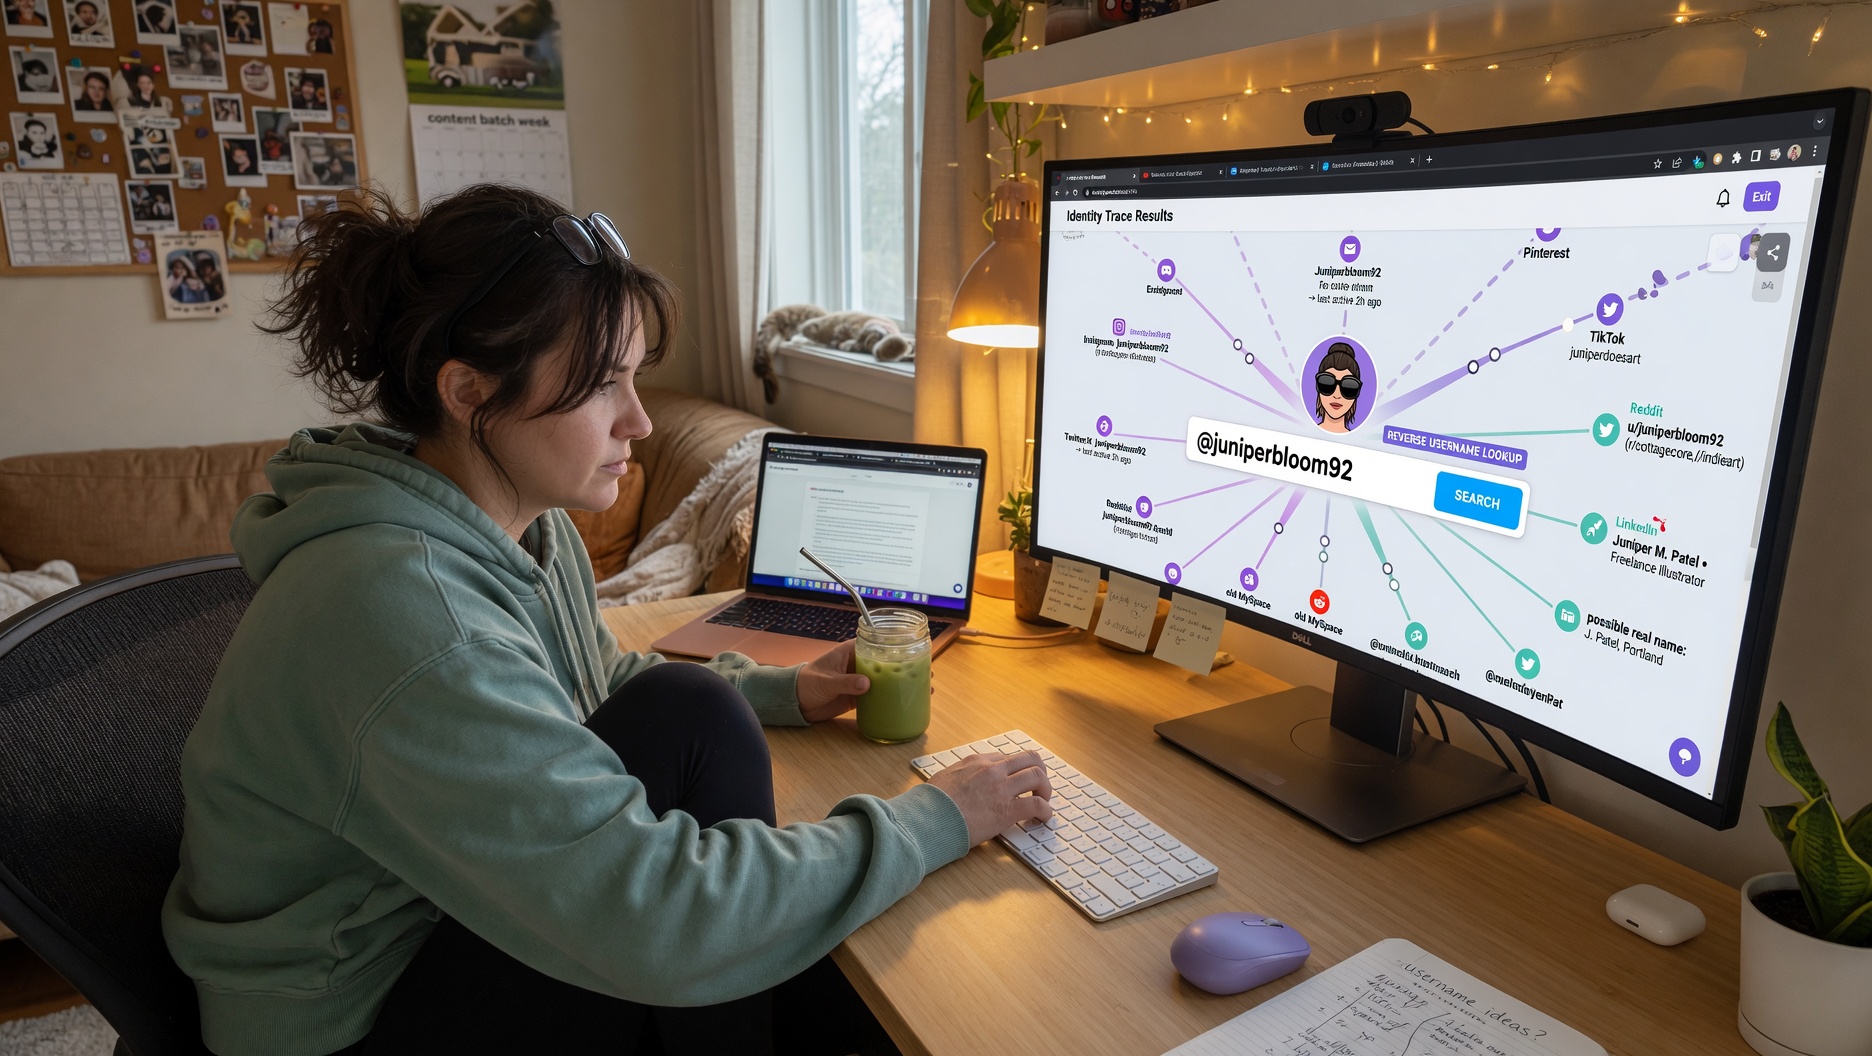
Routine lookups frequently leak sensitive metadata, including user IP addresses, geographic locations, query histories, and device fingerprints. A comprehensive safer lookup strategy incorporates privacy-enhancing technologies such as virtual private networks (VPNs), encrypted DNS resolvers (DNS-over-HTTPS or DNS-over-TLS), and onion routing networks where appropriate. By decoupling the query from the identity of the investigator, organizations protect themselves against targeted reconnaissance and counter-intelligence operations.
Comparative Analysis of Lookup Methodologies
Different lookup scenarios require distinct technological approaches. The table below compares standard public search practices with hardened, secure lookup methodologies across key operational vectors.
| Evaluation Metric | Standard Public Search | Hardened Safer Lookup Framework |
|---|---|---|
| Source Authentication | Relies on algorithmic rankings; vulnerable to spoofing. | Utilizes direct institutional registries, official APIs, and cryptographic hashes. |
| Network Privacy | High exposure of IP, query history, and metadata to ISPs and third parties. | Utilizes encrypted DNS, VPN tunneling, and minimal metadata sharing. |
| Execution Environment | Local browser running standard extensions and scripts. | Sandboxed virtual machines, remote browser isolation, or CLI utilities. |
| Data Integrity | Prone to man-in-the-middle manipulation and malvertising. | Verified via digital signatures, SSL/TLS inspection, and checksum validation. |
| Audit Trail | Fragmented browser caches and untrusted third-party trackers. | Centralized, immutable logging for compliance and forensic review. |
Implementing Safer Lookup Protocols in Enterprise Environments
Organizations must codify secure information retrieval policies to protect internal assets from social engineering and software supply chain attacks. When employees search for documentation, software packages, or external vendor portals, the margin for human error remains high.
Establishing Approved Repositories and Allow-Lists
Rather than allowing unconstrained web searches for software libraries, driver updates, or enterprise tools, organizations should maintain centralized, vetted internal repositories. Developers and IT administrators should execute lookups exclusively within approved package managers, internal artifact repositories, and verified vendor documentation portals configured within enterprise firewalls.
Browser-Level Hardening and Extension Control
Browsers serve as the primary interface for information retrieval, making them prime targets for malicious manipulation. Enterprise administrators must enforce strict extension policies, permitting only pre-approved productivity and security tools. Furthermore, advanced endpoint protection platforms should be integrated to analyze outgoing query patterns, flag typosquatted domains automatically, and block access to known phishing infrastructures identified by threat intelligence feeds.
Practical Troubleshooting and Common Pitfalls
Even with robust technical safeguards in place, users frequently encounter hurdles or commit avoidable errors during secure lookup operations. Recognizing these failure points is vital for maintaining operational resilience.
- Over-Reliance on Automated Safety Ratings: Many users trust third-party reputation scores implicitly. However, threat actors regularly compromise or manipulate reputation databases, or spin up fresh domains that lack historical negative flags. Always cross-reference reputation scores with direct source verification.
- Ignoring Certificate Warnings: Bypassing SSL/TLS certificate warnings because a site "looks legitimate" is a primary vector for credential harvesting. Any security exception should be treated as a hard stop.
- Failing to Verify File Checksums: When a lookup results in downloading a utility, patch, or document, failing to verify cryptographic checksums (SHA-256) against the author's published values leaves the system vulnerable to binary tampering.
- Neglecting Session Hygiene: Leaving search histories, cached credentials, and temporary session tokens exposed on shared or semi-public lookup terminals compromises the integrity of subsequent investigations. Always clear local session artifacts upon task completion.
Frequently Asked Questions
What makes a standard web search unsafe for sensitive lookups?
Standard search engines prioritize algorithmic relevance and commercial advertising placement over absolute security. Threat actors exploit this by purchasing targeted ads or manipulating search rankings to display lookalike domains that mimic trusted banks, government agencies, or software vendors, leading users straight into credential-harvesting traps.
How do virtual machines protect against malicious lookup attempts?
Virtual machines isolate the host operating system from the browser environment. If a malicious link encountered during a lookup triggers a zero-day browser exploit or attempts a drive-by download, the payload remains trapped inside the guest operating system container, preventing infection of the local network or primary workstation.
Why is SSL/TLS inspection insufficient on its own for secure lookups?
While SSL/TLS encryption ensures that data cannot be intercepted in transit between the user and the server, it does not verify the trustworthiness of the server operator. An attacker can easily obtain a valid cryptographic certificate for a malicious typosquatted domain, making the connection secure yet entirely fraudulent.
How can organizations prevent employees from falling for search engine poisoning?
Organizations can mitigate this risk by deploying enterprise-grade DNS filtering, enforcing direct navigation bookmarks for critical internal and external portals, implementing browser isolation technology, and conducting regular security awareness training focused specifically on malvertising identification.
Strategic Recommendations for Ongoing Information Security
Executing secure and reliable data retrievals is an ongoing discipline rather than a one-time configuration task. To maintain high security standards, organizations and individual users should systematically audit their lookup workflows, transition away from open-ended public search discovery for critical operations, and integrate automated threat intelligence feeds directly into their browsing and navigation stacks. By maintaining strict environment separation, verifying cryptographic signatures, and refusing to rely solely on search engine rankings, users can navigate the digital landscape with confidence and structural resilience.