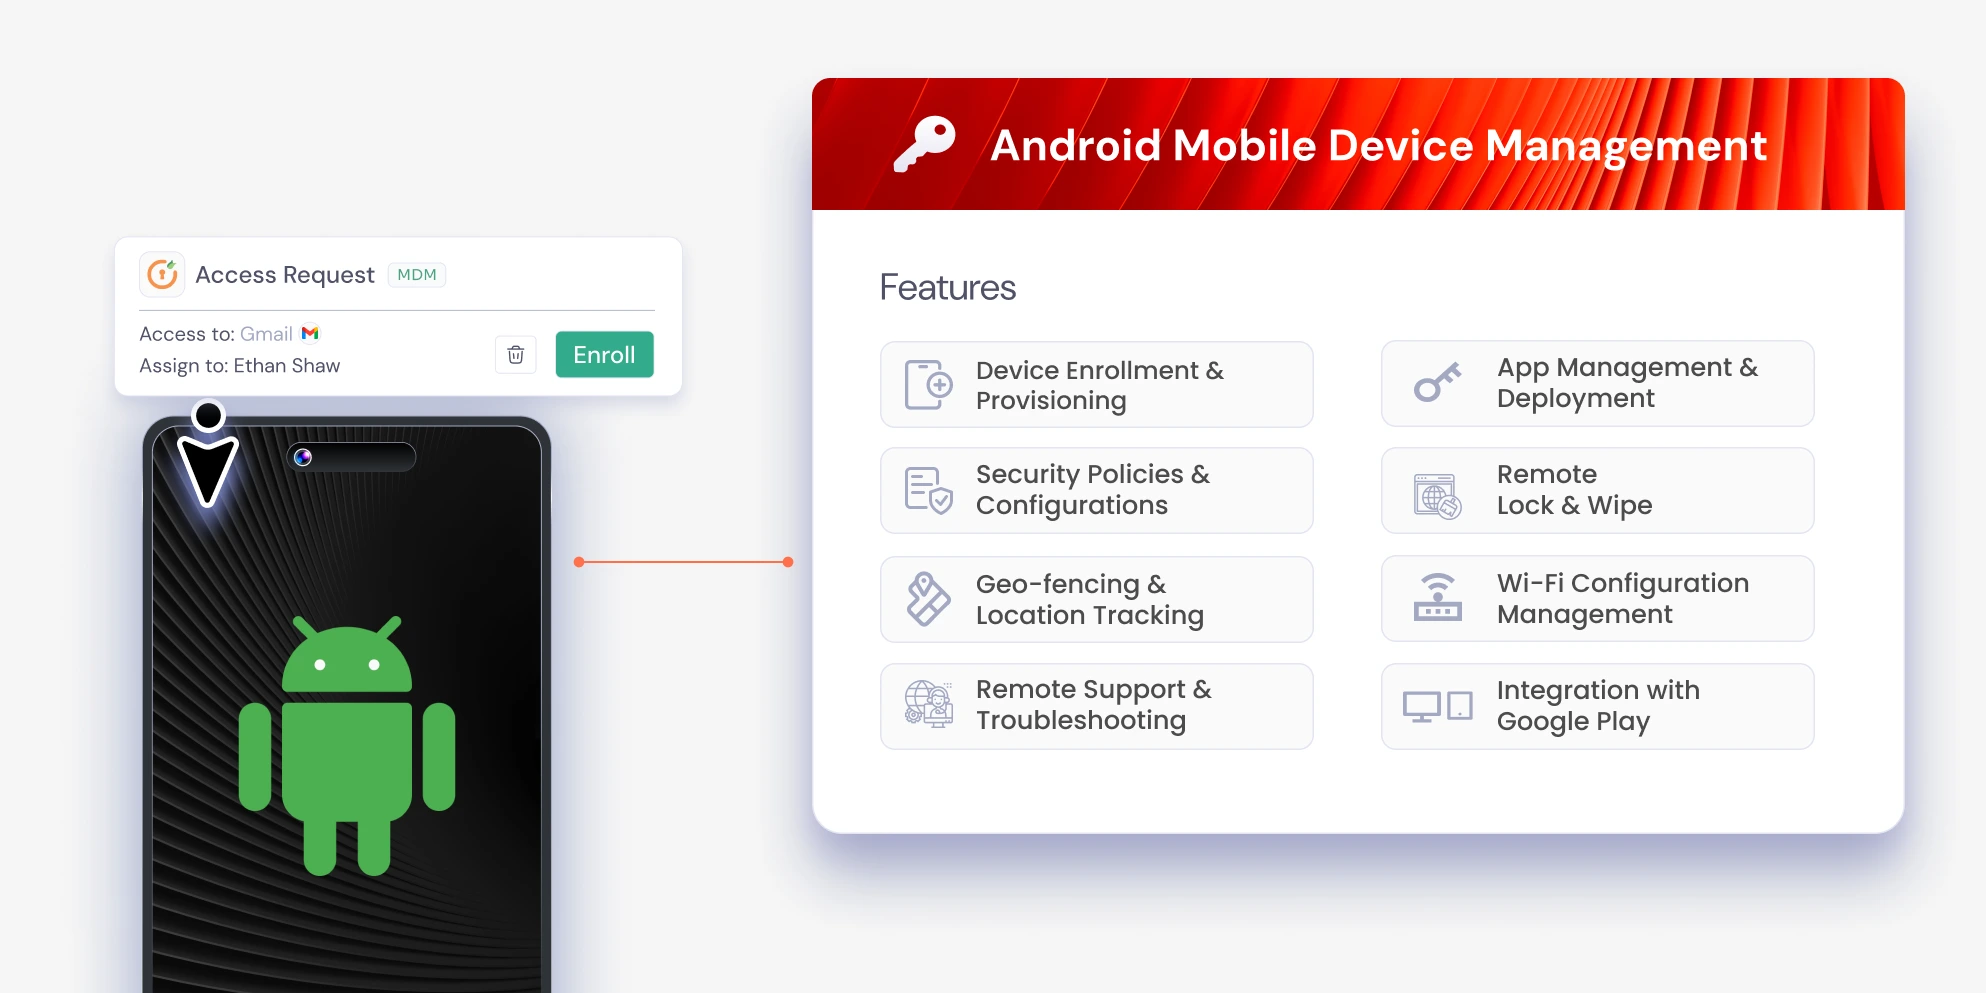
Android Mobile Device Management (MDM) refers to the administration, monitoring, securing, and support of corporate-owned or employee-owned Android smartphones and tablets from a centralized cloud or on-premises console. As organizations increasingly depend on mobile technology for daily operations, Android MDM provides IT administrators with the necessary control mechanisms to enforce security policies, distribute applications, and protect sensitive corporate data across a diverse ecosystem of hardware manufacturers.
Understanding Android MDM and Enterprise Mobility
The modern workplace relies heavily on mobile technology, transforming how employees access internal networks, customer data, and productivity applications. However, permitting unrestricted access to corporate resources via mobile endpoints introduces severe cybersecurity vulnerabilities. Devices can be lost, stolen, infected with malware, or misconfigured by end users, potentially exposing confidential information to unauthorized parties. Android MDM addresses these risks by acting as the foundational layer for Enterprise Mobility Management (EMM) and Unified Endpoint Management (UEM).
At its technological core, Android MDM operates by leveraging management APIs built directly into the Android operating system by Google. These APIs allow an authorized management server to interact securely with the device's firmware and operating system layers. Through a centralized dashboard, IT administrators can configure Wi-Fi profiles, enforce complex screen lock requirements, restrict hardware features like the camera or Bluetooth, and push configuration updates over the air without requiring physical access to the hardware.
Implementing an MDM framework also helps organizations comply with stringent regulatory frameworks, such as the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), and the Payment Card Industry Data Security Standard (PCI DSS). By maintaining strict oversight over how endpoints handle, process, and store sensitive data, businesses minimize the likelihood of accidental data leakage or malicious data exfiltration.
Evolution of Android Management Frameworks
To appreciate modern Android MDM, one must understand how device administration has evolved over the past decade. In the early days of Android enterprise adoption, management relied heavily on legacy Device Administrator APIs. These legacy APIs granted broad permissions to administrative applications, but they lacked granular controls, suffered from fragmentation across different device manufacturers, and posed significant security and privacy concerns because administrators could view personal data alongside corporate files.
Recognizing the need for a more secure, streamlined, and privacy-conscious approach, Google introduced Android Enterprise. This modern management framework fundamentally changed how corporate data and personal usage coexist on mobile endpoints. Android Enterprise shifted the paradigm from managing the entire device as a monolithic entity to managing specific profiles and accounts within the operating system.
Android Enterprise introduced distinct provisioning modes that cater to different organizational deployment scenarios:
- Fully Managed Device (Corporate-Owned): The organization owns the device and maintains complete control over all applications, settings, and security policies, ideal for dedicated work devices.
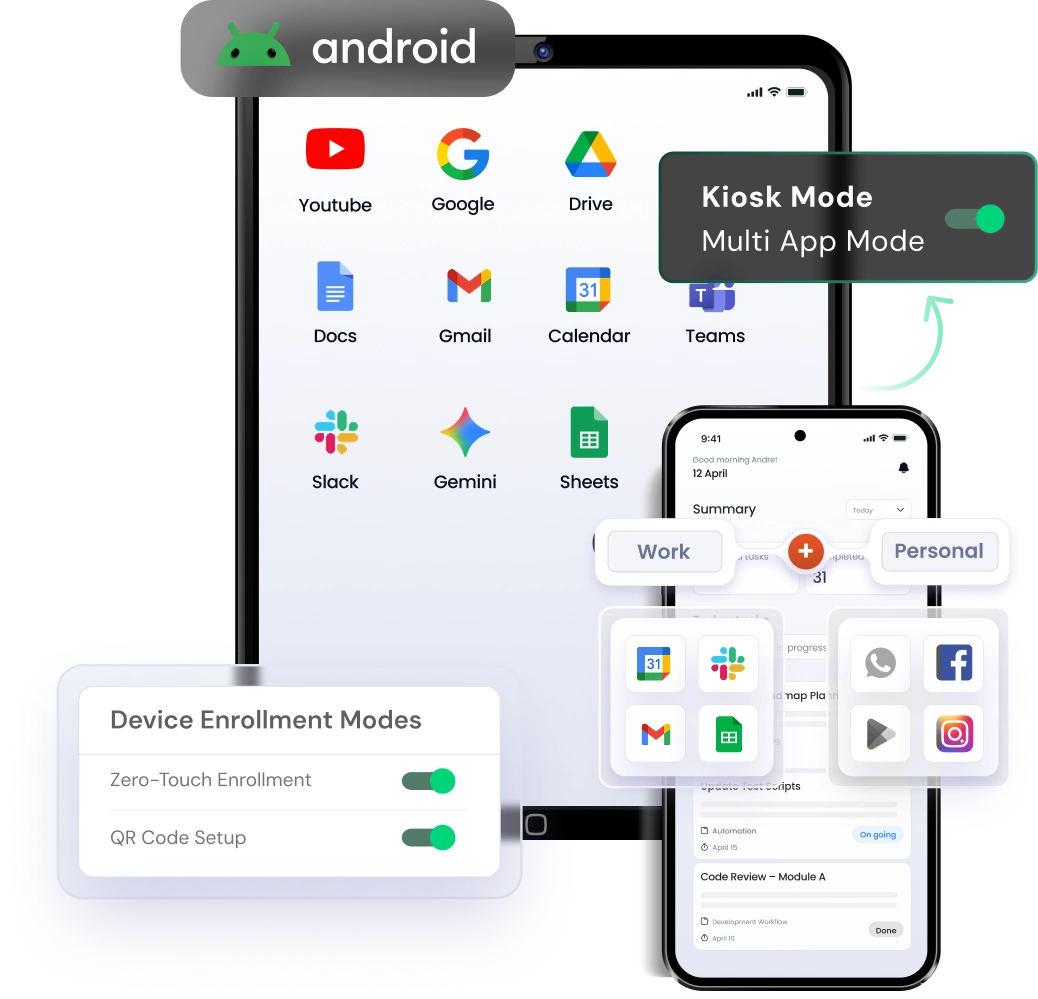
- Work Profile (Bring Your Own Device - BYOD): A secure, isolated container is created on the employee's personal device. Corporate apps and data live entirely within this work profile, while personal apps remain completely private and inaccessible to IT administrators.
- Dedicated Device (Corporate-Owned, Single-Use - COSU): Configured for a specific operational task, such as a retail point-of-sale terminal, a kiosk, or a warehouse inventory scanner, locking the device down to a single application or a restricted set of apps.
- Corporate-Owned with Work Profile: Combines elements of both worlds, giving the enterprise full control over the device while providing a separate work profile for organizational tasks, suitable for knowledge workers who need corporate-issued hardware.
Core Features and Capabilities of Android MDM Solutions
An enterprise-grade Android MDM solution offers a comprehensive suite of tools designed to manage the complete lifecycle of a mobile device, from initial unboxing to final retirement and data wiping.
Over-The-Air Provisioning and Enrollment
Deploying hundreds or thousands of mobile devices manually is entirely impractical. Modern Android MDM platforms support automated enrollment methods that streamline deployment. Using Android Zero-Touch Enrollment or Knox Mobile Enrollment (for Samsung devices), administrators can configure devices so that they automatically download and apply the appropriate MDM policies the moment the device connects to the internet during initial setup. Alternatively, administrators can utilize QR code provisioning or Near Field Communication (NFC) bump provisioning to enroll devices rapidly.
Application Management and Distribution
Distributing, updating, and removing applications across a fleet of endpoints is a primary function of any MDM platform. Administrators can connect their MDM console to Google Play to silently push required productivity tools, line-of-business (LOB) applications, and security utilities directly to managed devices or work profiles without requiring user intervention. Furthermore, IT teams can blacklist unauthorized applications, prevent side-loading of APK files from unknown sources, and enforce mandatory app updates to patch security vulnerabilities promptly.
Security Policies and Compliance Enforcement
Enforcing security baselines protects the enterprise perimeter. MDM administrators can mandate complex password policies, enforce screen timeout durations, disable screen captures within work apps, and restrict the use of removable storage media like micro-SD cards. If a device fails to comply with established security rules—such as being rooted, operating an outdated OS version, or losing connection to the management server for an extended period—the MDM system can automatically trigger remediation actions, such as revoking network access or executing a selective or full factory reset.
Remote Troubleshooting and Geolocation
When mobile users encounter technical difficulties, downtime directly impacts productivity. MDM solutions often include remote support tools that allow IT technicians to view device screens, pull diagnostic logs, and push network configuration fixes remotely. Additionally, location tracking capabilities enable organizations to locate lost or stolen hardware, though these features are often subject to strict privacy controls and employee notification policies, particularly in BYOD environments.
| Management Mode | Primary Use Case | Data Privacy Level | IT Control Scope |
|---|---|---|---|
| Work Profile (BYOD) | Employee-owned smartphones used for work | High (Personal data isolated) | Limited to work profile apps and data |
| Fully Managed | Corporate-owned knowledge worker phones | Low (Entire device managed) | Comprehensive device and app control |
| Dedicated Device (Kiosk) | Point-of-sale, digital signage, scanners | N/A (Single-purpose hardware) | Extreme lockdown, single app focus |
| Corporate-Owned with Work Profile | Corporate hardware with personal allowance | Moderate (Clear partition) | Full device visibility with private container |
Architectural Prerequisites for Deployment
Successfully implementing an Android MDM solution requires careful preparation across network infrastructure, identity management systems, and administrative policies. Skipping foundational steps often results in adoption friction, security gaps, and administrative bottlenecks.
Identity Provider (IdP) Integration
Modern MDM solutions rarely operate in an isolated vacuum. They integrate tightly with enterprise directory services and Identity Providers such as Microsoft Entra ID (formerly Azure AD), Okta, Google Workspace, or Ping Identity. Integrating with an IdP ensures that device enrollment is tied to verified corporate identities, enabling seamless Single Sign-On (SSO) experiences and automated user lifecycle management. When an employee joins or leaves the organization, their associated mobile access rights are automatically provisioned or revoked.
Network and Firewall Configuration
MDM servers communicate continuously with managed endpoints to transmit policy updates, collect telemetry data, and deliver push notifications via services like Google Cloud Messaging (GCM) or Firebase Cloud Messaging (FCM). Consequently, corporate firewalls and proxy servers must be configured to allow outbound HTTPS traffic (typically over port 443) to specific vendor endpoints and Google infrastructure services. Restrictive network policies that block these communication channels will cause devices to fall out of compliance and miss critical security updates.
Enterprise Mobility Strategy and Policy Drafting
Before deploying any software, stakeholders from IT, legal, human resources, and information security must collaborate to draft a comprehensive Mobile Device Acceptable Use Policy (AUP). This policy should clearly articulate what constitutes acceptable usage on corporate and personal devices, outline the scope of IT monitoring (especially regarding privacy in BYOD scenarios), detail the steps taken during device loss or theft, and specify user responsibilities regarding software updates and password hygiene.
Step-by-Step Implementation Workflow
Deploying an Android MDM environment involves a structured sequence of administrative tasks designed to ensure system stability and security before rolling devices out to end users.
Step 1: Selecting and Subscribing to an MDM Provider
Organizations must evaluate and select an MDM platform that aligns with their operational scale, budget, and technical requirements. Popular enterprise options include Microsoft Intune, VMware Workspace ONE, MobileIron (Ivanti), SOTI MobiControl, and Google Endpoint Management. Once selected, administrators establish the core administrative tenant and configure global settings.
Step 2: Establishing Enterprise Google Play Connection
Because Android endpoints rely heavily on Google services for app distribution and management, the MDM console must be linked to an Managed Google Play account (historically known as Android for Work). This connection establishes a secure bridge between the enterprise management server and Google's application ecosystem, allowing the push deployment of public applications and private internal APKs without requiring individual Google accounts on every device.
Step 3: Configuring Enrollment Rules and Group Policies
Administrators create logical groups within the MDM console based on department, geographical location, or security clearance. Policies are then drafted for each group. For instance, a finance department group might require strict encryption and automatic screen locking after one minute of inactivity, whereas a field sales group might have different location tracking parameters and application allowances.
Step 4: Pilot Testing and Phased Rollout
Never deploy an MDM policy globally on day one. IT administrators should select a pilot group of tech-savvy volunteers from different departments to test the enrollment workflow, verify application compatibility, and evaluate battery consumption and performance impacts. Feedback gathered during this phase allows administrators to refine configurations before initiating a company-wide rollout.
Step 5: Full Deployment and Ongoing Monitoring
Once pilot testing validates system stability, scale the deployment using automated provisioning methods such as Zero-Touch Enrollment. Continuously monitor the MDM dashboard's compliance reports, tracking metrics such as unmanaged devices, out-of-date operating systems, and pending application updates to maintain an optimal security posture.
Common Challenges and Troubleshooting Strategies
Even well-planned Android MDM deployments encounter operational hurdles. Anticipating these challenges ensures rapid resolution and minimizes user frustration.
Device Enrollment Failures
The most frequent issue encountered during deployment is failure to complete enrollment. This often stems from incorrect credentials, expired enrollment tokens, or network connectivity blocks caused by captive portals on public Wi-Fi networks.
- Troubleshooting Action: Verify that the device has an active, unrestricted internet connection, ensure time and date settings are synchronized automatically, and generate a fresh enrollment token if the previous one has expired.
Application Deployment Stalls
Applications may occasionally fail to install or update silently on managed devices. This can occur due to insufficient storage space, conflicts with existing side-loaded versions of the same application, or Google Play service synchronization delays.
- Troubleshooting Action: Check the MDM console error logs for specific error codes. Ensure that the target device has sufficient internal storage and that the Managed Google Play store is reachable. If a conflicting consumer version of the app is installed, it must be uninstalled before the enterprise version can be deployed.
Battery Drain and Performance Degradation
End users frequently express concern that installing MDM client software drains battery life or slows down their devices. While modern Android Enterprise management is deeply integrated into the OS kernel and highly optimized, poorly configured compliance check-in frequencies or aggressive location-polling policies can impact hardware performance.
- Troubleshooting Action: Review reporting intervals within the MDM policy settings. Adjust telemetry collection and location tracking frequencies from real-time to periodic intervals to strike an optimal balance between security visibility and battery conservation.
Frequently Asked Questions
Can an Android MDM administrator see my personal photos and messages on a personal phone?
No. When an organization manages an employee-owned device via Android Enterprise Work Profile mode, a strict separation boundary is enforced by the operating system. The IT administrator has absolute visibility and control only over the work profile container, its installed applications, and corporate data. Personal photos, text messages, browsing history, and personal applications remain completely private and inaccessible to the enterprise.
What happens to corporate data if an employee leaves the company?
When a user departs the organization, the IT administrator initiates a remote management command through the MDM console. For corporate-owned devices, a full factory reset is executed, returning the hardware to its original uninitialized state. For personal BYOD devices, the administrator executes a selective wipe, which instantly and permanently deletes the work profile container, corporate emails, and enterprise applications while leaving the user's personal data, photos, and apps entirely untouched.
Does Android MDM support all Android smartphone brands?
Modern Android MDM powered by Android Enterprise is supported across the vast majority of modern Android devices running Android 8.0 Oreo and higher, regardless of manufacturer (e.g., Google Pixel, Motorola, OnePlus). However, advanced hardware-level management features—such as deep firmware-level lockdown, customized over-the-air update scheduling, and silent application installation—often require vendor-specific APIs, such as Samsung Knox or ruggedized device integration extensions provided by manufacturers like Zebra or Honeywell.
Can an MDM system bypass a forgotten lock screen passcode?
Yes and no. Standard consumer privacy controls prevent an administrator from simply viewing a user's custom lock screen PIN. However, an MDM administrator can issue a remote command to clear the existing forgotten passcode and enforce the creation of a temporary new passcode directly from the management console, allowing the user to regain access to the device without performing a full factory data reset.
Is an internet connection required at all times for an MDM-managed device?
No, managed devices do not need continuous internet connectivity to function normally. Devices cache security policies, device certificates, and application configurations locally. However, if a device remains offline for an extended period, it may fail to report compliance status, receive crucial security patch updates, or process remote wipe commands until internet connectivity is re-established.
Conclusion and Next Actions
Implementing an Android MDM strategy is a foundational requirement for any modern enterprise seeking to leverage mobile productivity while safeguarding sensitive corporate assets. By transitioning away from legacy administration methods toward modern Android Enterprise frameworks, organizations achieve the ideal balance of robust security, regulatory compliance, and user privacy.
To take the next step, initiate a comprehensive inventory of your organization's mobile endpoints, evaluate your identity management infrastructure, and consult with stakeholders to draft a clear mobile acceptable use policy before selecting and testing a pilot MDM platform.