Navigating the myACI login portal requires understanding specific authentication protocols, security prerequisites, and account management procedures to ensure secure access to organizational systems or member services. Users must typically supply verified credentials, adhere to multi-factor authentication requirements, and utilize supported web browsers to prevent connection errors or authorization failures.
Understanding the MyACI Ecosystem and Portal Purpose
The myACI platform serves as a centralized gateway designed to connect authorized users with specialized administrative tools, operational dashboards, or member resources. Depending on the exact organizational framework utilizing the ACI infrastructure, these portals generally manage identity verification, role-based access control, and secure data transmission. Recognizing the foundational architecture of the portal helps users understand why specific security measures—such as password complexities and session timeouts—are enforced during every login attempt.
Securing access to enterprise portals is critical for maintaining data integrity and compliance with modern cybersecurity standards. The myACI login interface acts as the primary barrier against unauthorized intrusion. Consequently, the platform implements strict validation rules that check not only the entered username and password combination, but also the environmental context of the connection, including IP reputation, device recognition, and geographical consistency.
Prerequisites for a Successful MyACI Login
Before attempting to access the myACI portal, users must ensure their environment meets specific technical and administrative prerequisites. Overlooking these requirements frequently leads to persistent login errors, blocked sessions, or authentication loops.
Technical Requirements
- Modern Web Browsers: The portal utilizes up-to-date web technologies, demanding modern browsers such as Google Chrome, Mozilla Firefox, Microsoft Edge, or Apple Safari with JavaScript and cookies enabled.
- Stable Internet Connection: A reliable broadband or enterprise network connection prevents timeouts during the cryptographic handshake and credential verification phase.
- Secure Protocol Support: Browsers must support Transport Layer Security (TLS) version 1.2 or higher to establish an encrypted tunnel between the client device and the ACI servers.
Administrative Requirements
- Active User Account: The account must be provisioned by an authorized administrator or registered through the official onboarding process. Inactive, suspended, or expired accounts will be rejected at the authentication gateway.
- Verified Credentials: Users must possess their exact username (often an organizational email address or designated ID) and a temporary or permanent password that meets current complexity policies.
- Multi-Factor Authentication (MFA) Setup: Many configurations require an enrolled secondary device, such as an authenticator app, hardware token, or verified phone number for receiving SMS verification codes.
Step-by-Step MyACI Login Procedure
Executing a standard login requires a methodical approach to ensure credentials are submitted securely without interception or input error.
[User Browser] ---> (HTTPS / TLS 1.3) ---> [MyACI Gateway] | [Credential Check] | [MFA Verification] | [Authorized Dashboard]
- Navigate to the Official Portal: Open a trusted web browser and enter the official, verified URL for the myACI login page. Avoid using unverified search engine links or bookmarks from unsecured sources.
- Inspect Connection Security: Verify that the browser address bar displays a secure padlock icon and that the URL begins with
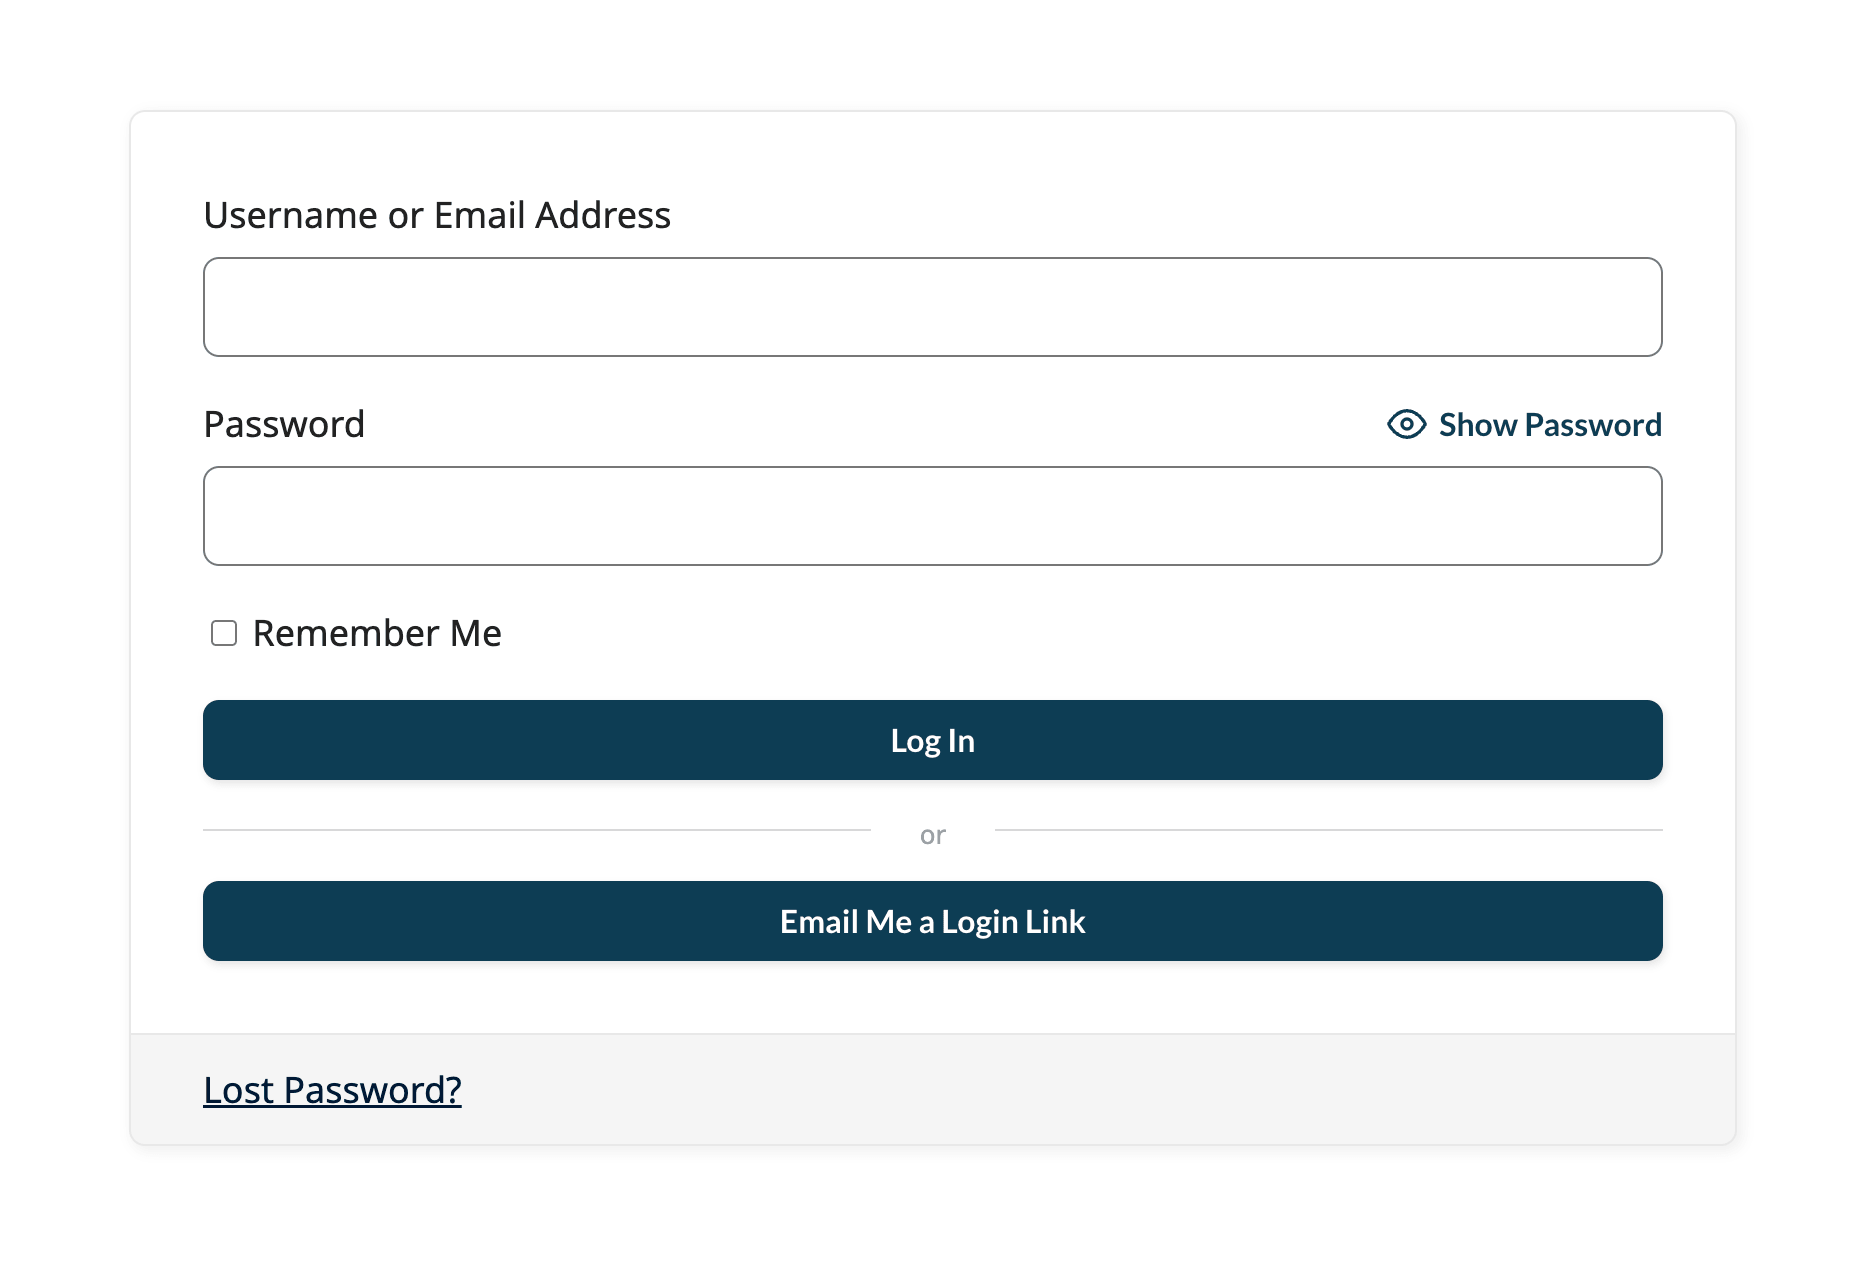
https://, indicating active encryption. - Enter Identification Details: Input your assigned username or organizational email address into the primary identity field. Check for trailing spaces that can cause authentication failures.
- Input Authentication Password: Enter your secure password into the designated field. If using a password manager, ensure it injects the credentials corresponding to the correct domain.
- Complete Multi-Factor Authentication (MFA): When prompted, provide the secondary verification factor, such as a time-based one-time password (TOTP) generated by an app or a code sent via SMS.
- Establish Dashboard Session: Upon successful verification, the system redirects the browser to the primary myACI user dashboard, initiating an active, timed session token.
Security Best Practices and Account Management
Maintaining the security of a myACI account requires constant vigilance regarding credential management and device hygiene. Because enterprise portals often house sensitive operational data, compromised credentials pose severe risks to both the individual user and the broader organization.
- Credential Confidentiality: Never share passwords, PINs, or MFA backup codes with colleagues, supervisors, or external support agents. Official administrators will never ask for a user's plain-text password.
- Password Rotation: Update account passwords periodically in accordance with organizational policy, avoiding predictable patterns, sequential numbers, or easily discoverable personal information.
- Session Termination: Always log out explicitly using the interface sign-out button when finished, especially when accessing the portal from shared, public, or unmanaged workstations. Close the browser window afterward to clear cached session cookies.
Comparison of Common Access Issues and Resolutions
When login attempts fail, identifying the exact symptom helps determine whether the issue stems from user error, browser configuration, or server-side restrictions.
| Symptom / Error Type | Probable Root Cause | Recommended Resolution |
|---|---|---|
| Invalid Credentials | Typographical error in username or password; expired temporary password. | Double-check input fields, verify caps lock status, or use the self-service password reset utility. |
| MFA Code Failure | Clock drift on the authenticator device; delayed SMS delivery; expired token window. | Resynchronize device time settings, request a new code, or use an alternative pre-registered verification method. |
| Account Locked Out | Exceeded maximum consecutive failed login attempts threshold. | Wait for the mandatory cooldown period to elapse, or contact the system administrator to unlock the profile. |
| Connection Timeout | Network packet loss, unstable Wi-Fi, or aggressive corporate firewall filtering. | Switch to a stable network connection, clear browser cache and cookies, or disable conflicting VPN extensions. |
| Browser Compatibility Error | Outdated browser version lacking modern cryptographic cipher support. | Update the web browser to the latest stable release or switch to a fully supported alternative. |
Troubleshooting Persistent MyACI Login Failures
If standard corrective actions fail to resolve access issues, users should methodically isolate the failure point through systematic troubleshooting steps.
Clearing Local Browser State
Corrupted cache files or outdated cookies frequently conflict with modern single-sign-on (SSO) and session management frameworks. Users should clear browser cache and cookies specifically for the myACI domain, or test the login procedure inside a private browsing / incognito window to verify whether local browser state is causing the interference.
Network and Firewall Diagnostics
Corporate networks, institutional firewalls, and aggressive security extensions (such as strict script blockers or ad blockers) can inadvertently block essential authentication scripts or telemetry endpoints required by the portal. Temporarily disabling browser extensions or testing the connection on an alternative trusted network can clarify whether network-level filtering is disrupting the session.
Contacting Support Channels
When account-level blocks, profile corruptions, or server outages occur, end-user troubleshooting is no longer effective. Users should contact their organization's internal IT helpdesk, system administrator, or designated support representative. Be prepared to provide specific error codes, the exact timestamp of the failure, and details regarding the browser and operating system being utilized.
Frequently Asked Questions
What should I do if I forget my myACI password?
Navigate to the login screen and select the self-service "Forgot Password" or "Reset Password" link. You will typically be required to enter your registered username or email address and complete an identity verification challenge (such as answering security questions or receiving an email reset link) to establish a new credential.
Why am I being asked for multi-factor authentication every time I log in?
Enforcing multi-factor authentication on every login session is a standard security configuration designed to mitigate unauthorized access risks. While some portals offer a "Remember this device" option, high-security environments often disable this feature to ensure compliance with regulatory mandates and internal security policies.
Is it safe to use password managers with the myACI portal?
Yes, reputable password managers that utilize client-side encryption and secure autofill protocols are generally safe and encouraged. They help users generate and store complex, unique passwords, reducing the risk of credential reuse across multiple online services.
Can I access the myACI portal from a mobile device?
Access is typically possible through mobile web browsers, provided the device meets the same technical security requirements as desktop systems. However, users should ensure they are connected to a secure cellular network or encrypted Wi-Fi rather than untrusted public hotspots.
What causes a "Session Expired" error immediately after logging in?
This error usually occurs due to a mismatch between system and device clocks, browser cookie blocking policies, or a prolonged delay between entering credentials and completing the multi-factor authentication prompt. Synchronizing your device clock and clearing browser cookies generally resolves the issue.
Conclusion and Next Actions
Successful engagement with the myACI portal relies on careful adherence to technical prerequisites, secure credential management, and prompt troubleshooting when access anomalies occur. Users should maintain updated browsers, safeguard their multi-factor authentication devices, and immediately report suspicious account activity to administrative personnel. For immediate access, proceed to the verified portal URL, input your authorized credentials, and complete the required verification steps.