A threat level is a formal assessment used by government agencies and organizations to communicate the likelihood and severity of a security incident, such as a terrorist attack or a cyber breach. These systems, such as the UK’s MI5 levels or the US National Terrorism Advisory System, guide the protective measures taken by security forces and the public.
Understanding the nuances of threat levels is essential for public safety, corporate security, and international travel. While these systems vary by country and sector, they share a common goal: providing a standardized framework for risk assessment and resource allocation. In 2026, these systems remain the backbone of national defense strategies, evolving to meet new challenges from digital warfare and decentralized physical threats.
The Hierarchy of National Security Threat Levels
National security threat levels are primarily managed by intelligence agencies and departments of internal affairs. They are not merely labels but are tied to specific operational protocols that dictate how police, military, and private security entities must behave.
The United Kingdom System (MI5 and JTAC)
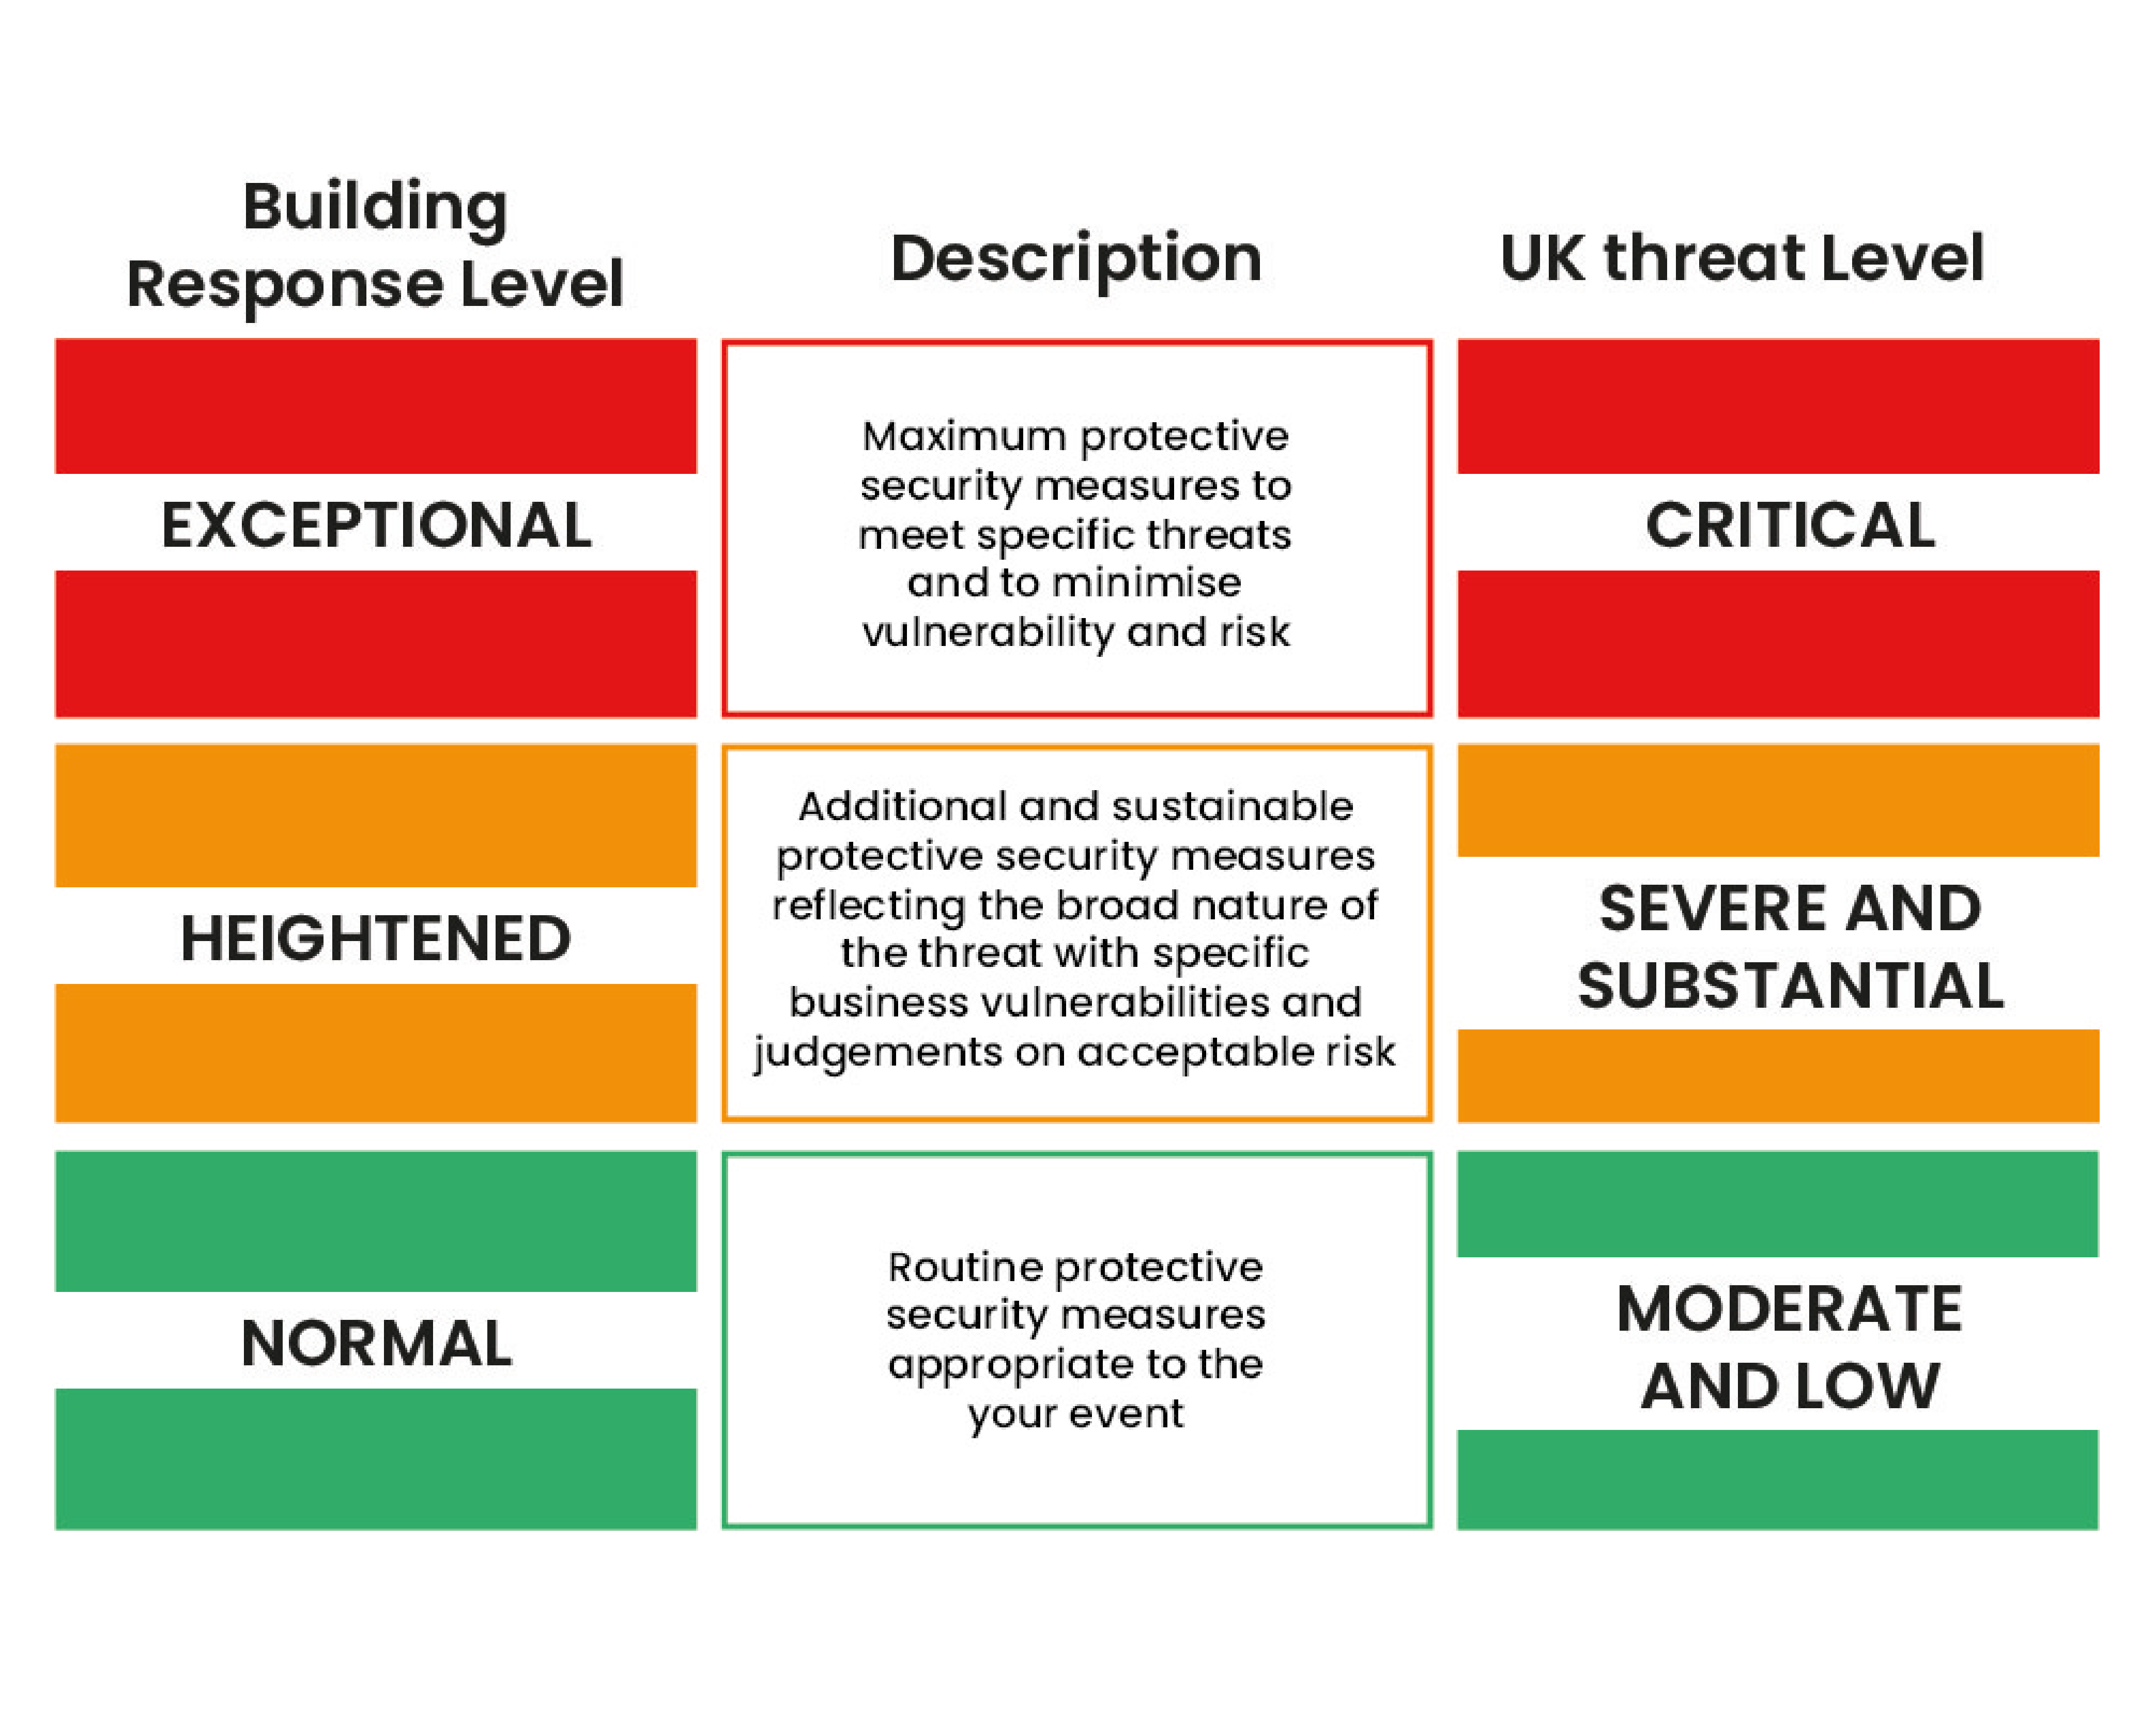
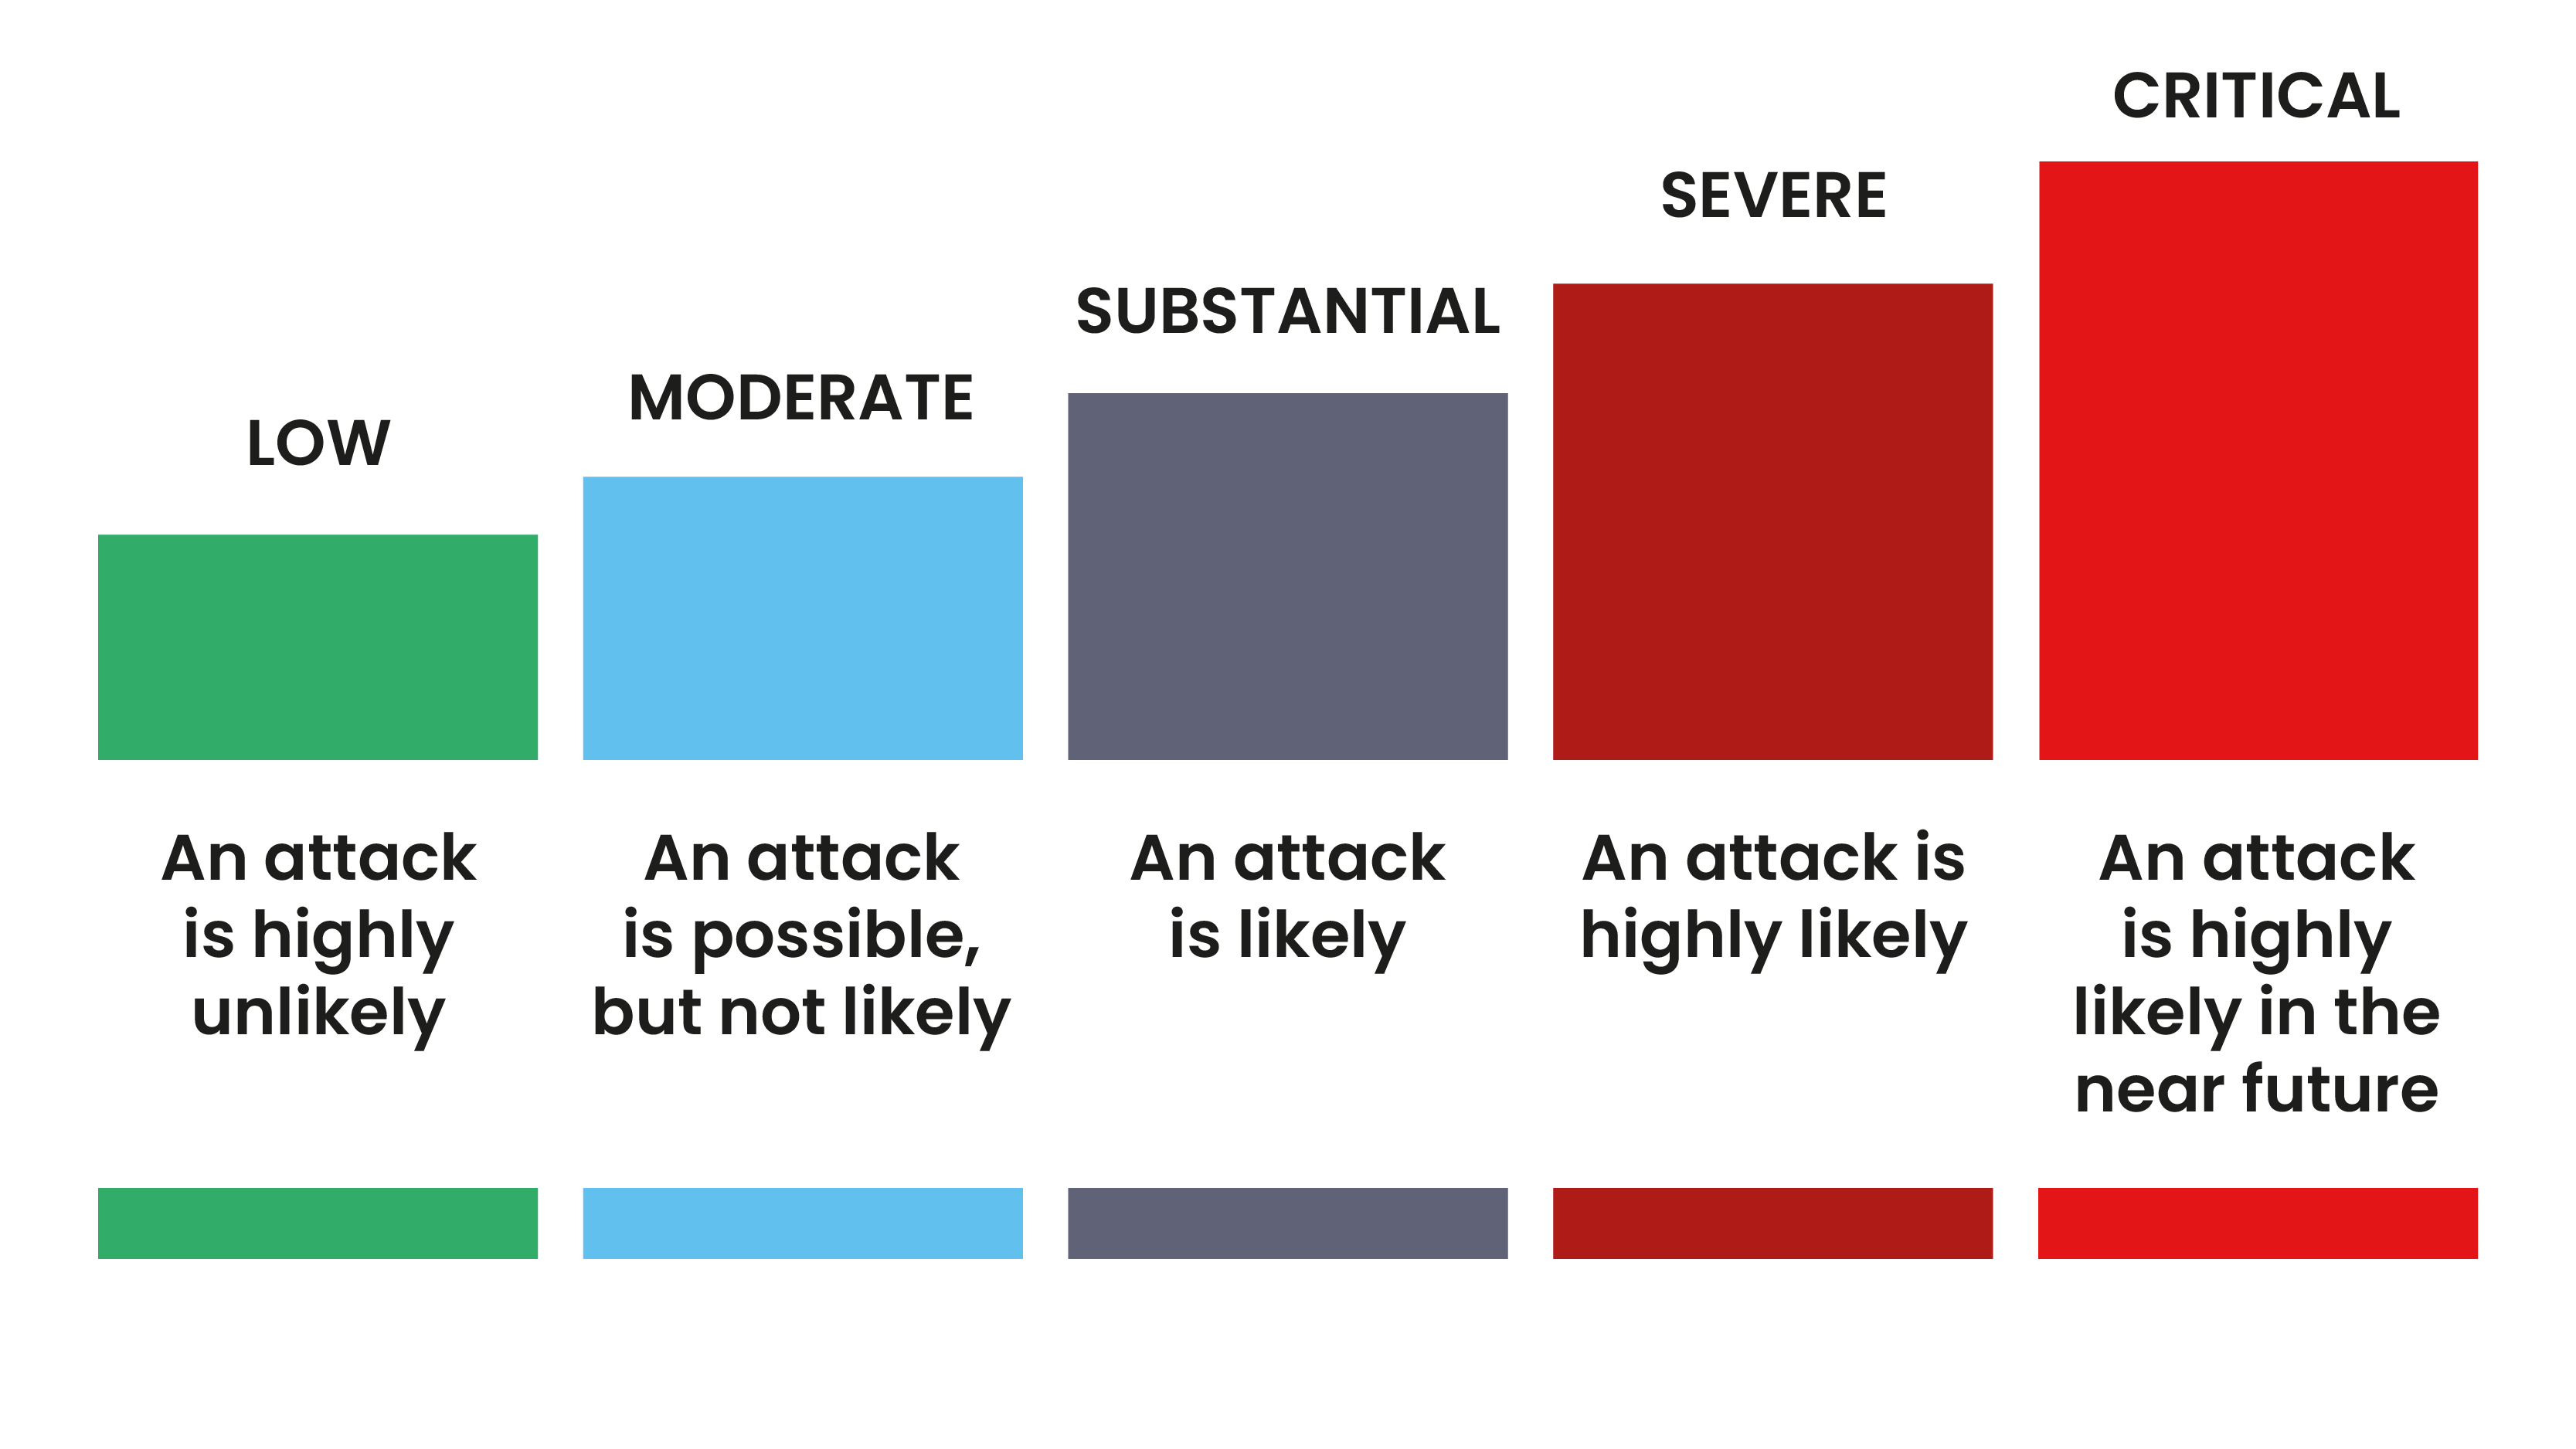
In the United Kingdom, the Joint Terrorism Analysis Centre (JTAC) is responsible for setting the national threat level. JTAC is an independent body hosted by MI5, comprising representatives from 16 government departments and agencies. As of 2026, the UK continues to utilize a five-tier system that provides a clear indicator of the likelihood of an attack.
- Low: An attack is highly unlikely. This level is rarely seen in the current global climate but represents a state of baseline security.
- Moderate: An attack is possible but not likely. Security measures are standard, with a focus on vigilance.
- Substantial: An attack is likely. This is often the "new normal" for many modern nations, indicating a persistent background threat.
- Severe: An attack is highly likely. This level often triggers increased police presence in transport hubs and crowded places.
- Critical: An attack is highly likely in the near future. This is the highest level and usually indicates that an attack is imminent or that an incident has just occurred and further actions are expected.
The UK also maintains separate threat levels for Northern Ireland-Related Terrorism (NIRT). This distinction is necessary because the intelligence profiles for domestic sectarian threats differ significantly from international or "lone actor" ideologies.
The United States System (NTAS)
The United States moved away from the 2002-era color-coded Homeland Security Advisory System (HSAS) in 2011, replacing it with the National Terrorism Advisory System (NTAS). Unlike a permanent "dial," the NTAS is designed to be more adaptive and informative.
The U.S. Department of Homeland Security (DHS) issues NTAS advisories in two formats:
- Bulletins: These describe long-term developments or trends regarding terrorism. They provide the public with context regarding the general security environment without necessarily indicating a specific, time-bound threat.
- Alerts: These are issued when there is specific, credible information about a threat. Alerts are divided into "Elevated" (no specific time or location) and "Imminent" (a threat that is believed to be unfolding or very close in time).
In 2026, the NTAS remains the primary vehicle for the DHS to communicate with state and local partners, as well as the private sector, ensuring that infrastructure owners (such as power grids and transit authorities) can adjust their security posture based on federal intelligence.
Military Readiness: DEFCON and FPCON
While public threat levels focus on terrorism and civil safety, military organizations use specialized systems to define readiness against state-level adversaries and internal security risks.
DEFCON (Defense Readiness Condition)
The DEFCON system is used by the United States Armed Forces to prescribe the posture of the military in response to international military situations. It ranges from 5 (lowest) to 1 (highest/nuclear war).
- DEFCON 5: Normal peacetime readiness.
- DEFCON 4: Increased intelligence watch and strengthened security measures.
- DEFCON 3: Increase in force readiness above that required for normal readiness. Air Force radio call signs may change to secure versions.
- DEFCON 2: Further increase in force readiness, but less than maximum readiness. This level was famously reached during the Cuban Missile Crisis.
- DEFCON 1: Maximum readiness; an immediate attack is expected or underway. This is reserved for the outbreak of nuclear war.
FPCON (Force Protection Condition)
FPCON is a Department of Defense (DoD) approved system that standardizes the identification of and recommended responses to health and safety threats against U.S. military personnel and facilities.
- FPCON Normal: Applies when a general global threat of terrorist activity exists.
- FPCON Alpha: Applies when there is an increased general threat of possible terrorist activity.
- FPCON Bravo: Applies when an increased or more predictable threat of terrorist activity exists.
- FPCON Charlie: Applies when an incident occurs or intelligence is received indicating some form of terrorist action or targeting against personnel or facilities is likely.
- FPCON Delta: Applies in the immediate area where a terrorist attack has occurred or when intelligence has been received that terrorist action against a specific location or person is imminent.
Cybersecurity Threat Levels and Risk Assessment
In the digital domain, "threat level" takes on a more technical meaning. Organizations use these levels to prioritize security patches, monitor network traffic, and activate incident response teams.
Enterprise Threat Levels
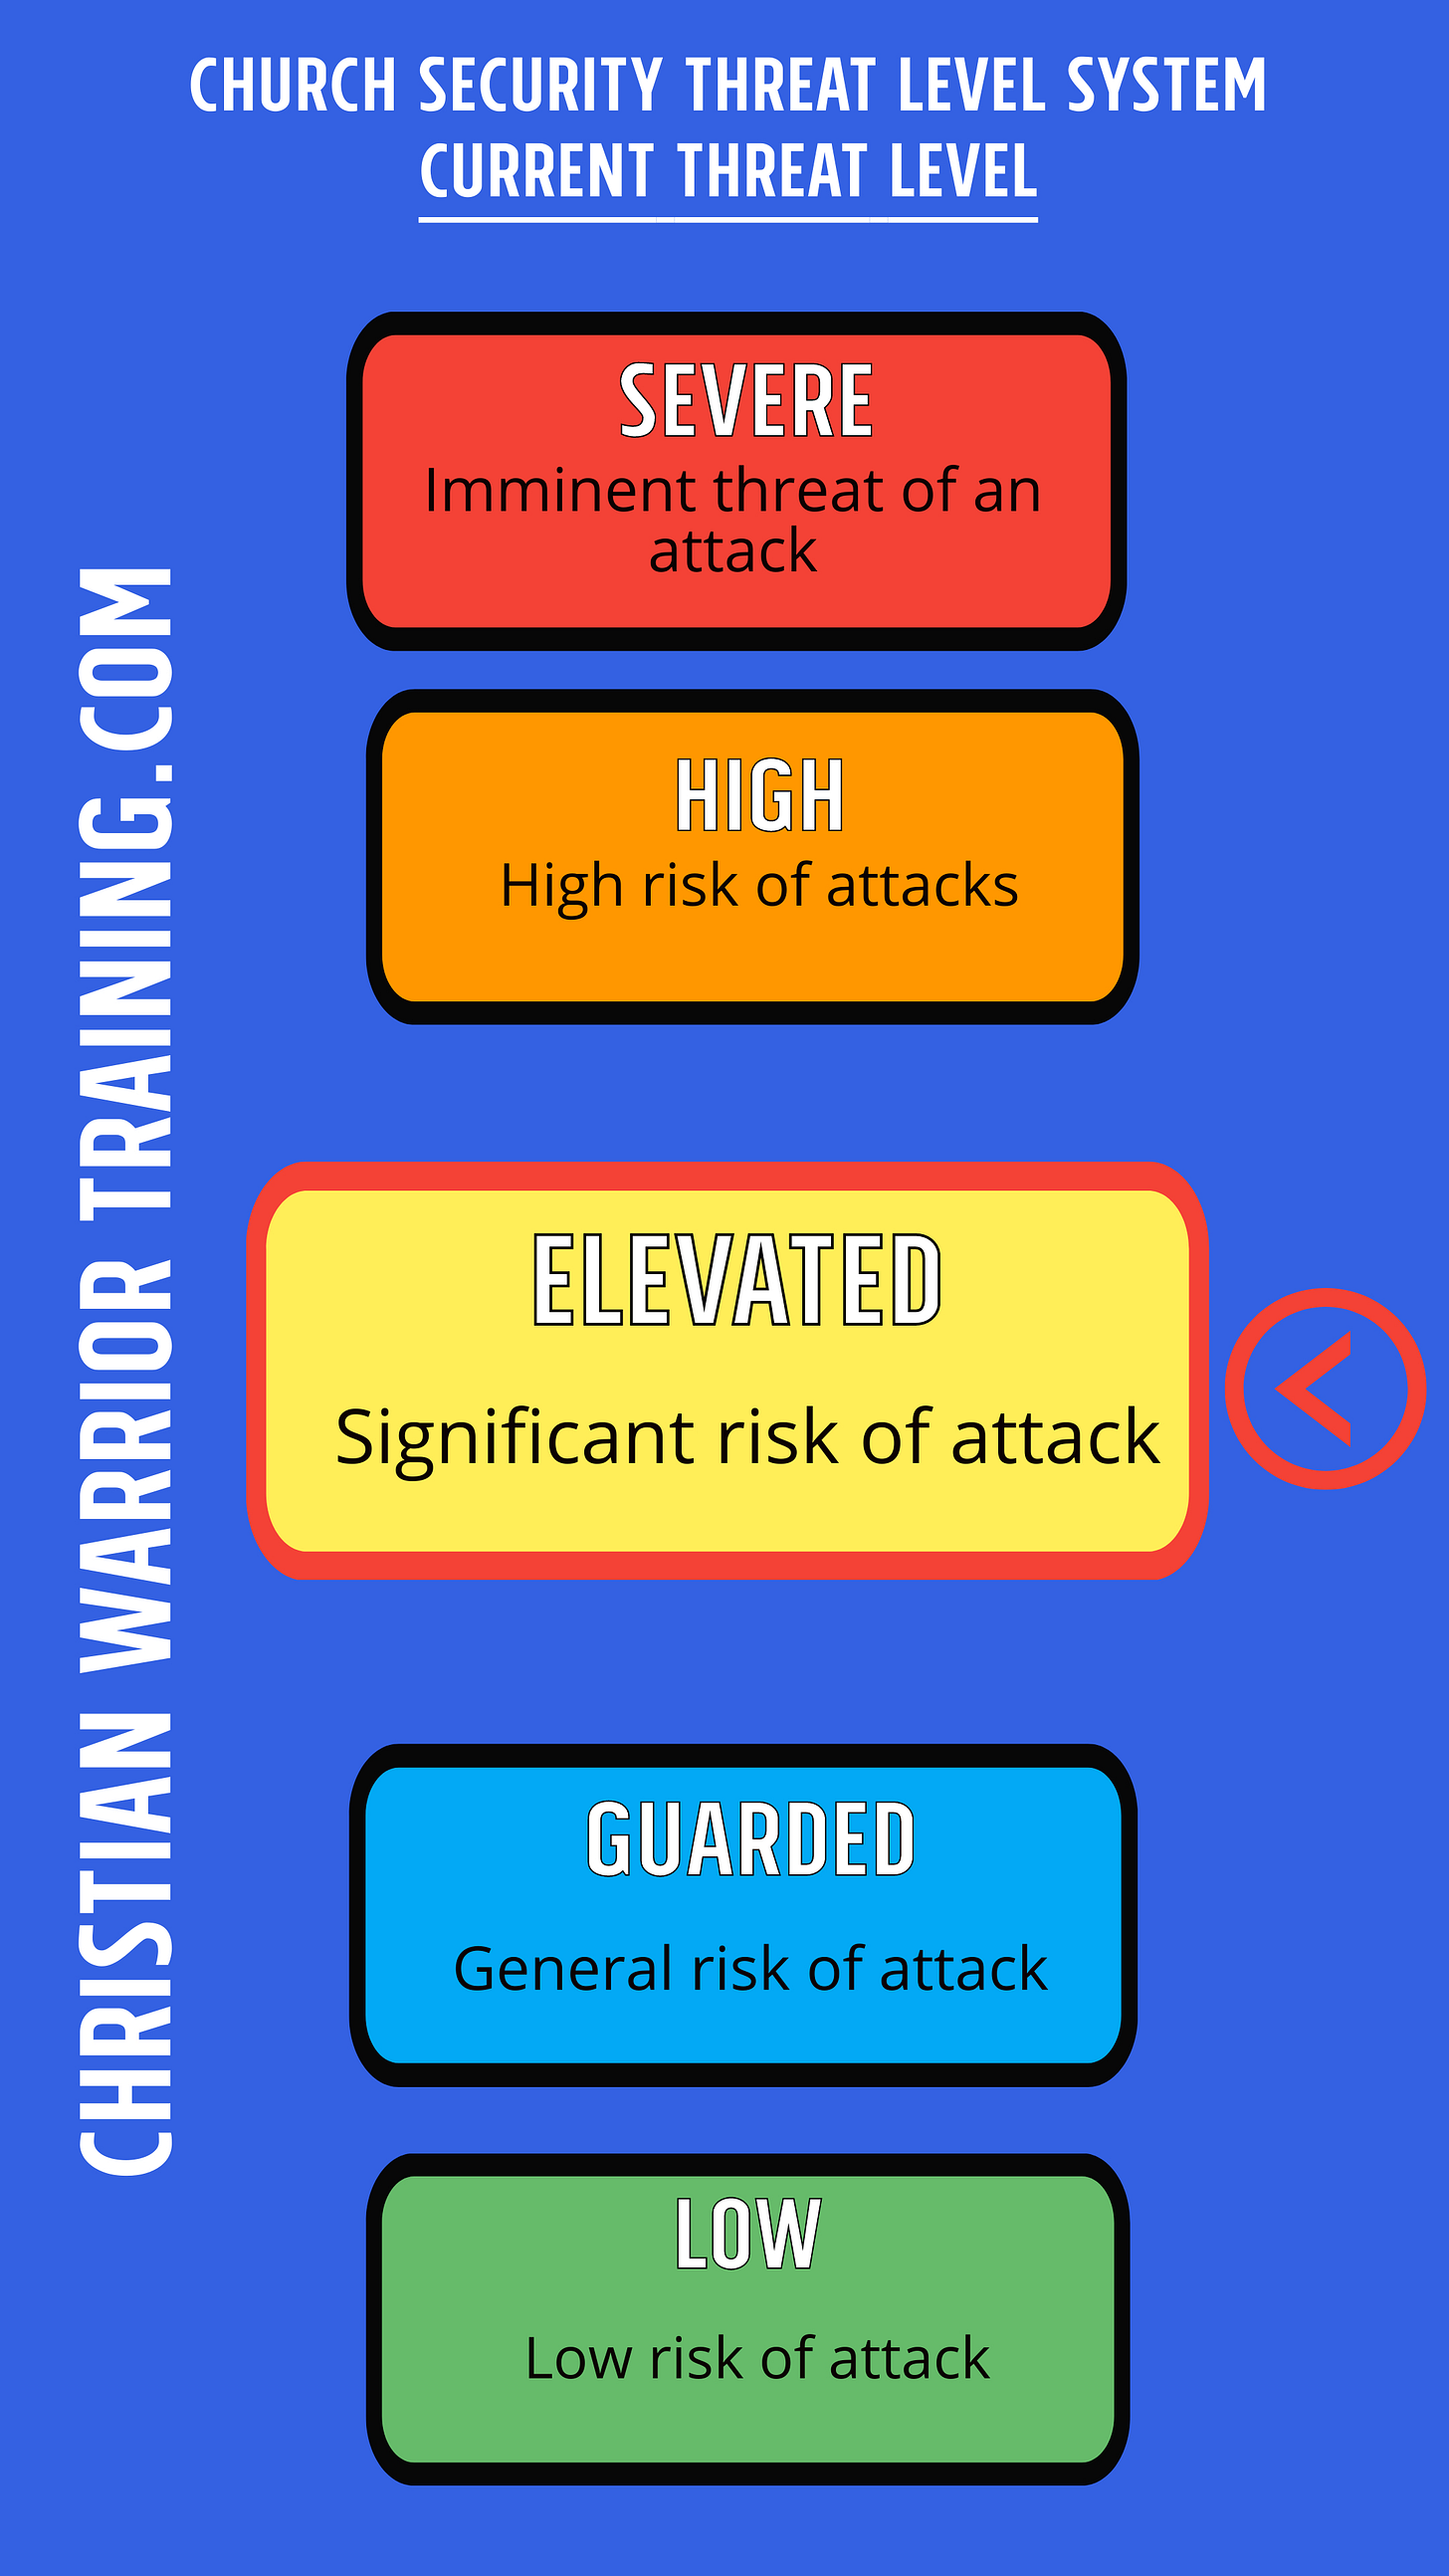
Many Large-scale Security Operations Centers (SOCs) use a 1-to-5 scale to categorize daily digital risks.
- Level 1 (Low): Normal background noise; standard phishing attempts blocked by automated filters.
- Level 2 (Guarded): Detection of new exploits in the wild that target software used by the organization.
- Level 3 (Elevated): Specific targeting of the organization's industry or a confirmed breach in a secondary system.
- Level 4 (High): A confirmed breach of internal systems with ongoing data exfiltration or malware spread.
- Level 5 (Severe): Critical infrastructure failure; widespread ransomware or total loss of administrative control.
The Role of CVSS in Threat Assessment
The Common Vulnerability Scoring System (CVSS) provides a numerical score reflecting the severity of an individual security vulnerability. While not a "threat level" for the whole organization, it determines the threat level of a specific software flaw. A CVSS score of 9.0–10.0 (Critical) demands immediate remediation, whereas a 0.1–3.9 (Low) might be addressed in the next routine update cycle.
The transition from a vulnerability (a hole in the fence) to a threat (someone trying to climb through it) is where the threat level is determined. Security teams monitor "Threat Intelligence" feeds to see if a Critical vulnerability is being actively exploited by known hacker groups.
Methodology: How Threat Levels Are Determined
Determining a national or organizational threat level is a data-driven process that involves weighing three primary factors: Intent, Capability, and Opportunity.
| Factor | Description | Example in Analysis |
|---|---|---|
| Intent | The desire of an adversary to carry out an attack. | Monitoring extremist propaganda or political declarations of war. |
| Capability | The physical or digital means to execute the attack. | Assessing an adversary's access to explosives, weapons, or zero-day exploits. |
| Opportunity | The existence of vulnerabilities or "soft targets." | Analyzing security gaps at large public events or unpatched server vulnerabilities. |
Intelligence Gathering
Intelligence agencies like MI5, the CIA, or the DGSI (France) collect data through various means:
- SIGINT (Signals Intelligence): Intercepting communications, such as emails or radio signals.
- HUMINT (Human Intelligence): Information gathered from undercover agents or informants.
- OSINT (Open-Source Intelligence): Monitoring social media, news reports, and public forums.
- IMINT (Imagery Intelligence): Satellite or drone photography of suspect sites.
The Decision-Making Process
Once data is collected, analysts look for patterns. For a threat level to be raised to "Critical" or "Imminent," there is usually "specific and credible" intelligence. This means the intelligence points to a particular target, a particular method, or a specific timeframe. Without specificity, the level usually remains at "Substantial" or "Elevated."
Practical Impact of Threat Level Changes
When a threat level changes, the impact is felt across multiple sectors of society. These changes are designed to harden targets and deter attackers by making the "opportunity" factor much harder to achieve.
Impact on Aviation and Transit
Transportation is often the first sector affected. At higher threat levels, passengers may experience:
- Enhanced screening of electronics and liquids.
- Increased use of K9 units (bomb-sniffing dogs) in terminals.
- Random vehicle searches at airport entrances.
- Deployment of armed police or military personnel to patrol train stations.
Impact on Government and Infrastructure
For government employees and contractors, a rise in the threat level often means:
- Mandatory ID checks for all personnel entering buildings.
- Restriction of visitor access.
- Increased monitoring of perimeter security and CCTV.
- Heightened cybersecurity protocols, including forced password resets or restricted remote access.
Public Guidance
The general public is rarely expected to change their daily lives significantly during "Substantial" or "Elevated" levels. However, at "Severe" or "Critical," the advice usually shifts to:
- Increased Vigilance: Reporting unattended bags or suspicious behavior to the "Anti-Terrorist Hotline."
- Preparedness: Reviewing emergency plans for homes and businesses.
- Cooperation: Expecting and accepting delays at public events and checkpoints.
Comparison of Global and Military Threat Systems
The following table compares how different organizations and nations categorize risk levels to help clarify the terminology.
| System | Agency | Lowest Level | Mid Level | Highest Level |
|---|---|---|---|---|
| National (UK) | JTAC / MI5 | Low | Substantial | Critical |
| National (US) | DHS / NTAS | Bulletin | Elevated Alert | Imminent Alert |
| Military (US) | DoD (DEFCON) | DEFCON 5 | DEFCON 3 | DEFCON 1 |
| Force Protection | DoD (FPCON) | Normal | Bravo | Delta |
| Cybersecurity | Standard SOC | Level 1 (Normal) | Level 3 (Elevated) | Level 5 (Emergency) |
Frequently Asked Questions
Who has the authority to change the national threat level?
In the United Kingdom, the decision is made by the Joint Terrorism Analysis Centre (JTAC), which is independent of direct political control, though it reports to the Home Secretary. In the United States, the Secretary of Homeland Security has the authority to issue NTAS alerts, usually in consultation with the President and the intelligence community. These decisions are based on classified briefings and are rarely subject to public debate before implementation.
Why doesn't the government always tell us the specific threat?
Revealing the specific details of a threat—such as the exact target or the method of intelligence gathering—could compromise "sources and methods." If a terrorist group realizes their communications are being intercepted, they will change their tactics, making them harder to track. Governments provide enough information for the public to be vigilant without providing a "roadmap" for the adversaries.
Is DEFCON the same as the terrorism threat level?
No. DEFCON (Defense Readiness Condition) is a measure of the United States military's readiness for state-on-state conflict or nuclear war. The national threat levels (like NTAS or MI5) focus on terrorism and domestic security. It is possible for the national threat level to be "Critical" while DEFCON remains at 4 or 5, and vice-versa.
How often are threat levels reviewed?
National threat levels are under constant review. In the UK, JTAC monitors intelligence 24/7. Formal reviews occur regularly, but the level can be changed instantly if a significant piece of intelligence is discovered or if a major incident occurs. In the U.S., NTAS Bulletins have an expiration date (usually several months), at which point they must be renewed, updated, or allowed to lapse.
Can a threat level be lowered after an attack?
Counterintuitively, the threat level often stays high or even increases immediately after an attack. This is because intelligence agencies must determine if the attack was a "lone wolf" incident or part of a larger, coordinated "wave." The level is only lowered once the immediate network associated with the attack has been disrupted and the risk of a "follow-on" strike is deemed to have passed.
Recommended Actions for High-Threat Environments
In 2026, the complexity of both physical and digital threats requires a proactive stance. If you reside in or are traveling to an area where the threat level has been raised to "Severe" or "Critical," consider the following steps:
- Stay Informed: Download official government safety apps (such as the FEMA app in the US or the CitizenAID app in the UK) and enable emergency alerts on your smartphone.
- Review "Run, Hide, Tell": Familiarize yourself with the standard response to an active threat. Move away from the danger, find cover if you cannot escape, and notify the authorities only when it is safe to do so.
- Audit Personal Security: For businesses, ensure that all access control points are functioning and that staff are briefed on heightened security protocols. For individuals, maintain a high level of situational awareness in crowded places.
- Digital Hygiene: In the event of a high cybersecurity threat level, ensure all software is updated, use multi-factor authentication (MFA) on all accounts, and be wary of "event-driven" phishing scams that exploit current news or emergencies.
While the presence of a high threat level can be unnerving, these systems are designed to prevent incidents by ensuring that the right resources—police, intelligence, and public awareness—are in the right place at the right time. Vigilance remains the most effective tool in any security framework.