An MDM network refers to an integrated framework combining Mobile Device Management (MDM) software with corporate network infrastructure to secure, monitor, and manage endpoints. It enforces strict security policies, manages access controls, and ensures that every connected mobile device, laptop, or IoT asset complies with organizational standards before accessing internal resources.
Understanding the Foundation of MDM Networks
To comprehend how an MDM network operates, one must first look at the intersection of modern enterprise mobility and network security. In traditional corporate environments, security perimeters were defined by physical walls and hardwired Ethernet cables. Employees worked on organization-owned desktop computers sitting inside an office building, protected behind a centralized firewall. Today’s workforce, however, demands mobility and flexibility. Employees access company data from smartphones, tablets, and personal laptops from virtually anywhere in the world.
This shift dismantled the traditional network perimeter. To re-establish control, organizations turned to Mobile Device Management platforms. When integrated deeply with the underlying network architecture, MDM transforms from a simple device-tracking tool into an active gatekeeper. An MDM network bridges the gap between endpoint configuration and network access control (NAC). It ensures that no device—regardless of whether it is corporate-owned or personal (Bring Your Own Device, or BYOD)—can communicate with sensitive servers or cloud repositories unless it meets predefined compliance benchmarks.
Furthermore, an MDM network relies on continuous communication loops. The MDM server constantly polls enrolled devices, checking for operating system updates, jailbreak or root attempts, unauthorized application installations, and missing security patches. Simultaneously, the network infrastructure dynamically adjusts permissions based on the real-time health data supplied by the MDM platform. If a device falls out of compliance, the network can automatically isolate it, quarantining the asset until the user or administrator resolves the underlying security violation.
Core Architecture and Components of an MDM Network Architecture
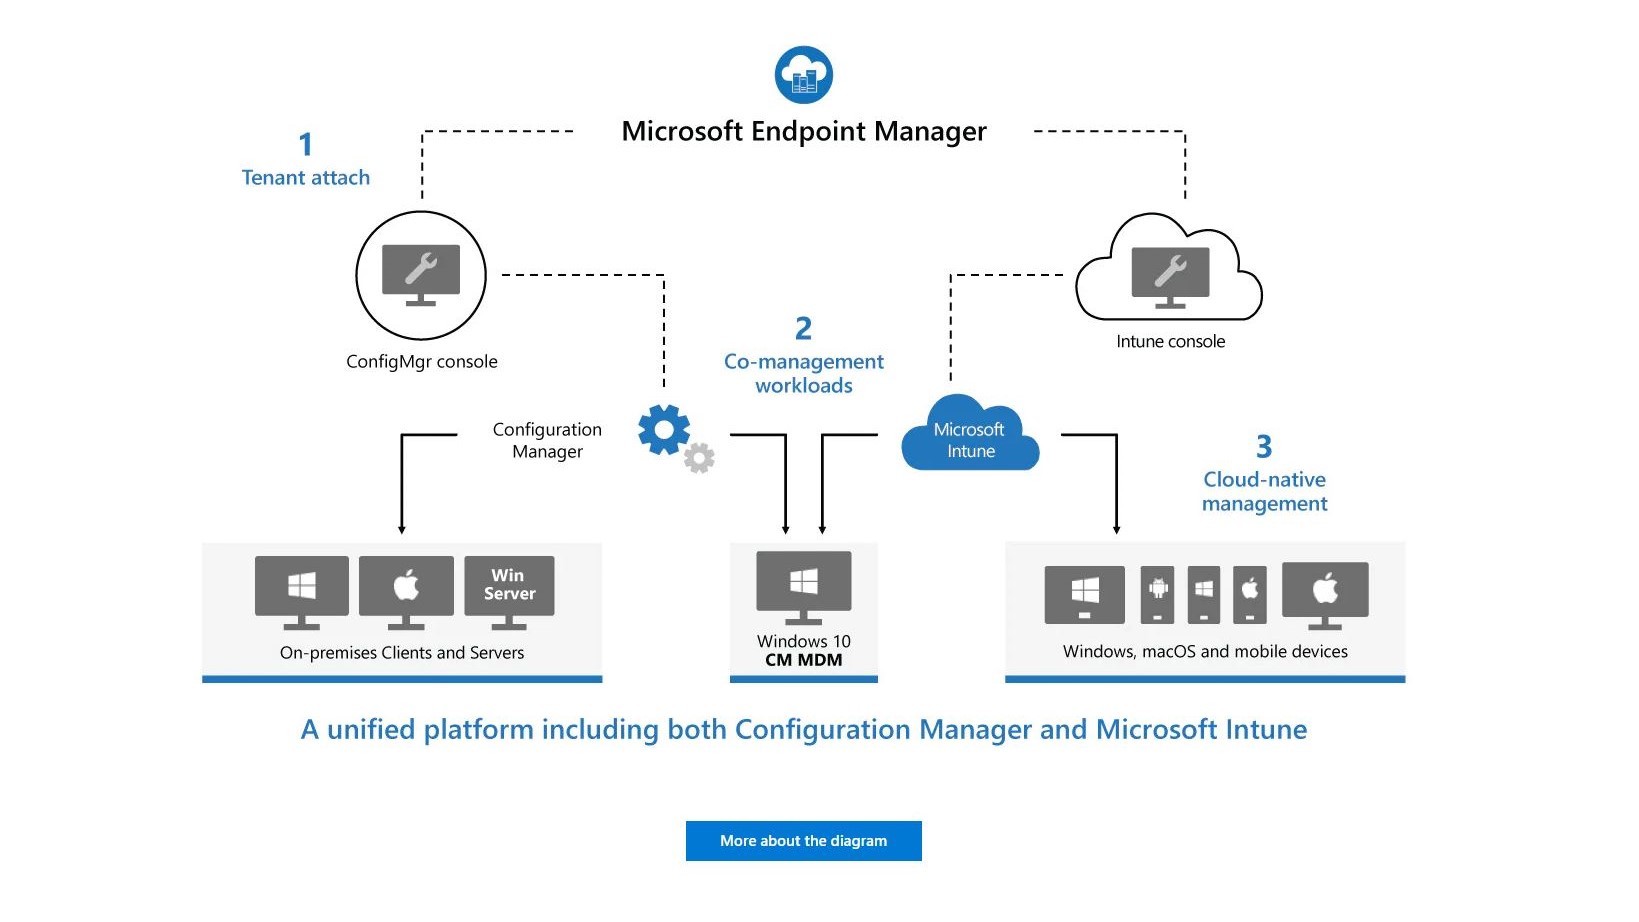
Building a robust MDM network requires a careful blend of software agents, cloud-hosted or on-premises management servers, and network enforcement points. Every component plays a distinct role in maintaining the security posture and operational integrity of the digital workspace.
- MDM Admin Console
- MDM Server (Cloud / On-Premises)
- Device Enrollment & OTA -> Managed Endpoints (iOS, Android, etc.)
- Compliance & Policy Checks -> Network Infrastructure (NAC, Firewalls, Wi-Fi)
- Managed Endpoints and Network Infrastructure interact bidirectionally
- MDM Server (Cloud / On-Premises)
The MDM Server and Enrollment Frameworks
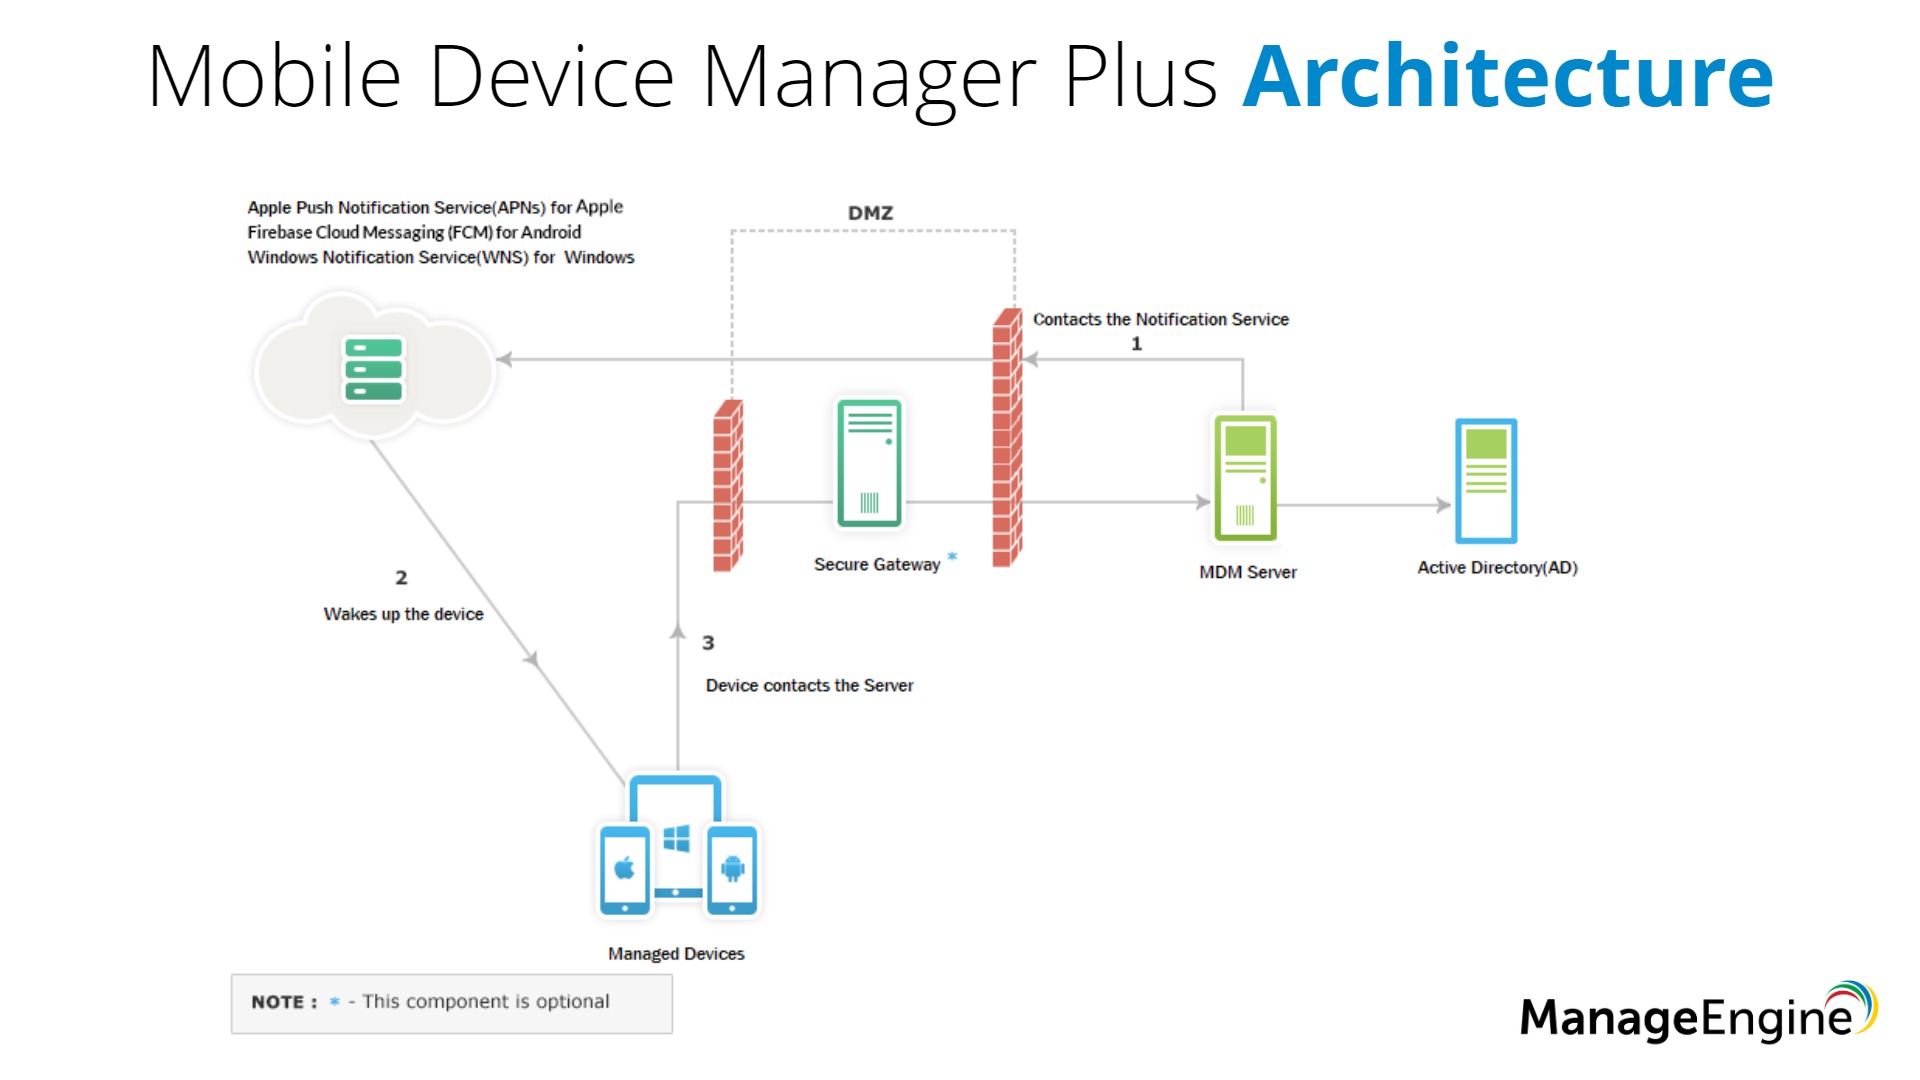
At the heart of the system is the MDM server. This server acts as the command center, communicating with endpoints via Over-The-Air (OTA) protocols. For Apple ecosystems, the server leverages the Apple Push Notification service (APNs). For Android enterprise deployments, it relies on Google Cloud Messaging or Firebase Cloud Messaging.
During the enrollment phase, the MDM server provisions configuration profiles onto the device. These profiles configure Wi-Fi credentials, virtual private network (VPN) settings, email parameters, and security restrictions. Automated enrollment programs—such as Apple Business Manager (ABM) and Android Enterprise Zero Touch—allow organizations to prepopulate settings before the device even reaches the end user, ensuring out-of-the-box compliance.
Network Access Control (NAC) and Gateways
While the MDM server manages the device state, the Network Access Control (NAC) system and enterprise firewalls enforce the rules at the packet level. NAC solutions inspect the identity of the device and query the MDM server via APIs to verify its compliance score. If the MDM server reports that a laptop has disabled its disk encryption (such as FileVault or BitLocker), the NAC immediately blocks that laptop from accessing the corporate database, redirecting the user to a remediation portal.
Client-Side Agents and Profiles
On the endpoint itself, either a lightweight management agent application or a native operating system profile runs silently in the background. This agent gathers telemetry data, enforces passcode complexities, blocks screen captures on sensitive applications, and facilitates remote wipe capabilities in the event of loss or theft.
Integration with Enterprise Network Infrastructure
Integrating an MDM platform directly into corporate networking hardware transforms static network segments into dynamic, context-aware environments. Organizations can no longer rely on static IP address filtering or basic pre-shared keys for Wi-Fi security.
802.1X Authentication and Certificate-Based Access
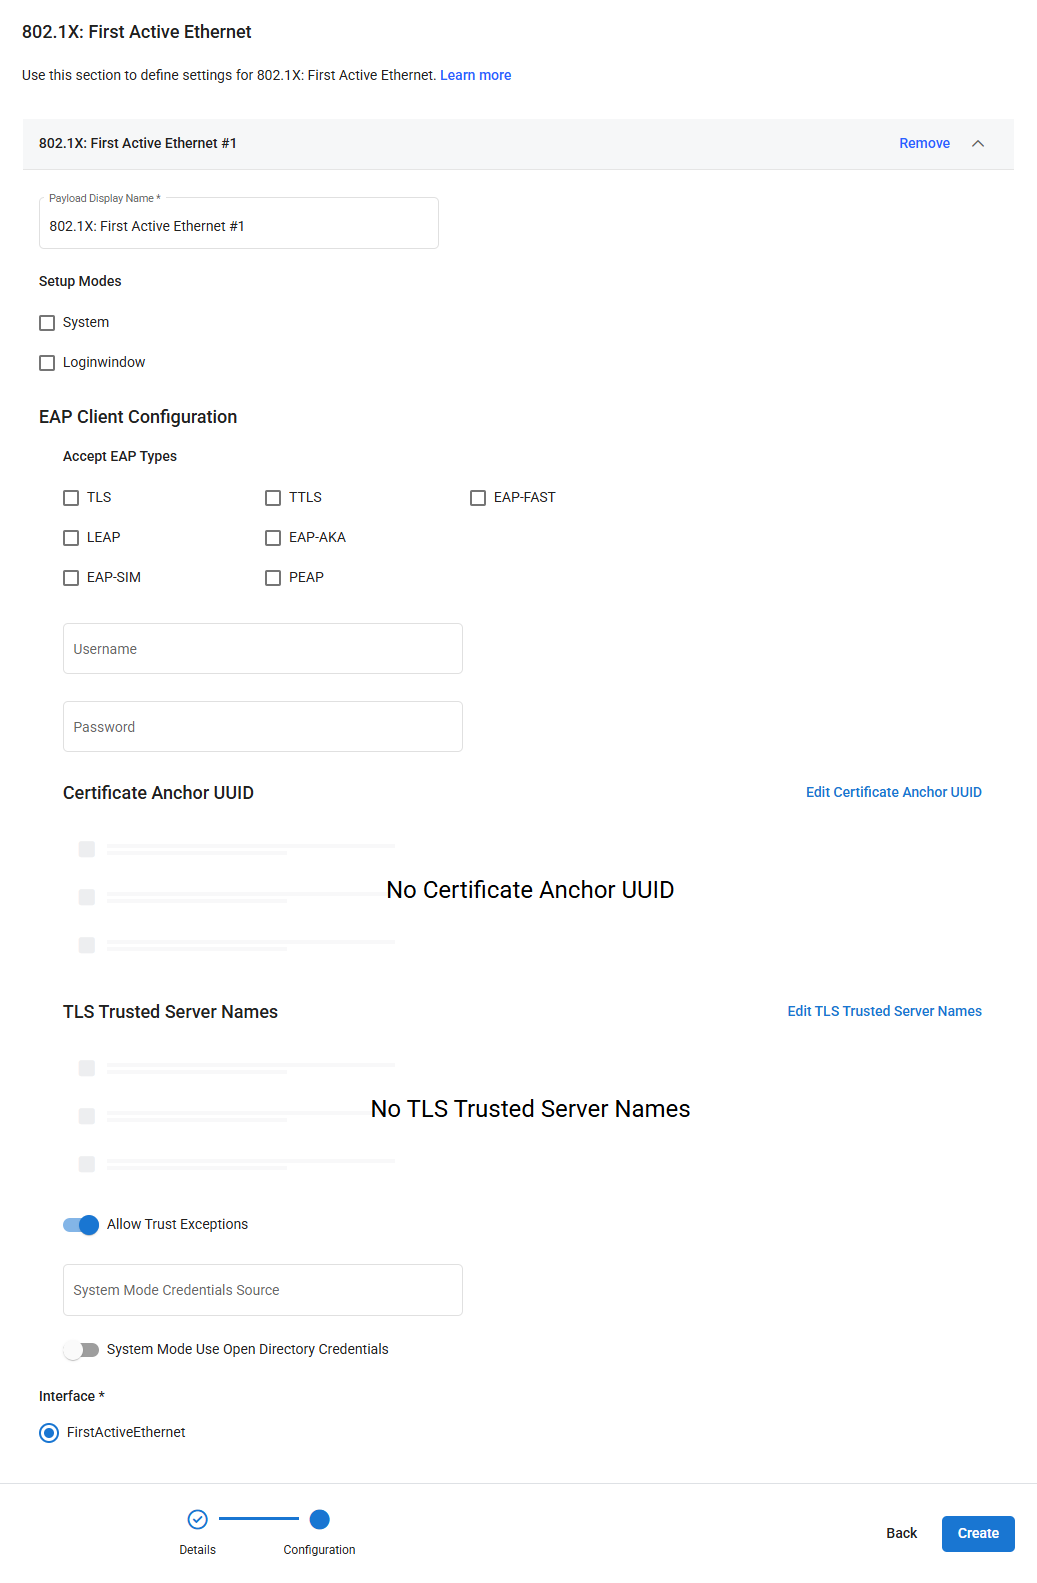
Modern MDM networks utilize 802.1X protocols alongside Extensible Authentication Protocol-Transport Layer Security (EAP-TLS) to authenticate devices. Instead of requiring users to remember complex passwords that are prone to phishing, the MDM server automatically pushes a unique digital certificate to the trusted device during enrollment.
When the device attempts to connect to the corporate Wi-Fi or local area network (LAN), the network switch or wireless access point validates this certificate against a secure Public Key Infrastructure (PKI). If the certificate is valid and the device is verified as compliant by the MDM system, access is granted. If a device is revoked or compromised, the administrator revokes the certificate, instantly severing its ability to authenticate on the network.
Dynamic VLAN Assignment and Micro-Segmentation
Once authenticated, an MDM network can dynamically assign devices to specific Virtual Local Area Networks (VLANs) or apply granular firewall policies based on device ownership. For example:
- Corporate-owned laptops receive full access to internal file shares, engineering servers, and enterprise resource planning (ERP) systems.
- Contractor or BYOD smartphones are placed into an isolated guest VLAN with internet-only access, completely blocked from lateral movement across the internal network.
- Internet of Things (IoT) devices managed via MDM are restricted strictly to communication endpoints required for their designated functions.
| Device Category | Authentication Method | Network Access Level | Remediation Action on Non-Compliance |
|---|---|---|---|
| Corporate Laptops | EAP-TLS Certificate + MDM Check | Full internal network & cloud resources | Quarantine to remediation VLAN until patched |
| BYOD Smartphones | Username/Password + MDM Container | Segmented intranet & cloud email only | Block access to internal apps; notify user |
| Managed IoT Assets | MAC Authentication Bypass + MDM Profile | Isolated single-purpose subnet | Disable network port / drop traffic |
Security Policies and Compliance Enforcement
An MDM network's primary value proposition lies in its ability to enforce security policies systematically without requiring manual intervention from IT support staff.
Conditional Access Policies
Conditional access acts as a dynamic shield. It evaluates multiple risk factors before granting access to applications like Microsoft 365, Google Workspace, or custom enterprise software. Factors include:
- Device Compliance: Is the operating system running a supported version with recent security patches?
- Location Risk: Is the login attempt originating from an unexpected geographic region or an unknown IP address range?
- Network Trust: Is the device connected via a secure, approved corporate VPN or encrypted enterprise Wi-Fi?
If any parameter violates policy, the system prompts for multi-factor authentication (MFA) or denies access outright.
Containerization and Data Loss Prevention (DLP)
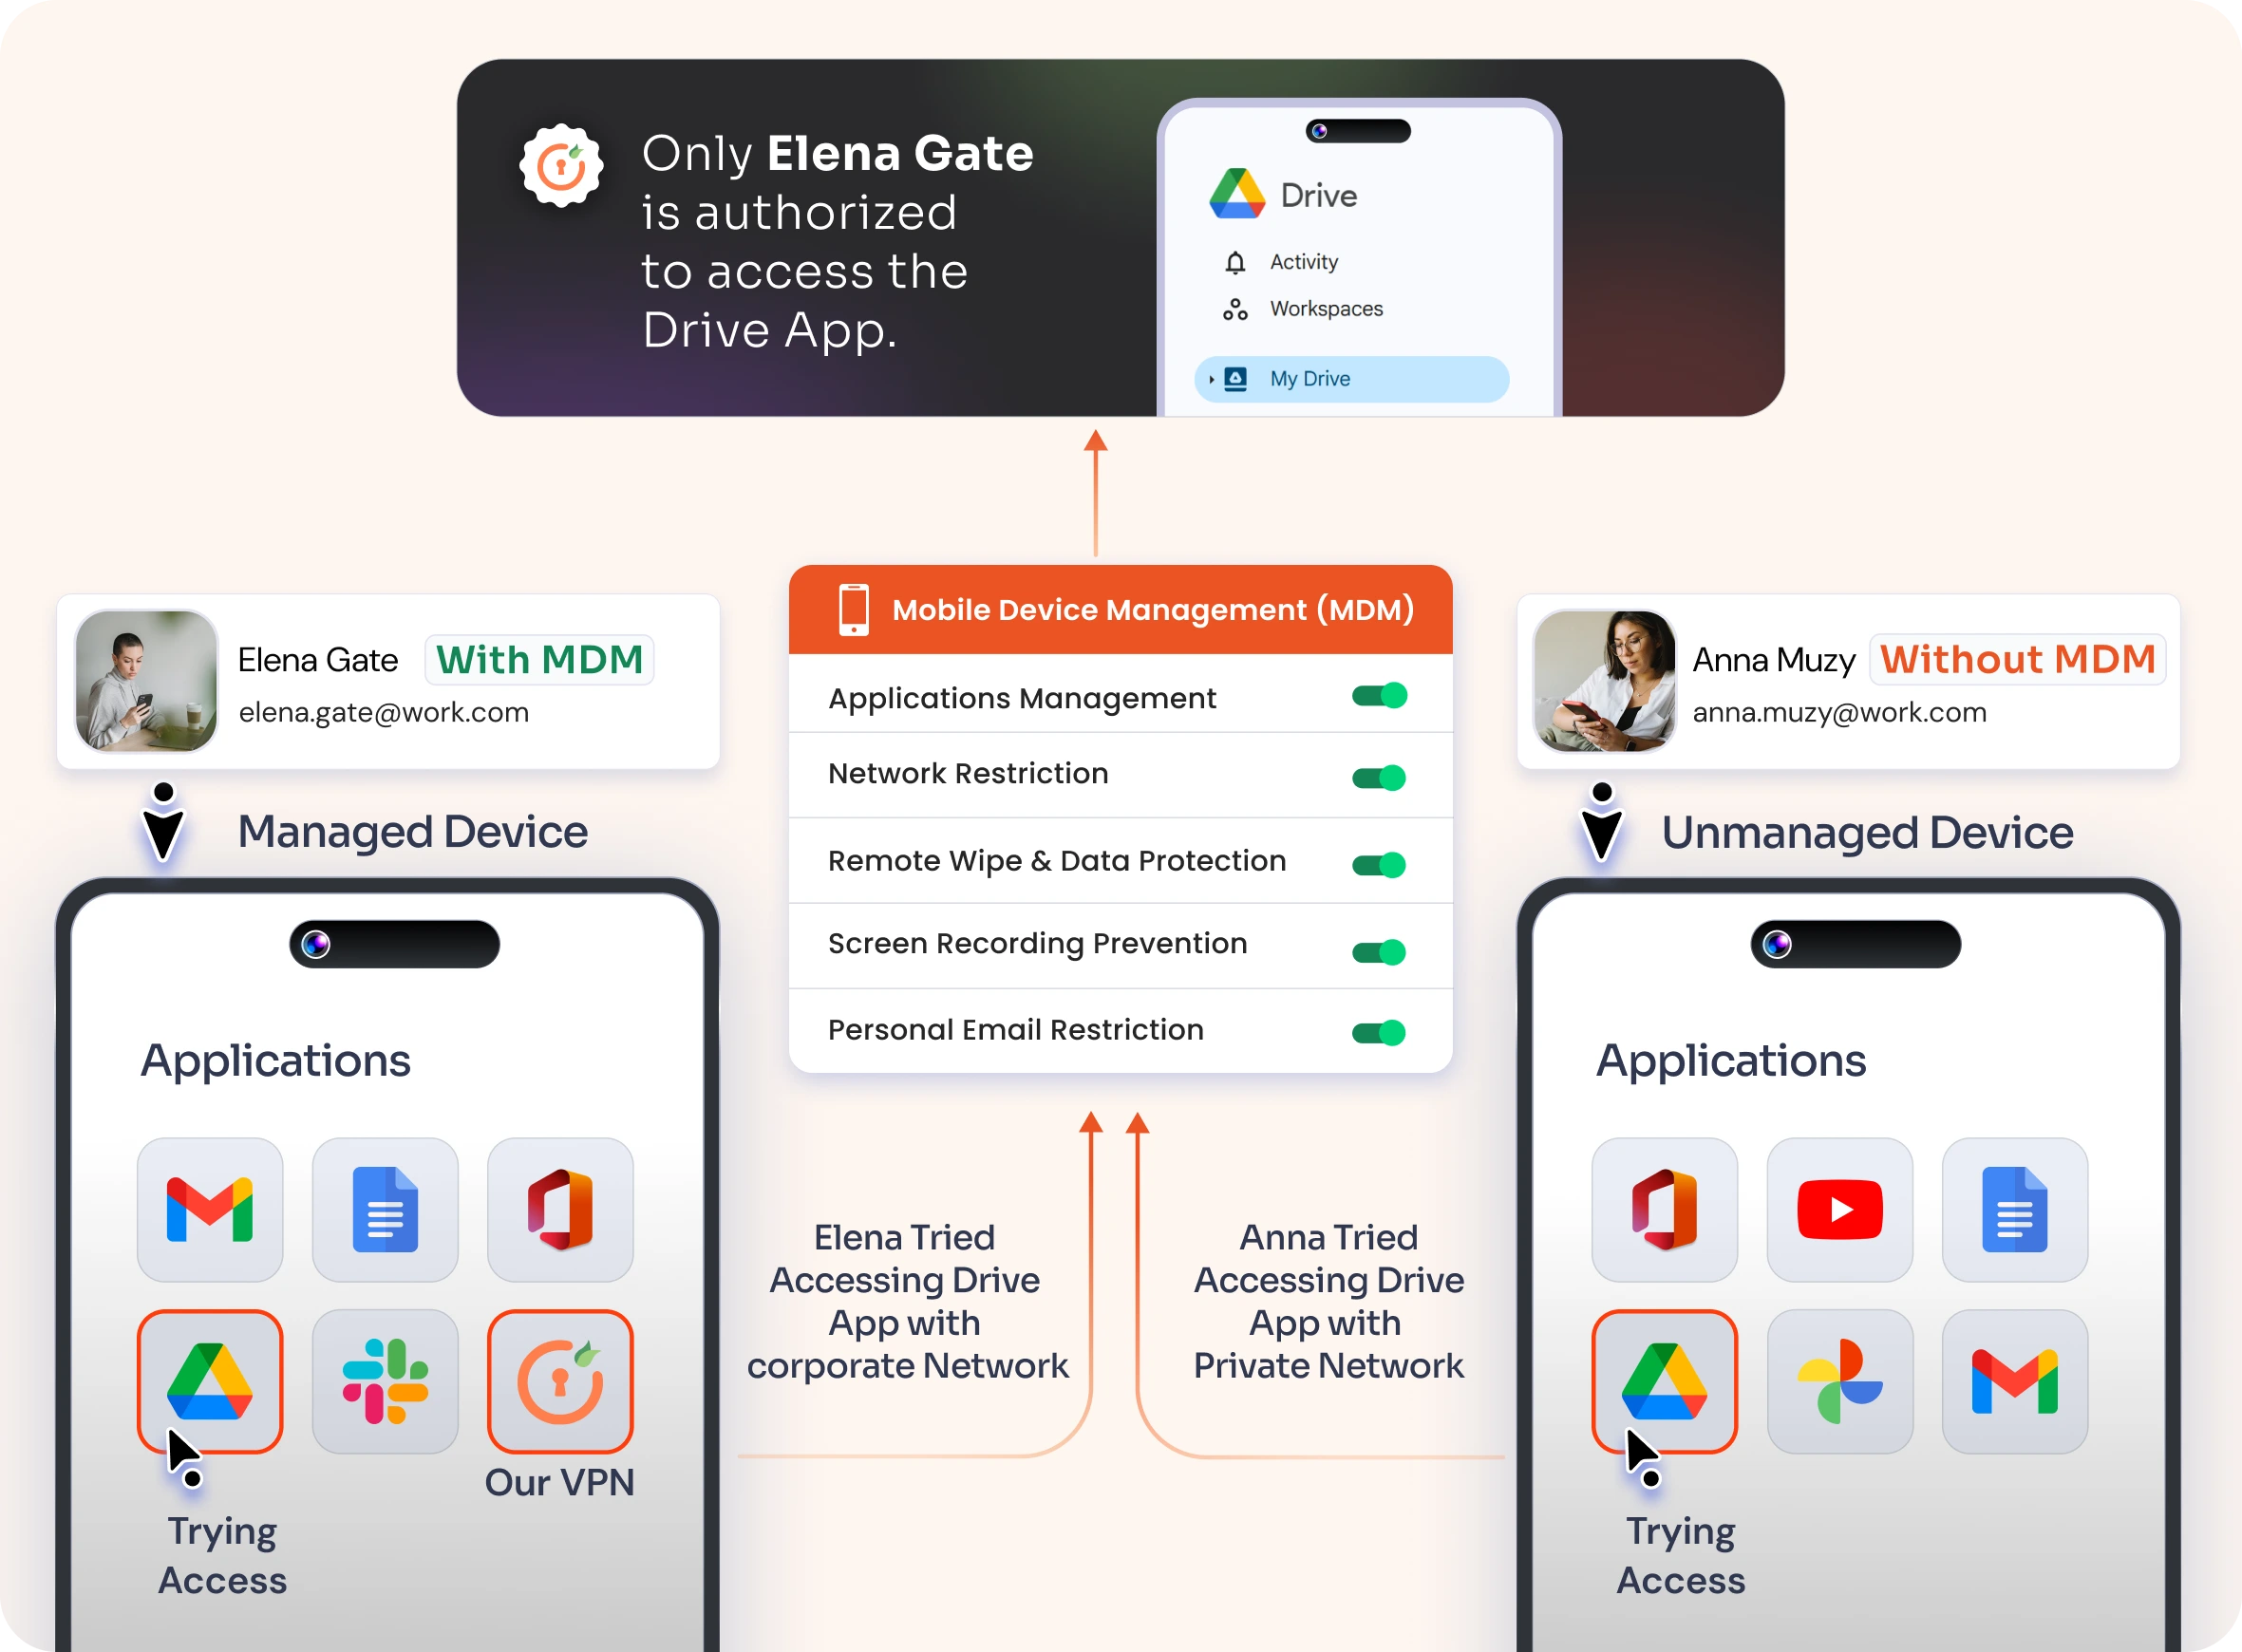
In BYOD scenarios, privacy is a major concern for employees who do not want corporate IT monitoring their personal photos, messages, or browsing history. MDM networks solve this through containerization. By creating a secure, encrypted workspace partition on the mobile device, corporate data is strictly separated from personal data.
Data Loss Prevention (DLP) policies within this container prevent users from copying text, forwarding corporate emails to personal accounts, or opening enterprise files inside unmanaged third-party applications. If an employee leaves the company, IT can execute a selective remote wipe, erasing the corporate container entirely while leaving personal files untouched.
Implementation Steps for Building an MDM Network
Deploying an MDM network requires a structured, multi-phase approach to minimize downtime and ensure seamless user adoption. Rushing deployment often leads to misconfigured policies, locked-out users, and security gaps.
Phase 1: Planning and Scoping
Define the objectives of the deployment. Identify the operating systems that need support (iOS, Android, Windows, macOS, ChromeOS), the types of devices (owned vs. BYOD), and the regulatory frameworks the organization must comply with (such as HIPAA, GDPR, or PCI-DSS).
Phase 2: Selecting and Configuring the MDM Solution
Choose between cloud-based MDM solutions (which offer rapid deployment and seamless scalability) and on-premises solutions (which provide granular control over data residency). Configure the administrative console, set up role-based access control (RBAC) for IT staff, and integrate directory services like Microsoft Entra ID (formerly Azure AD) or LDAP for user authentication.
Phase 3: Infrastructure and Certificate Authority Setup
Establish a secure PKI or integrate the MDM with existing certificate authorities. Configure RADIUS servers, wireless controllers, and NAC appliances to communicate with the MDM via APIs. Test the authentication pipeline to ensure certificates push correctly and 802.1X handshakes succeed.
Phase 4: Pilot Testing and Policy Refinement
Roll out the MDM network to a small pilot group—typically the IT department and select power users. Monitor enrollment success rates, verify that push notifications function reliably, and refine security policies to avoid overly aggressive restrictions that hinder productivity.
Phase 5: Full-Scale Enrollment and Monitoring
Initiate the organization-wide rollout using automated enrollment programs. Provide clear documentation and support channels for end users. Continuously monitor the MDM dashboard for compliance alerts, unmanaged endpoint attempts, and network anomaly logs.
Troubleshooting Common MDM Network Issues
Even well-configured MDM networks encounter operational hurdles. System administrators frequently face specific technical challenges that require systematic troubleshooting.
Enrollment Failures and Push Notification Drops
When devices fail to enroll, the root cause is often related to network firewall rules blocking necessary outbound ports or communication with Apple/Google push notification servers. Administrators must verify that firewalls permit traffic over standard HTTPS ports (TCP 443) and specific ports required by the MDM vendor. If devices suddenly stop receiving configuration updates, check the status of the APNs or FCM service certificates, as expired certificates break the communication tunnel immediately.
Certificate Authentication Errors
If users experience sudden disconnections from the corporate Wi-Fi or internal portals, check the validity of the client certificates pushed by the MDM. Time drift between the MDM server, the certificate authority, and the endpoint can cause certificate validation failures. Ensuring all network infrastructure and client devices sync their time via Network Time Protocol (NTP) resolves many authentication anomalies.
Policy Conflicts and Loop States
Occasionally, conflicting configuration profiles—such as conflicting Wi-Fi auto-join settings or overlapping VPN parameters—can cause a device to enter a loop state where it repeatedly drops and re-establishes network connections. Review the MDM console's device event logs to identify which specific profile triggered the conflict, remove the offending policy, and push an updated configuration.
Frequently Asked Questions
What is the difference between standard MDM and an MDM network?
Standard MDM focuses strictly on managing the software settings, applications, and security states of individual endpoints. An MDM network integrates this device management software directly with core network infrastructure—such as switches, firewalls, and NAC systems—allowing the network itself to dynamically enforce security compliance and control access based on real-time device health.
Can an MDM network track an employee's personal location on a BYOD device?
Most reputable MDM solutions configured for BYOD environments protect employee privacy by disabling geolocation tracking for personal partitions. Administrators can typically only view location data on fully owned corporate devices, while personal devices rely on containerization to secure work data without invading personal privacy.
How does an MDM network handle offline devices?
If a managed device goes offline (e.g., powered down or disconnected from the internet), it retains its last known compliance state within the network logs. Conditional access policies will automatically block the device from accessing sensitive cloud resources until it reconnects, checks in with the MDM server, and proves it remains fully compliant.
What happens to a device during a remote enterprise wipe?
A remote enterprise wipe removes all corporate applications, configuration profiles, data containers, and digital certificates from the device. On corporate-owned assets, it may trigger a full factory reset. On personal BYOD devices, it targets exclusively the corporate container, leaving personal photos, apps, and contacts completely untouched.
Do IoT devices require a specialized MDM network approach?
Yes. IoT devices often lack user interfaces, keyboards, or standard operating systems like iOS or Android. Consequently, managing them within an MDM network requires specialized device management protocols (such as MQTT or lightweight device management agents) and strict network segmentation to prevent lateral threats if an IoT sensor is compromised.
Conclusion and Next Actions
Deploying and maintaining an MDM network is a foundational step in securing modern, distributed enterprise environments. By bridging endpoint device management with dynamic network access controls, organizations eliminate blind spots and ensure that every connection meets strict compliance standards. To begin implementation, audit your current inventory of endpoints, evaluate your organization's compliance requirements, and consult with networking and security specialists to map out a seamless integration strategy.