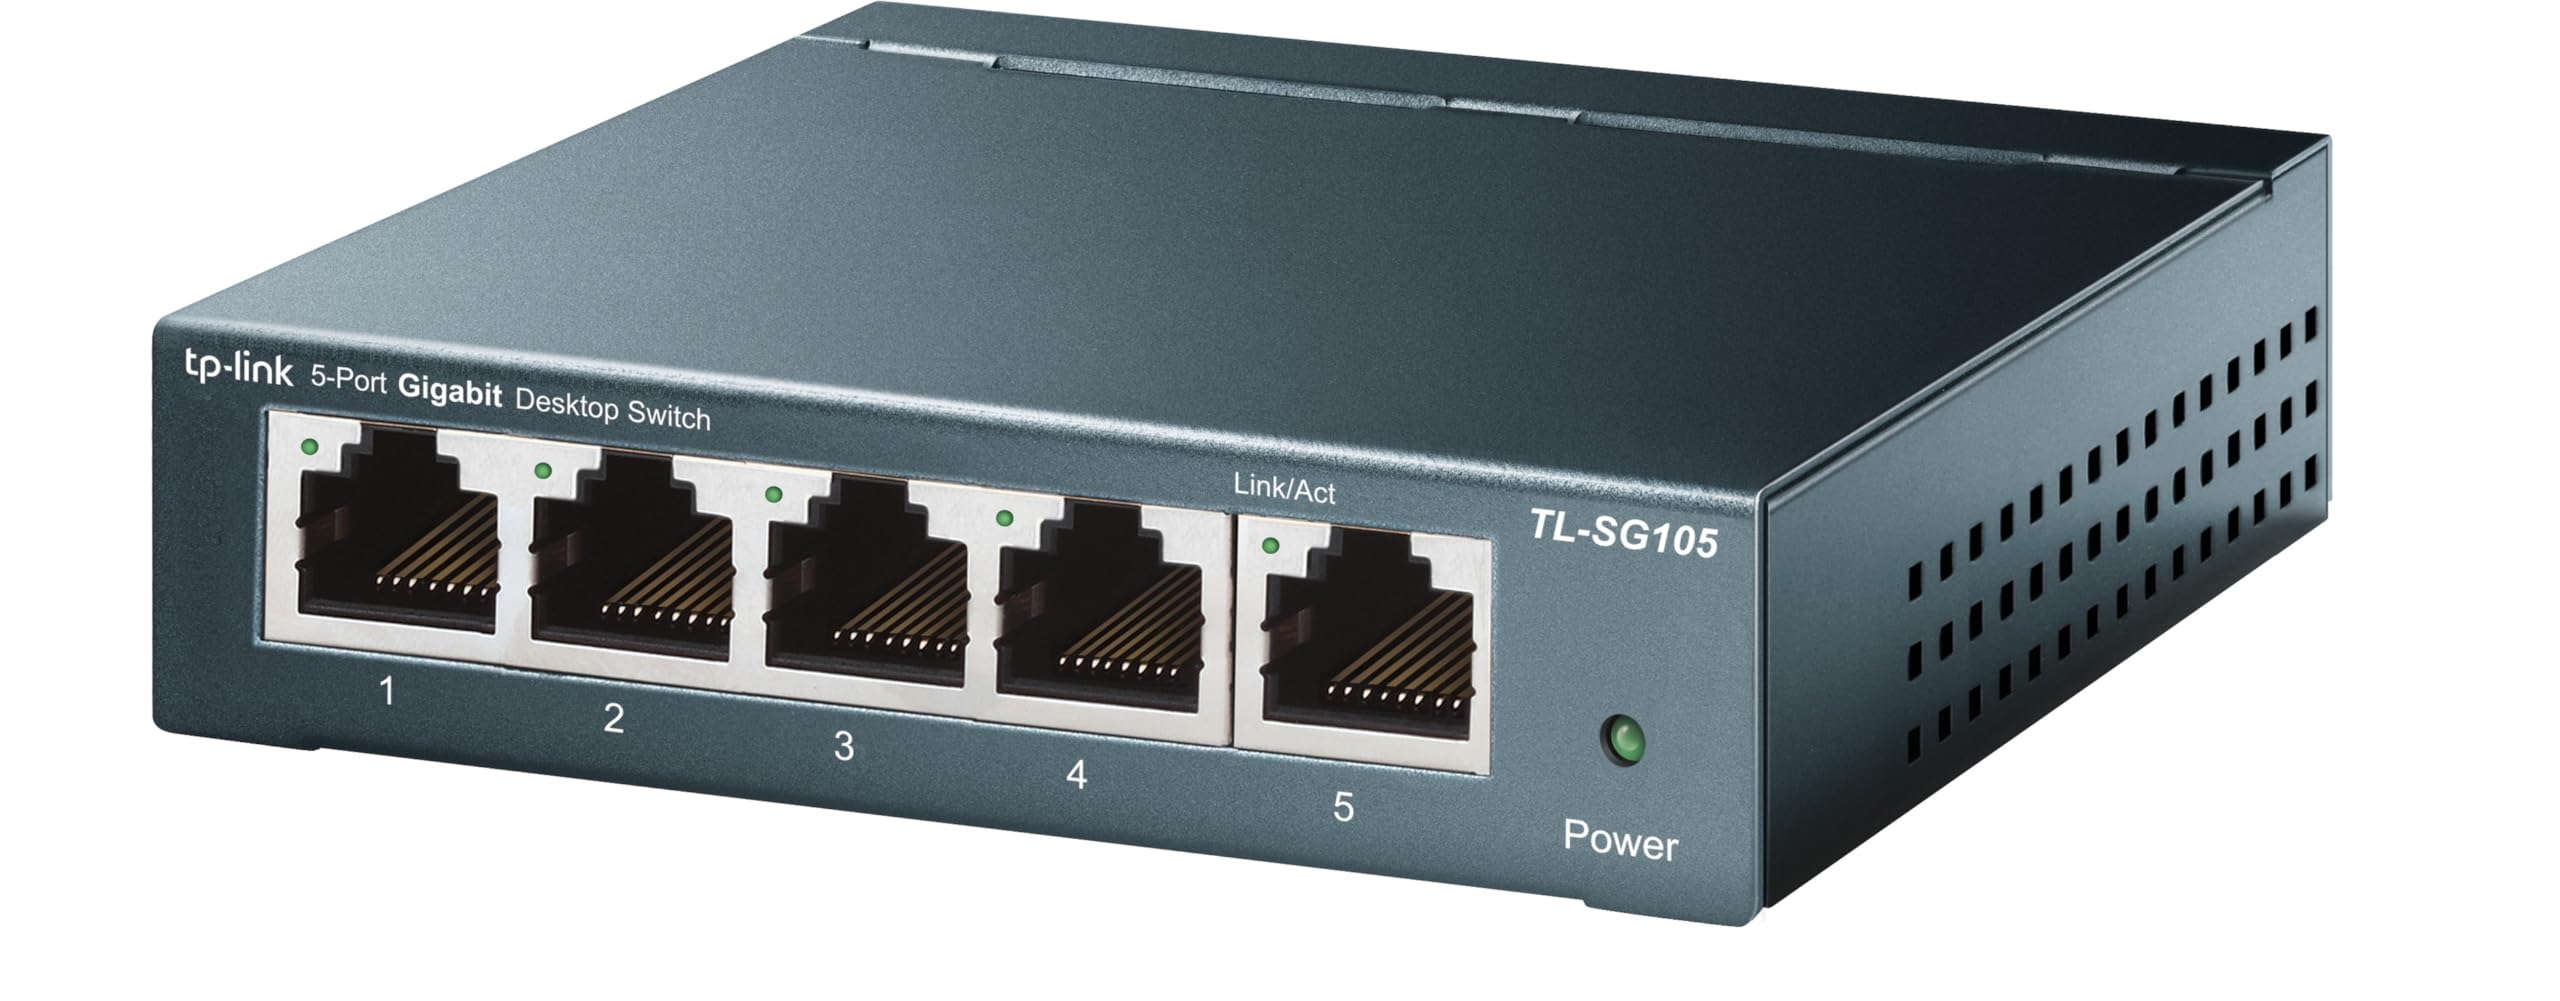
A networks hub serves as a centralized architectural point or digital environment where multiple network connections, data streams, and communication nodes converge to manage traffic efficiently. By consolidating administrative controls and routing pathways, a networks hub optimizes performance, enhances security monitoring, and simplifies infrastructure scalability across modern organizational ecosystems.
Introduction to Network Hubs and Centralized Architecture
In modern computing, data communication, and telecommunications, managing the sheer volume of traffic flowing between disparate endpoints requires strategic organization. A networks hub acts as a focal point where multiple devices, subnets, or external networks connect to exchange data. Historically, this term referred primarily to physical layer network hardware—such as multi-port Ethernet hubs that broadcast incoming data packets to all connected ports indiscriminately. However, the concept has evolved significantly. Today, a "networks hub" can describe physical hardware, enterprise-grade switching centers, software-defined networking (SDN) coordination points, or centralized digital platforms designed to manage complex interconnectivity.
Understanding the foundational architecture of a networks hub requires looking at how data travels and how bottlenecks are mitigated. When multiple devices attempt to communicate simultaneously, congestion can degrade performance. Modern network engineering addresses this through intelligent routing, segmentation, and centralized management interfaces. Whether deployed in an enterprise data center, a telecommunications exchange, or a cloud-based infrastructure, a well-structured networks hub reduces administrative overhead, minimizes latency, and provides a single pane of glass for monitoring uptime, bandwidth utilization, and security postures.
Historical Context and Evolution from Hardware to Software
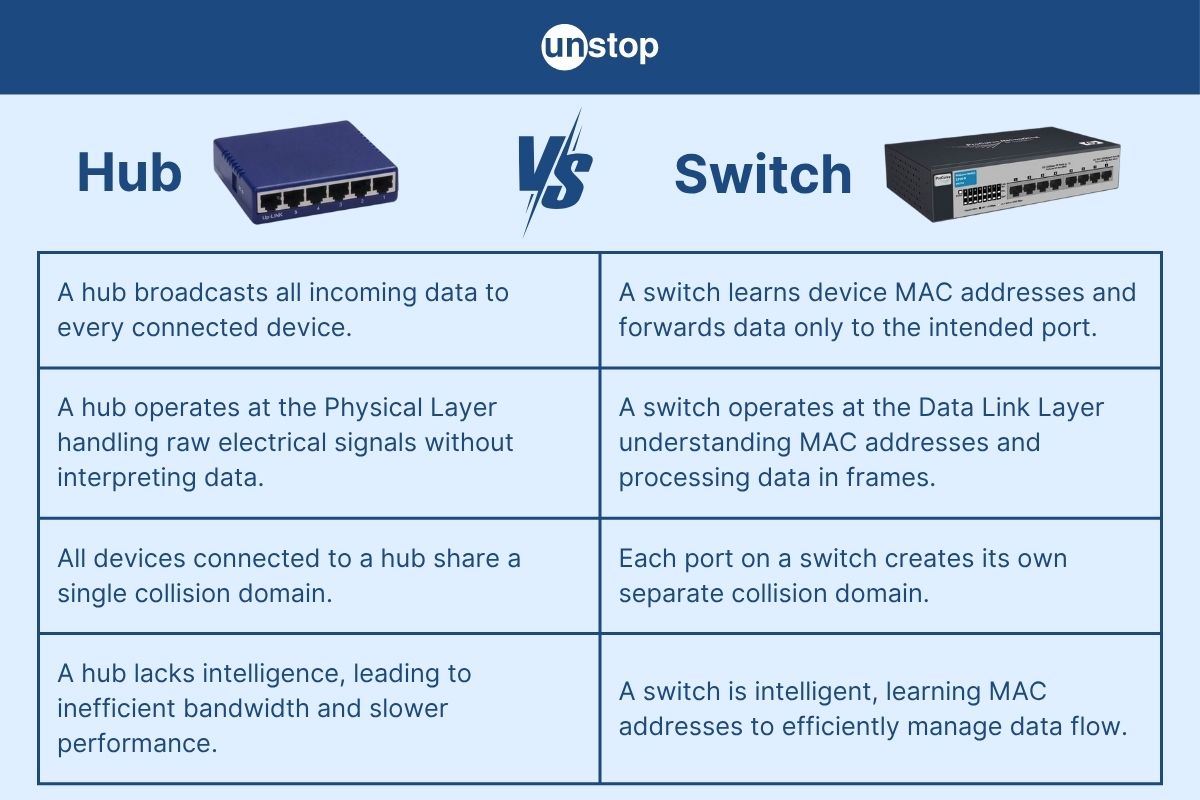
The evolution of the networks hub mirrors the broader transformation of information technology over the past several decades. In early local area network (LAN) implementations, passive or active physical hubs formed the backbone of shared-media networks. Operating at Layer 1 (the physical layer) of the Open Systems Interconnection (OSI) model, these traditional hardware hubs operated via a simple mechanism: any electrical signal or data packet received on one port was regenerated and broadcast out to all other ports.
While cost-effective and simple to deploy, physical Layer 1 hubs suffered from severe limitations:
- Collision Domains: All connected devices shared a single collision domain, meaning simultaneous data transmissions resulted in data collisions and required retransmission.
- Bandwidth Saturation: Total available bandwidth was divided among all active devices rather than dedicated to individual connections.
- Security Vulnerabilities: Because data was broadcast to every port, any device on the network could potentially capture traffic intended for other nodes, creating a high risk of eavesdropping.
As network demands escalated, Layer 2 network switches largely superseded traditional physical hubs by utilizing MAC (Media Access Control) addresses to forward frames only to the intended recipient port. Simultaneously, the definition of a "hub" expanded into the logical and software-defined realms. Modern network hubs often exist as virtualized control planes or centralized management dashboards—such as enterprise software-defined wide area network (SD-WAN) hubs or cloud-native interconnection points—that coordinate traffic across distributed multi-cloud and hybrid environments without relying on rudimentary physical broadcasting.
Core Functions and Architectural Components
To appreciate how a modern networks hub operates, it is essential to examine its core functional components and how they process traffic. Regardless of whether the hub is physical, virtual, or cloud-based, its primary responsibilities revolve around aggregation, translation, routing coordination, and security enforcement.
Traffic Aggregation and Distribution
At its core, a networks hub collects data streams originating from various edge devices, branch offices, or subnets and consolidates them into a unified traffic flow. Conversely, it receives outbound or return data and distributes it toward the correct destination addresses. In hardware implementations, this is handled by high-speed backplanes. In software-defined architectures, aggregation is managed through virtual overlay tunnels and centralized controllers that map network topologies dynamically.
Protocol Translation and Interoperability
Enterprise environments frequently utilize a mix of legacy systems and modern communication protocols. A sophisticated networks hub often incorporates translation mechanisms or integrates with gateways that convert data packets between disparate protocols—such as translating between Multiprotocol Label Switching (MPLS) circuits, broadband internet connections, cellular data streams, and internal Virtual Local Area Networks (VLANs).
Management and Control Plane Separation
Modern network hubs separate the data plane (the mechanisms that actually forward traffic) from the control plane (the decision-making logic that determines where traffic should go). By centralizing the control plane within a master hub or orchestration server, network administrators can push policy updates, Quality of Service (QoS) rules, and security patches globally across all connected edge devices instantly.
Types of Network Hubs in Modern Infrastructure
The terminology surrounding network hubs varies depending on the specific domain of information technology being discussed. Below is a breakdown of the primary categories of network hubs deployed in contemporary environments.
| Hub Type | Primary Layer / Medium | Core Function | Typical Use Case |
|---|---|---|---|
| Physical Ethernet Hub | Layer 1 (Physical) | Broadcasts data packets to all connected ports. | Obsolete for enterprise use; limited to legacy or isolated test labs. |
| SD-WAN Hub | Layer 3 / Overlay | Centralizes management and routing policies for distributed branch offices. | Enterprise multi-site wide area networking and cloud access optimization. |
| Cloud Interconnection Hub | Virtual / Software | Bridges disparate cloud providers, on-premises data centers, and SaaS platforms. | Multi-cloud enterprise architectures requiring low-latency private connectivity. |
| IoT Hub | Application / Transport | Aggregates, authenticates, and routes telemetry data from Internet of Things sensors. | Industrial automation, smart cities, and large-scale sensor deployments. |
Physical and Hardware-Based Hubs
As noted, traditional Layer 1 hubs are largely absent from modern production environments due to the ubiquitability of intelligent switches. However, specialized hardware hubs still exist in industrial settings (such as ruggedized industrial Ethernet hubs designed to withstand extreme temperatures and electrical interference) and specialized diagnostic tools like network tap hubs used for packet analysis.
Software-Defined and SD-WAN Hubs
In wide-area networking, the SD-WAN hub acts as the central aggregator for branch office connections. Instead of routing all traffic back through a costly corporate data center, an SD-WAN hub coordinates direct, secure internet breakouts while maintaining centralized visibility. It dynamically selects the optimal transport path—whether broadband, fiber, or 5G—based on real-time latency, jitter, and packet loss metrics.
Cloud and Virtual Hubs
Cloud service providers (such as Amazon Web Services with AWS Transit Gateway, Microsoft Azure with Virtual WAN, and Google Cloud with Network Connectivity Center) offer virtual network hubs. These cloud-native constructs eliminate the need to provision physical routing hardware. They allow administrators to connect hundreds of virtual private clouds (VPCs), virtual networks, and on-premises locations through a managed, highly available centralized hub.
Planning and Implementing a Networks Hub
Deploying a centralized network hub requires careful architectural planning, capacity forecasting, and security alignment. Whether implementing an enterprise SD-WAN hub or configuring a virtual cloud interconnection hub, organizations must follow a structured implementation methodology.
1. Requirements Gathering and Traffic Analysis
Before selecting hardware or cloud architecture, network engineers must analyze current and projected traffic flows. Key metrics to evaluate include:
- Bandwidth Demand: Peak and average data transfer rates across all connected nodes.
- Latency Tolerances: Sensitivity of applications (e.g., VoIP, video conferencing, financial trading algorithms) to delay.
- Geographic Distribution: Locations of branch offices, remote workers, data centers, and cloud regions.
2. High Availability and Redundancy Planning
A networks hub represents a single point of failure if proper redundancy is not engineered into the design. Enterprise deployments typically mandate redundant hub configurations—such as active-active or active-passive clustering across geographically diverse data centers or availability zones. This ensures that if one hub fails, traffic automatically reroutes without service interruption.
3. Security Integration and Access Control
Because a networks hub processes and aggregates massive volumes of organizational data, it represents a prime target for malicious actors. Implementation must include:
- Encryption: Mandatory use of IPsec or TLS tunnels for all traffic traversing the hub.
- Segmentation: Micro-segmentation to isolate sensitive financial or human resources traffic from general corporate internet browsing.
- Identity and Access Management (IAM): Strict authentication protocols for administrators accessing the hub management plane.
Performance Optimization and Troubleshooting
Once operational, a networks hub requires ongoing monitoring to maintain optimal performance. Network administrators rely on monitoring tools utilizing protocols such as Simple Network Management Protocol (SNMP), NetFlow, and sFlow to track bandwidth utilization, error rates, and dropped packets.
Common Operational Challenges
- Bandwidth Saturation: When aggregate traffic exceeds the hub's processing capacity or uplink bandwidth, queues fill up, leading to packet drops. Mitigation involves implementing robust Quality of Service (QoS) policies to prioritize mission-critical traffic over non-essential downloads.
- Bottlenecks in Software-Defined Controllers: In virtualized environments, insufficient CPU or memory allocation on the virtual hub appliance can cause control plane latency. Scaling up virtual resources resolves this constraint.
- Routing Loops: Misconfigured routing protocols (such as BGP or OSPF) can create loops where data packets bounce infinitely between nodes. Utilizing split-horizon rules and route poisoning prevents these issues.
Step-by-Step Troubleshooting Checklist
- Verify Physical or Virtual Status: Confirm that the underlying hardware or cloud instance is powered on and reporting healthy CPU and memory utilization metrics.
- Examine Interface Statistics: Check port or virtual interface error counters for cyclic redundancy check (CRC) errors, frame drops, or interface resets.
- Analyze Routing Tables: Inspect the hub's routing table to ensure valid paths exist for all destination subnets and that no stale routes are present.
- Test End-to-End Connectivity: Utilize diagnostic utilities such as
ping,traceroute, and packet capture tools (tcpdumpor Wireshark) to isolate where packets are being delayed or dropped.
Frequently Asked Questions
What is the difference between a traditional network hub and a network switch?
A traditional network hub operates at Layer 1 and broadcasts incoming data packets to all ports regardless of the destination, resulting in high collision rates and security risks. A network switch operates at Layer 2 (and often Layer 3), utilizing MAC or IP addresses to forward data exclusively to the specific port intended for the recipient, dramatically improving speed, security, and efficiency.
How does a cloud-based network hub differ from an on-premises hardware hub?
An on-premises hardware hub is a physical device installed in a rack within a local data center, requiring manual cabling and hardware maintenance. A cloud-based network hub is a virtualized service managed via software APIs provided by cloud vendors, allowing administrators to scale capacity instantly and connect distributed global resources without physical intervention.
Can a single networks hub handle multi-cloud environments?
Yes. Modern enterprise hubs, such as SD-WAN solutions and cloud transit gateways, are specifically designed to bridge multiple public cloud providers (e.g., AWS, Azure, Google Cloud) with on-premises data centers, providing a unified routing and security framework across disparate environments.
What security measures are necessary when deploying a centralized networks hub?
Essential security measures include enforcing end-to-end encryption (such as IPsec tunnels), implementing strict role-based access control (RBAC) for management interfaces, utilizing micro-segmentation to isolate critical workloads, and integrating intrusion detection and prevention systems (IDPS) to monitor traffic passing through the hub.
How do I prevent a networks hub from becoming a single point of failure?
To eliminate single points of failure, organizations should deploy redundant hub appliances in an active-active or active-passive cluster across separate physical data centers or cloud availability zones, combined with automated failover routing protocols.
Conclusion and Next Actions
A networks hub remains a cornerstone of efficient network design, whether implemented as an advanced SD-WAN controller, a virtual cloud interconnection point, or specialized routing hardware. By centralizing traffic aggregation, streamlining policy management, and enhancing security enforcement, organizations can overcome the complexities of modern multi-site and multi-cloud environments. To take the next step, conduct a thorough audit of your organization's current network topology, identify traffic bottlenecks, and evaluate whether transitioning to a centralized hub architecture can improve your operational resilience and scalability.