Operations Security (OPSEC) has evolved significantly as we navigate the 2026 threat landscape, shifting from a focus on static perimeter defense to a dynamic, intelligence-driven methodology. This guide provides an authoritative framework for protecting critical information and operational integrity against sophisticated adversaries who utilize automated reconnaissance and AI-augmented social engineering.
The 2026 Threat Paradigm and Information Security
In 2026, the primary threat to operational security is no longer just unauthorized access to a network; it is the synthesis of fragmented, publicly available data—often referred to as Open Source Intelligence (OSINT)—to build granular profiles of an organization's critical nodes. Attackers leverage generative AI to automate the discovery of human and technical vulnerabilities, making traditional security measures insufficient.
To maintain a robust OPSEC posture, organizations must adhere to the 2026 Critical Information List (CIL) methodology. This process requires identifying what data, if compromised, would be most damaging to mission success. By prioritizing these assets, resources are concentrated where they provide the highest defensive yield.
Core Pillars of Operational Security Management
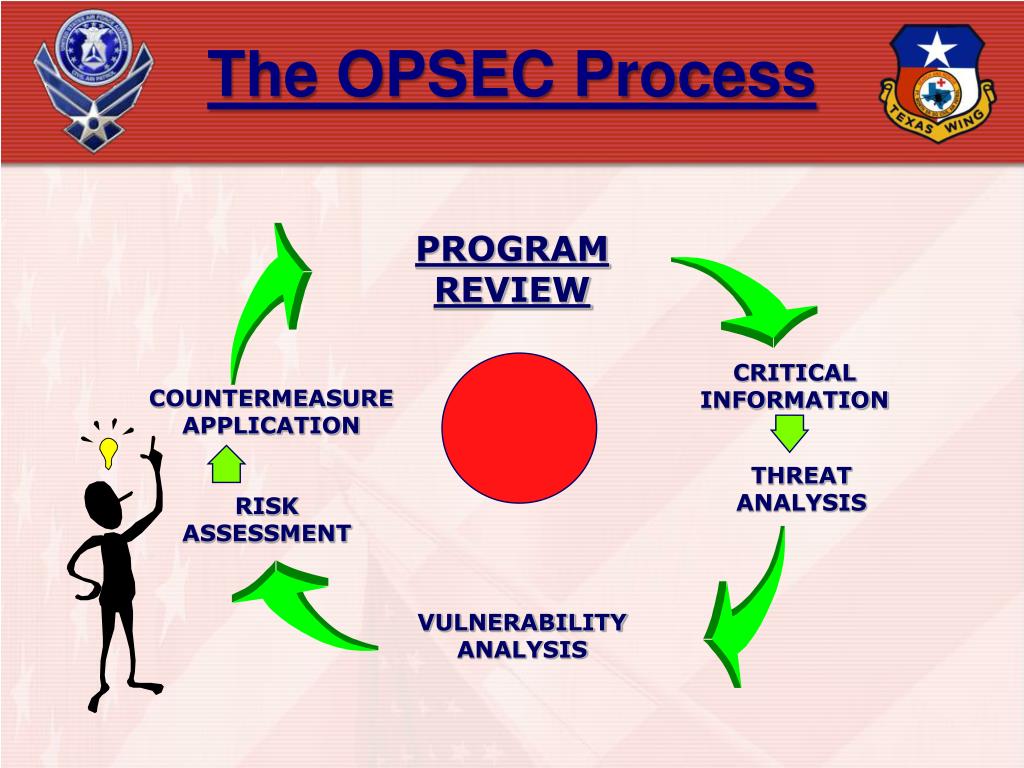
Effective OPSEC in 2026 relies on the integration of human behavior modification and advanced technical controls. The following pillars represent the standard for maintaining secrecy and operational integrity:
- Identification of Critical Information: Categorizing sensitive data that reveals intent, capabilities, and vulnerabilities.
- Threat Analysis: Evaluating the capabilities and intentions of potential adversaries using current 2026 threat intelligence data.
- Vulnerability Analysis: Assessing internal processes to identify where information leakage occurs, particularly through digital exhaust.
- Risk Assessment: Calculating the impact of potential exposure against the cost of countermeasures.
- Countermeasure Application: Implementing technical and procedural barriers to block information disclosure.
Comparative Analysis of Security Controls
Choosing the right framework for your specific operational environment is crucial. The table below outlines common security strategies and their effectiveness against modern 2026 attack vectors.
| Strategy | Primary Defense Mechanism | 2026 Effectiveness Rating | Implementation Difficulty |
|---|---|---|---|
| Zero Trust Architecture | Identity-based micro-segmentation | Exceptional | High |
| OSINT Masking | Reducing public data footprint | High | Moderate |
| Air-Gap Infrastructure | Physical isolation of critical systems | Absolute (for target assets) | Very High |
| AI-Driven Traffic Analysis | Behavioral anomaly detection | Moderate to High | High |
| Encryption at Rest/Transit | Standardized AES-256 and PQC | Essential (Minimum Baseline) | Low |
Practical Implementation of OPSEC Measures
Implementation must be treated as a continuous loop, not a one-time project. As we progress through 2026, the focus has shifted toward proactive information sanitization.
Digital Footprint Reduction
Reducing your organization’s exposure begins with strict control over what information is accessible to the public. Employees must be trained to recognize the "breadcrumb" effect, where seemingly harmless social media posts or professional updates provide attackers with enough context to craft highly personalized phishing attempts.
Technical Hardening Requirements
- Implement Post-Quantum Cryptography (PQC) standards for all long-term data storage.
- Transition to FIDO2-compliant hardware security keys, moving entirely away from SMS or app-based 2FA which are increasingly vulnerable to sophisticated man-in-the-middle attacks in 2026.
- Enforce strict metadata removal for all outgoing communications, including internal documentation and public-facing media.
Leadership Responsibility in OPSEC
Executive Oversight: Leadership must foster a culture where security is integrated into every workflow, not treated as an IT-only mandate. This involves formalizing OPSEC as a key performance indicator for all departments.
Continuous Verification: Regular red-teaming exercises in 2026 must involve full-spectrum simulations, testing not just technical defenses but also human responses to social engineering and information leakage.
Common Challenges and Mitigation Strategies
Organizations frequently struggle with balancing transparency with security. The "transparency paradox" suggests that the more an organization communicates, the more its security is jeopardized. Mitigation involves clear communication protocols that strictly limit information to a "need-to-know" basis.
- Insider Threat Mitigation: Utilize user and entity behavior analytics (UEBA) to identify shifts in patterns that might indicate compromised credentials or malicious intent.
- Supply Chain Security: In 2026, vetting third-party vendors is as important as internal hardening. Ensure all partners adhere to your internal OPSEC protocols.
- Information Sanitization: Establish a protocol for wiping meta-tags and geolocation data from all external communications.
Frequently Asked Questions regarding 2026 OPSEC
What is the most critical change in OPSEC for 2026? The most critical change is the mandatory integration of AI-resistant identification protocols and the formalization of OSINT reduction strategies to counter automated threat reconnaissance.
Does my organization need to be air-gapped to be secure? No, air-gapping is reserved for high-consequence assets. For most organizations, robust micro-segmentation and Zero Trust Architecture provide sufficient protection against modern threats.
How does OSINT affect my day-to-day operations? Adversaries use OSINT to map your internal structure, finding weak points in your team or software stack. Sanitizing public communications and minimizing metadata leakage are now essential daily hygiene tasks.
What is the minimum level of encryption required in 2026? As of 2026, the industry standard is moving toward post-quantum resistant encryption (PQC) for all data at rest and in transit, specifically replacing older RSA standards with lattice-based or hash-based alternatives.
Can OPSEC be fully automated? While tools can automate many technical aspects, OPSEC is fundamentally a behavioral science. It requires human judgment to determine the sensitivity of information and the context in which it is shared.
Strengthening Your Security Posture
Maintaining good OPSEC in 2026 requires moving past traditional "check-box" compliance. It demands a holistic, risk-based approach that prioritizes data minimization and identity assurance. If your organization is prepared to evaluate its vulnerability to current intelligence-gathering techniques, begin by conducting a comprehensive audit of your public-facing information and internal data handling workflows. Consult with a security architect to align your infrastructure with 2026 standards and ensure your team is trained to recognize the nuances of the modern threat landscape.