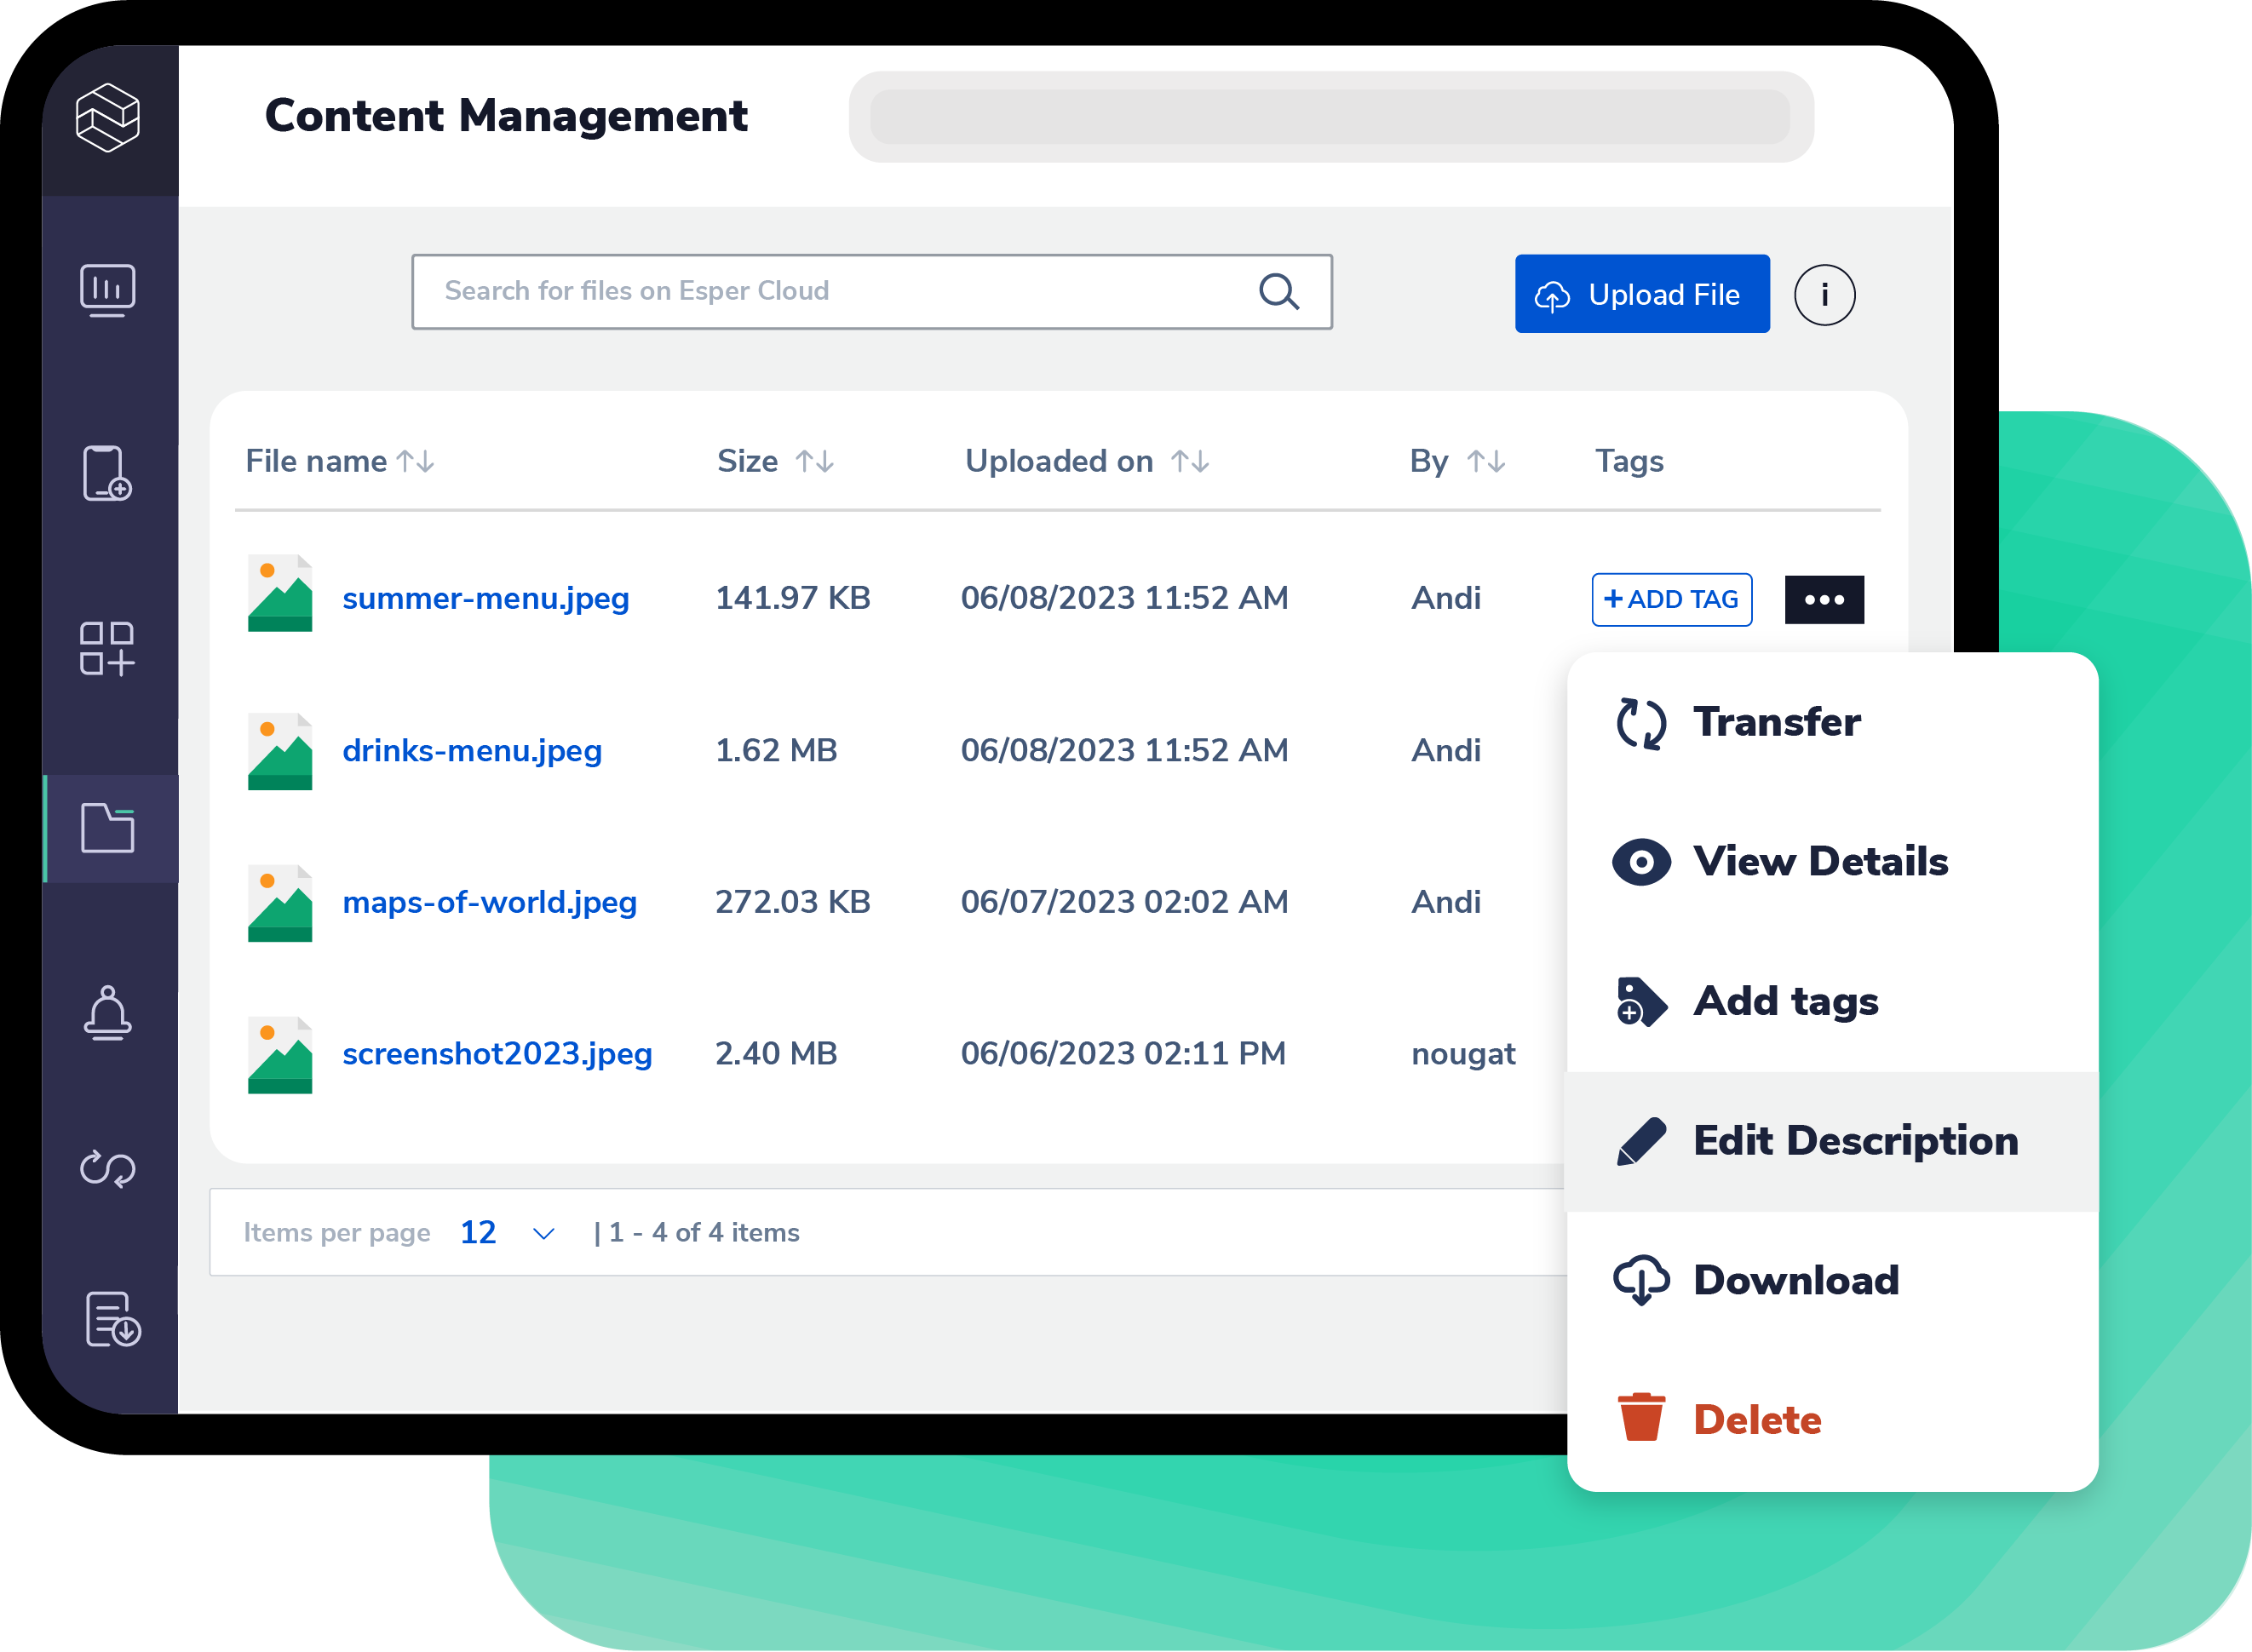
Mobile Device Management (MDM) software is a centralized administrative solution that enables organizations to secure, monitor, and manage employee smartphones, tablets, laptops, and specialized endpoints across various operating systems from a single console.
Modern enterprise environments no longer rely solely on static desktop computers locked inside an office perimeter. Instead, organizations support hybrid workforces, remote employees, and dynamic operational workflows utilizing a vast array of devices. This decentralization creates complex challenges regarding data security, corporate compliance, and application management. MDM software addresses these vulnerabilities by allowing IT administrators to enforce security policies, push software updates, configure network settings, and remotely wipe compromised or lost hardware. By acting as a bridge between corporate infrastructure and end-user endpoints, MDM solutions maintain organizational productivity while mitigating the risks associated with unauthorized access and data exfiltration.
Core Architecture and Operational Mechanics
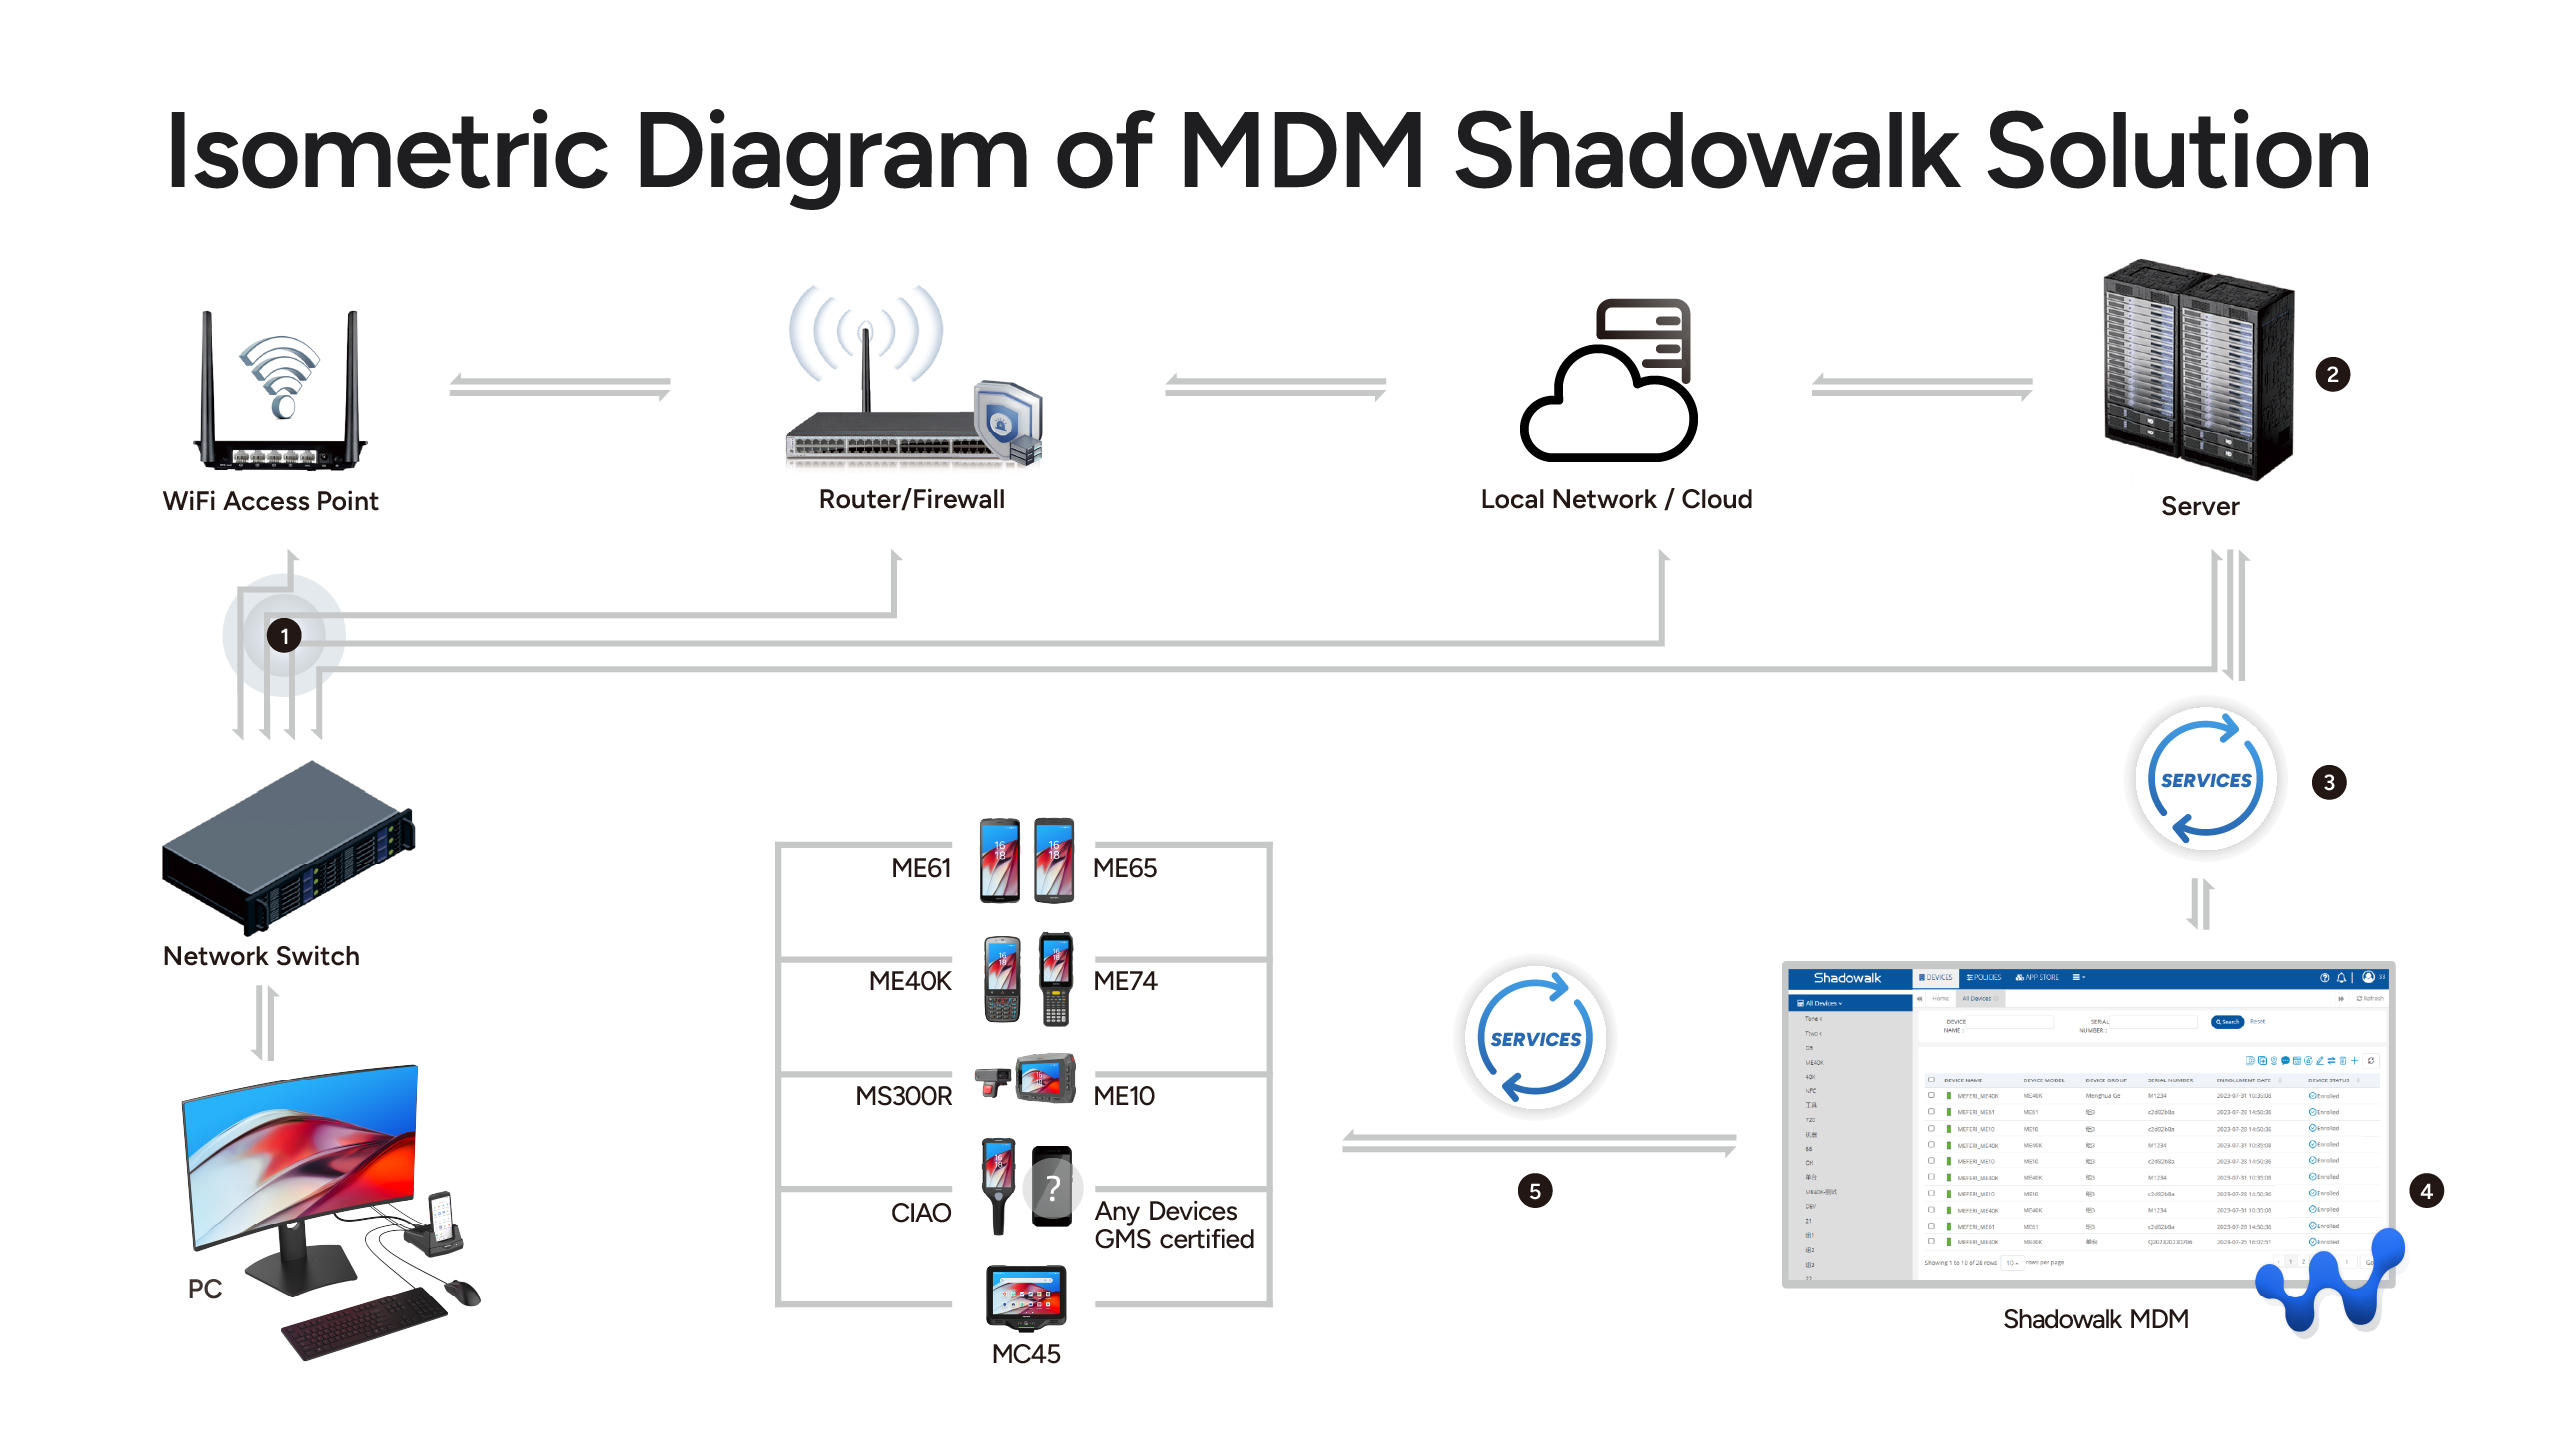
To understand how MDM software functions, one must examine its underlying architecture, which typically relies on a client-server model. The administrative component resides either on-premises or, more commonly, within a cloud-hosted infrastructure managed by the vendor. This server communicates securely with agent applications or native management frameworks embedded within the operating systems of managed endpoints.
Enrollment and Provisioning
The lifecycle of an enterprise device within an MDM ecosystem begins with enrollment. Administrators can onboard devices using several automated mechanisms, ensuring that configuration profiles apply immediately upon initial setup.
- Zero-Touch Deployment: Platforms such as Apple Business Manager, Android Enterprise, and Windows Autopilot allow organizations to purchase hardware and ship it directly to end users. Upon powering on and connecting to the internet, the device automatically recognizes its corporate affiliation, downloads the necessary configuration profiles, and enrolls in the MDM software without manual IT intervention.
- User-Initiated Enrollment: For Bring Your Own Device (BYOD) programs, users typically download an agent application from an app store or navigate to an enrollment portal, authenticating with corporate credentials to register their personal hardware.
Management Protocols and Over-The-Air (OTA) Commands
Once enrolled, the MDM server communicates with endpoints using secure over-the-air protocols. Administrators can issue immediate commands or schedule recurring check-ins. Common OTA commands include forcing screen lock updates, locating missing hardware via GPS, revoking enterprise application certificates, and initiating selective or full factory resets. The operating system's native management application programming interfaces (APIs)—such as the Apple MDM protocol or Android Management API—execute these instructions at a system level, ensuring users cannot easily bypass administrative controls.
Key Features and Capabilities of MDM Solutions
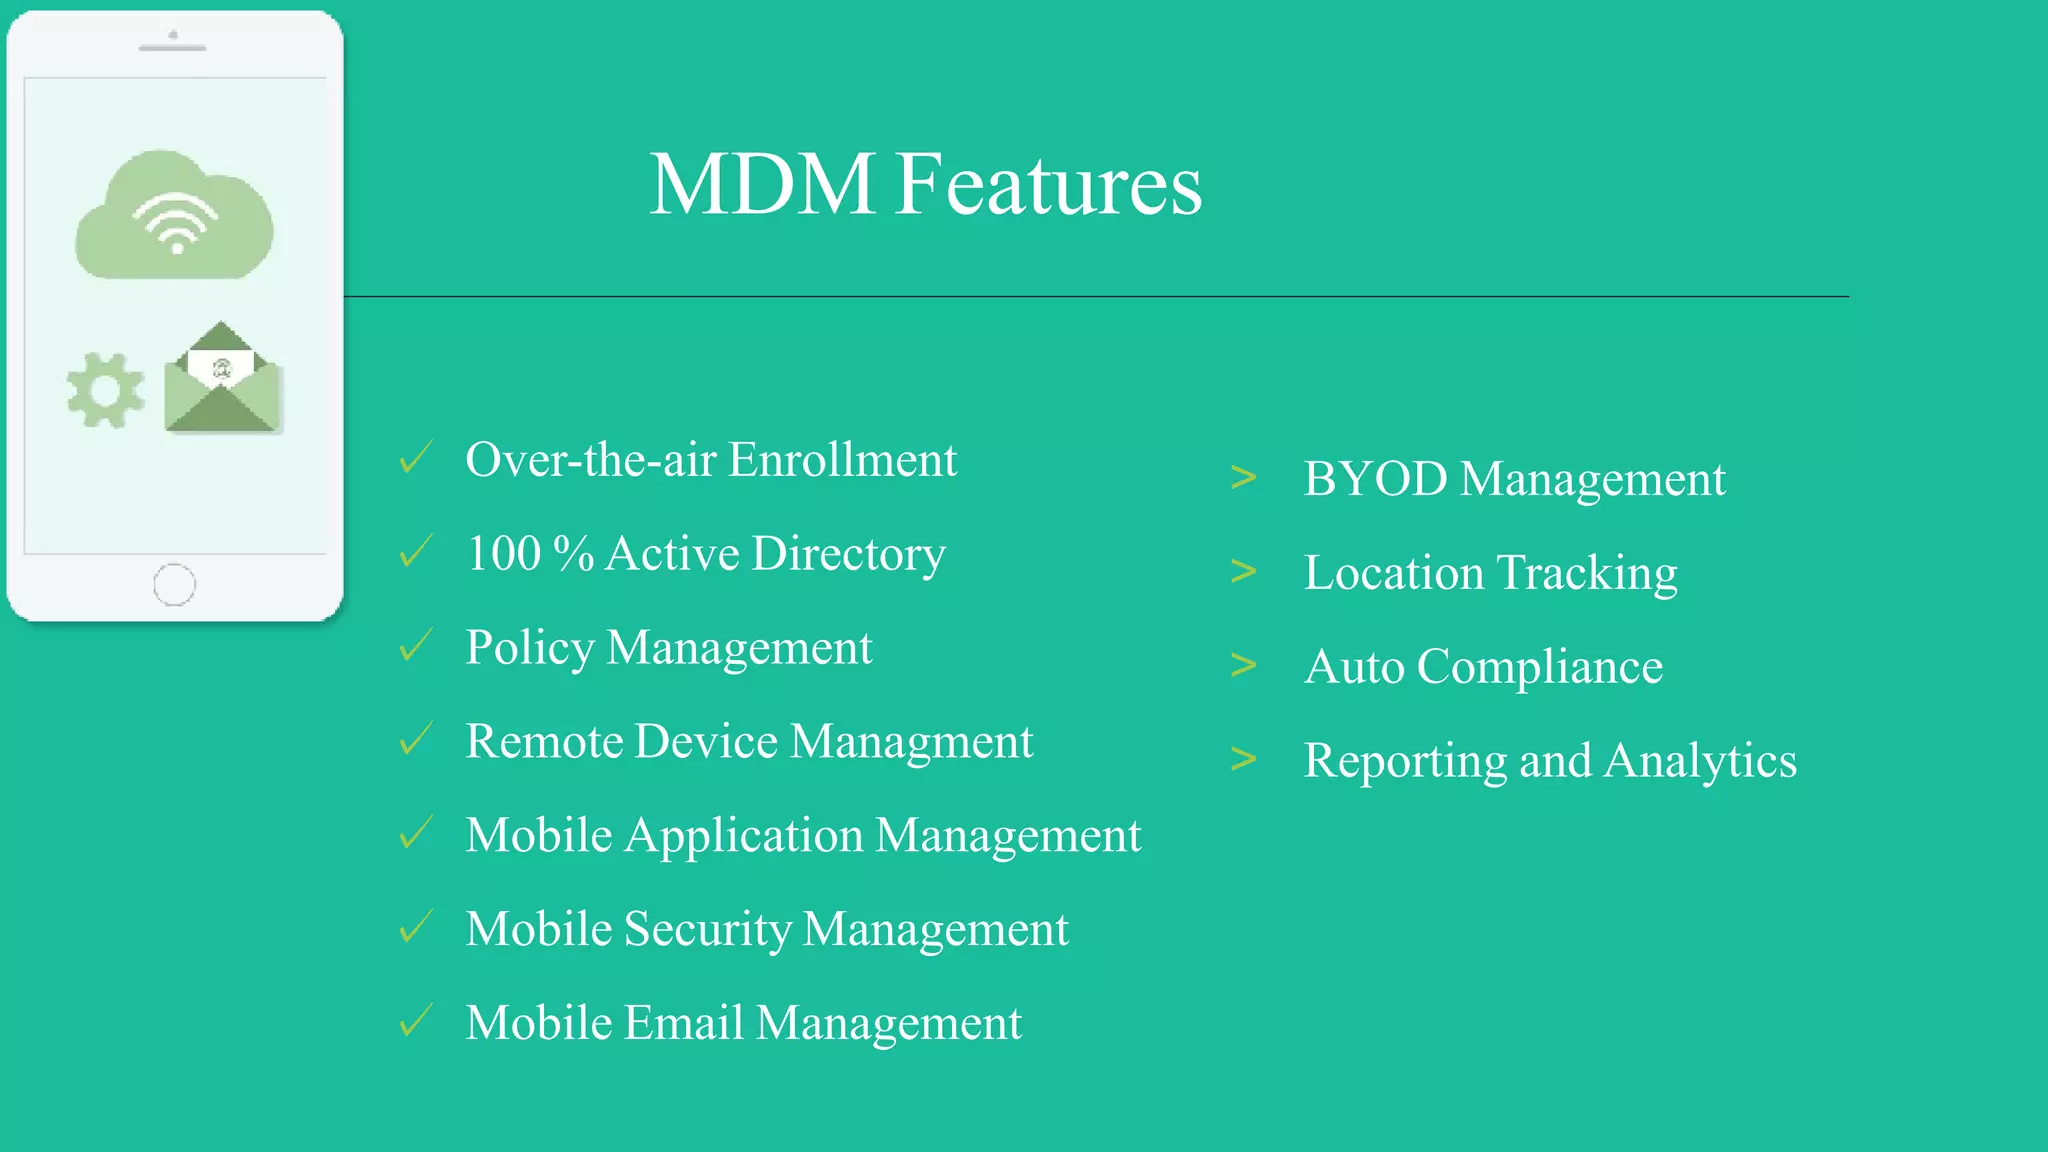
Enterprise-grade MDM platforms offer an extensive suite of features designed to address distinct administrative and security requirements. These capabilities generally fall into security enforcement, application lifecycle management, and asset tracking.
Security and Policy Enforcement
Enforcing robust security baselines is the primary driver for deploying MDM software. Administrators can configure and lock down device settings to prevent data leakage. Key enforcement mechanisms include:
- Passcode Policies: Requiring complex alphanumeric passwords, setting automatic screen timeout intervals, and defining maximum failed login attempts before triggering a wipe.
- Encryption Management: Mandating full-disk encryption (such as FileVault for macOS or BitLocker for Windows) and verifying that hardware-based security chips like Trusted Platform Modules (TPMs) are active.
- Peripheral Restrictions: Disabling built-in cameras, Bluetooth connections, USB file transfers, or screen-capture capabilities to safeguard sensitive environments or regulated data zones.
Application Management (MAM)
While MDM focuses on the entire device, Mobile Application Management (MAM) modules within MDM platforms specialize in software deployment and containerization. Administrators can silently push enterprise applications, update existing software packages, and configure app-specific settings without user intervention. Furthermore, containerization allows organizations to isolate corporate data from personal data on BYOD devices, creating an encrypted workspace where corporate emails, documents, and messaging apps reside separately from personal photos and social media.
Network and Connectivity Configuration
Managing how endpoints connect to corporate resources is critical for maintaining security perimeters. MDM software allows administrators to automatically provision Wi-Fi credentials, configure Virtual Private Network (VPN) profiles, and install enterprise certificates. This automation ensures that devices connect exclusively to approved, secure networks and prevents users from misconfiguring network settings that could expose traffic to interception.
Comparison of Operating System Management Paradigms
Managing devices through MDM software varies significantly depending on the operating system. Each ecosystem provides distinct APIs, security models, and administrative controls.
| Operating System | Primary Enrollment Frameworks | Native Containerization Support | Key Management Strengths | Primary Limitations |
|---|---|---|---|---|
| Android Enterprise | Android Zero Touch, QR Code, NFC | Work Profile (Profile Owner) | Granular separation of personal and corporate data; highly flexible OEM configuration APIs. | Fragmentation across hardware manufacturers and varying OS update cycles. |
| iOS / iPadOS | Apple Business Manager, Automated Device Enrollment (ADE) | Managed Apple IDs, User Enrollment | Deep system-level integration; highly reliable push notification service (APNs). | Strict adherence to Apple's proprietary frameworks and provisioning profiles. |
| Windows 10 / 11 | Windows Autopilot, Azure AD / Entra ID Join | Windows Information Protection (WIP), Enterprise State Roaming | Comprehensive desktop management parity; robust group policy transition paths. | Complex legacy application packaging requirements for non-MSI software. |
| macOS | Apple Business Manager, Automated Device Enrollment | FileVault management, Sandbox restrictions | Native management frameworks that mirror iOS security architectures. | Resistance among traditional Mac power users accustomed to unrestricted local admin rights. |
Deployment Models: BYOD vs. Corporate-Owned
Organizations must carefully evaluate their hardware provisioning strategy before selecting and configuring MDM software. The two primary paradigms—Bring Your Own Device (BYOD) and Corporate-Owned, Personally Enabled (COPE)—dictate how strictly administrators can manage privacy and control.
Bring Your Own Device (BYOD)
In a BYOD model, employees utilize personal smartphones, tablets, or laptops for work tasks. This approach reduces hardware acquisition costs and increases user satisfaction by allowing individuals to work on familiar hardware. However, it introduces significant privacy and security challenges. MDM software in a BYOD environment must strictly respect user privacy. Administrators deploy containerized work profiles that manage corporate data exclusively. They cannot view personal text messages, browse personal photos, or track personal location data outside of corporate hours. If an employee leaves the company, the MDM administrator executes a selective wipe, removing only the corporate container and its associated data while leaving personal files intact.
Corporate-Owned Hardware
Corporate-owned deployment models grant IT departments absolute control over the device lifecycle. Whether designated for single-use functions (such as a retail kiosk or warehouse inventory scanner) or general employee use (COPE), these devices are fully managed. Administrators can restrict installation of unauthorized software, track precise geolocation coordinates, enforce continuous compliance monitoring, and execute complete factory resets if the hardware is lost, stolen, or decommissioned.
Compliance, Privacy, and Regulatory Considerations
Deploying MDM software introduces complex legal and ethical obligations, particularly regarding employee privacy and data protection regulations such as the General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), and industry-specific frameworks like HIPAA.
Administrators must transparently communicate what data the MDM software collects and monitors. While tracking device health, battery levels, and operating system versions is standard, monitoring user web traffic, keystrokes, or real-time location can violate privacy laws if implemented without explicit consent or a legitimate operational justification. Organizations should establish clear internal policies outlining the scope of MDM monitoring, ensure encryption protocols comply with regulatory standards, and restrict administrative access to authorized personnel via Role-Based Access Control (RBAC).
Common Implementation Mistakes and Troubleshooting
Organizations transitioning to an MDM-managed environment frequently encounter operational hurdles that can disrupt workflows if not addressed proactively.
- Failing to Define Policy Scopes Early: Applying overly restrictive policies—such as disabling Bluetooth or cameras universally—can paralyze specific departments like marketing or field sales. Administrators should segment users into dynamic groups based on job roles rather than applying a single, monolithic policy to the entire enterprise.
- Neglecting End-User Communication: Sudden enrollment prompts or unexpected device locks often cause user friction and resistance. Clear communication explaining why the MDM software is installed, what privacy safeguards are in place, and who to contact for support significantly improves adoption rates.
- Overlooking Certificate Expirations: MDM platforms rely heavily on SSL certificates, push notification certificates (such as the Apple Push Certificate), and SCEP/NDES enrollment certificates. If a push certificate expires, communication with all enrolled endpoints halts immediately until renewed, cutting off remote management capabilities.
- Inadequate Testing of OS Updates: Major operating system updates released by Apple, Google, or Microsoft can deprecate existing MDM APIs or break custom configuration profiles. Administrators should leverage testing environments and staging groups to validate OS updates before pushing them to production fleets.
Selecting the Right MDM Solution
Choosing an appropriate MDM platform requires a comprehensive assessment of organizational requirements, existing infrastructure, budget constraints, and technical expertise. Key evaluation criteria include:
- Ecosystem Compatibility: Ensure the platform natively supports all operating systems utilized within the organization (iOS, Android, Windows, macOS, ChromeOS, and Linux).
- Scalability and Hosting: Determine whether a cloud-hosted (SaaS) or on-premises deployment model aligns with corporate IT infrastructure and security compliance mandates.
- Integration Capabilities: Verify that the MDM solution integrates smoothly with existing directory services (such as Microsoft Entra ID, Okta, or Google Workspace), security information and event management (SIEM) tools, and IT service management (ITSM) ticketing systems.
- Administrative Usability: Evaluate the administrative console interface to ensure reporting, policy creation, and remote troubleshooting workflows are intuitive and efficient for the IT support team.
Frequently Asked Questions
Can MDM software access my personal photos and text messages on a BYOD device?
No, when configured correctly for a BYOD environment using containerization (such as Android Work Profile or Apple User Enrollment), MDM software operates strictly within a segregated corporate partition. The administrator cannot view personal photos, personal emails, text messages, browsing history, or social media activity.
What happens to a corporate device if it is lost or stolen?
If a device is lost or stolen, an administrator can log into the MDM console and issue a remote lock command to prevent unauthorized physical access. If recovery is unlikely, the administrator can initiate a remote wipe command, which instantly deletes all corporate data or performs a complete factory reset, restoring the hardware to its original default state.
Does MDM software drain device battery or slow down performance?
Modern MDM agents are designed to run lightweight background processes with minimal resource consumption. While routine check-ins, security telemetry reporting, and location updates consume nominal battery power, the impact on everyday device performance and battery longevity is generally negligible unless configured with excessively aggressive polling frequencies.
Can MDM software be uninstalled by the end user?
On corporate-owned devices, the MDM profile is locked and protected by system-level permissions, preventing users from removing the management software. On BYOD devices, users retain the right to remove the MDM profile; however, doing so automatically revokes access to corporate email, internal networks, and enterprise applications associated with that device.
How does MDM differ from Unified Endpoint Management (UEM)?
MDM historically focused on mobile devices such as smartphones and tablets. Unified Endpoint Management (UEM) is the evolutionary successor to MDM, expanding centralized control to encompass traditional desktops, laptops, ruggedized hardware, Internet of Things (IoT) devices, and wearables from a single administrative pane of glass.
Next Actions and Implementation Strategy
To successfully implement MDM software within your organization, begin by conducting a comprehensive inventory of all endpoints currently in use, categorized by operating system and ownership model (corporate vs. personal). Next, define clear security baselines and compliance requirements in collaboration with legal and executive stakeholders. Conduct a proof-of-concept (PoC) pilot with a small, representative group of users to test enrollment workflows, policy enforcement, and application deployment before initiating a full enterprise-wide rollout.