The term "web criminal" refers to individuals, organized syndicates, or state-sponsored groups that use the internet, digital infrastructure, and computing systems to commit illicit acts for financial gain, espionage, or disruption. These malicious actors operate across complex underground economies, exploiting vulnerabilities in software, human psychology, and network architectures to perpetrate fraud, extort organizations, and steal sensitive data.
The Anatomy of Modern Cybercrime: Defining the Web Criminal
Understanding the modern web criminal requires looking past the cinematic cliché of the lone teenager hacking into corporate mainframes from a basement. Today’s cybercrime landscape is dominated by highly specialized, industrialized operations that function much like traditional corporations. These ecosystems feature distinct divisions of labor, including software developers, initial access brokers, money launderers, and customer support desks that assist victims in paying ransoms.
The primary driver for the vast majority of web criminals is financial monetization. Cybercrime-as-a-Service (CaaS) has democratized illicit digital operations, allowing individuals with minimal technical skills to purchase turnkey malware suites, phishing kits, and rented botnets on illicit dark web marketplaces. Consequently, the barrier to entry for committing digital offenses has dropped dramatically, leading to a massive surge in the volume and frequency of attacks globally.
To understand how these threat actors operate, security professionals categorize them based on their motivations, funding, and organizational structure. The table below outlines the primary classifications of digital threat actors:
| Threat Actor Type | Primary Motivation | Typical Target | Technical Sophistication | Funding Source |
|---|---|---|---|---|
| Cybercrime Syndicates | Financial Profit | Businesses, Financial Institutions, Consumers | High to Advanced | Self-funded via illicit activities |
| State-Sponsored Groups | Espionage, Sabotage, Geopolitical Advantage | Governments, Critical Infrastructure, Defense Contractors | Extremely High | Nation-state governments |
| Hacktivists | Ideology, Political Statement, Disruption | Government Portals, Corporations, Public Figures | Low to Moderate | Donations, Crowdfunding |
| Script Kiddies | Notoriety, Boredom, Minor Vandalism | Vulnerable Websites, Gaming Servers | Low | Self-funded |
| Insider Threats | Retaliation, Financial Gain, Espionage | Employer Databases, Intellectual Property | Varies | Internal access |
Common Methodologies and Vectors Employed by Web Criminals
Web criminals rely on a diverse toolkit to breach perimeters, compromise data, and maintain persistence within a target environment. Rather than relying on a single exploit, sophisticated attacks often chain multiple techniques together, moving laterally across a network until they achieve their objective.
Social Engineering and Phishing
Human error remains the most reliable vector for digital compromise. Phishing involves sending deceptive communications—usually via email, SMS, or messaging platforms—designed to trick recipients into revealing sensitive credentials, installing malware, or authorizing fraudulent wire transfers.
Advanced variants include spear-phishing, which targets specific high-profile individuals within an organization, and Business Email Compromise (BEC), where criminals impersonate executives or vendors to divert corporate funds. These techniques bypass technical security controls by manipulating human trust, urgency, and fear.
Exploit Kits and Vulnerability Exploitation
When targeting public-facing web applications or enterprise infrastructure, web criminals actively scan for unpatched software vulnerabilities. Automated tools continuously probe the internet for known security flaws (tracked via Common Vulnerabilities and Exposures, or CVEs).
Once a vulnerable system is identified, attackers deploy exploit kits to execute arbitrary code, escalate privileges, and establish a foothold. This highlights the critical importance of rigorous patch management and continuous vulnerability assessments across all digital assets.
Ransomware and Extortion Operations
Ransomware has evolved from simple screen-locking software into a sophisticated multi-stage extortion mechanism. Modern ransomware groups infiltrate a network, exfiltrate sensitive intellectual property or customer data, and then encrypt operational files.
Web criminals then demand a ransom—typically payable in privacy-focused cryptocurrencies like Monero or Bitcoin—threatening to publish or sell the stolen data if the victim refuses to pay. This double-extortion model increases the pressure on organizations, as system backups alone no longer mitigate the risk of data exposure.
The Underground Economy: How Web Criminals Monetize Crime
The underground digital economy operates with surprising efficiency, featuring specialized forums, escrow services, and reputation ratings for cybercrime vendors. Understanding this marketplace illuminates how web criminals sustain and scale their operations.
Initial Access Brokers
An entire sub-sector of the cybercrime economy is dedicated solely to breaching networks and selling the access credentials to other criminal groups. These "Initial Access Brokers" (IABs) scan for exposed Remote Desktop Protocol (RDP) ports, VPN vulnerabilities, or compromised employee credentials. Once they successfully infiltrate a network, they package this access and auction it to ransomware gangs or state-sponsored actors, streamlining the attack lifecycle.
Malware-as-a-Service and Cryptojacking
Much like legitimate software companies offer Software-as-a-Service (SaaS), web criminals rent out malware variants under subscription models. Ransomware-as-a-Service (RaaS) allows affiliate hackers to deploy sophisticated encryption tools in exchange for a percentage of the extorted ransom, while the core developers maintain the infrastructure and decryption mechanisms.
Similarly, cryptojacking involves secretly installing cryptocurrency-mining scripts onto compromised computers or cloud environments, siphoning computing power and electricity from unsuspecting victims to generate digital currency for the criminal.
Defensive Strategies: Protecting Systems Against Web Criminals
Mitigating the threat posed by web criminals requires a defense-in-depth strategy that assumes perimeter breaches are inevitable. Organizations and individuals must implement layered security controls to detect, contain, and remediate threats before they result in catastrophic damage.
Identity and Access Management (IAM)
Because web criminals heavily rely on compromised credentials, securing access points is paramount. Organizations should enforce Multi-Factor Authentication (MFA) across all corporate systems, email accounts, and remote access gateways. Transitioning toward phishing-resistant MFA methods—such as hardware security keys (FIDO2/WebAuthn)—significantly reduces the risk of credential-based attacks.
Furthermore, adhering to the principle of least privilege ensures that users and applications only possess the minimum access necessary to perform their specific functions. This limits lateral movement if an account is compromised.
Employee Security Awareness Training
Given the prevalence of social engineering, regular and engaging security awareness training is essential. Organizations should conduct simulated phishing campaigns to test employee vigilance and educate staff on how to identify suspicious communications, verify unusual requests through out-of-band channels, and report anomalies to security teams immediately.
Continuous Monitoring and Incident Response
Visibility into network traffic, endpoint activity, and cloud infrastructure allows security teams to spot anomalous behavior early in the attack chain. Endpoint Detection and Response (EDR) and Extended Detection and Response (XDR) tools provide real-time telemetry, enabling automated containment of infected devices. Having a well-documented and regularly tested Incident Response (IR) plan ensures that an organization can respond swiftly and methodically if a breach occurs.
Frequently Asked Questions
What motivates web criminals to target small businesses?
Small and medium-sized businesses (SMBs) are frequently targeted because they often lack the robust security budgets and dedicated IT security staff found in large enterprises. Web criminals view SMBs as "low-hanging fruit" that can be easily compromised and extorted for moderate ransoms, or used as stepping stones to infiltrate larger supply-chain partners.
How do law enforcement agencies track down web criminals?
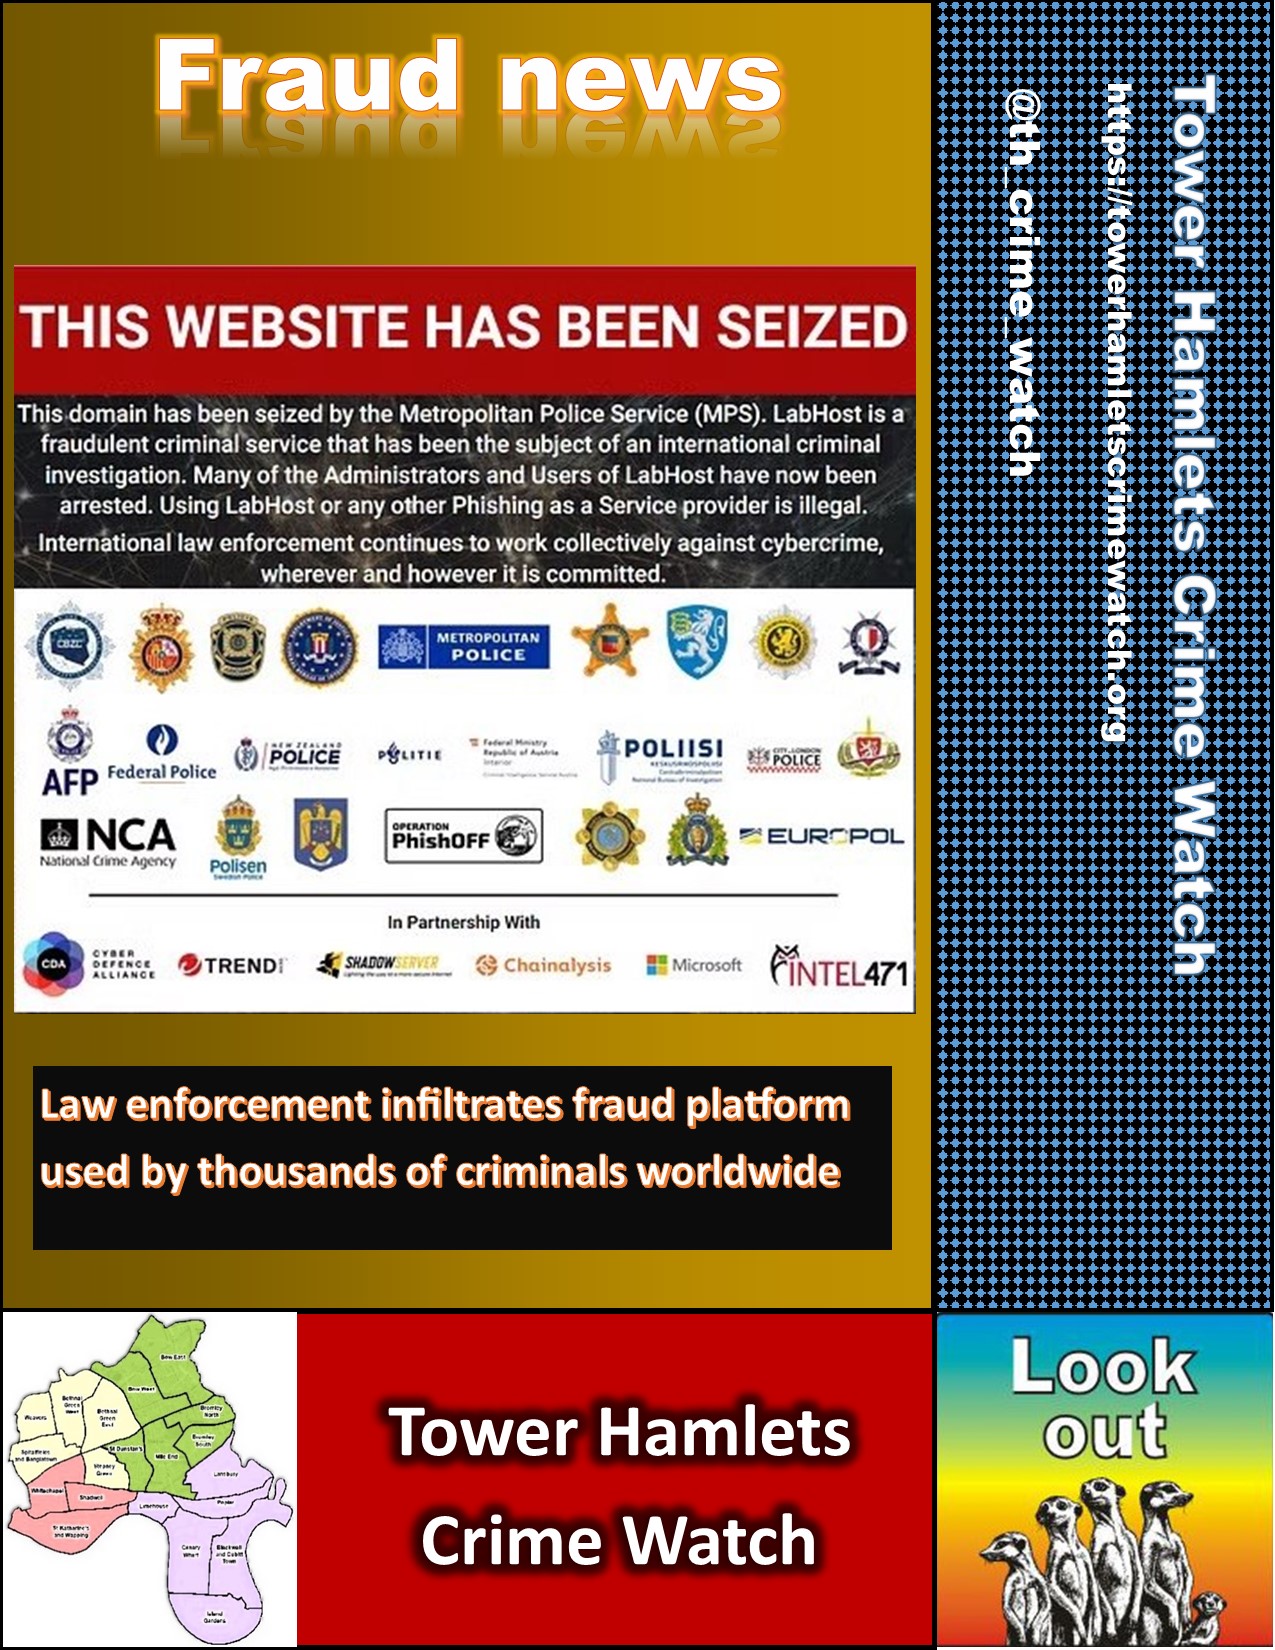
Law enforcement agencies, such as Europol, the FBI, and national cyber units, track web criminals by analyzing blockchain transactions, seizing underground server infrastructure, deploying undercover agents into dark web forums, and collaborating with private cybersecurity firms to analyze malware signatures and attribution markers.
What is the difference between a hacktivist and a cybercriminal?
While both engage in unauthorized digital intrusions, their primary objectives differ. Cybercriminals are driven primarily by financial gain or espionage. Hacktivists are motivated by political, ideological, or social causes, often seeking to disrupt services, deface websites, or leak data to embarrass targets rather than secure a monetary payout.
Can personal devices be targeted by web criminals?
Yes. Personal devices are frequently targeted via phishing emails, malicious mobile applications, malvertising, and unsecured home Wi-Fi networks. Web criminals target individuals to steal banking credentials, deploy spyware, commit identity theft, or conscript home computers into botnets used for distributed denial-of-service (DDoS) attacks.
How can I verify if my credentials have been compromised?
You can monitor security breach notifications and check whether your email addresses or passwords have appeared in known data leaks by using reputable credential-monitoring services, such as Have I Been Pwned. If a leak is detected, you should immediately update your passwords and enable multi-factor authentication on all affected accounts.
Practical Next Actions
To safeguard your digital assets against modern web criminals, immediately audit your current security posture. Begin by ensuring that multi-factor authentication is active on all personal and professional accounts, verify that all operating systems and software applications are running the latest security patches, and establish secure, offline backups for critical data to protect against ransomware extortion.