SAP HANA database security encompasses the multi-layered methodologies, architectural controls, and administrative practices required to protect mission-critical in-memory data, system resources, and analytical workloads against unauthorized access, data breaches, and regulatory non-compliance as of 2026.
Introduction to SAP HANA Database Security
In modern enterprise architectures, the SAP HANA database serves as the high-performance analytical and transactional core for enterprise resource planning, supply chain management, and financial reporting. Because these systems centralize vast amounts of sensitive corporate data, intellectual property, and personally identifiable information, robust database security is paramount. Securing SAP HANA requires a comprehensive strategy that spans multiple layers: network perimeter defense, identity and access management, data encryption, auditing, and vulnerability management.
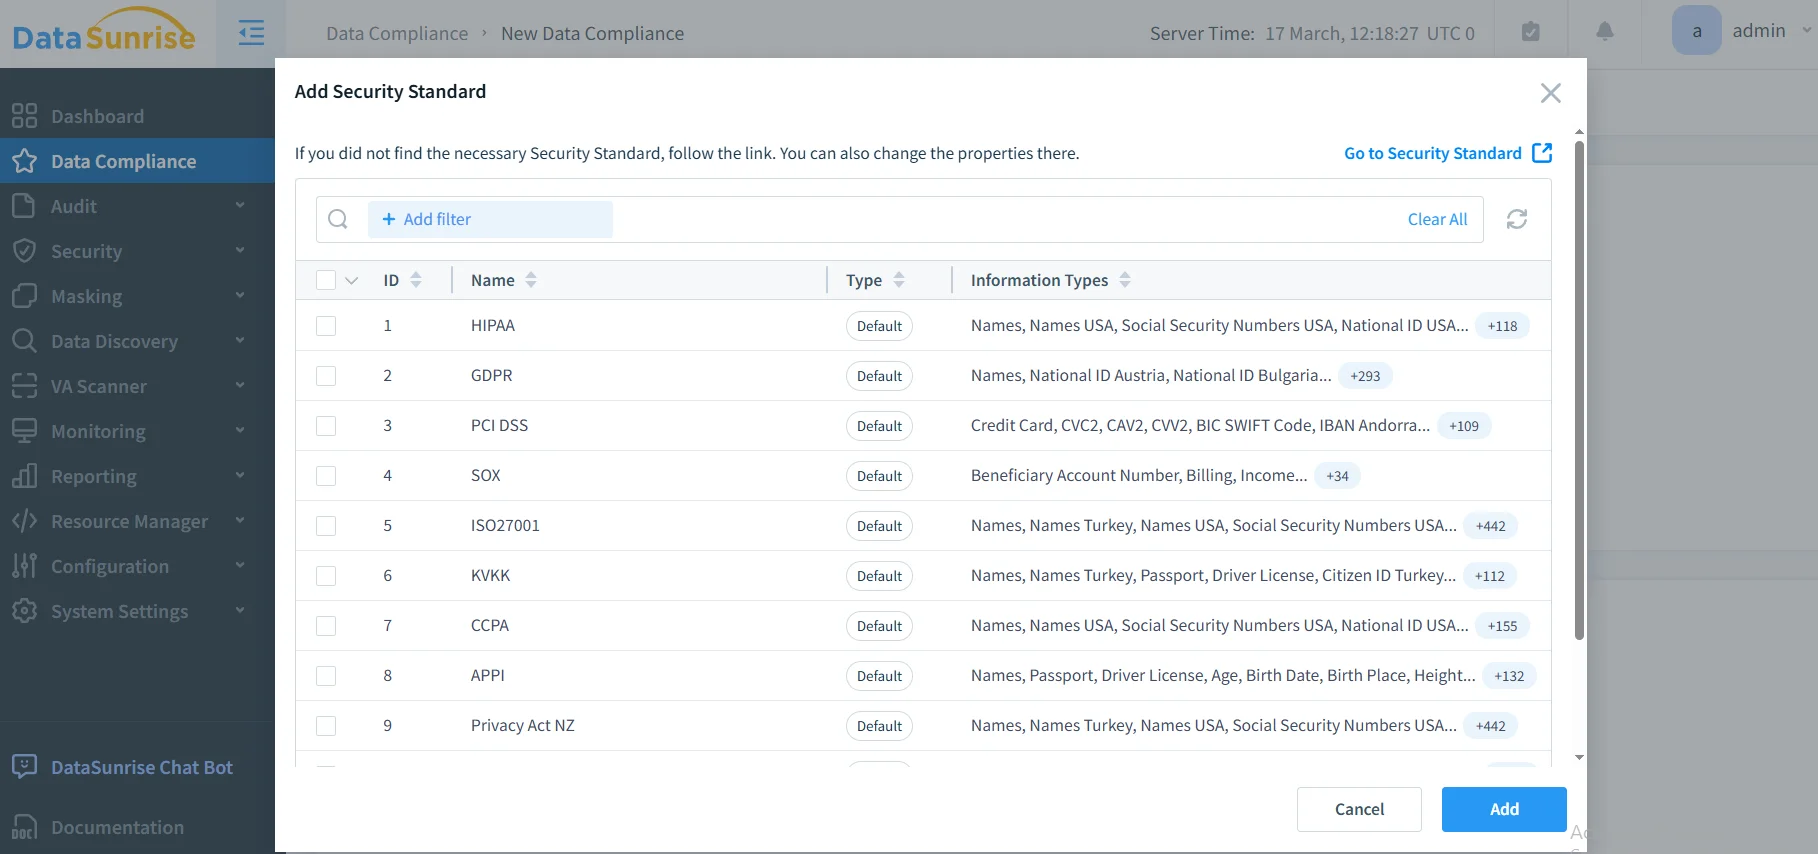
Unlike traditional disk-based relational database management systems, SAP HANA processes data primarily in-memory using columnar and row-based storage engines. This unique architecture introduces specific security considerations regarding memory management, multi-tenancy isolation, and high-speed data propagation. Administrators must implement granular security controls that align with corporate governance frameworks and industry compliance mandates, such as GDPR, HIPAA, and PCI-DSS, without degrading system performance or user productivity.
Core Architectural Layers of SAP HANA Security
The security architecture of SAP HANA is built upon a defense-in-depth model. This model ensures that if one layer of defense is compromised, subsequent layers remain active to prevent unauthorized data exposure or system manipulation.
Network and Transport Layer Security
Securing communication channels between clients, application servers, and the SAP HANA database is the first line of defense. SAP HANA supports Transport Layer Security (TLS) and Secure Sockets Layer (SSL) protocols to encrypt all data in transit across the network.
- Client-to-Database Communication: All traffic flowing between client applications (such as SAP NetWeaver, SAP S/4HANA, or custom JDBC/ODBC clients) and the SAP HANA database should be encrypted using TLS. This prevents eavesdropping, man-in-the-middle attacks, and session hijacking.
- Inter-Service and Distributed Communication: In scaled-out distributed landscapes or high-availability multi-node deployments, communication between different SAP HANA index servers, worker nodes, and name servers must also be encrypted using internal TLS certificates.
- Firewall and Port Hardening: Organizations must restrict network access to SAP HANA ports (typically starting from
30015for instance numbers, and39013for HTTP services) using enterprise firewalls, security groups, and virtual local area networks (VLANs). Only authorized application servers and administrative endpoints should be permitted to communicate directly with database ports.
Authentication Mechanisms
SAP HANA provides flexible authentication frameworks to verify the identity of database users and administrators before granting access to system resources.
- User Authentication Methods: Users can authenticate via standard database user credentials (username and password), Kerberos tickets, X.509 client certificates, Security Assertion Markup Language (SAML) assertions, or JSON Web Tokens (JWT).
- Password Policies: Administrators must enforce stringent password complexity rules, expiration intervals, and account lockout thresholds to mitigate brute-force and credential-stuffing attacks. SAP HANA allows the configuration of global password policies that dictate minimum length, character composition (uppercase, lowercase, numbers, special characters), and reuse restrictions.
- Single Sign-On (SSO): Implementing Kerberos or SAML-based SSO reduces password fatigue, minimizes administrative overhead, and integrates the database into the organization's broader enterprise identity management infrastructure.
Identity and Access Management (IAM)
Controlling what authenticated users can view and modify is governed by SAP HANA's robust authorization model. The platform relies on a combination of privileges and roles to enforce the principle of least privilege.
Privileges in SAP HANA
Privileges define the specific actions a user can perform on database objects or system-level configurations. SAP HANA categorizes privileges into several distinct types:
- System Privileges: Authorize users to perform administrative tasks across the entire database, such as creating users, managing backups, configuring parameters, and monitoring system performance (e.g.,
DATA ADMIN,USER ADMIN,BACKUP ADMIN). - Object Privileges: Grant rights to execute specific operations on tables, views, procedures, or schemas. These include
SELECT,INSERT,UPDATE,DELETE,EXECUTE, andALTER. - Analytic and Modeling Privileges: Essential for SAP HANA's advanced analytical workloads, these privileges control access to data filtered by specific dimension values within information views (Calculation Views). This enables complex row- and column-level security scenarios.
- Package Privileges: Control access to design-time repository objects stored in the SAP HANA repository, governing who can create, edit, or transport application content.
Roles and Role Management
Assigning privileges directly to individual user accounts is inefficient and prone to administrative errors. Instead, SAP HANA utilizes roles as containers for collections of privileges.
- Predefined Roles: SAP HANA delivers several restricted system roles out-of-the-box (such as
PUBLIC,MONITOR, andCATALOG READ). Administrators should avoid granting overly permissive predefined roles indiscriminately. - Custom Roles: Organizations should construct custom roles tailored to specific job functions (e.g.,
FIN_ANALYST,SALES_MANAGER). Users are then assigned to these roles, simplifying lifecycle management when job responsibilities change.
Authorization Comparison Matrix
| Privilege Type | Target Entity | Common Examples | Typical Assignment |
|---|---|---|---|
| System Privileges | Database instance / System | CREATE USER, BACKUP ADMIN, TRACE ADMIN |
Database Administrators (DBAs) |
| Object Privileges | Tables, Views, Procedures | SELECT, INSERT, EXECUTE |
Application owners and service accounts |
| Analytic Privileges | Calculation Views / Attributes | Row-level data filters based on region or department | Business end-users and analysts |
| Package Privileges | Repository development packages | REPO.READ, REPO.EDIT_CONTENT |
Developers and modelers |
Data Encryption at Rest
Protecting data while it resides on persistent storage media is critical for regulatory compliance and physical security mitigation. SAP HANA provides native data-at-rest encryption capabilities that secure data volumes, log volumes, and backup files.
Native Cryptographic Services
SAP HANA includes an integrated cryptographic library (SAP Cryptographic Library / CommonCryptoLib) that handles encryption operations without requiring external third-party tools.
- Data Volume Encryption: Encrypts entire data persistence volumes on disk. Individual database pages are encrypted in memory before being written to disk and decrypted upon being read back into memory.
- Log Volume Encryption: Secures transaction log volumes to ensure that uncommitted or committed transactional data cannot be read from raw storage disks if storage media is stolen or improperly decommissioned.
- Backup Encryption: Ensures that database backups stored on disk, tape, or cloud object storage are fully encrypted, protecting sensitive corporate archives against unauthorized extraction.
Encryption Key Management
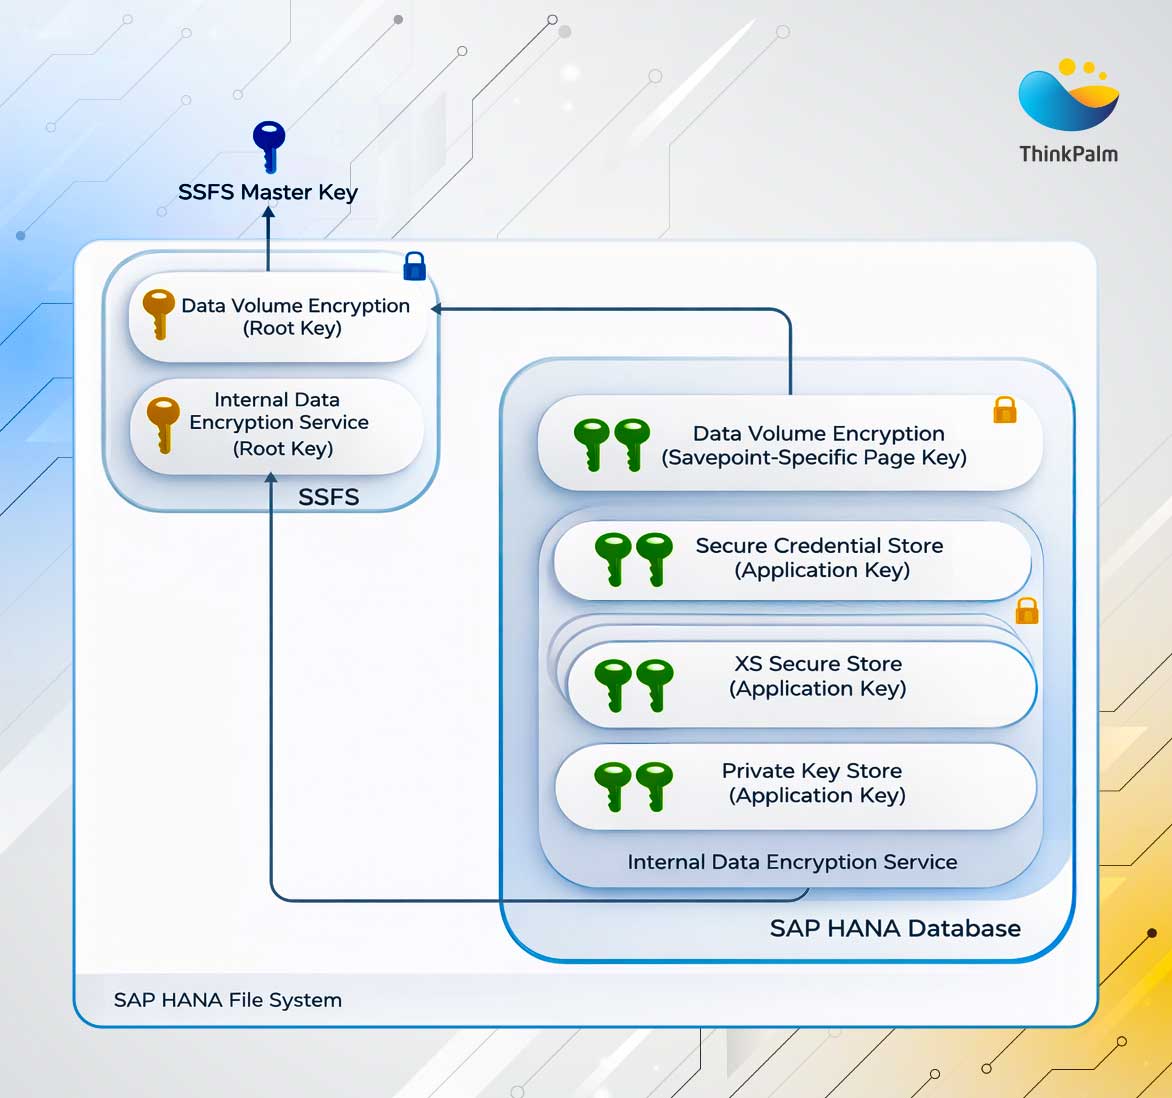
The security of encrypted data depends heavily on proper key lifecycle management. SAP HANA employs a hierarchical key management architecture:
- Root Keys: Securely stored in a dedicated secure store (SSFS - Secure Storage in File System) or external Key Management Interoperability Protocol (KMIP) compliant key management systems.
- Data Encryption Keys (DEKs): Used to encrypt actual data blocks and are themselves encrypted by the root keys.
- Key Rotation: Administrators must establish regular schedules for rotating root keys to comply with security best practices and internal policies.
Auditing and Compliance Monitoring
Continuous monitoring and forensic logging are essential components of a mature security posture. SAP HANA features an advanced auditing engine that tracks critical security-relevant events across the database instance.
Configuring Audit Policies
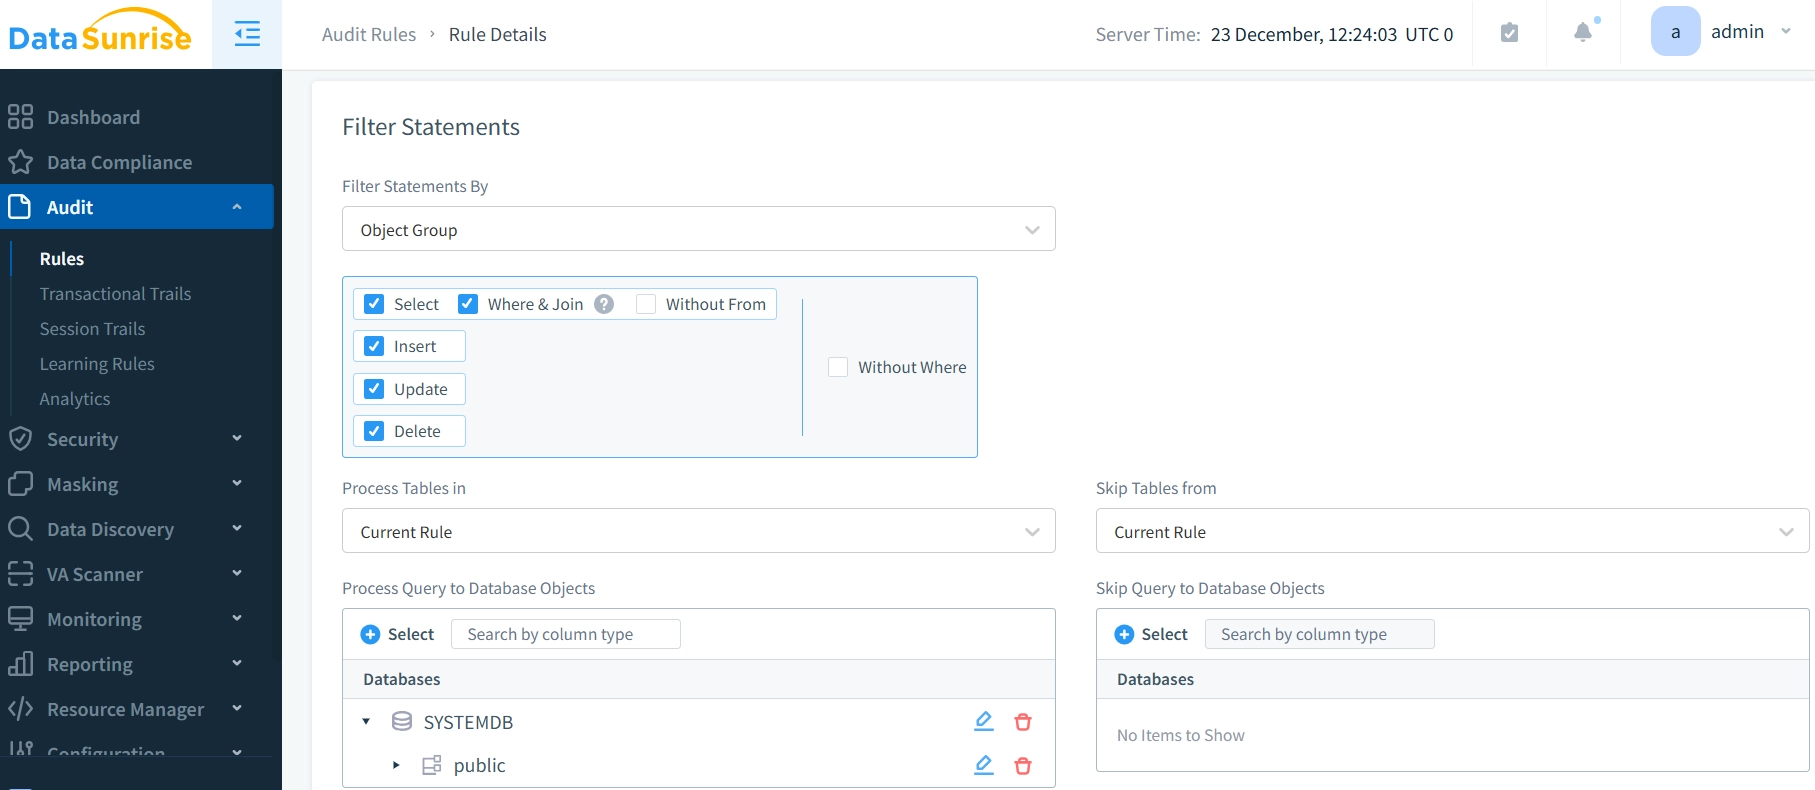
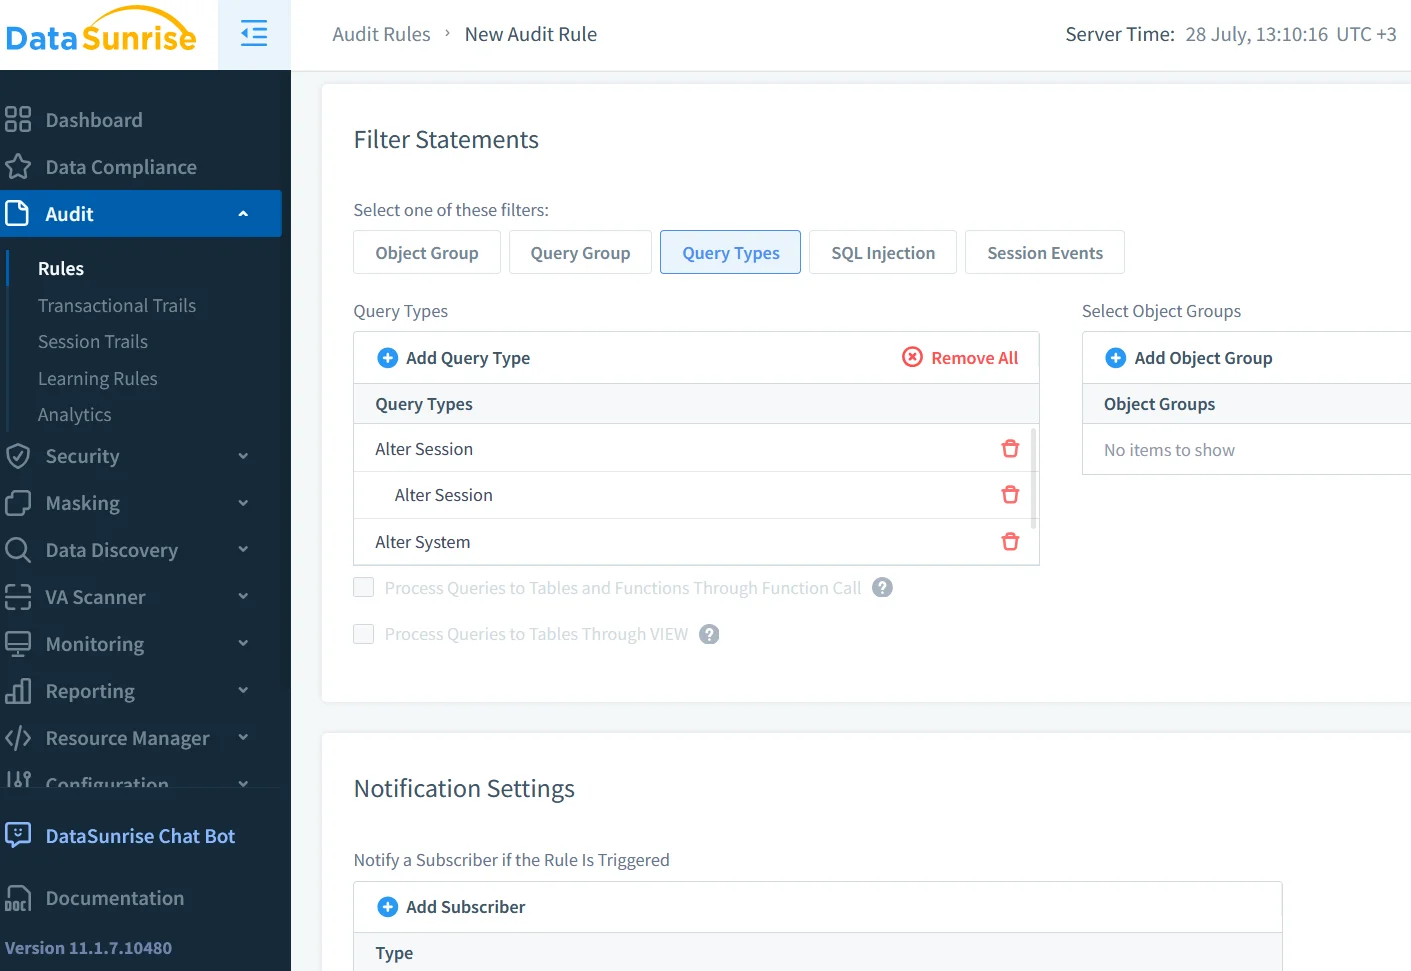
Administrators can create, alter, and drop audit policies using SQL commands or the SAP HANA cockpit. An audit policy specifies:
- Events to Monitor: Actions such as failed logon attempts, unauthorized access to sensitive tables, alterations to user privileges, or execution of administrative commands.
- Audit Level: Severity levels (e.g., Low, Medium, High) assigned to captured events.
- Auditing Targets: Destination repositories where audit logs are stored, including database audit tables (
AUDIT_LOG), syslog facilities, or specialized monitoring tools.
Reviewing and Securing Audit Trails
Audit logs themselves represent a high-value target for malicious actors attempting to cover their tracks. Consequently, audit tables must be protected with strict object privileges, ensuring that standard database users and even application owners cannot modify or delete audit records. Compliance officers and security information and event management (SIEM) systems should regularly ingest SAP HANA audit logs for anomaly detection and forensic analysis.
Multi-Tenancy and Database Isolation
Modern SAP HANA deployments frequently utilize Multi-Tenant Database Containers (MDC), allowing a single SAP HANA system to host multiple isolated tenant databases. Ensuring secure multi-tenancy is vital to prevent cross-tenant data leakage.
- System Database vs. Tenant Database: The system database is responsible for overall landscape management, database creation, and tenant monitoring, whereas tenant databases hold customer-specific application data. Administrative separation must be maintained strictly; system database administrators should not automatically have unrestricted read access to tenant database application data.
- Isolated Network and Resource Pools: Administrators can configure resource limits (CPU, memory) and network isolation rules per tenant to mitigate denial-of-service risks and ensure strict tenant boundaries.
Common Security Misconfigurations and Troubleshooting
Even with advanced tooling, improper configuration can leave SAP HANA databases vulnerable. Addressing common pitfalls is essential for maintaining an impenetrable posture.
Frequent Security Pitfalls
- Default Credentials: Failing to change initial passwords for default system accounts (such as
SYSTEM,HXSAWEB, or internal technical users) immediately after installation. - Over-Privileged Service Accounts: Assigning broad
SYS_REPOorADMINprivileges to routine application connection profiles. - Unencrypted Client Connections: Allowing unencrypted SQL or ODBC connections to traverse corporate networks without mandatory TLS enforcement.
- Neglected Patch Management: Delaying the application of SAP Security Notes and Support Package Stacks (SPS), leaving known vulnerabilities exposed.
Troubleshooting Security and Access Issues
When users report access denials or connection failures, administrators should follow a structured troubleshooting methodology:
- Check Trace Files: Inspect the
indexserverandnameservertrace files within the SAP HANA cockpit or file system to identify authorization errors (e.g.,insufficient privilegemessages). - Verify Effective Privileges: Use system views such as
EFFECTIVE_PRIVILEGESorGRANTED_PRIVILEGESto determine precisely why a user is blocked from accessing a specific object or view. - Validate Certificate Chains: For TLS/SSL connectivity issues, verify that client trust stores correctly contain the root and intermediate certificates of the SAP HANA server.
Frequently Asked Questions
What is the primary difference between system privileges and object privileges in SAP HANA?
System privileges grant administrative capabilities across the entire database instance, such as user creation, system configuration, and backup execution. Object privileges control granular access rights—such as SELECT, INSERT, or UPDATE—on specific database objects like tables, views, or schemas.
How does SAP HANA protect data at rest?
SAP HANA provides native data-at-rest encryption utilizing the SAP Cryptographic Library. It encrypts data volumes, log volumes, and database backups using a hierarchical key management structure, ensuring that unauthorized parties cannot read raw storage media or stolen backup files.
Can SAP HANA integrate with enterprise single sign-on (SSO) systems?
Yes, SAP HANA supports multiple external authentication providers, including Kerberos, SAML 2.0, and JSON Web Tokens (JWT), enabling seamless integration with enterprise identity providers and Active Directory infrastructures for Single Sign-On.
What is the purpose of analytic privileges in SAP HANA?
Analytic privileges enforce row- and column-level data security within SAP HANA information views (Calculation Views). They ensure that users only see data rows that match specific authorization criteria defined by organizational rules, such as regional or departmental boundaries.
How often should SAP HANA encryption root keys be rotated?
While the exact frequency depends on organizational risk appetite and regulatory frameworks, security best practices and compliance standards generally recommend rotating root encryption keys at least annually, or immediately following any suspected security incident or administrative staff turnover.
Conclusion and Next Actions
Securing an SAP HANA database requires a continuous, disciplined approach encompassing network hardening, robust identity management, encryption, and diligent auditing. Organizations must move beyond default configurations and establish formal governance policies that reflect the critical nature of in-memory data assets. As a practical next action, database administrators and security officers should conduct an immediate security baseline audit using the SAP HANA Security Checklist and SAP Security Notes to identify and remediate active vulnerabilities.