An iOS deeplink is a specialized URL scheme or universal link designed to direct users from an external source—such as a mobile browser, email, or social media platform—directly to specific content or functionality inside an installed or uninstalled iOS application.
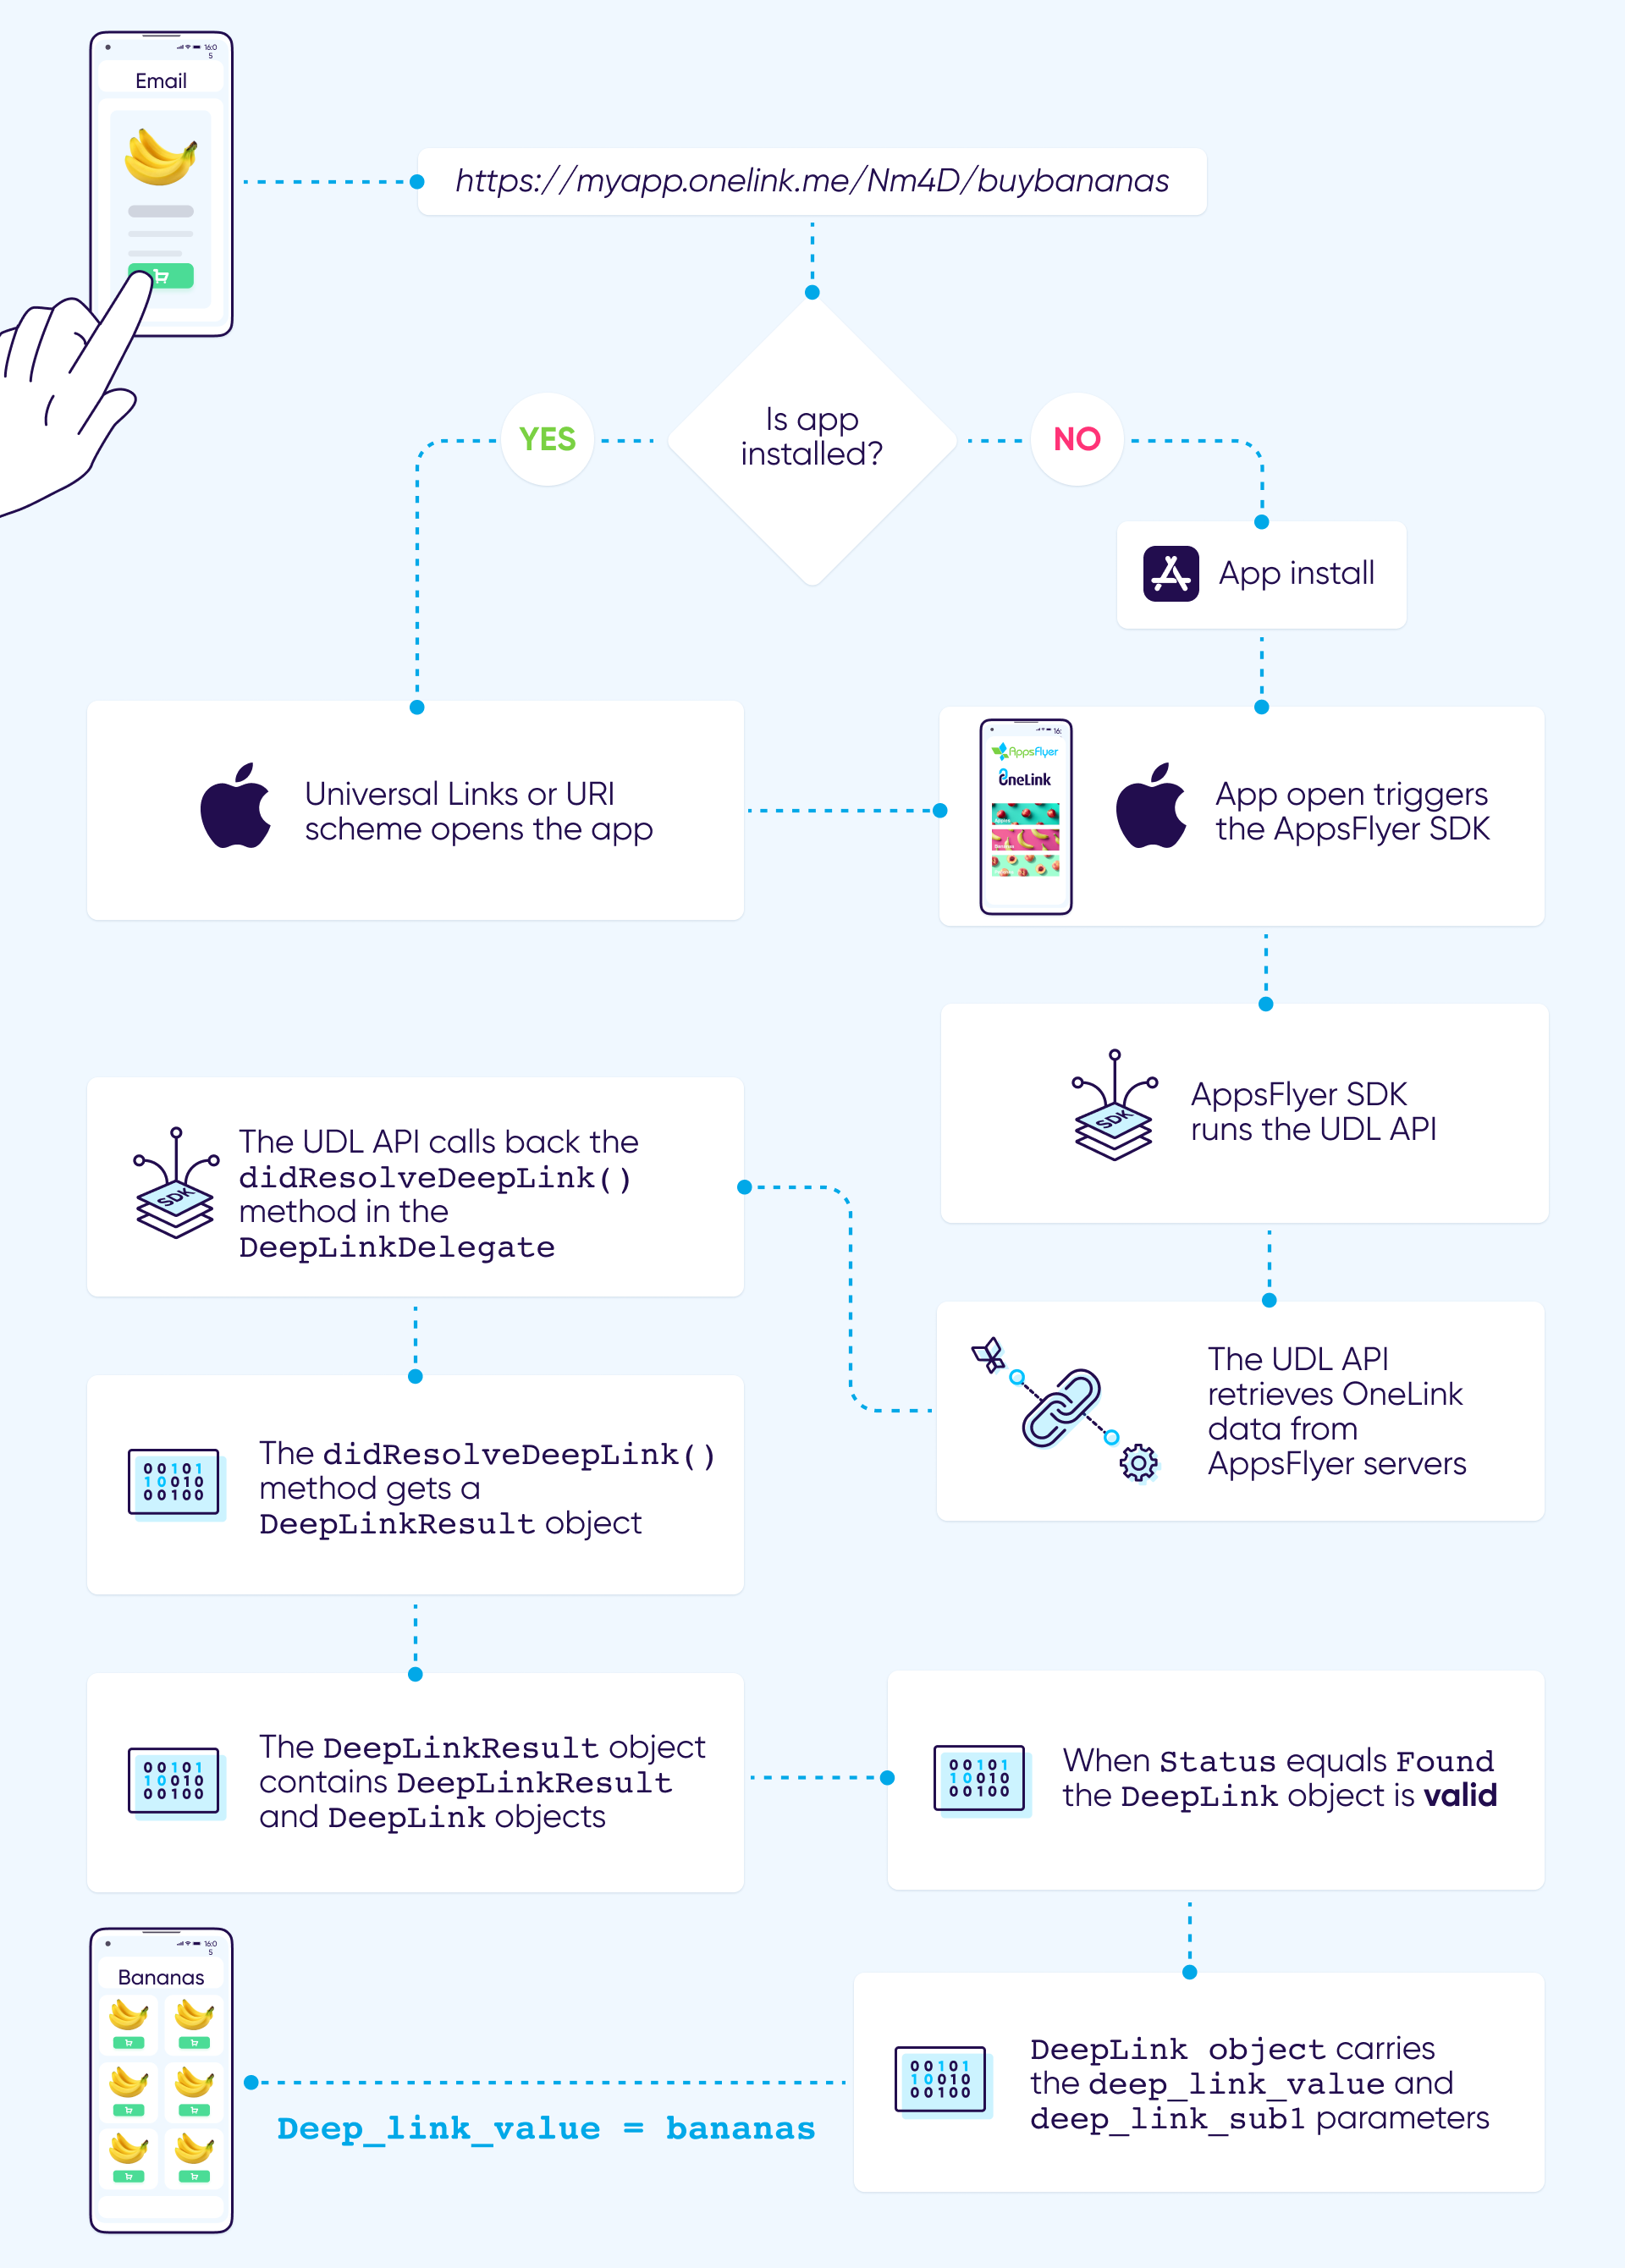
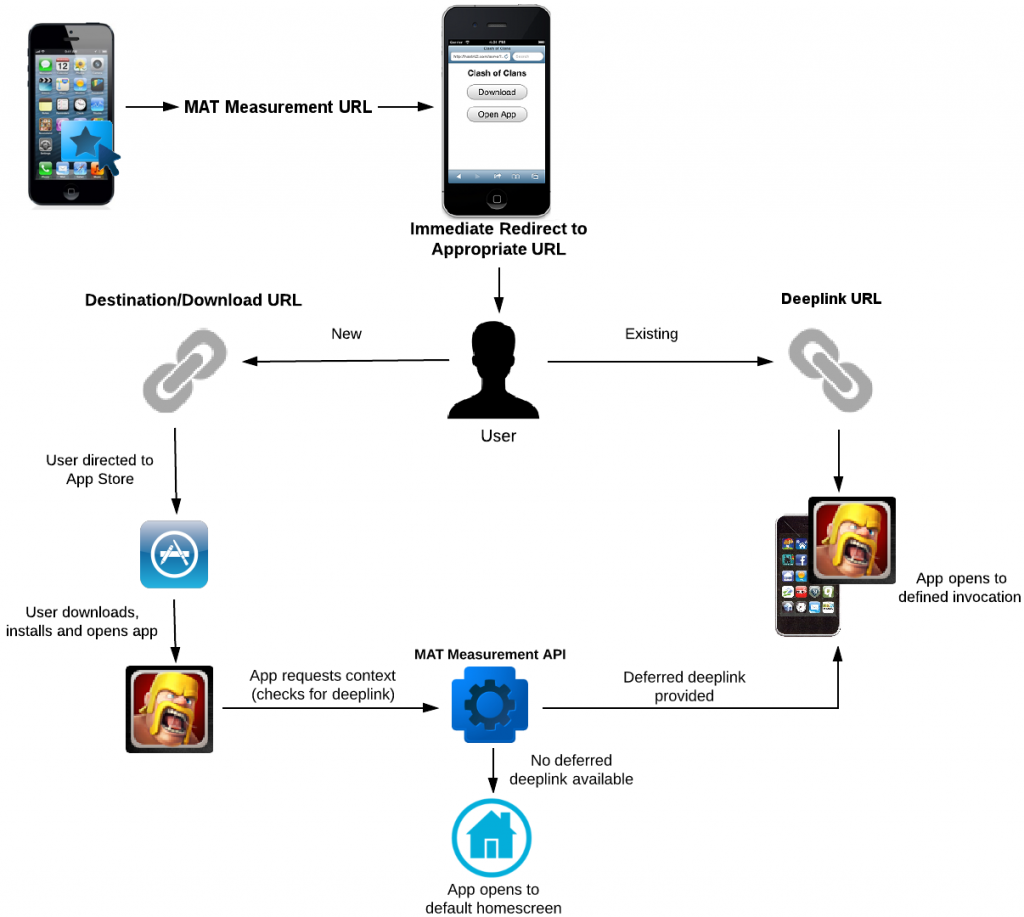
Implementing deep links correctly on Apple's mobile operating system requires navigating a nuanced ecosystem of traditional custom URL schemes and modern Universal Links. Unlike standard web navigation, mobile deep linking requires bridging the gap between the web browser and the native app container. When a user taps a properly configured link on an iPhone or iPad, the iOS operating system evaluates whether the target application is installed. If the app is present, the system launches it and passes the URL payload to the application delegate for handling. If the application is not installed, the link typically falls back to a designated web URL or redirects the user to the App Store.
Mastering this technology is essential for mobile developers, product managers, and digital marketers seeking to reduce friction in user acquisition, streamline onboarding flows, and create cohesive cross-platform experiences. This guide examines the technical foundations, configuration steps, comparative frameworks, and troubleshooting methodologies necessary to deploy robust deeplink architecture in iOS applications.
Foundations of iOS Deep Linking
To implement deep linking effectively, developers must understand the underlying mechanics that govern how iOS handles incoming Uniform Resource Identifiers (URIs). The iOS ecosystem utilizes two primary mechanisms for deep linking: Custom URL Schemes and Universal Links. Each approach relies on distinct architectural patterns, security models, and operating system behaviors.
Custom URL Schemes
Custom URL schemes represent the traditional method for deep linking on iOS devices. A custom scheme uses a unique application-specific identifier prefix followed by a custom path (for example, myapp://product/12345). To configure a custom URL scheme, developers register the scheme in the application's Info.plist file under the CFBundleURLTypes key.
When an application registers a custom scheme, it claims ownership of that string across the entire device. However, this model introduces a significant security vulnerability known as scheme hijacking. Because iOS does not verify ownership of custom URL schemes, if two different apps register the exact same scheme (e.g., myapp://), iOS behavior is non-deterministic, potentially allowing a malicious application to intercept sensitive data payloads intended for another app. Furthermore, checking whether an application is installed via canOpenURL: requires explicit declaration in the Info.plist under LSApplicationQueriesSchemes, a requirement enforced by Apple's privacy guidelines to limit app enumeration.
Universal Links
Introduced by Apple in iOS 9, Universal Links provide a secure, HTTP-based standard for linking directly to content inside an app while offering a seamless fallback to Safari if the app is not installed. Universal Links utilize standard https:// URLs, establishing a cryptographic association between a website domain and a mobile application.
The core advantage of Universal Links lies in their security and user experience. Because they rely on standard web URLs, they function gracefully on the web when no app is present. When the app is installed, iOS verifies the domain ownership by querying an Apple-hosted content delivery network (CDN) that checks an apple-app-site-association (AASA) JSON file hosted on the developer's web server. This verification prevents other applications from intercepting links intended for a specific brand or service.
Technical Architecture and Prerequisites
Implementing Universal Links requires coordination between the iOS application target and the hosting web server. Neglecting either component will result in link resolution failure, causing iOS to default to opening the link in Safari instead of the native application.
Server-Side Configuration: The AASA File
The foundation of Universal Link security is the apple-app-site-association file. This file must be served from the root directory of your domain (or a well-known directory: https://yourdomain.com/.well-known/apple-app-site-association).
The server must serve the AASA file with the application/json content type over a valid TLS/HTTPS connection. The file contains a JSON structure detailing which app IDs are authorized to handle specific URL paths for that domain:
{ "applinks": { "apps": [], "details": [ { "appID": "TEAMID.com.example.myapp", "paths": ["/catalog/*", "/item/*", "!/catalog/exclude/*"] } ] } }
In this structure, TEAMID corresponds to your 10-character Apple Developer Team ID, and com.example.myapp represents your app's bundle identifier. The paths array dictates which routes trigger the native application. Prefixer rules apply: using * matches wildcard paths, while prepending an exclamation point (!) explicitly excludes specific paths from being handled as universal links.
Client-Side Configuration: Entitlements and Capabilities
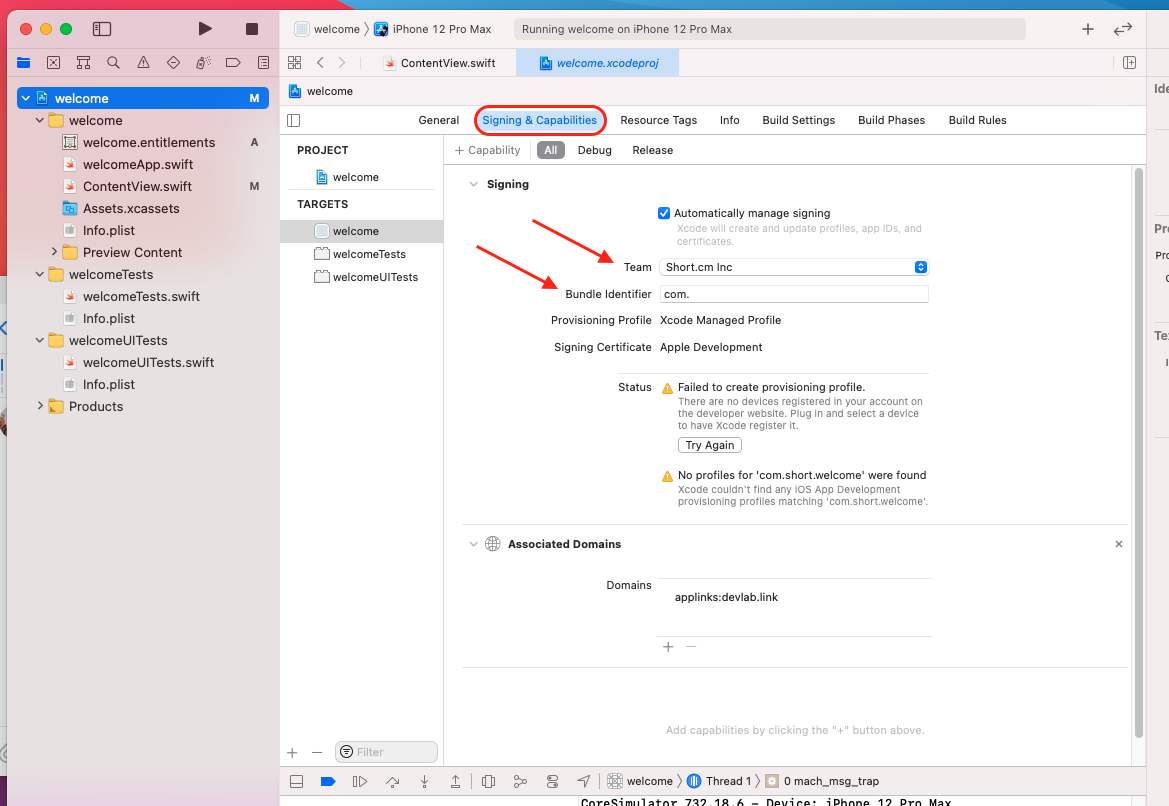
Once the server hosts the AASA file, the iOS application must be configured with the Associated Domains entitlement. This step informs the operating system which domains to query during app installation.
- Navigate to your Apple Developer account and ensure the Associated Domains capability is enabled for your App ID.
- In Xcode, select your project target, navigate to the Signing & Capabilities tab, and click + Capability to add Associated Domains.
- Under the Associated Domains section, add your domain using the required prefix:
applinks:yourdomain.com. You can specify multiple domains if your infrastructure spans several properties.
Handling Incoming Links in Code
When a Universal Link successfully launches or wakes up your iOS application, the operating system delivers the URL via the UIScene lifecycle or the legacy UIApplicationDelegate methods. Modern iOS applications utilizing SwiftUI or programmatic UIKit lifecycle methods implement these handlers in the app delegate or scene delegate.
// Swift implementation for handling incoming Universal Links in UIApplicationDelegate func application(_ application: UIApplication, continue userActivity: NSUserActivity, restorationHandler: @escaping ([UIUserActivityRestoring]?) -> Void) -> Bool { // Verify that the activity type is browsing web if userActivity.activityType == NSUserActivityTypeBrowsingWeb, let incomingURL = userActivity.webpageURL { // Parse the URL and route to the appropriate view controller or state AppRouter.shared.handle(url: incomingURL) return true } return false }
For applications utilizing the modern UIWindowScene lifecycle introduced in iOS 13, link handling is managed inside the scene delegate when the scene connects or receives user activities:
func scene(_ scene: WillConnectToSessionOptions, openURLContexts URLContexts: Set) { guard let urlContext = URLContexts.first else { return } let incomingURL = urlContext.url AppRouter.shared.handle(url: incomingURL) }
Comparative Analysis: Deep Linking Approaches
Choosing the correct linking strategy depends on your application's security requirements, target audience, and maintenance capabilities. The following comparison highlights the operational differences between Custom URL Schemes and Universal Links.
| Feature / Attribute | Custom URL Schemes | Universal Links | Deferred Deep Linking |
|---|---|---|---|
| Protocol | Custom string (myapp://) |
Standard HTTPS (https://) |
HTTPS with attribution backend |
| Security | Low (Vulnerable to scheme hijacking) | High (Cryptographically verified via AASA) | High (Relies on server-side attribution) |
| App Not Installed Fallback | Fails or throws system error | Seamlessly opens web browser (Safari) | Redirects to App Store, preserves context post-install |
| Ownership Verification | None | Required via Apple-App-Site-Association file | Verified via SDK fingerprinting or clipboard |
| Setup Complexity | Minimal (Info.plist configuration) |
Moderate (Requires server-side file and Xcode entitlement) | High (Requires third-party SDK or custom backend) |
Deferred Deep Linking Mechanics
A common marketing and product requirement is deferred deep linking. Standard deep links fail when a user does not have the app installed because the routing context is lost during the App Store download and installation process. A deferred deep link solves this problem by capturing the user's intent, routing them through the App Store, and delivering the original content payload upon the application's first launch after installation.
Because iOS sandbox security prevents direct communication between Safari and a newly installed application regarding pre-installation web traffic, developers typically implement deferred deep linking using one of two primary methodologies:
- Probabilistic Matching (Fingerprinting): When a user clicks a link, the tracking server records metadata about the incoming request, including IP address, device model, operating system version, and screen resolution. When the user installs the app and opens it for the first time, the app's initialization SDK sends a similar fingerprint to the server. If the signatures match within a short temporal window, the server associates the install with the click and returns the deep link payload.
- Deterministic Matching (Pasteboard or SKAdNetwork): Historically, some implementations utilized the iOS pasteboard to copy deep link data on the web and read it inside the app. However, Apple has progressively restricted pasteboard access with prominent system banners notifying users when an app reads clipboard contents. Modern attribution often leverages Apple's privacy-preserving frameworks like SKAdNetwork for installation validation, combined with first-party server redirects.
Verification, Testing, and Diagnostics
Verifying that an iOS deeplink functions correctly requires testing across multiple entry points, including mobile Safari, third-party messaging apps, and direct terminal commands.
Testing via Simulator and Terminal
Developers can test URL schemes and Universal Links directly from the macOS Terminal using the xcrun simctl utility while running an iOS Simulator:
xcrun simctl openurl booted "https://yourdomain.com/catalog/item/12345"
To test custom URL schemes:
xcrun simctl openurl booted "myapp://catalog/item/12345"
Verifying the AASA File
Apple maintains a validation tool to check whether your domain correctly serves the AASA file and whether iOS can parse it. You can inspect your domain's configuration using Apple's CDN validator endpoint or by executing a curl request to verify headers:
curl -I https://yourdomain.com/.well-known/apple-app-site-association
Ensure the server returns Content-Type: application/json and a 200 OK status code. Any redirects or authentication challenges on the AASA endpoint will cause iOS to fail validation.
Common Pitfalls and Troubleshooting
Even with correct configuration, engineers frequently encounter edge cases that break deep link functionality. Understanding these failure modes saves significant debugging time.
- AASA Caching Issues: Apple caches AASA files aggressively when an app is installed from the App Store or TestFlight. If you update your AASA file on the server, existing installations may not reflect the changes immediately. Deleting and reinstalling the app forces iOS to re-fetch the AASA file from the server.
- Wildcard Path Misconfigurations: Overly broad path definitions in the AASA file (such as
/*) can cause unintended routing loops where standard web traffic is forcibly intercepted by the app, preventing users from accessing regular web pages. - Universal Link Triggering from Safari: Universal Links do not trigger when a user types the URL directly into the Safari address bar and presses enter, nor do they trigger when a user taps a link on the exact same domain the link originates from (same-origin policy). To test Universal Links reliably in Safari, paste the link into Notes or Messages, or tap a link on an external website.
- App Transport Security (ATS) Violations: Ensure that any API endpoints contacted during the deep link resolution flow comply with Apple's ATS requirements, utilizing TLS 1.2 or higher with secure cipher suites.
Frequently Asked Questions
What is the difference between a custom URL scheme and a Universal Link?
A custom URL scheme uses a proprietary prefix (e.g., myapp://) and suffers from security vulnerabilities because any app can register the same scheme. Universal Links use standard HTTPS URLs (e.g., https://example.com/path), offering cryptographic verification via an AASA file and a seamless fallback to the mobile web if the app is not installed.
Why is my Universal Link opening in Safari instead of my iOS app?
This typically occurs because the AASA file is missing, incorrectly formatted, served with the wrong content type, or hosted without valid HTTPS. Additionally, if you are testing by typing the URL directly into the Safari address bar, iOS intentionally bypasses Universal Link triggering. Test by tapping the link from an external source like Apple Notes or Messages.
How do I handle deep links when the app is not installed?
To handle uninstalled states, developers use deferred deep linking. This technique captures user intent via web-based attribution (using probabilistic fingerprinting or server-side session matching), directs the user to the App Store, and delivers the deep link payload to the app upon its first launch.
Can I test Universal Links on the iOS Simulator?
Yes, Universal Links can be tested on the iOS Simulator. However, because simulator network behavior and caching can occasionally diverge from physical hardware, final verification should always be performed on a physical iOS device connected to Xcode.
How do I update my AASA file without forcing users to update their app?
iOS periodically checks for updates to the AASA files associated with installed apps. However, because Apple's CDN caches these files, updates may take time to propagate. For immediate testing during development, deleting and reinstalling the app forces iOS to download the freshest AASA file from your domain.
Conclusion
Implementing robust iOS deeplink architecture requires careful attention to server infrastructure, cryptographic verification, entitlements configuration, and client-side routing logic. By transitioning legacy custom URL schemes to modern Universal Links and establishing reliable fallback mechanisms for uninstalled states, engineering teams can deliver secure, frictionless navigation between the web and native mobile environments. Regular testing via simulator utilities and rigorous AASA validation ensure that your deep linking implementation remains resilient across future iOS updates.