A Mobile Device Management (MDM) solution is a centralized software platform that allows IT and security administrators to provision, secure, monitor, and manage corporate-owned and employee-owned endpoints across an organization from a single console.
Modern enterprise architecture relies heavily on distributed endpoints, spanning corporate offices, remote home workspaces, and mobile environments. As the perimeter of the corporate network dissolves, organizations must maintain absolute visibility and control over every smartphone, tablet, laptop, and specialized device accessing sensitive company data. A robust MDM solution serves as the foundational cornerstone for modern endpoint management, bridging the gap between user productivity and rigorous cybersecurity compliance. This guide explores the architecture, core capabilities, implementation lifecycles, and evaluation criteria necessary for deploying an effective device management strategy.
Understanding MDM Architecture and Core Concepts
At its foundational level, a Mobile Device Management solution operates on a client-server architecture. The server component, typically hosted in the cloud by the vendor or on-premises within a secure corporate data center, acts as the command center. The client component consists of an agent application or deeply integrated native operating system hooks running on the target endpoint—whether that device is running iOS, Android, macOS, Windows, or ChromeOS.
Communication between the MDM server and the managed endpoints occurs via secure, encrypted protocols, leveraging native APIs built directly into modern operating systems. For example, Apple devices rely on the Apple Push Notification service (APNs) to maintain a persistent connection channel, allowing the management server to issue commands instantly. Similarly, Android Enterprise utilizes Google Play services to provision and govern devices securely without requiring manual user intervention during setup.
Administrators interact with this architecture through an administrative console, a web-based dashboard where policies are defined, applications are packaged, and security compliance reports are generated. When an administrator updates a security compliance rule—such as enforcing a mandatory passcode change or blocking access to compromised devices—the MDM server transmits this policy update over-the-air (OTA) to the target endpoint, which immediately enforces the directive.
Key Capabilities and Technical Features of Modern MDM Platforms
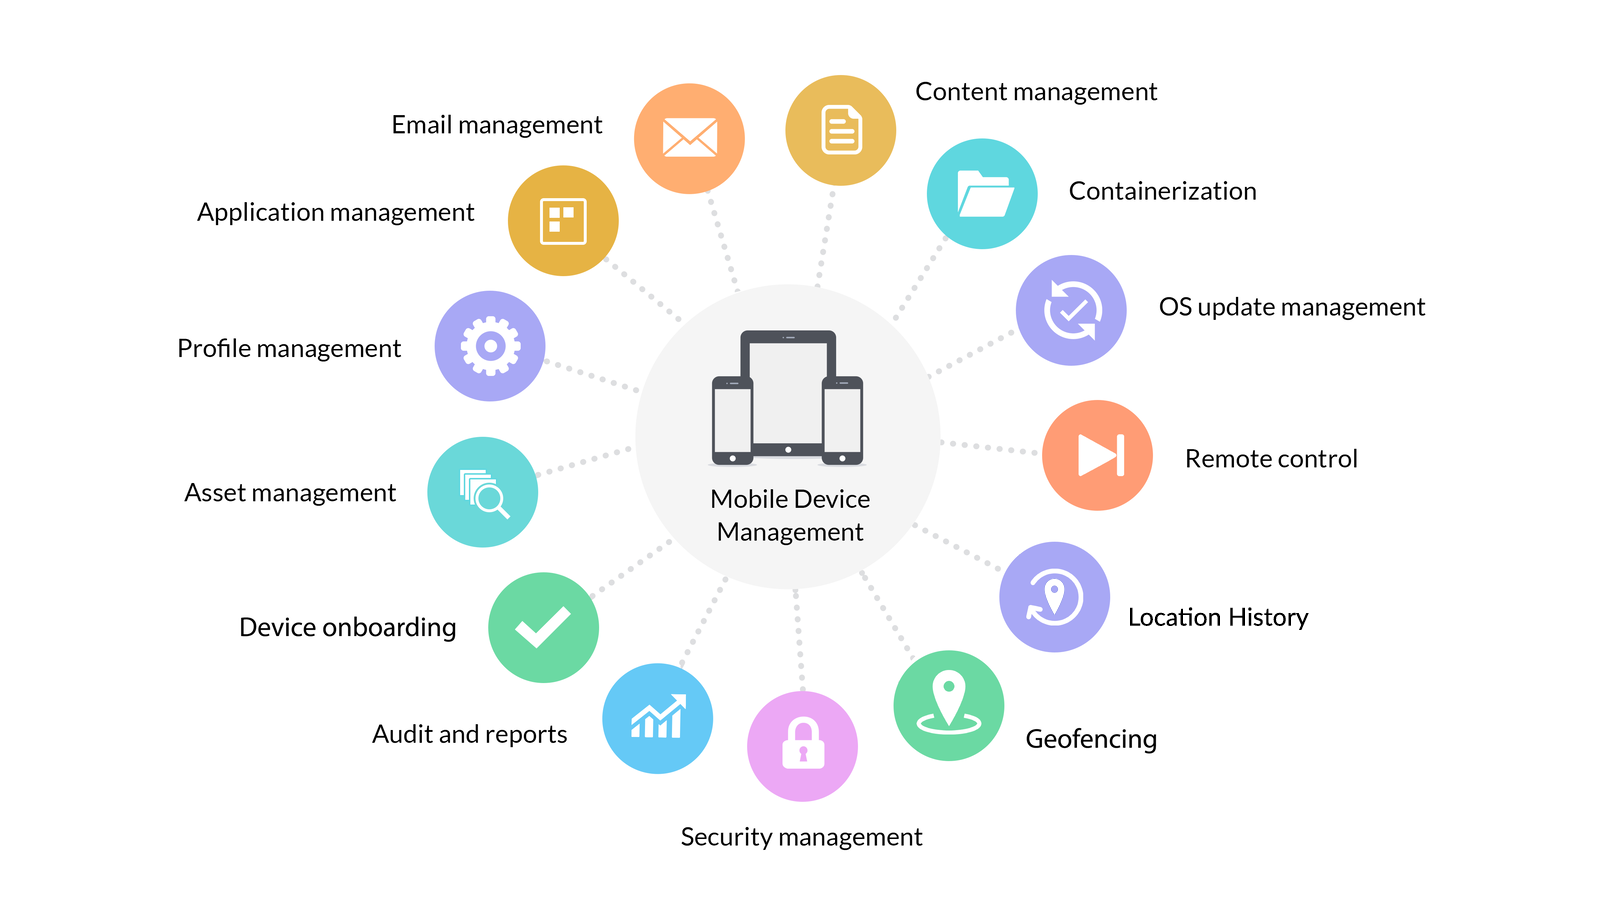
Enterprise-grade MDM solutions have evolved far beyond simple remote locking and wiping. Today, they encompass a comprehensive suite of features designed to manage the entire lifecycle of an endpoint, from initial unboxing to final retirement.
Over-the-Air Enrollment and Provisioning
Manual configuration of corporate devices is inefficient and prone to human error. Modern MDM solutions integrate directly with device manufacturer deployment programs—such as Apple Business Manager, Android Enterprise, and Windows Autopilot—to facilitate zero-touch enrollment. When a user turns on a brand-new device for the first time, the device automatically recognizes its corporate affiliation, contacts the MDM server, downloads the required security profiles, and configures corporate email and Wi-Fi networks without requiring IT personnel to touch the physical hardware.
Configuration and Policy Management
Administrators utilize policy profiles to enforce organizational security standards uniformly across diverse device fleets. These policies dictate operational parameters such as:
- Enforcing complex alphanumeric passcodes and automatic screen timeout durations.
- Disabling specific hardware components, such as built-in cameras, Bluetooth adapters, or removable storage media, in high-security environments.
- Configuring secure Wi-Fi, VPN, and cellular access points automatically to ensure encrypted transit of corporate data.
- Restricting software installations and blocking unauthorized operating system downgrades.
Application Management and Distribution
Managing software distribution across distributed endpoints requires robust application lifecycle management capabilities. An MDM platform acts as an enterprise app store, allowing IT teams to push internal line-of-business (LOB) applications, public store apps, and web apps directly to targeted user groups. Administrators can silently install apps, update them automatically without user intervention, and push configuration parameters directly to the application layer. Furthermore, administrators can revoke application access instantly if a device falls out of compliance or an employee departs the organization.
Remote Troubleshooting and Diagnostics
When end-users experience technical difficulties, resolving the issue quickly minimizes productivity loss. MDM solutions offer remote support tools that allow IT administrators to view device screens, pull detailed diagnostic logs, push network configuration fixes, and restart services without requiring physical access to the endpoint.
Security, Compliance, and Data Protection
Information security represents the primary catalyst for enterprise MDM adoption. As data breaches become increasingly sophisticated, securing endpoints at the operating system and application layers is mandatory for regulatory compliance under frameworks such as GDPR, HIPAA, and PCI-DSS.
Containerization and Data Separation
In environments where employees use personal devices for work—commonly known as Bring Your Own Device (BYOD)—maintaining user privacy while protecting corporate assets is critical. MDM solutions address this challenge through containerization. By creating an encrypted partition or work profile on the device, the MDM isolates corporate emails, documents, and applications from personal photos, messages, and apps. Corporate data cannot be copied and pasted into personal applications, shared via personal cloud storage, or accessed by unauthorized third-party apps.
Remote Lock and Wipe Capabilities
If a device is lost, stolen, or compromised, administrators can execute remote commands to secure the hardware instantly. A remote lock prevents unauthorized individuals from accessing the device interface. If the device cannot be recovered, an enterprise wipe removes all corporate data, application caches, and configuration profiles while leaving personal data untouched on BYOD devices, or executes a complete factory reset on corporate-owned assets.
Compliance Monitoring and Conditional Access
Security is not a static state; it requires continuous verification. MDM platforms constantly monitor device health, checking for indicators of compromise such as jailbreaking (iOS) or rooting (Android), outdated operating system patches, or disabled security features. Through integrations with Identity and Access Management (IAM) systems and Conditional Access policies, an MDM can automatically revoke a device's access to corporate resources if it detects a security violation, preventing lateral movement by malicious actors.
| Management Mode | Primary Use Case | Data Privacy Level | Control Over Hardware |
|---|---|---|---|
| Corporate-Owned (COBO) | Dedicated enterprise hardware; highly regulated industries. | Complete organizational ownership; no personal data allowed. | Maximum control over settings, apps, and hardware features. |
| Bring Your Own Device (BYOD) | Employee-owned smartphones and tablets used for work. | High privacy for the user; corporate visibility restricted to work container. | Moderate control restricted to the enterprise container and policies. |
| COPE (Corporate-Owned, Personally Enabled) | Company-issued devices permitted for limited personal use. | Balanced; personal data is protected, but corporate policy governs baseline security. | High control with structured partitions for personal apps and media. |
Evaluating and Selecting the Right MDM Solution
Choosing an MDM platform requires a thorough assessment of an organization's technical environment, security posture, budget, and staffing resources. Because the market features numerous vendors ranging from traditional endpoint management giants to cloud-native unified endpoint management (UEM) providers, organizations must evaluate prospective solutions against specific criteria.
Operating System Compatibility and Ecosystem Support
An organization utilizing a heterogeneous device fleet—running a mix of macOS laptops, Windows workstations, iOS executive iPhones, and Android ruggedized field devices—requires an MDM solution capable of managing all platforms natively from a single pane of glass. Verify that the vendor maintains rapid update cycles to support new operating system releases on day one, preventing security gaps when users upgrade their software.
Scalability and Deployment Models
Organizations must decide between cloud-hosted (SaaS) and on-premises deployment models. Cloud-hosted MDM solutions reduce infrastructure overhead, scale seamlessly as the enterprise grows, and ensure automatic updates without administrative intervention. Conversely, highly regulated sectors or organizations with strict data residency mandates may require on-premises deployment to maintain absolute control over management databases.
Integration with Existing Enterprise Infrastructure
An effective MDM solution does not operate in a vacuum. It must integrate smoothly with existing enterprise tools, including:
- Identity Providers (IdPs) like Microsoft Entra ID, Okta, or Ping Identity for single sign-on (SSO) and automated user provisioning.
- Security Information and Event Management (SIEM) systems to forward audit logs and compliance alerts.
- Helpdesk and IT Service Management (ITSM) platforms to streamline ticket creation and device assignment.
Total Cost of Ownership (TCO)
Beyond the initial per-device license fee, organizations must calculate the total cost of ownership, which includes administrative training, implementation services, ongoing maintenance, and potential third-party integration costs. Choosing a platform that simplifies daily operations through automation can significantly reduce the internal labor costs associated with endpoint management.
Step-by-Step Implementation Lifecycle
Deploying an MDM solution successfully demands a structured, phased approach to minimize disruption to business operations and end-user productivity.
- Discovery and Requirements Gathering: Catalog all existing endpoints, identify operating system distributions, map security and compliance requirements, and define administrative roles and permissions.
- Architecture and Environment Setup: Configure the MDM server instance, establish secure connections with manufacturer deployment portals (Apple Business Manager, Android Enterprise), and integrate with corporate identity providers.
- Policy and Profile Design: Draft configuration profiles, security baselines, and application deployment packages tailored to different user groups and device ownership models.
- Pilot Testing: Roll out the MDM configuration to a controlled pilot group—typically the IT department and a cross-section of volunteer business users. Validate enrollment workflows, test app push deployments, and verify security container isolation.
- Phased Enterprise Rollout: Execute the broader deployment in waves (by department, geography, or device type), providing clear communication, documentation, and helpdesk support to end-users.
- Continuous Monitoring and Optimization: Review compliance dashboards, audit security logs, update software deployment packages, and refine policies as organizational needs evolve.
Common Pitfalls and Troubleshooting Strategies
Organizations embarking on an MDM implementation frequently encounter avoidable challenges. Anticipating these hurdles ensures a smoother deployment lifecycle.
- Inadequate End-User Communication: If users do not understand why an MDM is being installed on their devices, they may perceive it as invasive spyware, leading to resistance and low adoption rates. Transparent communication highlighting privacy protections and productivity benefits is essential.
- Overly Restrictive Policies: Enforcing rigid security rules—such as extremely short screen timeouts or blocking essential consumer apps on personal devices—drives users toward shadow IT workarounds. Balance security mandates with practical usability.
- Neglecting Network Bandwidth: Pushing large software updates or multi-gigabyte line-of-business applications simultaneously to thousands of endpoints can saturate corporate internet bandwidth. Implement intelligent caching and staggered deployment schedules to mitigate network congestion.
- Orphaned Devices: When employees leave the organization or devices are retired without proper unenrollment procedures, they can remain active in the MDM console, skewing compliance metrics and wasting license allocations. Establish strict offboarding workflows that include automated device wiping and license reclamation.
Frequently Asked Questions
What is the difference between MDM and UEM?
Mobile Device Management (MDM) traditionally focuses on smartphones and tablets, emphasizing configuration profiles, security policies, and application management for mobile operating systems. Unified Endpoint Management (UEM) represents the evolution of MDM, combining traditional mobile management with desktop management capabilities for Windows, macOS, and Linux workstations, IoT devices, and ruggedized hardware into a single administrative platform.
Does an MDM allow employers to see personal data on a BYOD device?
No. In a properly configured Bring Your Own Device (BYOD) deployment utilizing containerization (such as Android Enterprise Work Profiles or Apple User Enrollment), the MDM administrator has zero visibility into personal photos, text messages, browsing history, or personal applications. The management capabilities are strictly constrained to the encrypted corporate container and baseline device compliance checks.
What happens to a device when it is unenrolled from an MDM?
When a device is officially unprovisioned and removed from the MDM platform, all corporate configuration profiles, security certificates, enterprise applications, and managed data containers are automatically deleted from the device. Personal files, photos, and personal applications remain untouched on employee-owned hardware.
Can an MDM solution track the physical GPS location of an employee?
While technical capabilities exist to track device GPS coordinates, most enterprise MDM platforms provide granular privacy controls regarding location tracking. Administrators can choose to disable location tracking entirely, restrict tracking to lost or stolen devices only, or provide clear disclosures to employees regarding when and why location data is accessed to comply with regional privacy regulations like GDPR.
How do updates affect MDM-managed devices?
MDM solutions allow IT administrators to manage operating system and application updates centrally. Administrators can test updates in a pilot environment, schedule installation windows to occur outside of business hours to prevent user disruption, and defer major operating system updates temporarily to ensure line-of-business application compatibility.
Conclusion and Next Actions
Deploying a comprehensive Mobile Device Management solution is no longer an optional luxury for modern enterprises; it is a fundamental requirement for maintaining security, regulatory compliance, and operational efficiency across distributed workforces. To begin your organization's MDM journey, conduct an inventory of your current endpoint ecosystem, define your security and compliance baselines, and engage reputable vendors for tailored demonstrations and proof-of-concept evaluations. By prioritizing user privacy, architectural scalability, and seamless integration, organizations can establish a resilient endpoint management strategy that empowers productivity while neutralizing modern cyber threats.