BJ’s Wholesale Club utilizes enterprise identity management solutions like OneLogin to streamline secure authentication, single sign-on (SSO), and identity governance for corporate employees, internal applications, and select partner ecosystems. This infrastructure enforces centralized credential control, multi-factor authentication (MFA), and role-based access control (RBAC) across corporate digital environments.
Understanding BJ's Wholesale Club and OneLogin
Enterprise identity and access management (IAM) forms the bedrock of modern corporate cybersecurity and operational efficiency. For large-scale retail organizations like BJ's Wholesale Club—operating numerous warehouse locations, distribution centers, and corporate offices—managing user identities efficiently is critical.
What is OneLogin?
OneLogin is a cloud-based Identity-as-a-Service (IDaaS) platform designed to secure user access to web applications, cloud infrastructure, and internal enterprise systems. Acquired by One Identity, the platform provides centralized directory integration, single sign-on capabilities, adaptive multi-factor authentication, and automated user provisioning. For large enterprises, deploying an IDaaS solution like OneLogin ensures that employees, contractors, and partners can access the exact tools they need while maintaining strict adherence to corporate security policies.
The Intersection of BJ's Wholesale Club and Enterprise IAM
When enterprise environments reference "BJ's Onelogin," they are typically pointing toward the centralized authentication portal used by BJ's Wholesale Club corporate team members, IT administrators, and authorized vendors. Rather than maintaining separate usernames and passwords for disparate software-as-a-service (SaaS) tools—such as human resources portals, inventory analytics platforms, communication tools, and ticketing systems—users authenticate through a unified OneLogin portal.
This centralization minimizes credential fatigue, reduces the attack surface vulnerable to phishing, and gives IT security teams granular visibility into user access logs and session behaviors.
Purpose and Core Benefits of the Integration
Integrating enterprise directories with an IDaaS platform like OneLogin yields substantial benefits for large retail corporations. These advantages span security enhancement, administrative efficiency, and improved user experience.
Enhanced Security Architecture
Retail environments handle vast amounts of sensitive data, ranging from corporate financial records to internal logistics data. Centralizing authentication through OneLogin allows security teams to enforce robust defensive postures:
- Adaptive Multi-Factor Authentication (MFA): Requires users to verify their identity using secondary methods (such as push notifications, authenticator apps, or hardware tokens) when logging in from unrecognized devices or novel geographic locations.
- Granular Role-Based Access Control (RBAC): Restricts application visibility and data access based on an employee's specific job function, department, or warehouse location.
- Immediate Revocation: Ensures that when a corporate employee or contractor leaves the organization, deactivating their account in the primary directory instantly revokes access across all integrated cloud and on-premises applications.
Operational and Administrative Efficiency
Managing hundreds or thousands of digital identities manually introduces human error and administrative overhead. Identity integration streamlines these workflows:
- Single Sign-On (SSO): Eliminates the need for users to remember multiple distinct credentials, drastically reducing the volume of password-reset helpdesk tickets.
- Automated Provisioning: Streamlines the onboarding and offboarding lifecycle by automatically assigning or removing application licenses and access permissions based on directory attributes.
Eligibility, Prerequisites, and Access Requirements
Accessing the corporate OneLogin portal associated with BJ's Wholesale Club is strictly restricted. It is not designed for retail warehouse club members or general shoppers managing personal loyalty or wholesale membership accounts.
Target User Segments
The authentication portal serves specific internal populations:
- Corporate Staff: Headquarters and administrative personnel requiring access to enterprise software suites.
- IT and Systems Administrators: Technical personnel responsible for managing user directories, security policies, and application integrations.
- Authorized Vendors and Partners: External entities granted temporary or specialized access to specific internal resources under strict contractual and technical oversight.
Technical Prerequisites for Users
To successfully authenticate and navigate the portal, users must typically meet specific technical and environmental requirements:
- Active Enterprise Account: A valid, active corporate user identifier provisioned by the internal IT department.
- Compliant Endpoints: Corporate-issued or authorized devices meeting baseline endpoint security policies (e.g., active antivirus, current operating system patches).
- MFA Enrollment: Registration of at least one approved multi-factor authentication device, such as a smartphone running a supported authenticator application.
Comparison of Access Management Tiers
To understand how enterprise identity solutions differ from consumer-facing accounts, the following table outlines the operational boundaries between corporate IAM portals and standard consumer warehouse membership portals.
| Feature / Attribute | Corporate OneLogin Portal | Consumer Membership Account |
|---|---|---|
| Primary Audience | Corporate employees, IT admins, approved vendors | Warehouse club shoppers and members |
| Authentication Goal | Enterprise application SSO and resource access | Shopping, coupon clipping, renewal management |
| Security Controls | Mandatory adaptive MFA, IP restrictions, strict RBAC | Standard password, optional consumer two-factor auth |
| Provisioning Source | Internal HR systems and Active Directory | Self-service consumer registration |
| Support Channel | Internal IT Helpdesk / Corporate Support | Customer Care / Club Member Services |
Step-by-Step Authentication and Navigation Workflow
For authorized users needing to access corporate applications through the portal, the standard operational sequence follows established enterprise IAM best practices.
1. Navigating to the Portal URL
Users must navigate to the specific corporate OneLogin subdomain designated for the organization. Entering credentials into unverified or generic login pages should be avoided to prevent credential harvesting.
2. Primary Credential Entry
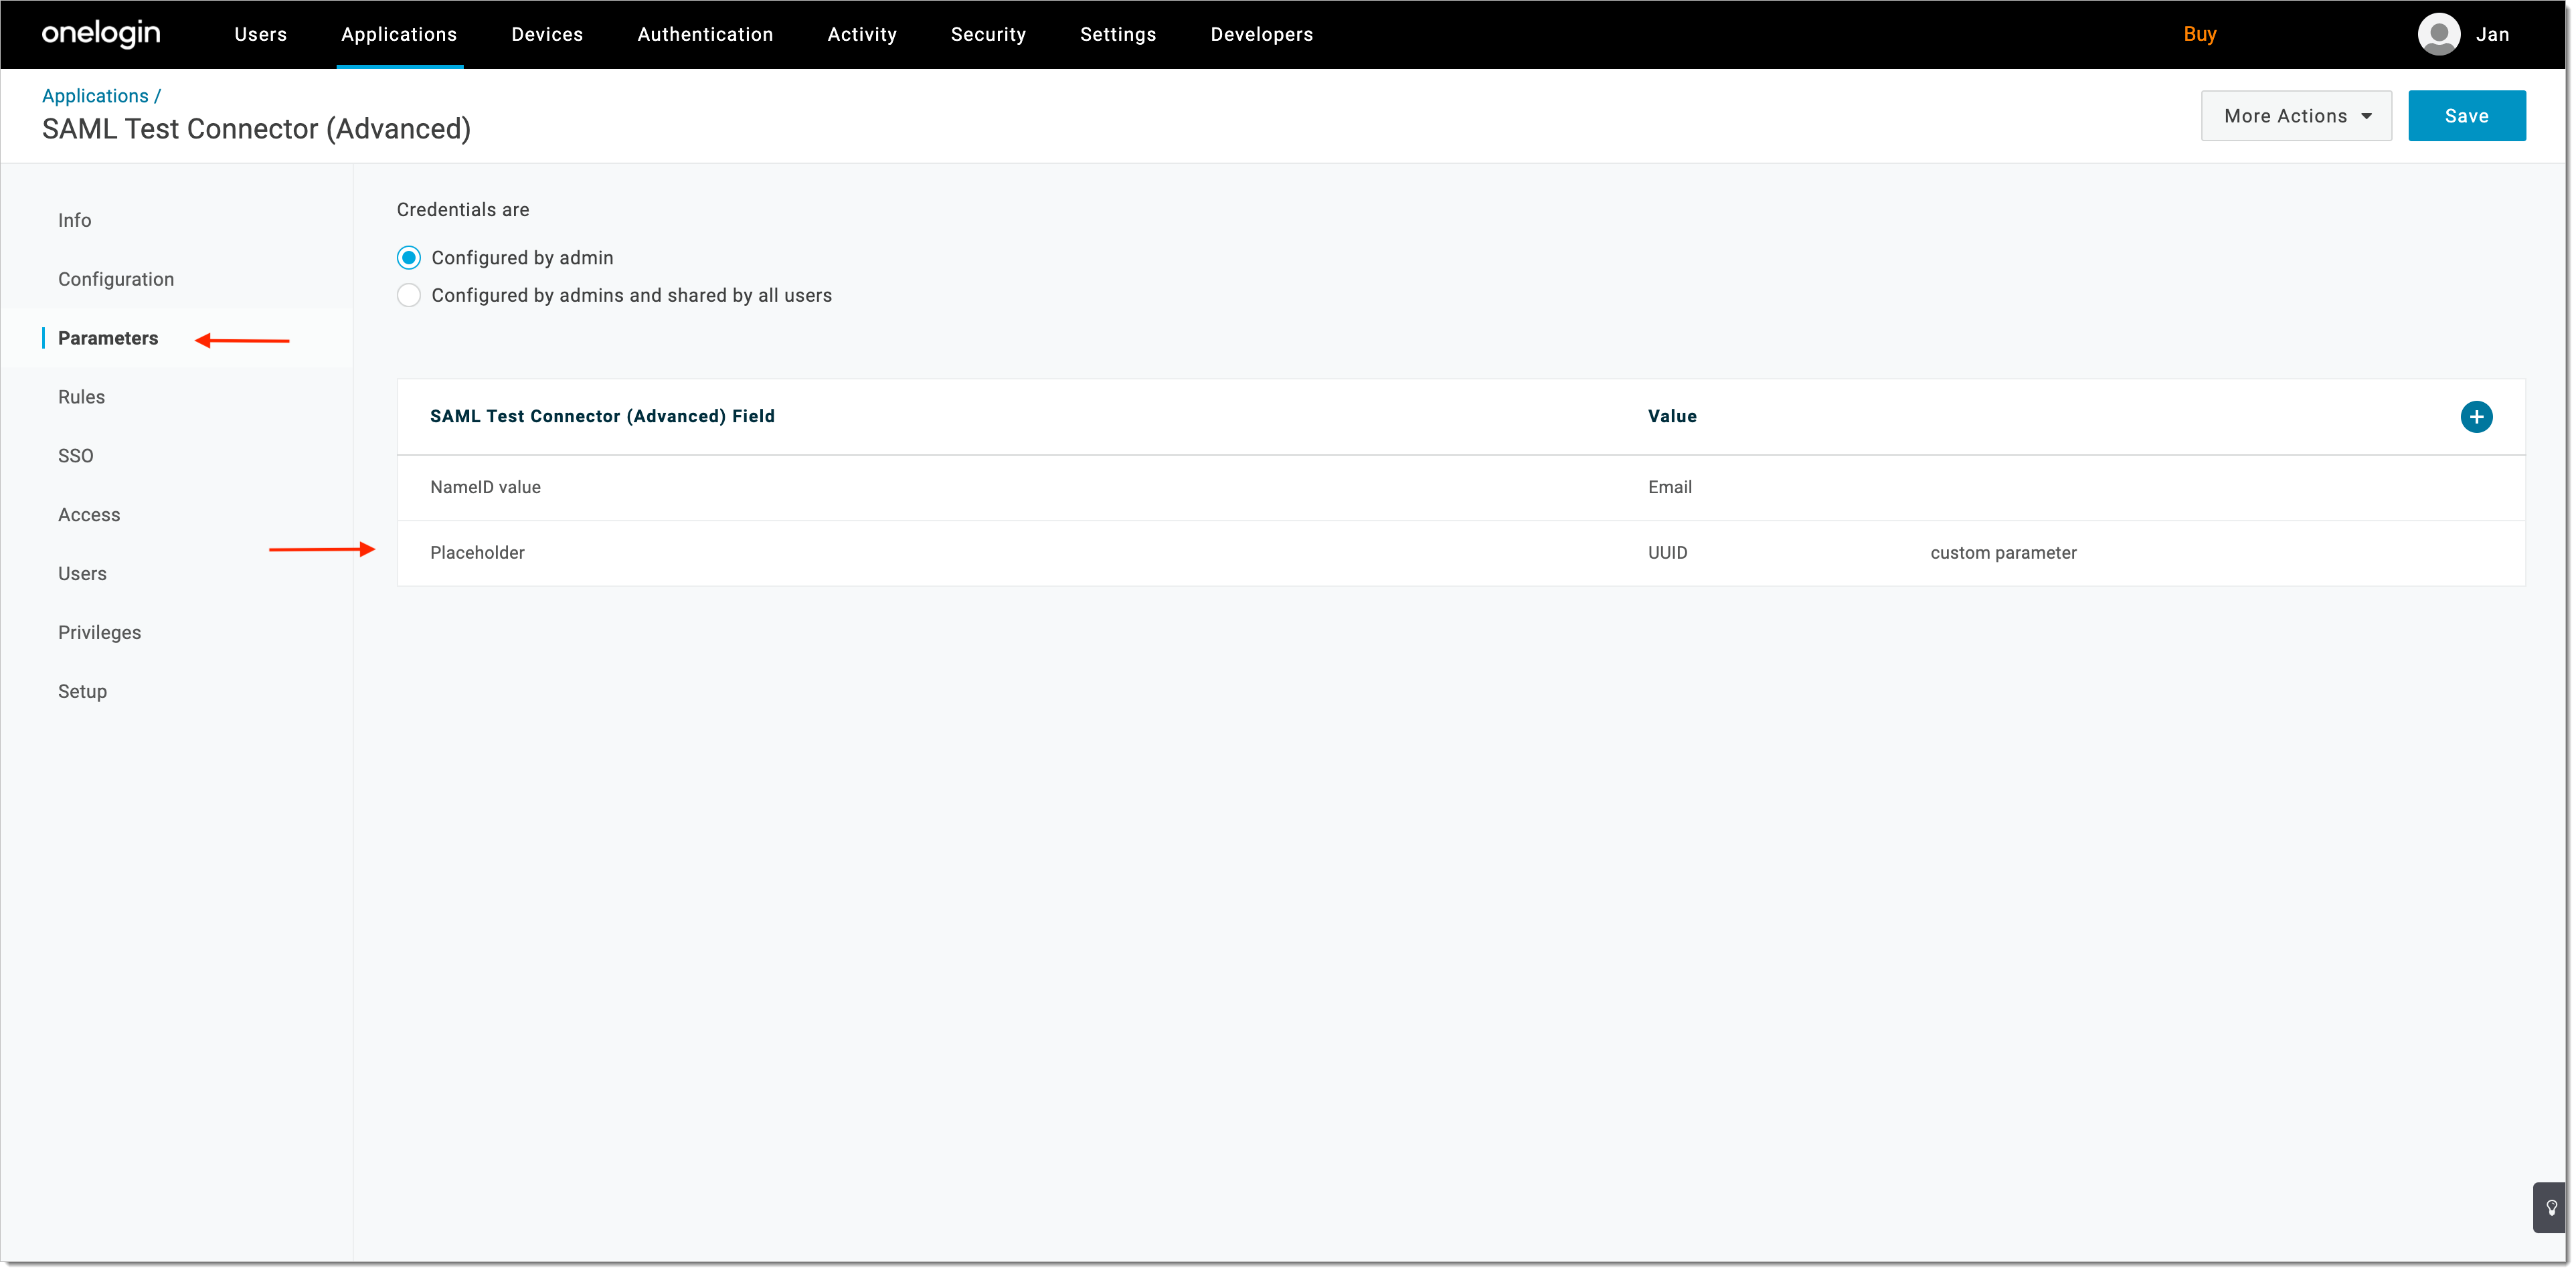
Users input their organizational username (often an email format) and their primary network password. These credentials are validated against the enterprise directory service (such as Microsoft Active Directory or Azure AD) integrated with the IDaaS instance.
3. Multi-Factor Authentication (MFA) Challenge
Upon successful validation of primary credentials, the system prompts the user for secondary verification. Depending on corporate policy, this may involve:
- Approving an push notification on a registered mobile device.
- Entering a time-based one-time password (TOTP) generated by an authenticator application.
- Providing biometric confirmation if accessing via supported mobile hardware.
4. Application Dashboard Navigation
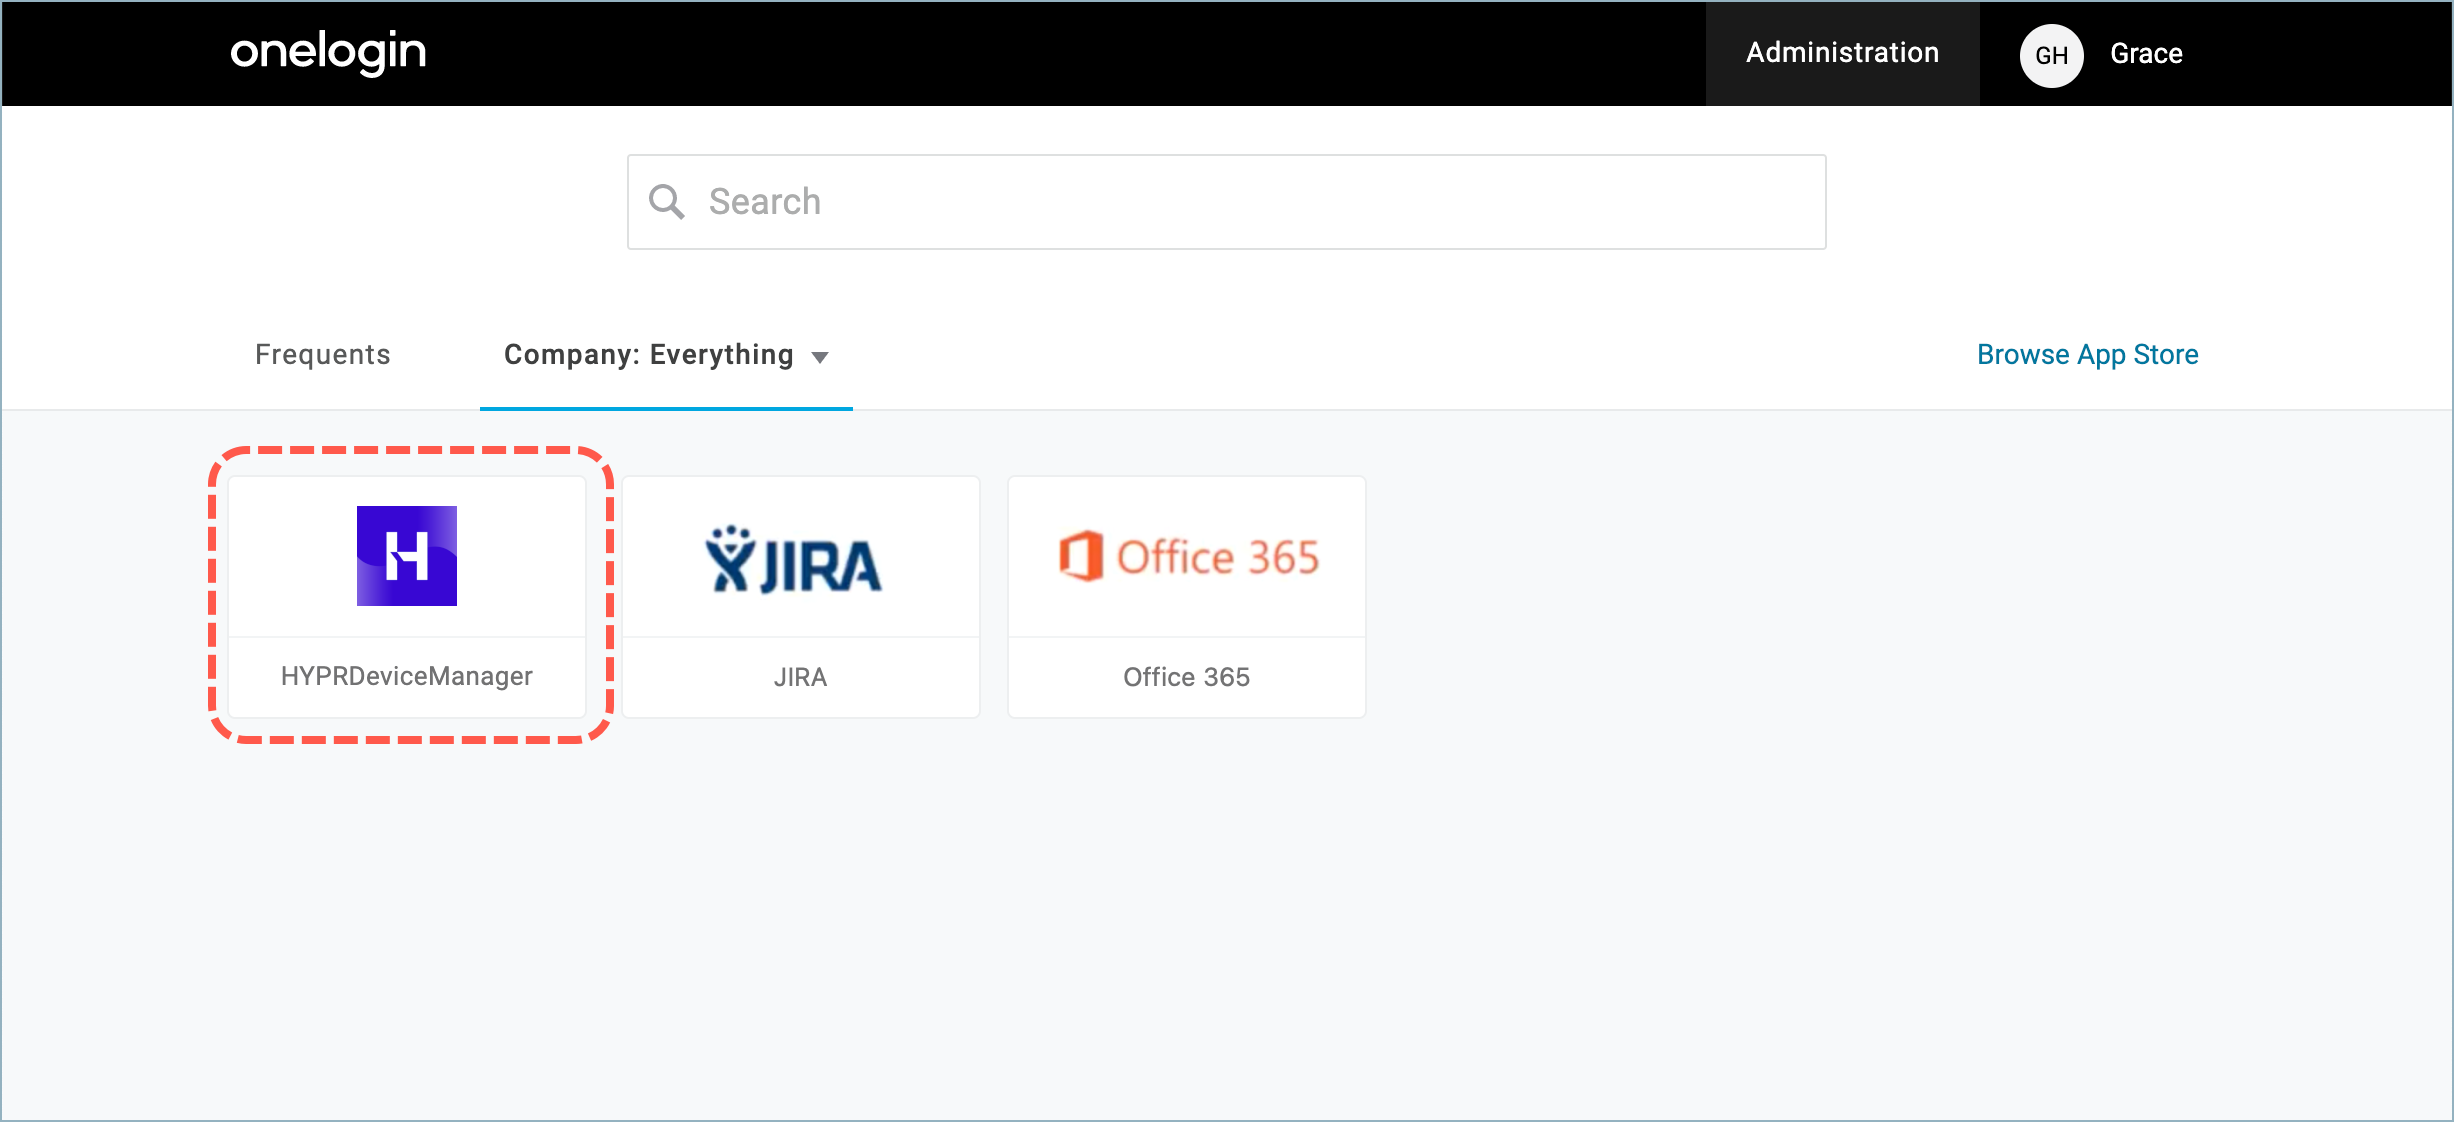
Once authentication succeeds, the user is presented with the OneLogin application catalog dashboard. This interface displays icons for all authorized SaaS and internal web applications the user has permission to access, enabling seamless single-click launching.
Common Challenges and Troubleshooting
Users attempting to access enterprise identity portals occasionally encounter technical roadblocks. Understanding these hurdles helps expedite resolution.
Authentication Failures and Locked Accounts
Exceeding the maximum allowed incorrect password attempts typically triggers an automatic account lockout to prevent brute-force attacks.
- Resolution: Users must contact the internal IT helpdesk or use self-service password reset mechanisms if pre-configured by their system administrators.
MFA Device Synchronization Issues
Push notifications failing to arrive or TOTP codes being rejected often stem from network latency or device time drift.
- Resolution: Ensure the mobile device has an active internet connection, verify that the device clock is set to automatic network time synchronization, or utilize alternative verification methods if available.
Browser Compatibility and Cache Conflicts
Outdated browsers or corrupted browser cache and cookies can interfere with SAML assertions and SSO token exchanges.
- Resolution: Clear browser cache and cookies, attempt authentication in an incognito or private browsing window, or switch to an officially supported enterprise browser version.
Security Best Practices for Identity Portals
Maintaining the integrity of corporate identity infrastructure requires strict adherence to cybersecurity guidelines.
- Never Share Credentials: Corporate accounts are strictly individual; sharing login details or MFA tokens violates baseline security policies.
- Report Suspicious Prompts: If an unexpected MFA push notification is received when the user is not actively attempting to log in, report the incident immediately to the security operations center (SOC).
- Secure Session Management: Always log out of the portal session and close the browser window when stepping away from shared or public workstations.
Conclusion
The integration of enterprise identity management solutions like OneLogin at organizations such as BJ's Wholesale Club provides a secure, scalable foundation for digital operations. By centralizing authentication, enforcing adaptive multi-factor security, and streamlining application access for authorized personnel, the organization safeguards sensitive data while optimizing user productivity. Understanding the clear distinction between internal administrative portals and consumer-facing membership accounts ensures proper navigation and adherence to enterprise security protocols.