The BAPLC login process provides authorized users with secure access to designated account management portals, administrative resources, and member-specific services. Gaining access typically requires navigating a secure authentication portal, entering valid credentials, and complying with specific organizational security policies or multi-factor verification steps.
Understanding the Purpose of the BAPLC Portal
Online portals serve as the central operational nexus for organizations, associations, or corporate entities utilizing specialized management software. The primary purpose of a dedicated login gateway is to secure sensitive data, restrict unauthorized entry, and provide a streamlined user experience for members, employees, or clients.
Digital access gates ensure that all backend activities—ranging from administrative updates to data retrieval—occur within a protected environment. By authenticating users through encrypted channels, organizations protect proprietary information, personal data, and operational logs from malicious actors. Understanding this objective framework helps users approach the login process with an awareness of why specific security measures, such as session timeouts and complex password requirements, are strictly enforced.
Prerequisites and Eligibility for Portal Access
Before attempting to use the login interface, individuals must satisfy specific prerequisites. Access to portals associated with organizational acronyms like BAPLC is rarely open to the general public; instead, it is restricted to verified stakeholders.
Identity Verification and Account Creation
Access requires an active, pre-approved account. New users cannot typically self-register without an invitation, employment contract, membership standing, or administrative approval. Identity verification often involves:
- An official corporate or organizational email address.
- A unique identification number assigned during onboarding.
- Verification through an IT administrator or human resources department.
Technical System Requirements
Modern web portals utilize advanced encryption and dynamic scripting, which places demands on user hardware and software. To prevent authentication failures, users should ensure they meet baseline technical standards:
- Web Browsers: Access is optimized for current versions of major browsers, including Google Chrome, Mozilla Firefox, Apple Safari, and Microsoft Edge. Outdated browsers may fail to load security certificates.
- JavaScript and Cookies: Browsers must have JavaScript enabled and accept secure session cookies to handle authentication tokens.
- Network Stability: A stable broadband or secure cellular connection is required to prevent packet loss during the cryptographic handshake between the user's browser and the server.
Step-by-Step Guide to the Login Process
Executing a successful login involves a systematic sequence of actions designed to prove identity and establish an encrypted session.
- Navigate to the Official Portal: Open a trusted web browser and enter the verified URL for the portal. Avoid clicking unverified links found in search engine advertisements or unsolicited emails to prevent phishing attacks.
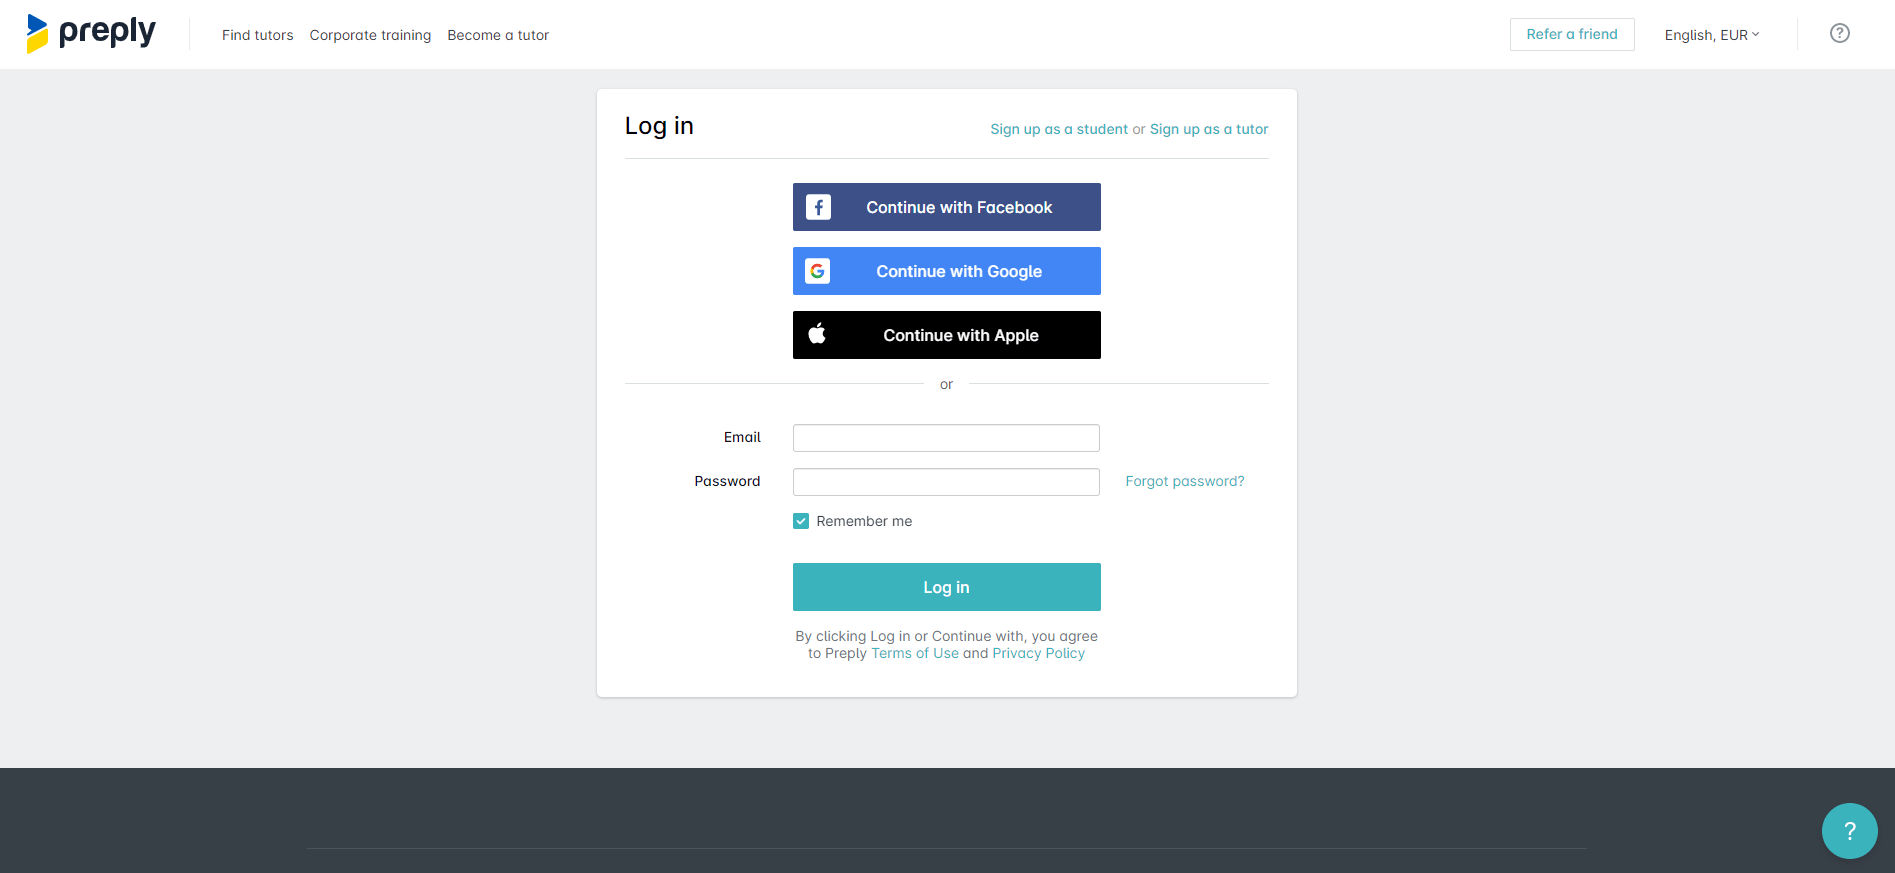
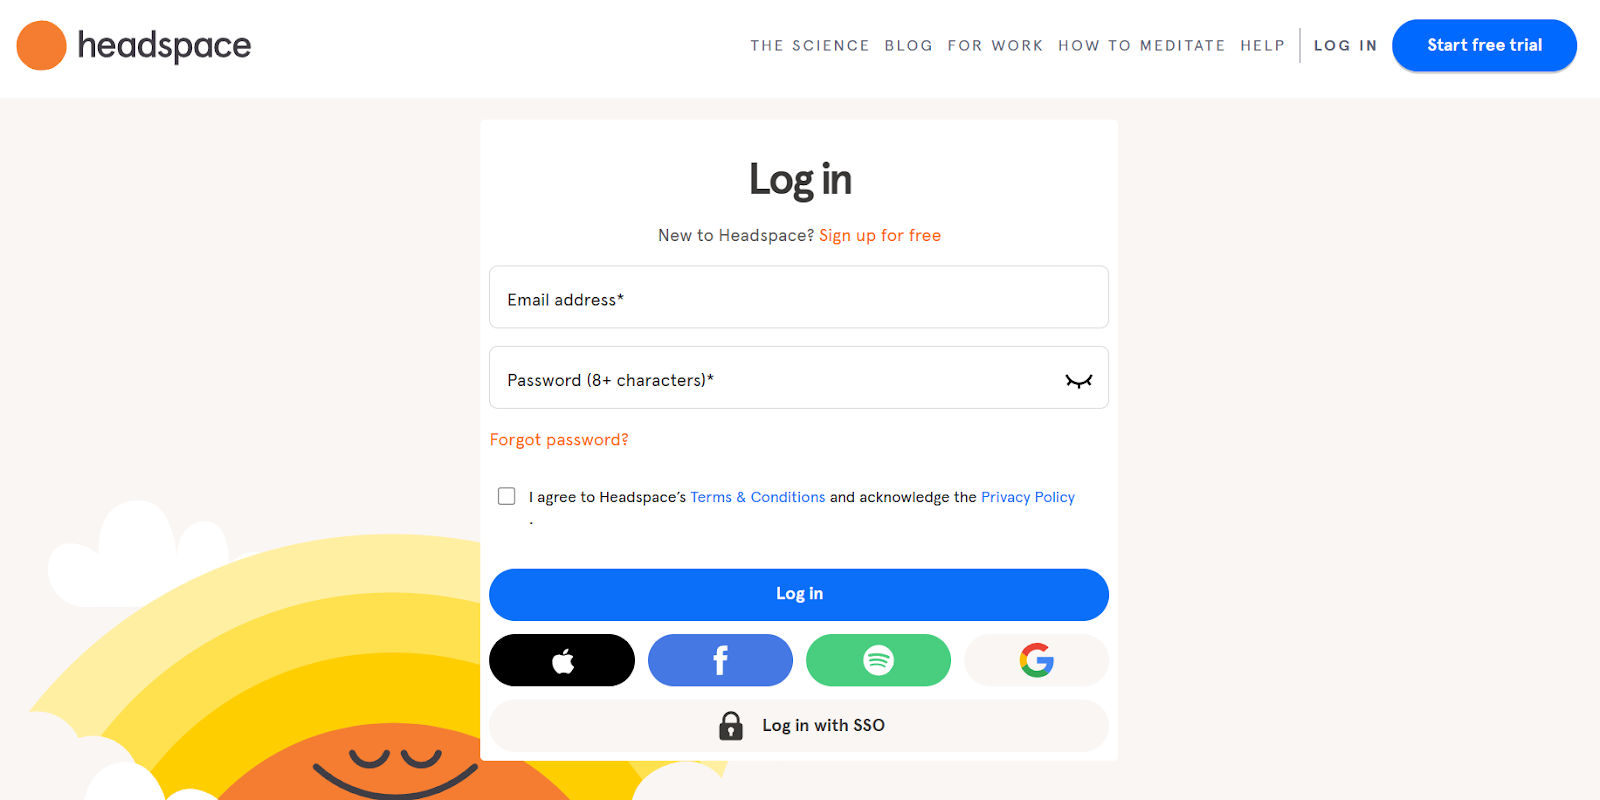
- Locate the Authentication Fields: On the homepage, find the designated login area, usually marked by "Sign In," "Log In," or "Portal Access."
- Enter Credentials: Input your registered username (frequently an email address) and your secure password into the respective form fields.
- Complete Multi-Factor Authentication (MFA): If enabled by the system administrator, enter the one-time passcode (OTP) sent via SMS, generated by an authenticator application (such as Google Authenticator or Microsoft Authenticator), or delivered to an alternative email address.
- Establish the Session: Click the submit button. Upon successful verification, the browser will redirect you to your personalized dashboard or account management interface.
| Step | Action Required | Potential Risk / Error | Corrective Action |
|---|---|---|---|
| 1. Navigation | Enter official URL | Phishing site redirection | Bookmark the genuine login page; check SSL certificates. |
| 2. Input | Type username and password | Typographical errors | Use a password manager to securely auto-fill credentials. |
| 3. MFA | Provide secondary token | Expired code or delayed SMS | Resend code or check authenticator app synchronization. |
| 4. Session | Access dashboard | Session timeout / 403 error | Clear browser cache and cookies; log in again. |
Account Security and Credential Management
Maintaining the integrity of a secure portal requires strict adherence to password hygiene and security protocols. Because digital accounts are frequent targets for credential-stuffing attacks and social engineering, users must manage their credentials proactively.
Password Complexity and Rotation
Passwords should be robust, combining uppercase and lowercase letters, numeric digits, and special symbols. Avoid using predictable sequences, personal information, or dictionary words. Many enterprise-grade systems mandate periodic password rotation, requiring users to update their credentials every 90 days. Reusing passwords across multiple platforms dramatically increases vulnerability; if a secondary website suffers a data breach, attackers can test those same credentials against administrative portals.
Multi-Factor Authentication Best Practices
Multi-factor authentication adds a vital layer of defense beyond standard passwords. Even if an unauthorized party discovers your password, they cannot gain entry without the secondary verification factor. App-based MFA generators are generally preferred over SMS text messages, as the latter can be intercepted via SIM-swapping attacks.
Common Login Issues and Troubleshooting
Users occasionally encounter technical roadblocks during authentication. Recognizing the symptoms of these errors allows for rapid resolution without unnecessary escalation to support desks.
Invalid Credentials Error
The most frequent issue is an incorrect username or password. Before submitting a support ticket, verify that your Caps Lock key is disabled and check for trailing spaces copied during auto-fill operations. If the password remains unrecognized, utilize the self-service "Forgot Password" or "Reset Password" utility linked on the login page.
Account Lockout Protocols
To thwart brute-force attacks—where automated scripts attempt thousands of password combinations per minute—systems automatically lock accounts after a specific number of consecutive failed attempts (typically three to five). If an account is locked, users must either wait for the lockout timer to expire (often 15 to 30 minutes) or contact their system administrator to manually reset the status.
Browser Compatibility and Cache Conflicts
Corrupted cache files, outdated cookies, or aggressive ad-blockers can interfere with login scripts, resulting in blank screens or infinite redirect loops. Troubleshooting steps include:
- Opening the portal in an Incognito or Private Browsing window to test without extensions.
- Clearing cached images and files for the specific domain.
- Updating the web browser to the latest stable release.
Frequently Asked Questions
What should I do if I forget my login password?
Locate the "Forgot Password" or "Reset Credentials" link located directly beneath the login form. Enter your registered email address or username to receive a secure password-reset link. Follow the instructions within the email to establish a new, secure password. If you do not receive the email within a few minutes, check your spam folder or contact your organization's IT support desk.
Why does the portal keep logging me out automatically?
Portals implement automated session timeouts for security reasons. If a user remains inactive for a designated period (such as 15 or 30 minutes), the server terminates the session to prevent unauthorized access if the device is left unattended. Saving your work frequently and refreshing your browser window can help maintain active connections during long administrative sessions.
Is it safe to save my login credentials in my web browser?
Saving credentials in modern, encrypted browsers or reputable third-party password managers is generally considered safe for personal devices, provided the device itself is protected by a strong biometric lock or login PIN. However, you should never save credentials on shared, public, or library computers.
How can I enable multi-factor authentication on my account?
If multi-factor authentication is not enabled by default, navigate to your account settings or security profile page after logging in. Look for a section labeled "Two-Factor Authentication," "Security Settings," or "MFA." Follow the on-screen prompts to link an authenticator app or register a trusted mobile phone number.
Who should I contact if my account remains locked?
If self-service recovery options fail or your account is permanently suspended due to security policies, reach out directly to your organization’s internal IT helpdesk, system administrator, or customer support team. Provide your username and a clear description of the error message encountered to accelerate the resolution process.
Next Actions and Recommendations
To ensure uninterrupted access to your account, bookmark the verified BAPLC login page directly in your browser rather than relying on search engine results. Periodically review your security settings, ensure your recovery email is up to date, and adopt a reliable password manager to protect your credentials against emerging digital threats.