iOS security is a multi-layered, hardware- and software-integrated defense model designed to protect user data, system integrity, and device privacy against sophisticated local and remote threats. This architecture combines a secure boot chain, dedicated hardware security components like the Secure Enclave, strict application sandboxing, and continuous code signing enforcement to maintain a high baseline of protection without compromising everyday usability.
Foundations of iOS Security Architecture
The defensive posture of Apple's mobile operating system is built on the principle of defense-in-depth. Every layer of the system—from silicon up to the user interface—relies on the layer beneath it to verify its integrity. This structured approach prevents unauthorized modifications and ensures that even if one security boundary is compromised, subsequent barriers remain intact.
The Secure Boot Chain and Hardware Root of Trust
The foundation of iOS security is established at the hardware level through the Secure Boot Chain. When an iOS device powers on, its application processor executes immutable code stored in dedicated Read-Only Memory (ROM), often referred to as the Boot ROM. This code contains Apple's root public key, which is used to cryptographically verify the integrity of the Low-Level Bootloader (LLB).
Once the LLB is verified and executed, it proceeds to verify and load the iBoot bootloader, which in turn verifies the kernel and the rest of the operating system before allowing the device to boot. This continuous validation process ensures that no unauthorized, modified, or jailbroken operating system components can be loaded into memory. If any signature fails verification, the device enters a recovery mode or refuses to boot entirely, preventing persistence vectors from altering the core system files.
The Secure Enclave Processor
Modern iOS devices feature a dedicated, isolated subsystem known as the Secure Enclave Processor (SEP). The SEP operates independently of the main application processor and runs its own secure operating system. It manages cryptographic operations for device features, protects encryption keys, and enforces security policies related to user authentication, such as Touch ID and Face ID biometric data.
Biometric templates are never transmitted to Apple servers or stored in accessible device storage. Instead, mathematical representations of the user's face or fingerprint are processed within the Secure Enclave and checked against encrypted keys stored securely within the hardware. This isolation ensures that even if the main operating system kernel is compromised by malware, the cryptographic keys protecting user data remain safe within the hardware boundary of the Secure Enclave.
Application Sandboxing
Every third-party app installed on iOS operates within a strict security boundary known as a sandbox. The sandbox limits an application's access to files, preferences, network resources, and hardware components. Applications cannot read data written by other apps, modify system files, or access sensitive hardware sensors without explicit user authorization mediated by the operating system.
Data sharing between applications is tightly controlled through system-defined mechanisms, such as document providers, URL schemes, and extensions that run in separate, isolated processes. This containment strategy prevents a compromised application from escalating privileges or spreading malicious code to other parts of the system or user data repository.
Code Signing, Verification, and Memory Protection
To ensure that malicious code cannot execute on the device, iOS enforces a strict execution policy: every piece of code running on the device must be cryptographically signed by an approved certificate authority.
Mandatory Code Signing
Developers must sign their applications using certificates issued by Apple. During installation, the operating system verifies the cryptographic signature of the application binary, ensuring that it has not been tampered with since it was built and that it originates from a verified developer account.
Furthermore, iOS enforces dynamic code signing protections. Applications cannot generate executable code at runtime (often referred to as write-XOR-execute or W^X enforcement). This stops an entire class of exploitation techniques, such as return-oriented programming (ROP) and buffer overflow attacks that attempt to inject and execute shellcode in memory.
Advanced Memory Safety Mitigations
Apple continuously integrates advanced compiler-level and kernel-level mitigations to stop memory corruption vulnerabilities. These include:
- Address Space Layout Randomization (ASLR): Randomly shifts the locations of key data areas, such as the base of the executable, the stack, the heap, and libraries, in a process's address space, making it difficult for an attacker to predict target addresses.
- Pointer Authentication Codes (PAC): Utilizes specialized hardware instructions to cryptographically sign pointers in memory. If an attacker attempts to overwrite a function pointer, the signature becomes invalid, and the processor halts execution immediately.
- KTRR (Kernel Text Read-Only Region): Hardware-enforced protection that locks down the kernel read-only memory regions, preventing unauthorized runtime patches to the kernel.
Data Protection and Cryptography
Data security on iOS centers on robust, hardware-backed encryption that protects files both at rest and in transit. The Data Protection API allows developers and the operating system to apply granular encryption policies to individual files and database entries.
Encryption Classes and Key Hierarchy
When a user sets a device passcode, iOS derives a master key using cryptographic algorithms combined with hardware-specific identifiers stored in the Secure Enclave. This key is never exposed to the software layer in plaintext. Files are categorized into different Data Protection classes based on when they need to be accessed:
- Complete Protection (NSFileProtectionComplete): Files are inaccessible when the device is locked. The decryption key is discarded from memory shortly after the device locks and is only retrieved when the user unlocks the device with their passcode or biometrics.
- Complete Until First User Authentication (NSFileProtectionCompleteUnlessOpen): Files can be accessed even after the device locks if they were already open. If closed, they cannot be reopened until authentication occurs.
- Complete Unless Open (NSFileProtectionCompleteUntilFirstUserAuthentication): The default class for many app files. Keys remain available after the device boots once the user has unlocked the device at least once, allowing background processes to function.
- No Protection (NSFileProtectionNone): Files are encrypted using a key tied to the device hardware, accessible as long as the device is powered on, regardless of lock status.
| Data Protection Class | Key Availability | Typical Use Case |
|---|---|---|
| Complete Protection | Only when device is unlocked | Highly sensitive user data, financial records, health data |
| Complete Unless Open | Accessible if opened before lock; locked otherwise | Standard application documents and cached data |
| Complete Until First Auth | Available after first unlock following reboot | Background tasks, push notifications, essential app services |
| No Protection | Always available while powered on | Non-sensitive cache files, temporary assets |
Advanced Data Protection for iCloud
Expanding upon local file encryption, Apple offers Advanced Data Protection for iCloud, which utilizes end-to-end encryption for the majority of cloud-stored data categories. When enabled, data such as iCloud Backups, Notes, Photos, Reminders, and Safari Bookmarks are encrypted using keys known only to the user's trusted devices. This ensures that even in the event of a cloud infrastructure breach or a legal subpoena directed at cloud data providers, the underlying user content cannot be decrypted by unauthorized parties.
Network Security and Communication Privacy
Protecting data in transit is equally critical to the iOS security model. The operating system enforces secure network communications defaults and provides mechanisms to audit and restrict network activity.
Transport Layer Security (TLS) Requirements
iOS enforces strict Transport Layer Security (TLS) standards. By default, App Transport Security (ATS) requires all HTTP connections made by applications to use secure HTTPS protocols backed by modern TLS versions (TLS 1.2 or TLS 1.3) with secure cipher suites and forward secrecy. Developers must explicitly request exceptions for legacy or non-secure backend services, which are subject to rigorous review during the App Store submission process.
VPN Frameworks and Network Extensions
Enterprise and personal users can leverage robust VPN (Virtual Private Network) frameworks and Network Extension APIs to tunnel traffic securely. iOS supports modern protocols such as IKEv2 and WireGuard (via third-party applications), alongside Per-App VPN configurations. Per-App VPN ensures that only designated corporate applications route their traffic through the secure corporate gateway, while personal traffic remains direct and unencrypted by the enterprise, balancing privacy with security.
Privacy Controls and User Consent Frameworks
Security on iOS is deeply intertwined with user privacy. The operating system provides granular authorization prompts before applications can access sensitive sensors, personal data, or hardware capabilities.
Transparency and Control Over Permissions
Applications must declare their intended data access requirements within their configuration manifest files. When an app attempts to access sensitive resources for the first time, iOS presents a mandatory system-prompt asking the user to grant or deny permission. These permissions cover:
- Location services (precise vs. approximate)
- Camera and microphone access
- Contacts, calendars, and reminders
- Local network discovery
- Bluetooth peripherals
- App Tracking Transparency (ATT) across other companies' apps and websites
Users can review, audit, and revoke these permissions at any time through the system Settings application, ensuring continuous oversight of application behavior.
Enterprise Management and Device Supervision
For organizational deployments, iOS provides a comprehensive framework for Mobile Device Management (MDM) and supervision. Supervision mode unlocks advanced configuration options that allow IT administrators to enforce security compliance policies across fleet devices.
Remote Configuration and Security Enforcement
Through MDM solutions, organizations can enforce strict passcode complexities, disable specific hardware features (such as the camera, Siri, or AirDrop), mandate encrypted backups, and deploy secure certificates. Furthermore, automated enrollment programs ensure that devices purchased through corporate channels are automatically tethered to the organization's MDM profile out of the box, preventing users from bypassing enterprise security controls during initial setup.
Managed Apple IDs and Data Separation
Enterprises can provision Managed Apple IDs for employees. These accounts allow organizations to manage cloud storage and application licenses while maintaining a strict cryptographic boundary between personal and corporate data on the same device. Managed apps and corporate documents remain containerized and can be wiped remotely by the organization without touching the user's personal photos, messages, or applications.
Common Security Misconfigurations and Troubleshooting
While iOS provides robust default protections, user configuration errors and outdated software can introduce vulnerabilities. Maintaining optimal device security requires addressing common operational hurdles.
Updating and Patch Management
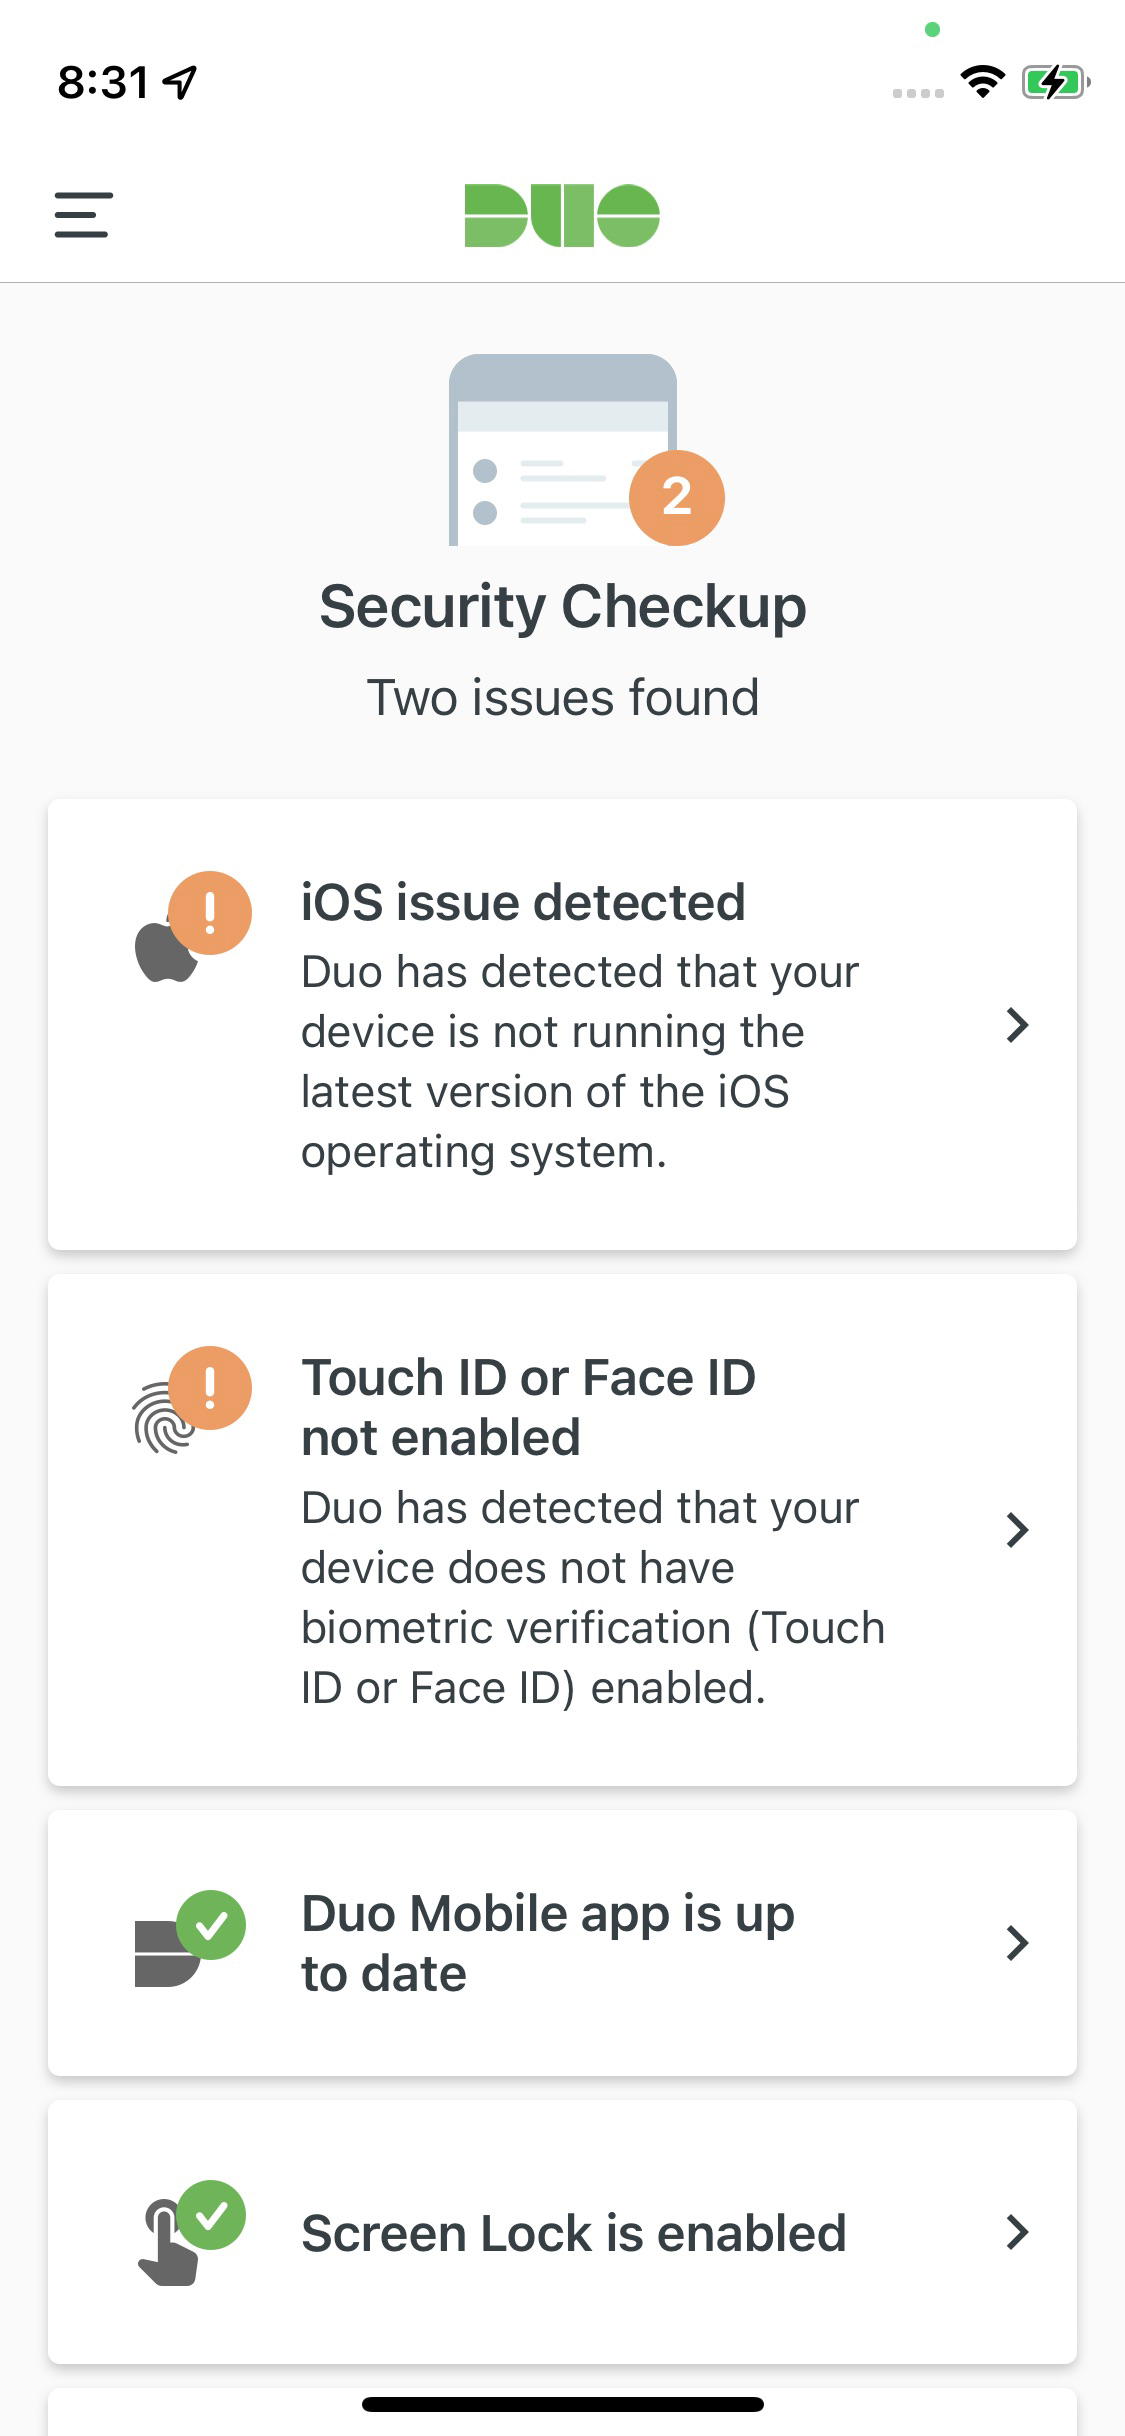
The most effective countermeasure against emerging threats is maintaining an up-to-date operating system. Apple issues security updates regularly, addressing zero-day vulnerabilities and known exploit chains. Users should enable automatic updates (Settings > General > Software Update > Automatic Updates) to ensure critical security patches are applied promptly without requiring manual intervention.
Managing Lost or Stolen Devices
In the event of a lost or stolen device, users should leverage the Find My network. Activating Lost Mode remotely locks the device with a passcode, suspends Apple Pay functionality, and displays a custom message with contact information. If the device cannot be recovered, users can initiate a remote wipe command to purge all local data while retaining Activation Lock, which renders the device permanently unusable to unauthorized holders by tying it to the original owner's Apple ID.
Frequently Asked Questions
Can iOS devices get viruses or malware?
While traditional computer viruses are rare on iOS due to application sandboxing and code signing, devices are still susceptible to other threats, such as sophisticated spyware, phishing attacks, malicious configuration profiles, and zero-day exploits targeting browser or kernel vulnerabilities. Maintaining updated software remains the primary defense against these vectors.
What is the difference between standard iCloud encryption and Advanced Data Protection?
Standard iCloud encryption protects most data categories in transit and on Apple servers, but Apple retains the decryption keys for certain services to facilitate account recovery. Advanced Data Protection enables end-to-end encryption for additional categories like backups, notes, and photos, meaning keys are held exclusively on your trusted devices and Apple cannot decrypt them even under legal demand.
How does App Tracking Transparency protect my privacy?
App Tracking Transparency (ATT) requires applications to obtain explicit user consent before tracking user activity across apps and websites owned by other companies. When denied, the application is blocked from accessing the Identifier for Advertisers (IDFA), preventing advertisers from building a comprehensive cross-app behavioral profile.
Is jailbreaking safe for my device?
Jailbreaking removes the built-in software restrictions imposed by iOS, allowing the installation of unauthorized apps and system modifications. However, this process disables critical security barriers, including the secure boot chain verification, app sandboxing, and code signing enforcement, leaving the device exposed to malware and data theft.
How can I secure my Apple ID against unauthorized access?
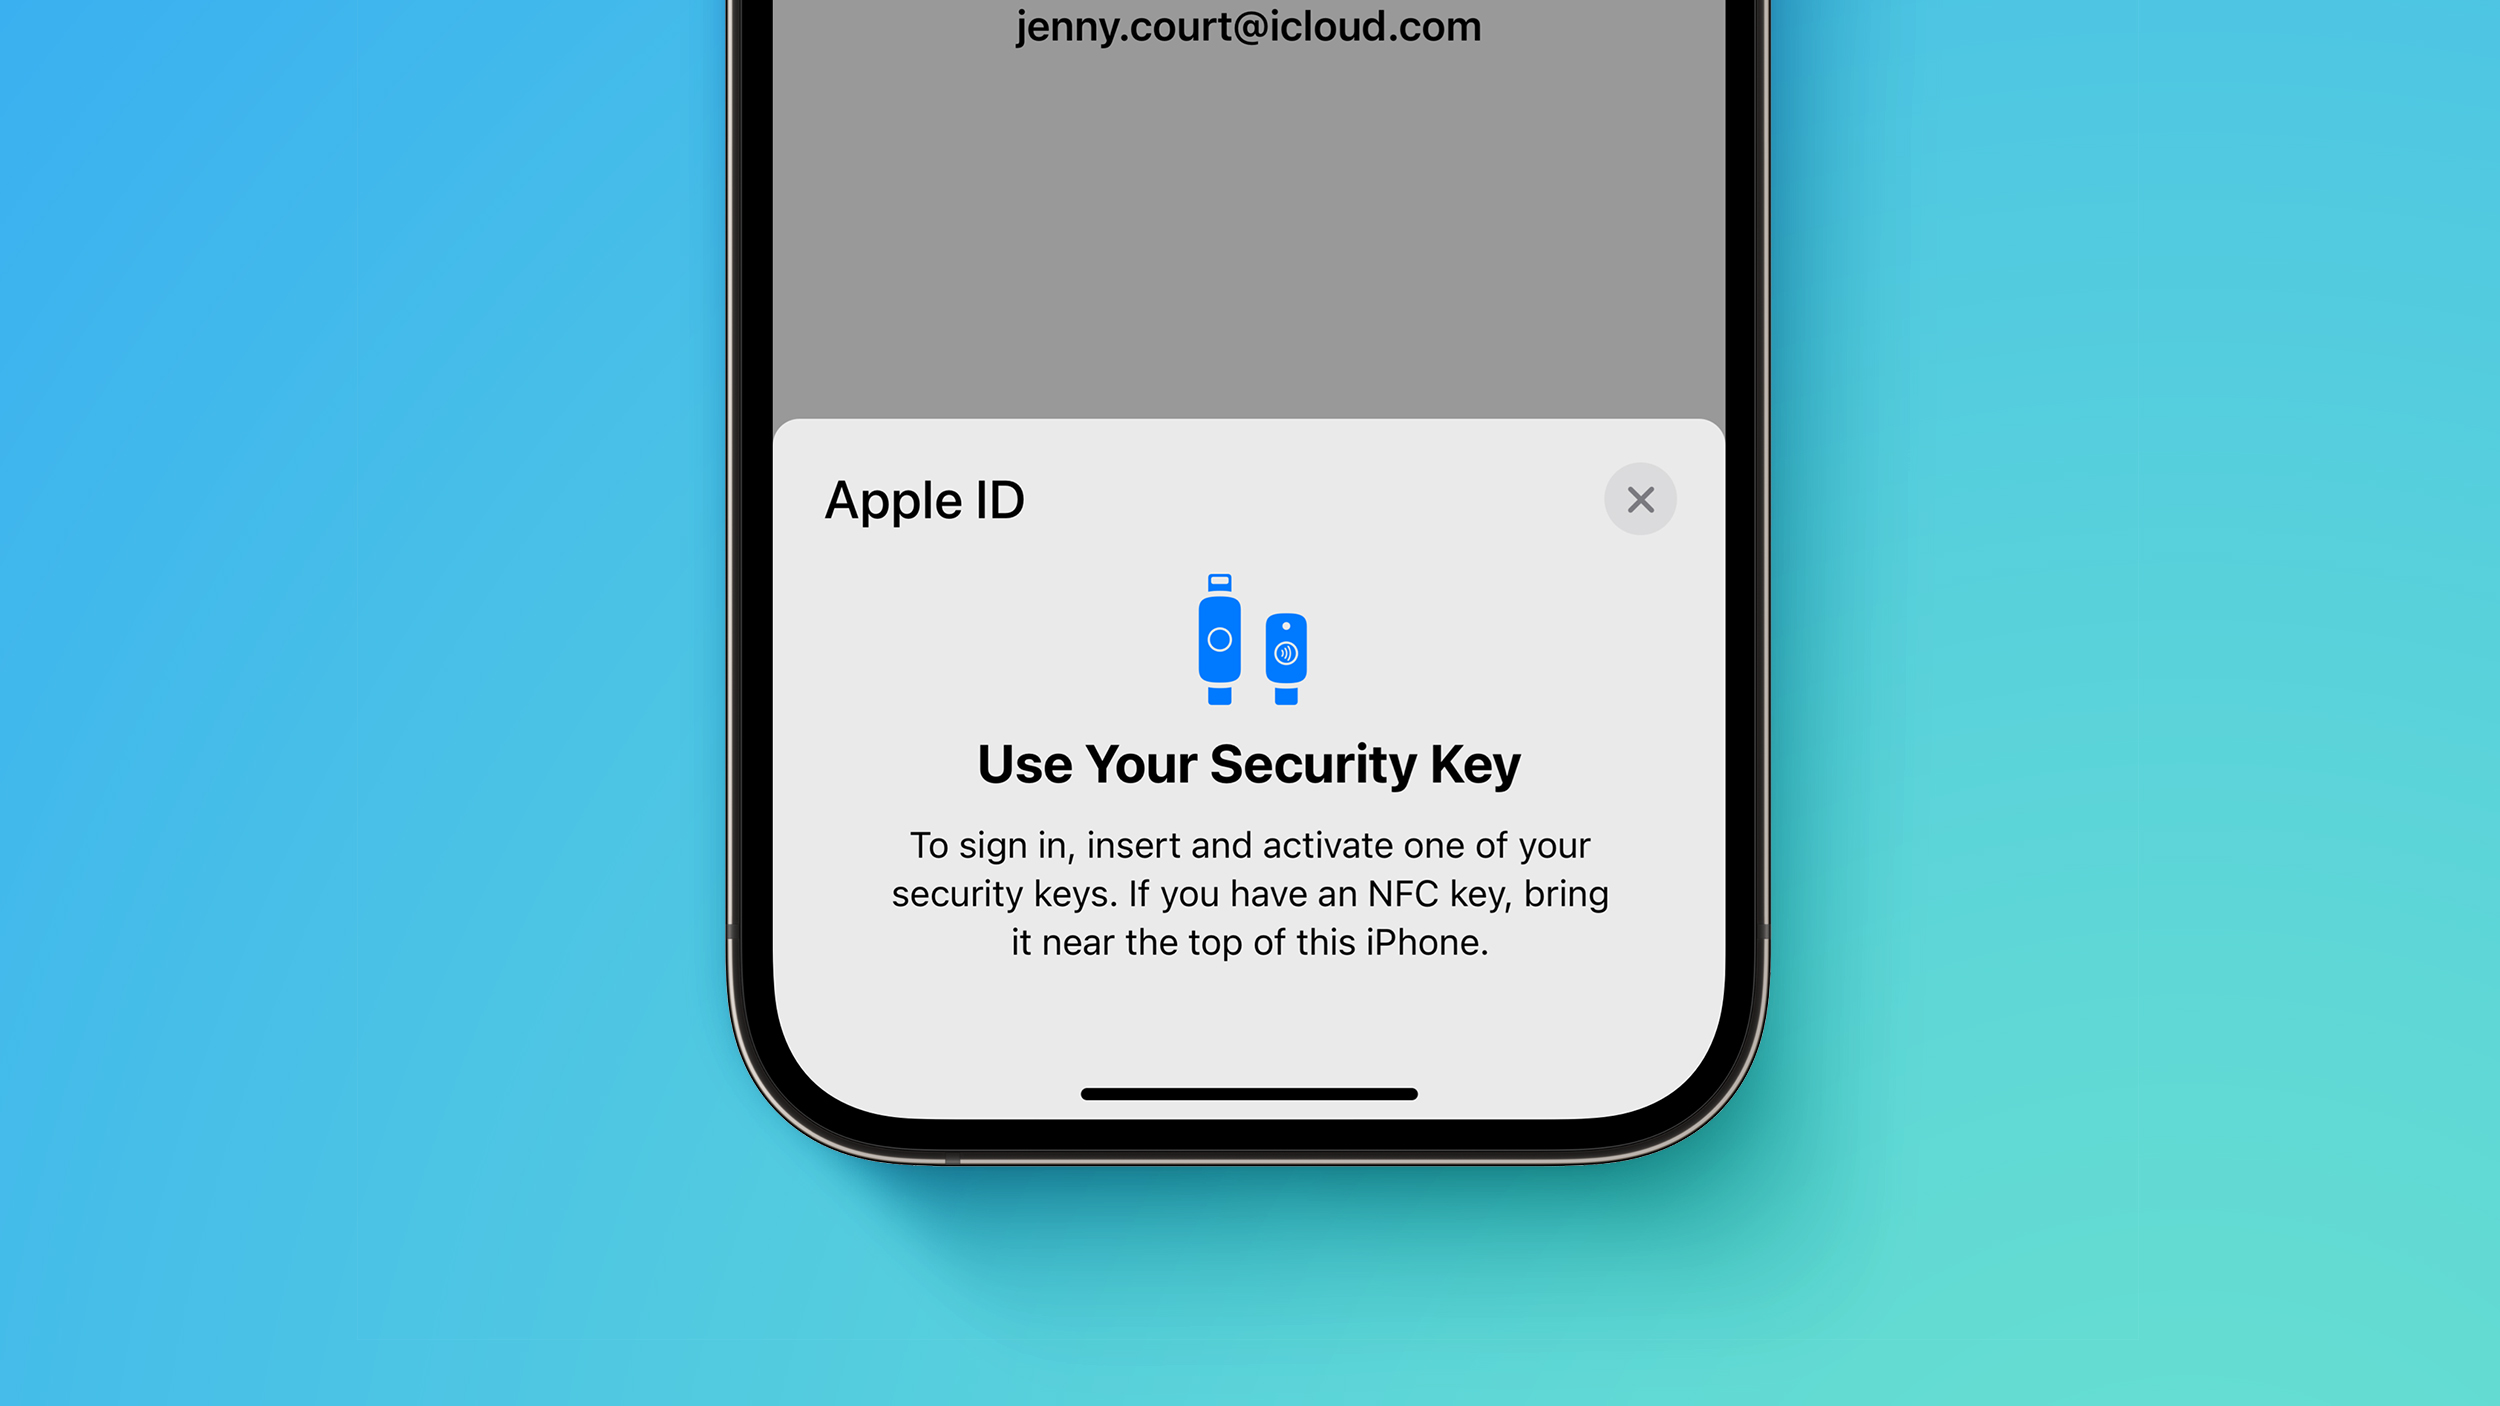
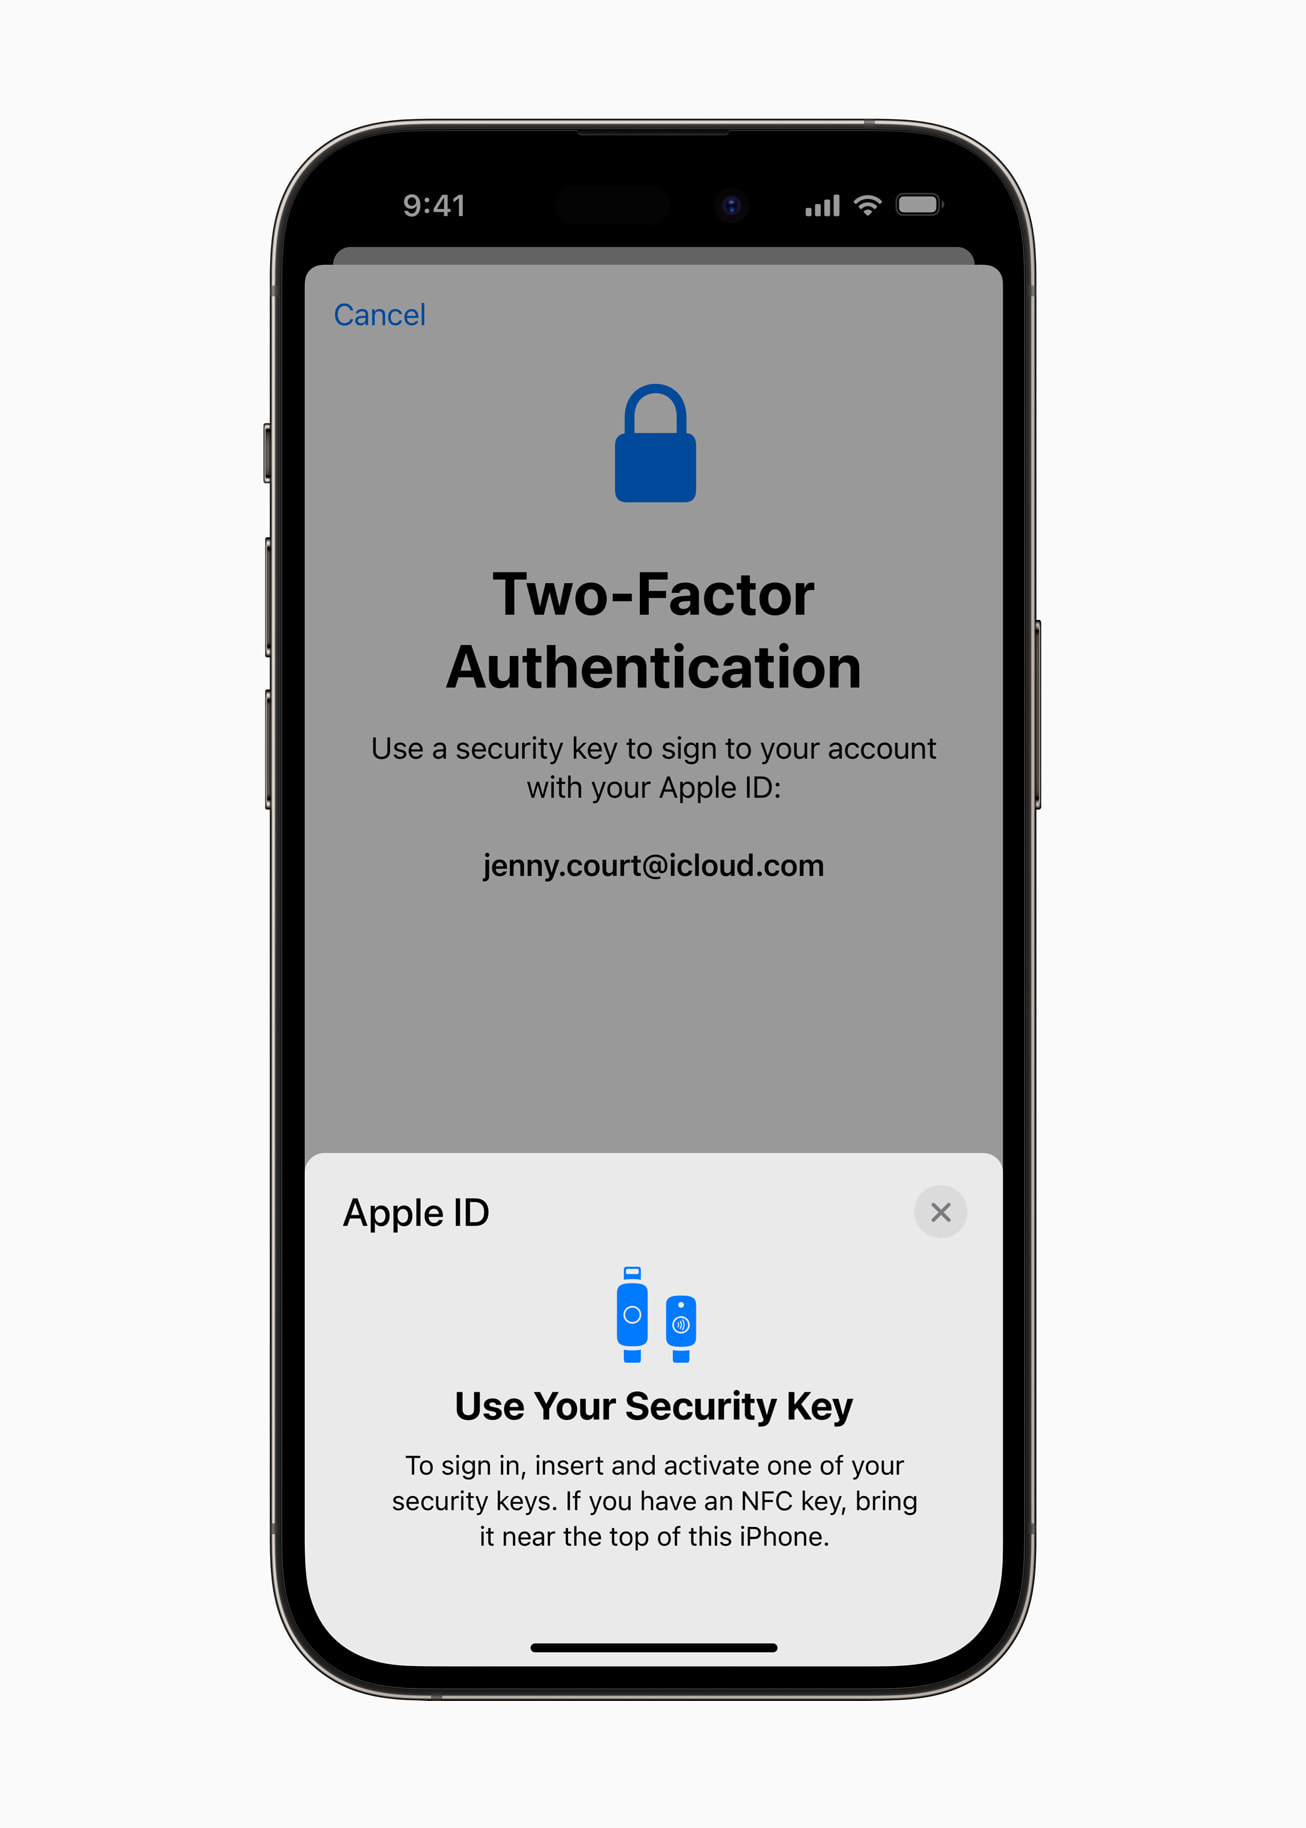
Securing an Apple ID requires enabling two-factor authentication (2FA), using a strong, unique password, and regularly reviewing trusted devices associated with the account. Additionally, users should never share verification codes and should remain vigilant against phishing messages designed to mimic Apple support notifications.
Recommendations for Maintaining Optimal Device Security
To maintain a secure iOS environment, enforce a proactive security routine: enable automatic software updates, review application privacy permissions periodically to revoke unnecessary access, utilize strong passcodes paired with biometric authentication, and enable Advanced Data Protection for iCloud if end-to-end cloud security is a priority. For enterprise environments, deploy a managed MDM solution to enforce centralized compliance policies and protect corporate assets from unauthorized exposure.