PCI testing refers to the assessment procedures required to validate that an organization protects cardholder data in accordance with the Payment Card Industry Data Security Standard (PCI DSS). These assessments, which include vulnerability scanning and penetration testing, are mandatory for businesses that process, store, or transmit credit card information to ensure secure transaction environments and mitigate the risk of data breaches.
The Role of PCI DSS in Modern Commerce
The Payment Card Industry Data Security Standard (PCI DSS) is a set of security requirements established by the PCI Security Standards Council (PCI SSC). By 2026, the reliance on digital payment infrastructure has reached a point where the integrity of financial transactions is central to consumer trust and institutional stability. PCI testing is not an optional security enhancement but a fundamental operational requirement for any merchant or service provider involved in the card payment ecosystem.
The primary objective of this testing is to identify weaknesses before malicious actors can exploit them. As threat vectors evolve, the methods used to secure the Cardholder Data Environment (CDE) must remain rigorous. Testing verifies that security controls—ranging from firewalls and encryption to access monitoring—are not only configured correctly but are effectively preventing unauthorized access.
Core Components of PCI Testing
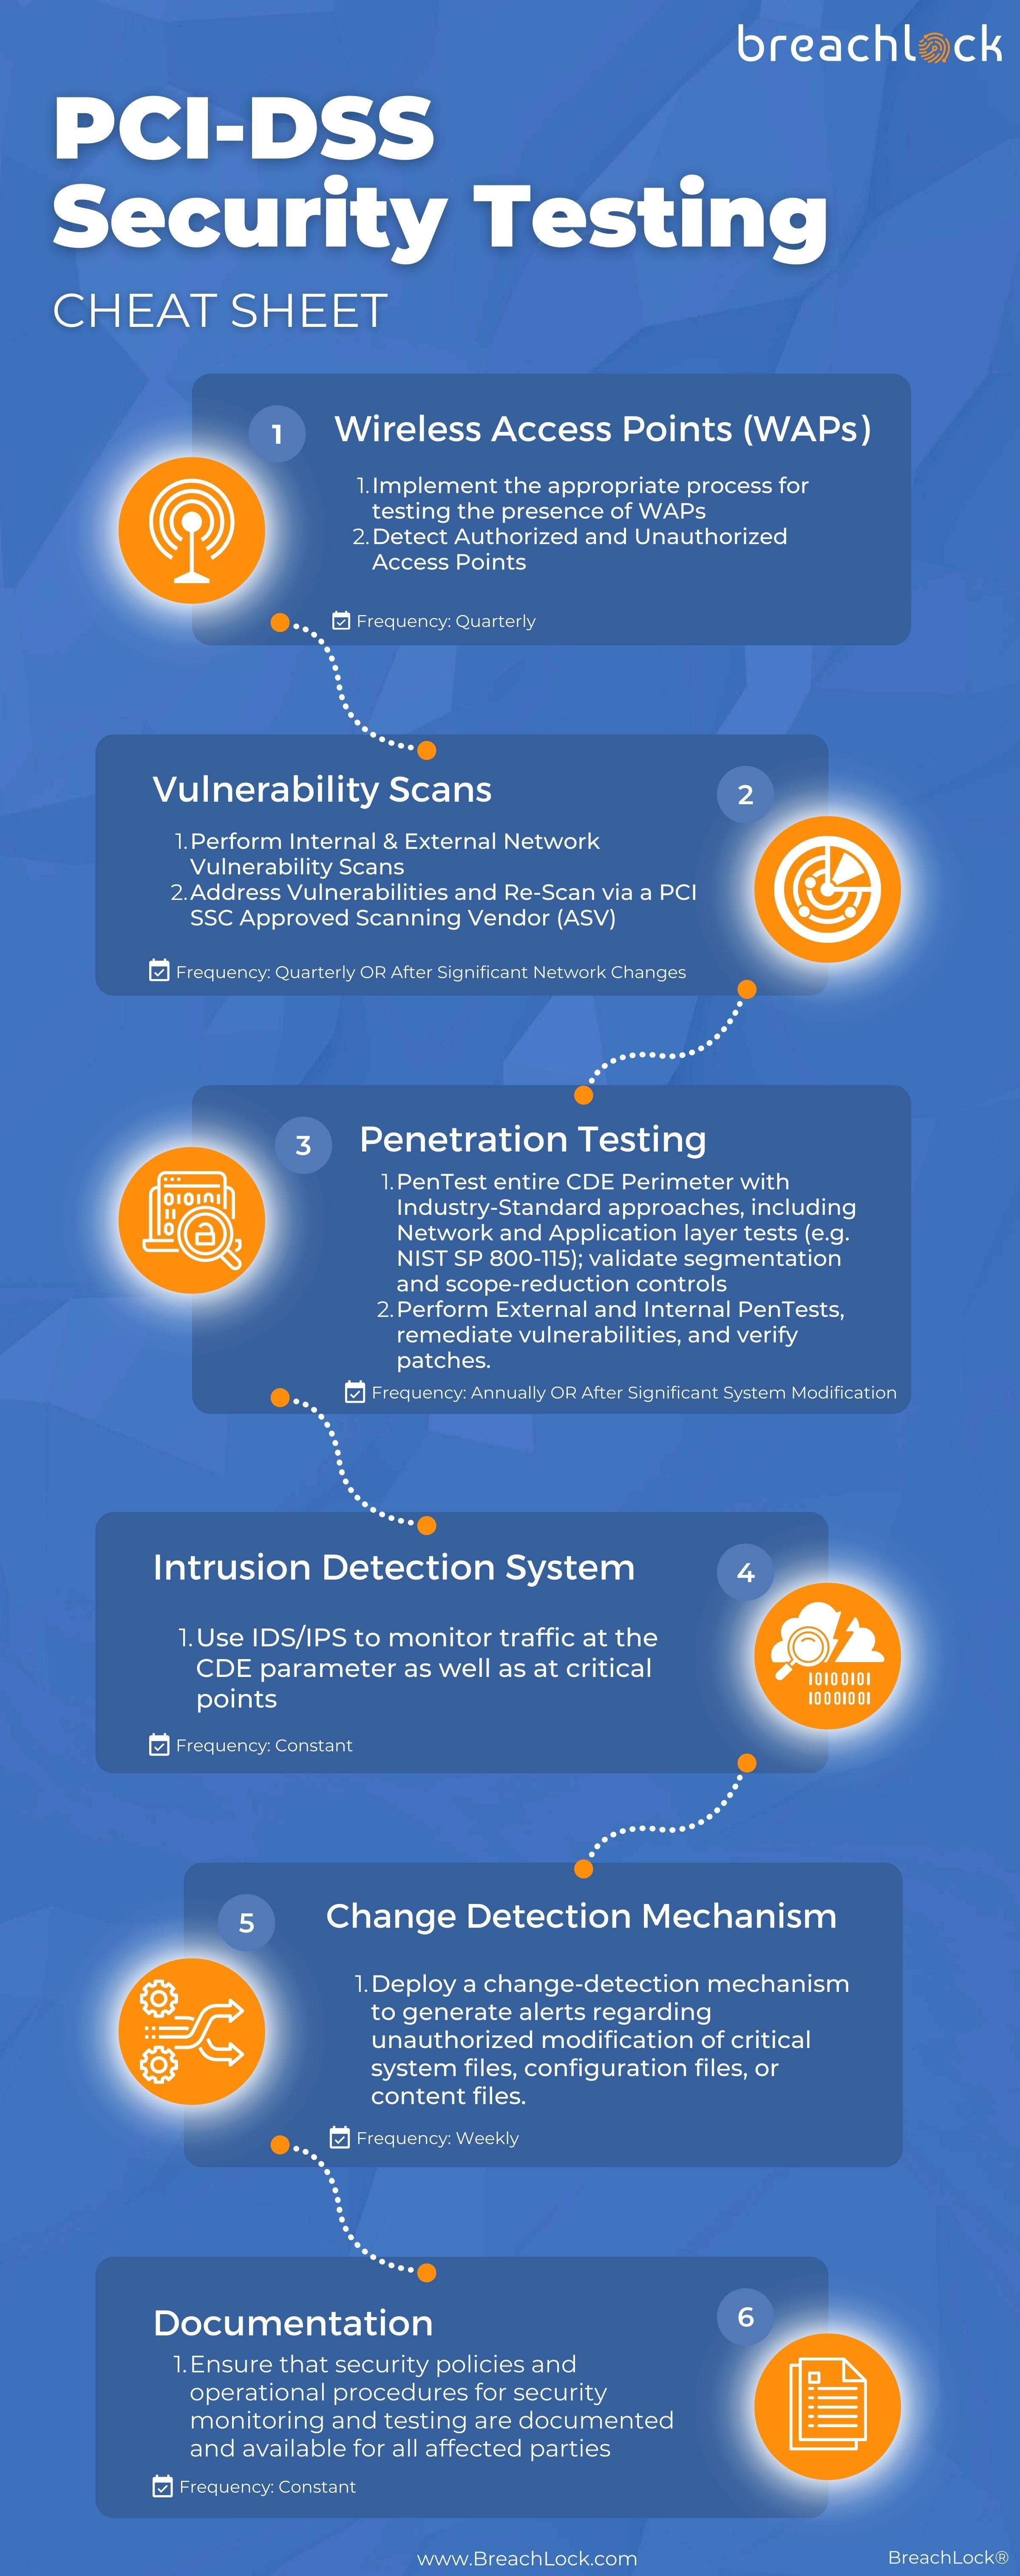
PCI testing generally encompasses two distinct but complementary activities: internal and external vulnerability scanning, and periodic penetration testing. Understanding the distinction between these methods is essential for maintaining compliance.
1. Vulnerability Scanning
Vulnerability scanning is an automated, non-intrusive process that audits systems to identify known security vulnerabilities. It checks for outdated software versions, misconfigurations, and missing security patches.
- External Scans: These must be performed by an Approved Scanning Vendor (ASV) authorized by the PCI SSC. These scans target the public-facing IP addresses of an organization's network to ensure that there are no high-risk vulnerabilities accessible from the open internet.
- Internal Scans: These are performed inside the organization’s network, often using automated tools. They identify internal risks that could be leveraged by an attacker who has already breached the perimeter.
2. Penetration Testing
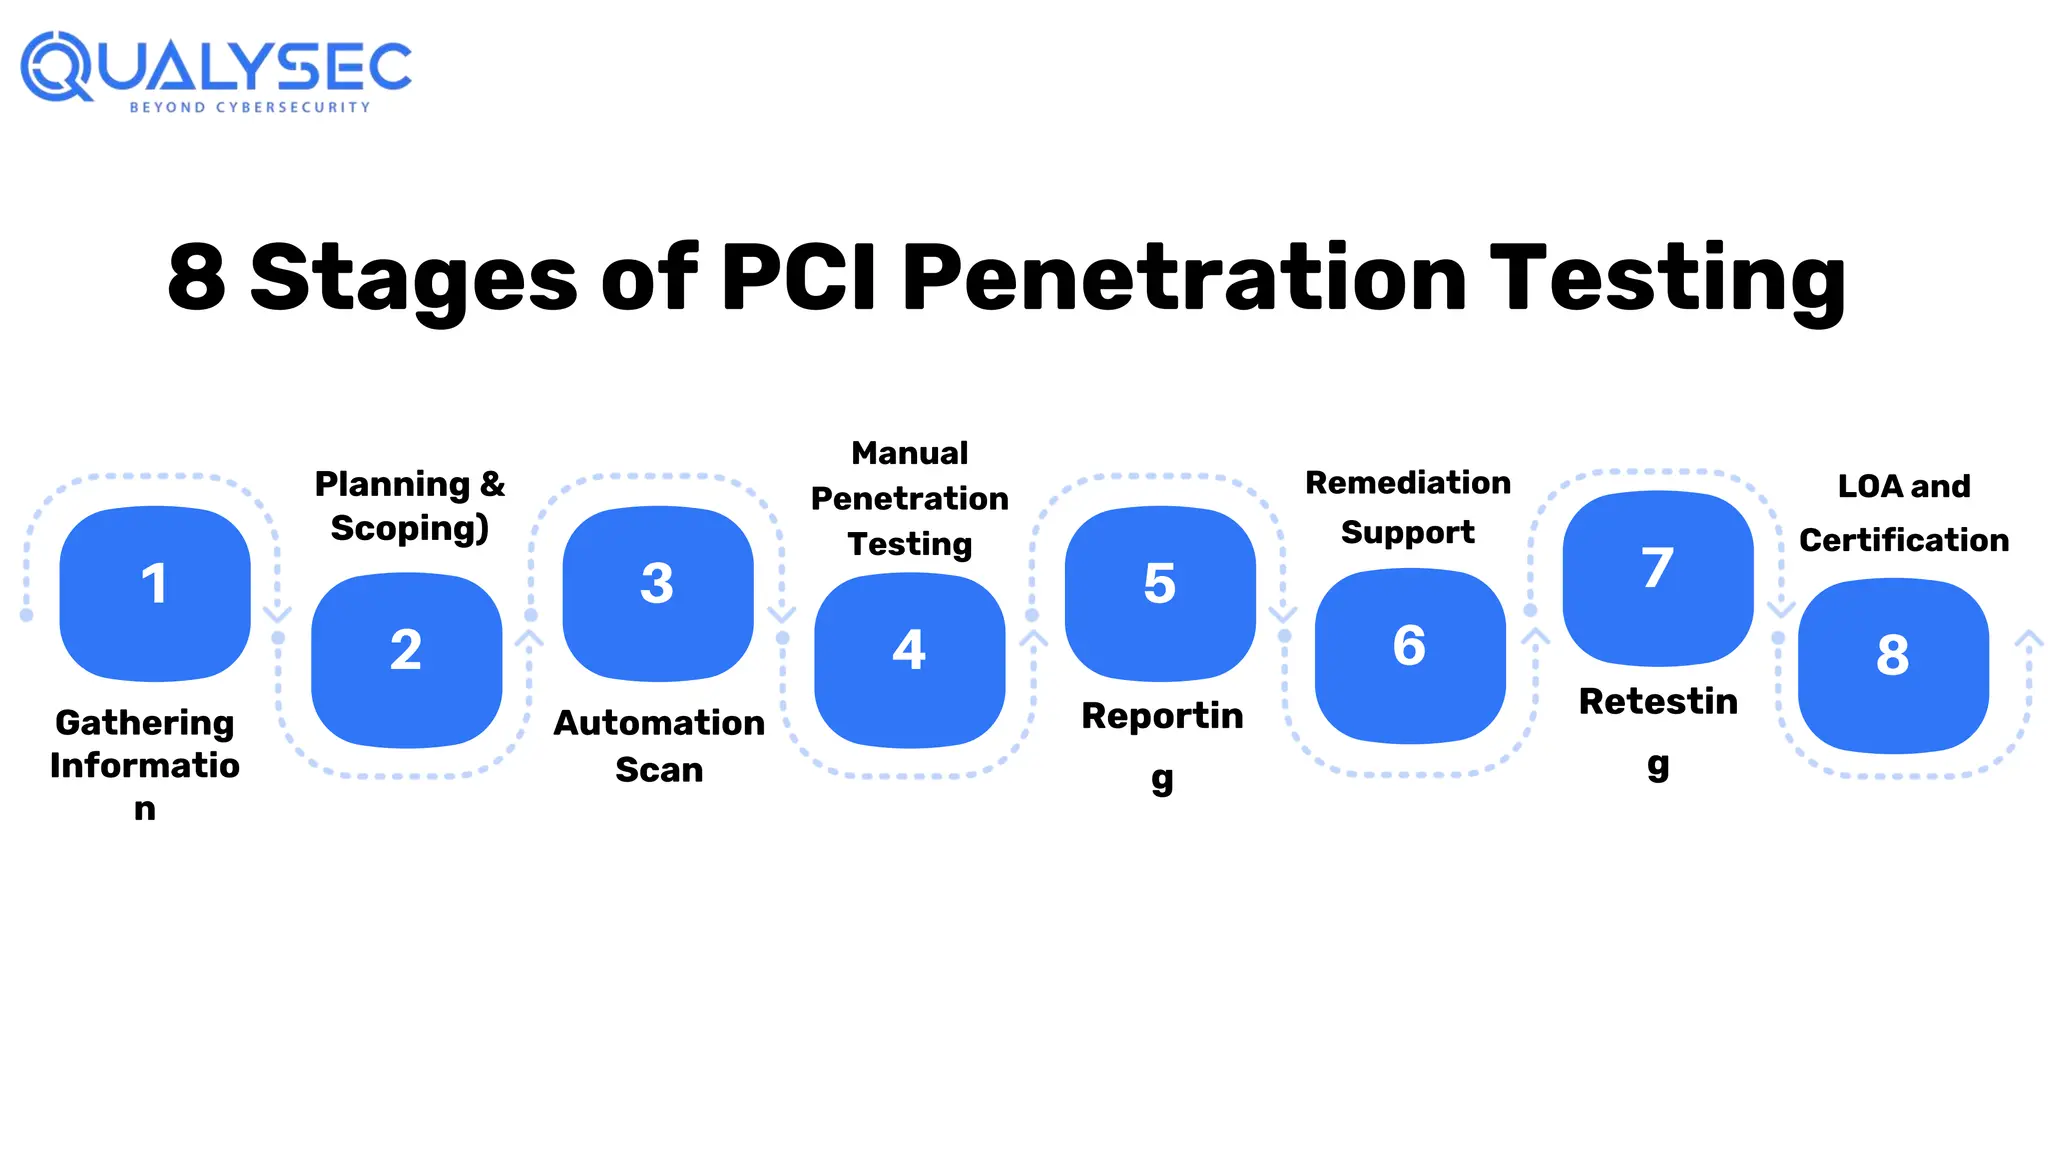
Unlike automated scanning, penetration testing (pen testing) is a manual, "ethical hacking" exercise. A qualified security professional attempts to exploit identified vulnerabilities to determine the actual risk they pose. The goal is to simulate the strategies and tactics of real-world attackers. PCI DSS requires penetration testing to verify that the security controls are sufficient to protect cardholder data, specifically targeting the CDE and any systems connected to it.
Determining Compliance Requirements
Not all entities face the same testing burden. The PCI SSC categorizes merchants and service providers based on their annual transaction volume and the manner in which they handle data.
| Entity Type | Transaction Volume/Status | Typical Testing Requirement |
|---|---|---|
| Level 1 Merchant | Over 6 million annual transactions | Full onsite assessment, annual pen test, quarterly ASV scans |
| Level 2 Merchant | 1 million to 6 million transactions | Annual Self-Assessment Questionnaire (SAQ), quarterly ASV scans |
| Level 3 Merchant | 20,000 to 1 million e-commerce transactions | Annual SAQ, quarterly ASV scans |
| Level 4 Merchant | Fewer than 20,000 e-commerce transactions | Annual SAQ, quarterly ASV scans (if applicable) |
Note: Requirements may vary depending on the specific acquiring bank or payment processor. Always consult with your acquiring financial institution to confirm your specific reporting obligations.
The Testing Lifecycle: A Step-by-Step Approach
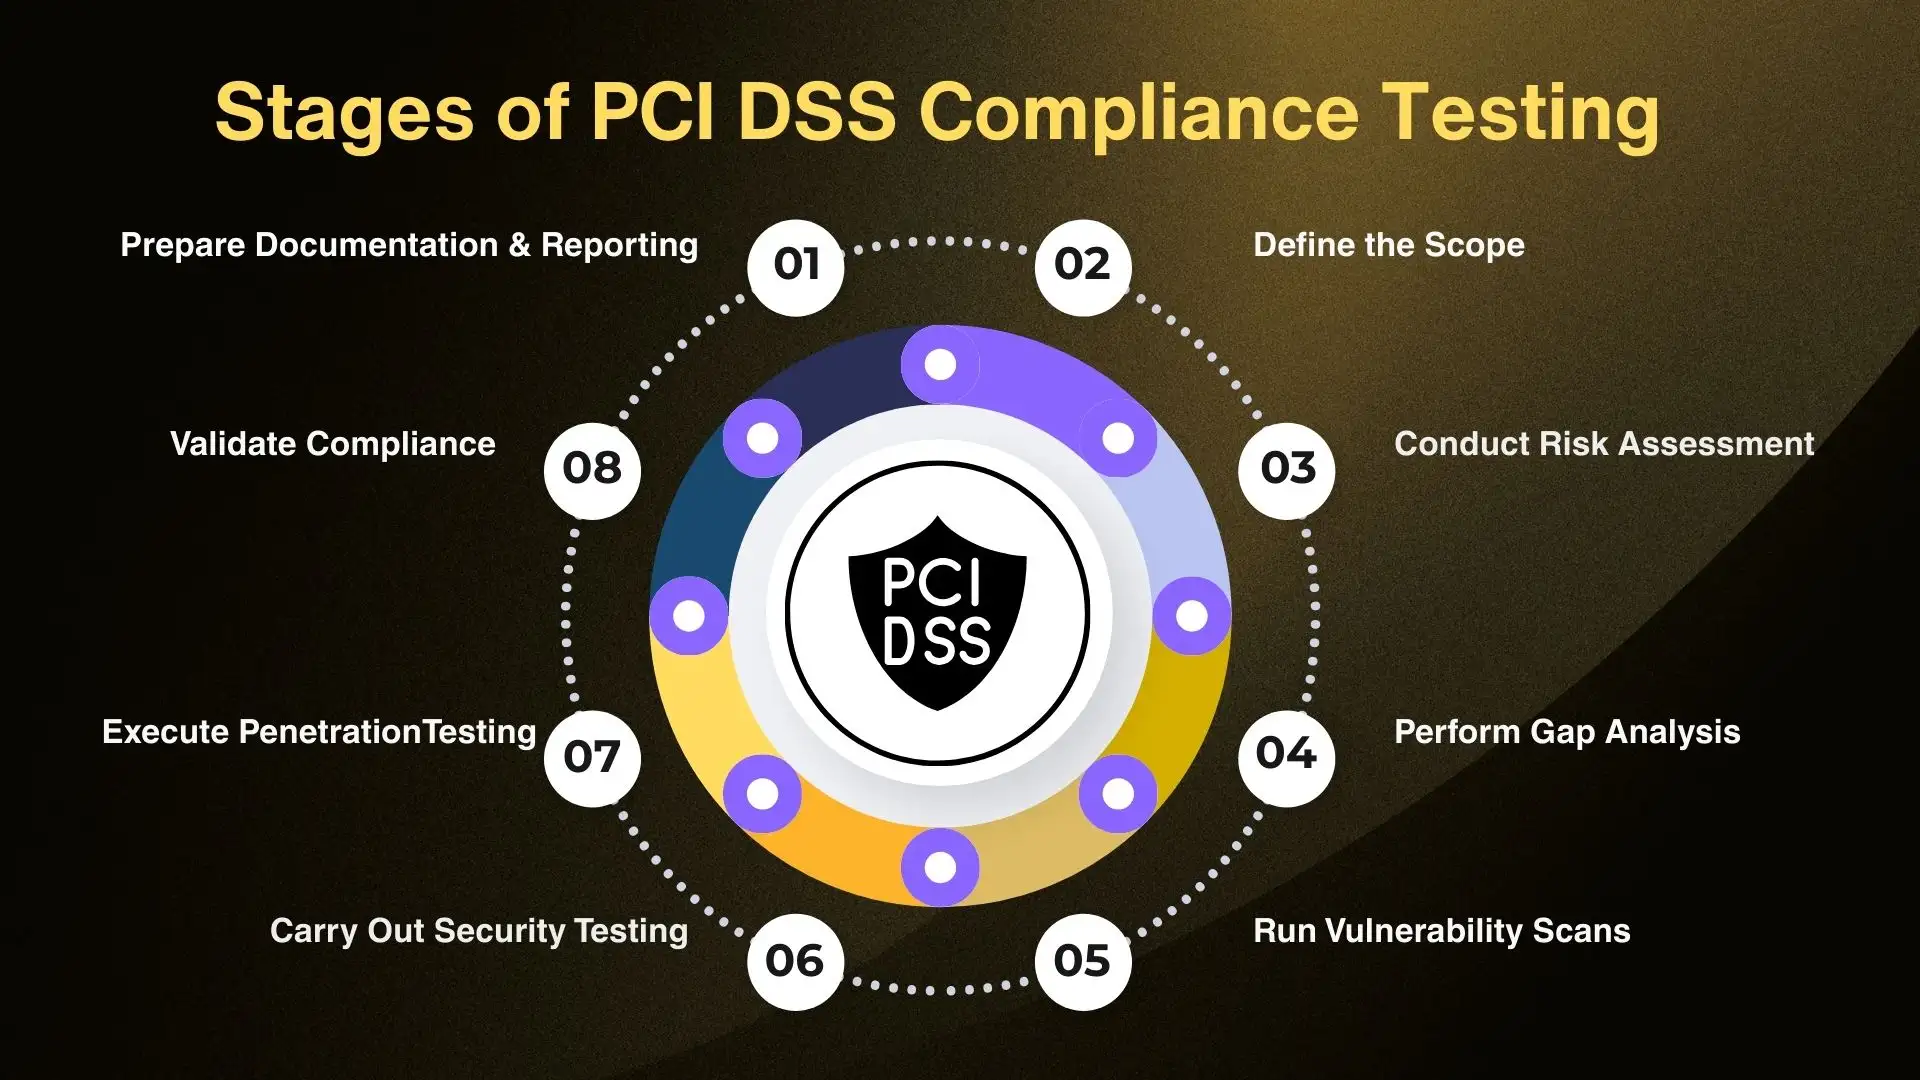
To maintain compliance throughout the year, organizations should treat PCI testing as a continuous lifecycle rather than a one-time event.
Step 1: Scoping the Cardholder Data Environment
Before testing begins, define the boundaries of your CDE. This includes all systems, applications, and networks that process, store, or transmit cardholder data. Minimizing the scope of your CDE—often referred to as scope reduction—is the most effective way to lower the complexity and cost of testing.
Step 2: Remediation
If a vulnerability scan or penetration test reveals a flaw, it must be remediated. This typically involves patching software, reconfiguring firewalls, or updating security policies. Once remediation is complete, the testing process must be repeated to verify that the fix was successful and did not introduce new vulnerabilities.
Step 3: Reporting and Attestation
For larger organizations, the output of these tests contributes to the Report on Compliance (ROC). Smaller merchants typically complete a Self-Assessment Questionnaire (SAQ) and provide an Attestation of Compliance (AOC) to their acquiring bank. These documents serve as formal proof that the required testing has been performed and that all identified risks have been addressed.
Common Pitfalls and Troubleshooting
Many organizations struggle with PCI compliance due to common misconceptions. Addressing these early can prevent significant delays during the audit process.
- Failure to Scan Non-Public Assets: Organizations sometimes focus only on their website, ignoring secondary systems like payment gateways or internal databases that also store sensitive data. Ensure the entire CDE is in scope.
- Ignoring Shadow IT: Unauthorized software or shadow IT assets—devices or applications used by employees without IT approval—are often the weakest links. Regular network discovery is critical to ensuring these assets are covered by your testing protocols.
- Misunderstanding Penetration Test Scope: A common error is performing a web application test while ignoring the underlying network infrastructure. PCI DSS requires that the test covers both the network and the application layers to ensure comprehensive protection.
Addressing Evolving Security Threats in 2026
As of 2026, the complexity of payment environments has increased significantly due to the integration of cloud-native services and third-party APIs. Organizations must ensure that their testing methodologies account for these modern architectures. When using cloud providers, the "shared responsibility model" applies; while the provider secures the infrastructure, the merchant remains responsible for securing the data and configurations within that environment. Testing must verify that these configurations remain secure after deployment.
Frequently Asked Questions
How often must I perform a penetration test? PCI DSS requires penetration testing at least annually and after any significant change to the network infrastructure or the CDE. Significant changes include adding new hardware, modifying firewall rules, or updating core software components.
What is an Approved Scanning Vendor (ASV)? An ASV is a company with a set of security services and tools approved by the PCI SSC to conduct external vulnerability scanning. You must use an ASV to conduct the quarterly external scans required for compliance.
Do I need a penetration test if I use a payment gateway? Even if you use a third-party payment gateway, you are still responsible for the security of your local environment and any systems that connect to that gateway. The scope of your penetration test may be smaller, but it is rarely eliminated entirely.
What happens if I fail a scan? Failing a scan simply means vulnerabilities were detected. You are required to patch these issues and rescan until all "high" or "critical" vulnerabilities are resolved. Your ASV will provide instructions on the specific findings that need remediation.
Is PCI testing equivalent to a full security audit? No. PCI testing is a subset of the broader security requirements needed to protect your organization. While it ensures compliance with payment card standards, a robust security posture also requires incident response planning, employee training, and ongoing threat intelligence.
Recommended Next Actions
To begin or improve your PCI testing regimen, follow these three steps:
- Map your data flows: Identify every point where card data enters, exits, or is stored in your network. Use this map to define your official CDE scope.
- Verify your ASV: Confirm that your chosen scanning vendor is listed on the official PCI SSC list of Approved Scanning Vendors for the current year.
- Engage professional auditors: If your transaction volume is high, do not attempt to navigate the ROC process alone. Engage a Qualified Security Assessor (QSA) to provide expert guidance on your testing procedures and documentation requirements.