While iOS does not support traditional virus scanners due to Apple’s strict sandboxing architecture, users still face significant mobile threats like phishing, malicious Wi-Fi networks, and software vulnerabilities, making security apps focused on web protection, network monitoring, and system updates essential.
The question of whether Apple's mobile operating system requires traditional antivirus software often leads to confusion. To understand device security on mobile platforms, it is necessary to examine how Apple structures its operating system, the types of threats mobile users encounter, and what security tools actually do on iOS devices.
Understanding iOS Architecture and Security Design
Apple designs iOS with a security model centered around application isolation, commonly referred to as sandboxing. Every app downloaded from the App Store operates within its own restricted container. An application cannot inspect the files of another app, modify the operating system core, or access private system directories without explicit, granular user permission and system-level entitlements.
This architecture fundamentally differs from traditional desktop environments like Windows or macOS. On a standard desktop computer, a user-installed program often runs with broad administrative privileges. If that program executes malicious code, it can potentially scan the entire hard drive, alter system files, and inject itself into other running processes.
Because iOS sandboxes every application, a standard antivirus scanner cannot crawl the file system to look for malicious signatures across different apps. If an app attempted to scan other apps or system files, the operating system would block the action. Therefore, apps branded as "antivirus for iOS" do not actually scan for and destroy computer viruses in the traditional sense. Instead, they function as multi-layered security suites designed to protect against network-based attacks, unsafe web pages, unsecured Wi-Fi connections, and compromised device settings.
Real-World Threats to iOS Devices
Although iOS is widely recognized for robust baseline security, it is not immune to cyberattacks. Threat actors have adapted their tactics to target mobile users through attack vectors that bypass traditional file-based defenses. Understanding these threats clarifies why security tools are still deployed on iPhones and iPads.
Phishing and Social Engineering
Phishing represents one of the most prevalent attack vectors on mobile devices. Attackers send fraudulent text messages (smishing), deceptive emails, or malicious links via messaging apps, tricking users into visiting lookalike login portals for banks, streaming services, or corporate credentials. Because mobile screens are smaller and display abbreviated URLs, users often struggle to spot the subtle domain discrepancies that reveal a fake website.
Man-in-the-Middle (MitM) Attacks and Unsafe Wi-Fi
Mobile devices frequently connect to public Wi-Fi networks in coffee shops, airports, and hotels. If these networks lack adequate encryption, malicious actors can intercept traffic passing between the device and the internet. This allows attackers to harvest sensitive data or redirect browsing traffic to spoofed destinations.
Operating System Vulnerabilities and Zero-Days
Even with Apple’s rigorous patch management, zero-day vulnerabilities—security flaws unknown to the vendor—are occasionally discovered and exploited by sophisticated threat groups. Nation-state spyware and commercial surveillanceware have historically targeted high-profile individuals by exploiting unpatched vulnerabilities in iOS through zero-click exploits delivered via messaging apps.
Compromised System Configurations
Jailbroken devices, outdated operating systems, and disabled security features (such as missing device passcodes or disabled biometric locks) drastically increase vulnerability levels. While jailbreaking deliberately removes Apple’s sandbox restrictions to allow unauthorized software modifications, it also strips away the built-in integrity checks that keep malware at bay.
Core Capabilities of iOS Security Apps
Because traditional virus scanning is technically impossible on iOS, legitimate security applications for the platform provide specialized features tailored to mobile threat vectors. Evaluating these capabilities helps users determine which features provide genuine value.
Web Protection and Phishing Blockers
The most effective security apps for iOS integrate tightly with Safari or utilize local VPN configurations to filter web traffic. When a user attempts to navigate to a known malicious, fraudulent, or phishing domain, the security app intercepts the request and blocks the page from loading, presenting a warning screen instead.
Wi-Fi Security Scanners
Mobile security tools monitor the integrity of connected wireless networks. They analyze router configurations, check for Address Resolution Protocol (ARP) spoofing attempts, and alert users if they connect to an unsecured or rogue Wi-Fi hotspot that could compromise data privacy.
Virtual Private Networks (VPNs)
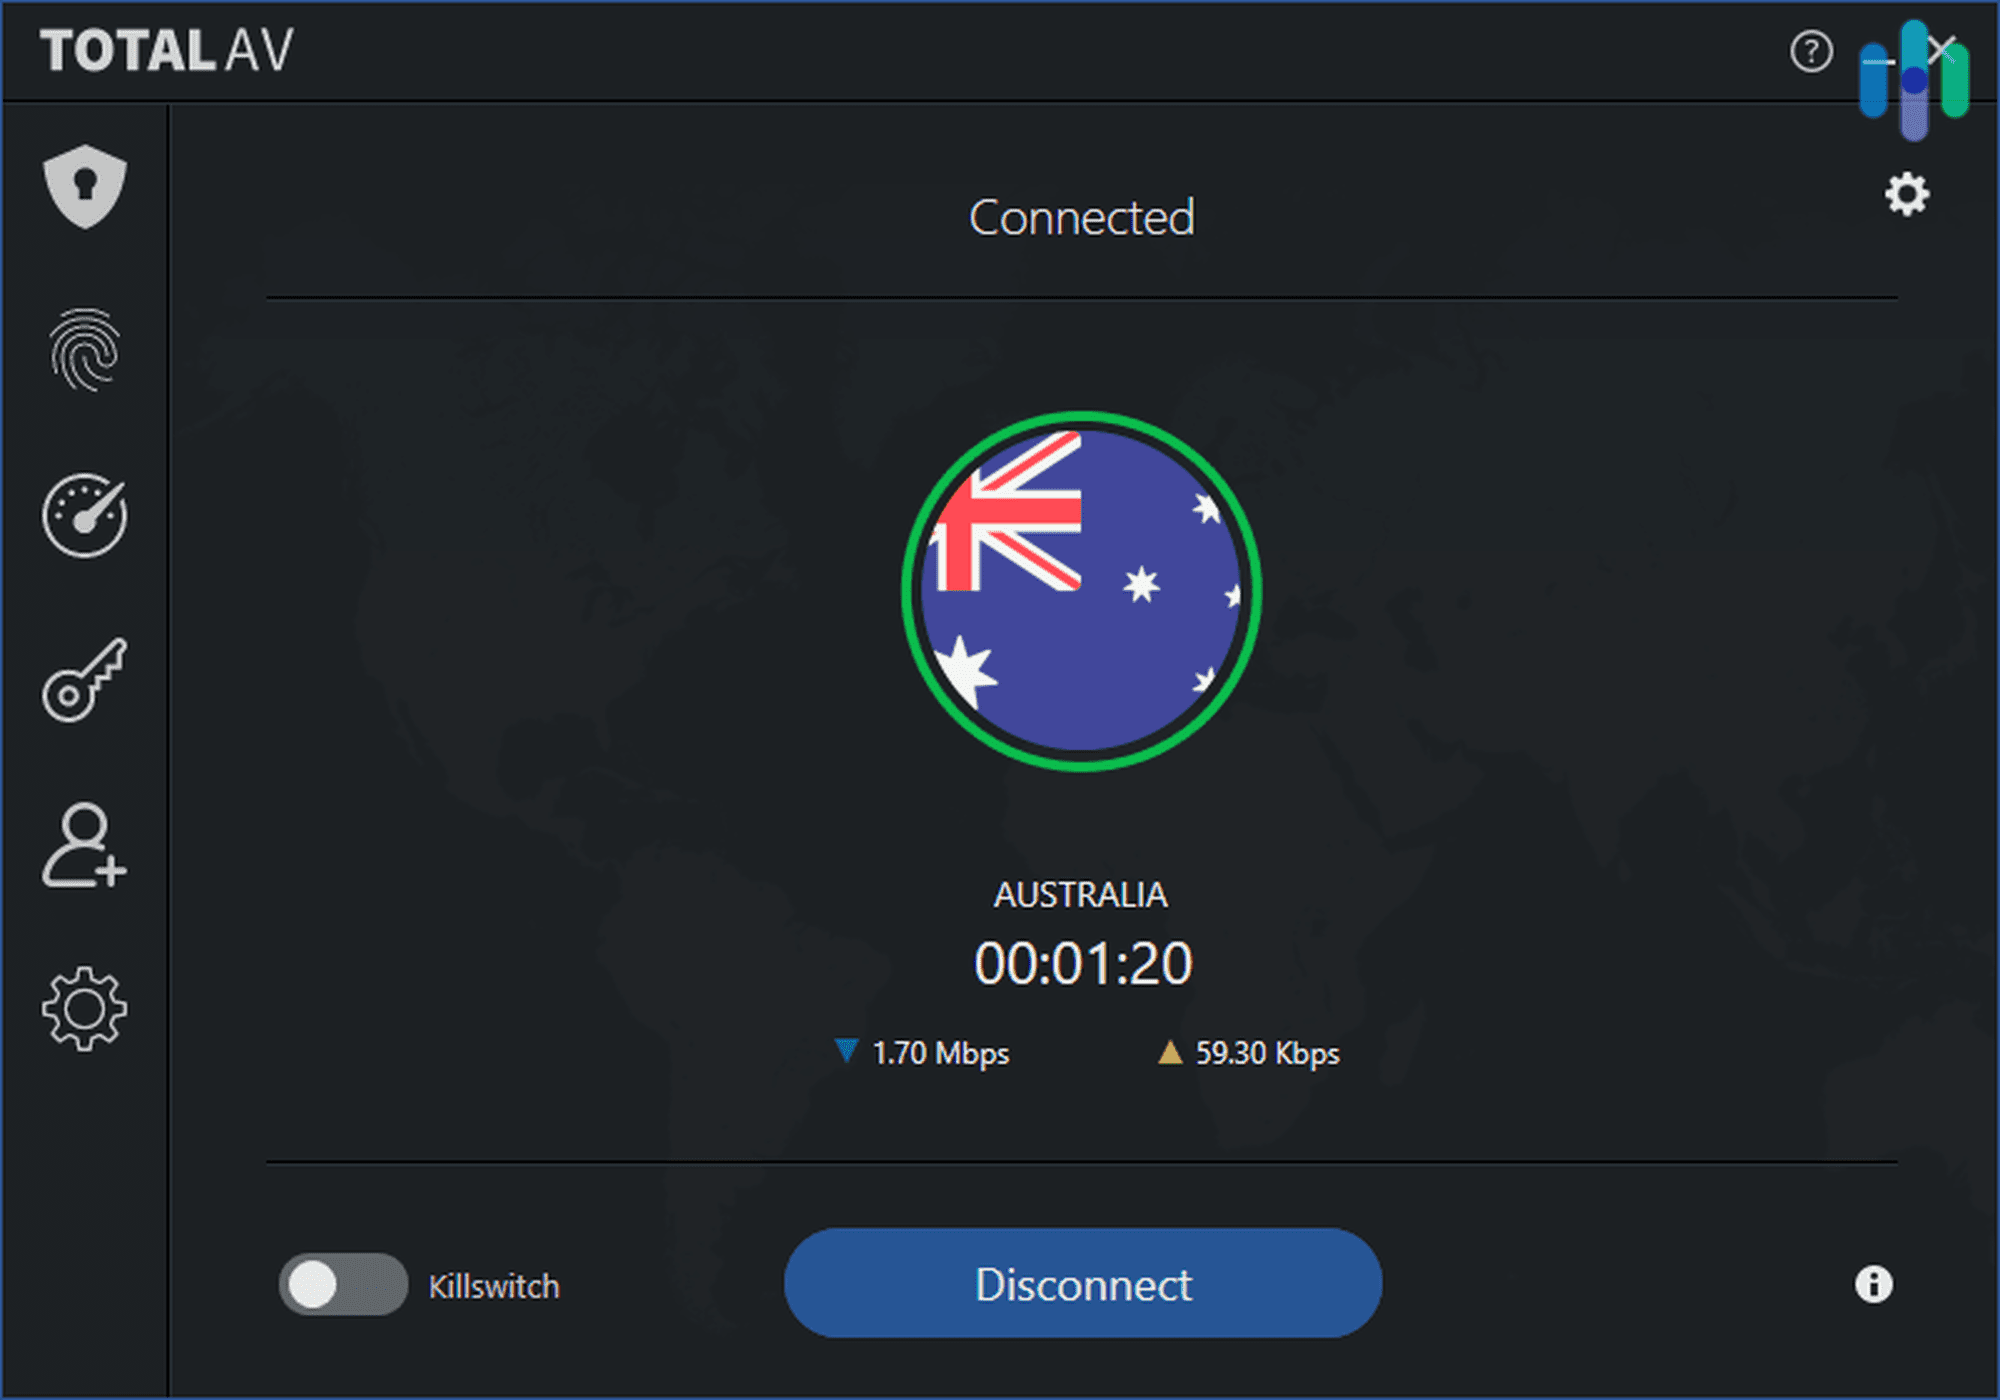
Many iOS security suites bundle a VPN service. A VPN encrypts all internet traffic leaving the device, shielding user data from snooping on public Wi-Fi networks and masking the user's IP address from third-party trackers.
System Integrity and Update Monitors
Because operating system updates patch critical security vulnerabilities, security apps often feature update monitors. These tools notify users immediately when a new iOS update is available, ensuring the device runs the latest security patches. Furthermore, they check for system anomalies, such as unexpected operating system modifications that might indicate a jailbreak.
| Feature | Functionality | Protection Level | Primary Benefit |
|---|---|---|---|
| Web Guard | Blocks malicious URLs and phishing links in browsers | High | Prevents credential theft and drive-by exploits |
| Wi-Fi Inspector | Detects compromised or unencrypted wireless networks | Medium-High | Shields data on public hotspots |
| VPN Integration | Encrypts network traffic and hides IP addresses | High | Secures data in transit across untrusted networks |
| System Auditor | Verifies OS version, passcode status, and jailbreak signs | Medium | Ensures baseline device hardening is active |
Comparing iOS Built-In Security vs. Third-Party Apps
Apple builds extensive security measures directly into iOS. Before purchasing a third-party security app, users should evaluate what Apple provides natively versus what supplemental apps add.
Built-In Apple Security Features
- App Sandbox: Isolates applications to prevent unauthorized data access between programs.
- App Store Review: Screens all submitted applications for malicious code, private API usage, and policy violations before publication.
- Advanced Data Protection: Provides end-to-end encryption for iCloud backups, notes, photos, and messages.
- Lockdown Mode: An extreme, optional protection setting designed for individuals who may be targeted by sophisticated digital threats, disabling certain complex web technologies and message attachments.
- Automatic Security Responses: Delivers rapid security fixes between standard iOS updates without requiring a full system reboot.
Third-Party Security Additions
While Apple's native protections handle core system integrity and app distribution, third-party apps extend protection into areas Apple leaves to the user:
- Real-time global threat intelligence databases that track emerging phishing domains faster than standard browser blacklists.
- Cross-platform protection synchronization, allowing users to manage security across Windows, Android, macOS, and iOS from a single dashboard.
- Identity theft monitoring, which scans the dark web for leaked email addresses, passwords, and Social Security numbers.
Cost, Privacy Considerations, and Limitations
When selecting an iOS security app, users must balance protection benefits against subscription costs and privacy implications.
Financial Considerations
Free security apps on iOS typically offer basic Wi-Fi checks and update notifications, while advanced features—such as integrated VPN bandwidth, real-time web protection, and identity theft alerts—generally require an annual subscription model ranging from $30 to $100 per year. Users should carefully review subscription terms to avoid unexpected recurring charges.
Privacy Trade-Offs
To filter web traffic or route internet data, many third-party security apps require the installation of a local VPN profile or a configuration profile. This means the app provider routes or inspects DNS requests and browsing metadata. Users must research the privacy policy and data-logging practices of the security vendor to ensure their browsing habits are not being monetized or shared with third parties.
Technical Limitations
Due to iOS operating system constraints, third-party apps cannot:
- Scan downloaded files or attachments for hidden computer viruses.
- Clean or quarantine infected system files.
- Override system-level permissions granted directly by the user.
Step-by-Step Guide: Securing an iOS Device
Users looking to maximize their mobile security should follow a structured approach that prioritizes native settings before exploring third-party software.
- Update the Operating System: Navigate to Settings > General > Software Update and enable automatic updates to ensure the device receives the latest security patches immediately upon release.
- Enable Two-Factor Authentication (2FA): Secure your Apple ID and associated email accounts with hardware-backed 2FA or trusted authentication apps to prevent unauthorized account access.
- Review App Permissions: Go to Settings > Privacy & Security to audit which applications have access to location data, the microphone, camera, and local network devices. Revoke permissions for apps that do not require them.
- Configure Safari Security Settings: Ensure Fraudulent Website Warning is enabled under Settings > Safari to leverage built-in phishing detection.
- Evaluate Third-Party Apps: If you frequently use public Wi-Fi or require advanced phishing protection beyond Safari's default capabilities, research and install a reputable security suite from the App Store that features transparent privacy practices and verified web filtering.
Frequently Asked Questions
Can iPhones get infected with computer viruses?
No. Due to the strict sandboxing architecture of iOS, traditional computer viruses designed to replicate across file systems and infect other programs cannot execute or spread on an iPhone or iPad. However, iPhones can still be targeted by phishing campaigns, malicious websites, and zero-day spyware exploits.
Do I need to install an antivirus app on my iPhone?
Most users do not need a traditional antivirus app on iOS because Apple's built-in sandboxing and App Store review processes provide strong baseline protection. However, users who frequently navigate untrusted websites, use public Wi-Fi networks extensively, or want advanced phishing protection and identity theft monitoring often benefit from dedicated mobile security suites.
How do iOS security apps protect the device if they cannot scan files?
iOS security apps protect devices by operating at the network and application layer rather than scanning the file system. They utilize local VPNs and browser extensions to block malicious URLs, scan wireless networks for security vulnerabilities, monitor dark web databases for leaked credentials, and verify that the operating system has not been modified or jailbroken.
What is the difference between a VPN and an iOS security app?
A Virtual Private Network (VPN) encrypts internet traffic between your device and a remote server, protecting data from interception on public Wi-Fi. An iOS security app is often a broader suite that may include a VPN alongside web-filtering tools to block phishing sites, system update monitors, and data breach alerts.
How can I tell if my iPhone has been compromised?
Signs of compromise include unexplained battery drain, apps opening or closing spontaneously, unusual data usage spikes, unfamiliar apps appearing on the home screen, or receiving persistent security alerts from trusted accounts. If you suspect your device is compromised, update iOS immediately, change your Apple ID password, revoke unknown app permissions, and reset the device to factory settings if necessary.
Practical Recommendations
For most users, maintaining a secure iOS device relies less on downloading third-party scanning tools and more on adopting strong digital habits. Keep the operating system updated, practice caution when clicking links received via text messages or email, secure your accounts with multi-factor authentication, and avoid jailbreaking the device. If your threat model involves frequent travel, reliance on public Wi-Fi networks, or exposure to high-risk phishing targets, investing in a reputable security suite with robust web filtering and VPN protection provides a worthwhile layer of defense.