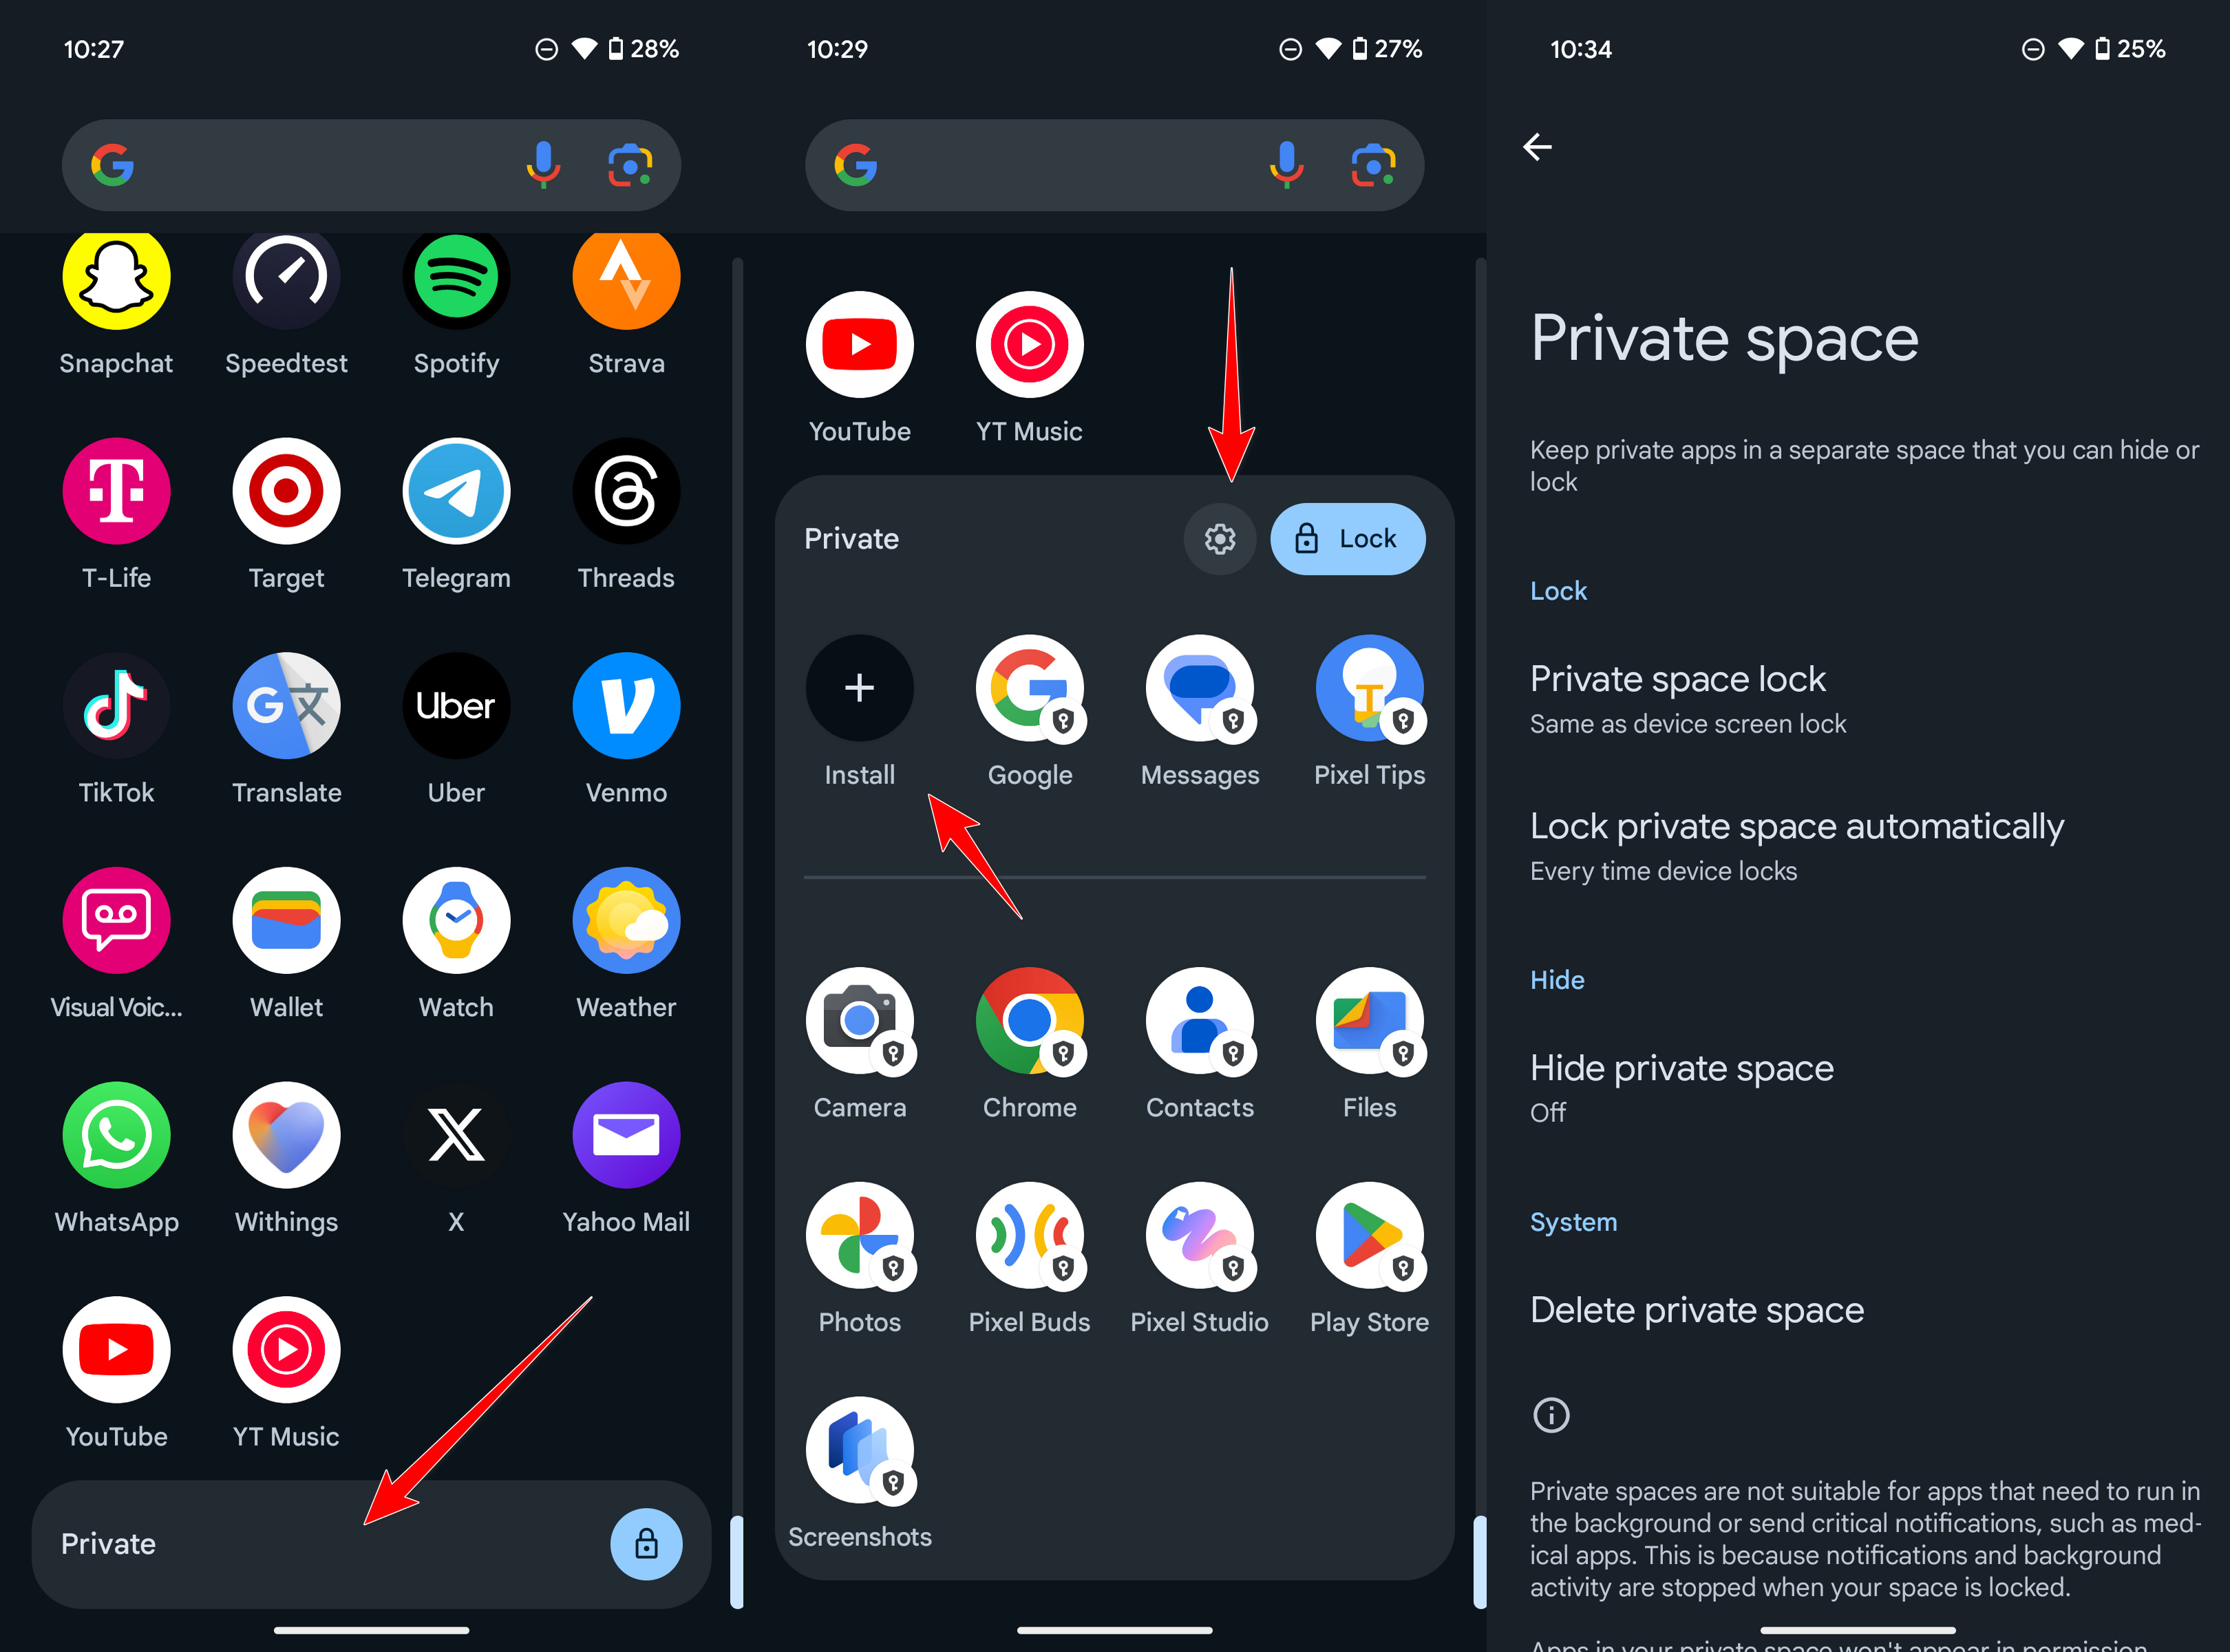
A private app is a software application designed for restricted distribution, intended exclusively for specific users, such as employees within an organization or members of a closed group. Unlike public applications available on global app stores, private apps are managed through controlled deployment channels, ensuring that only authorized personnel or entities can download, install, and access the proprietary data contained within.
Defining the Private App Ecosystem
In the context of software development and distribution, the term "private app" refers to a deliberate architecture where accessibility is gated. While consumer apps prioritize discovery and broad market reach, private apps prioritize security, compliance, and internal workflow integration. These applications are often bespoke, built to solve specific operational challenges, automate internal data reporting, or facilitate secure communication within a corporate firewall.
The distinction between a public and a private app is fundamentally one of intent and infrastructure. A public application is designed for the App Store or Google Play store, where it undergoes a broad review process and is available to any user with a compatible device. A private application, by contrast, bypasses these public storefronts. It utilizes mechanisms such as Mobile Device Management (MDM) systems, Unified Endpoint Management (UEM) platforms, or dedicated enterprise distribution programs to push updates and manage installation privileges.
Primary Use Cases for Restricted Distribution
Organizations utilize private apps to maintain control over their intellectual property and sensitive workflows. The decision to move from a web-based portal to a dedicated private application usually hinges on the need for native hardware integration—such as using a device’s camera for secure document scanning, utilizing offline caching for field workers, or accessing biometric authentication features that web browsers may not fully support.
Common deployment scenarios include:
- Internal Productivity Suites: Apps designed for employees to clock in, request leave, or access human resources documentation.
- Field Operations: Tools for technicians or inventory managers who require robust, offline-capable interfaces in environments with intermittent internet connectivity.
- B2B Client Portals: Specialized applications provided by a service provider to a specific client organization, containing proprietary data or tools relevant only to that partnership.
- Beta Testing and Pre-Release: Distributing experimental versions of a product to a controlled set of testers before a public release to gather feedback without exposing the software to the general public.
Technical Infrastructure and Distribution Channels
Managing a private app requires a technical infrastructure that replaces the functionality of public app stores. For developers targeting the Apple ecosystem, this often involves the Apple Business Manager (ABM) and the use of Custom Apps. These apps are private and distributed via the Volume Purchase Program (VPP) or via redemption codes.
For the Android ecosystem, the transition from legacy private distribution to the Google Play Console's "Private Apps" feature has streamlined the process. Organizations can now host private applications within their managed Google Play environment. When a user logs into their work-managed device, the private app appears in their managed Play Store interface, having been pushed there by the company’s IT administrator.
Comparison of Distribution Methods
| Method | Target Audience | Primary Control Mechanism | Use Case |
|---|---|---|---|
| MDM/UEM Deployment | Employees | Device policy profiles | Internal corporate tools |
| Custom App Store Links | B2B Partners | Authenticated URLs/Tokens | Client-specific portals |
| Enterprise Provisioning | Large Organizations | Digital certificates | Scaled internal distribution |
| TestFlight/Firebase App Distribution | Beta Testers | Email invitations | Pre-release testing |
Security, Compliance, and Data Sovereignty
Security is the primary driver for using a private app rather than a standard web application. By restricting the app to managed devices, an organization can enforce policies such as remote wiping (deleting all app data if a device is reported lost or stolen) and preventing data from being copied or shared to unauthorized applications or cloud storage services.
Furthermore, private apps allow for granular access control. Since the application is typically linked to an organization’s Identity Provider (IdP)—such as Microsoft Entra ID or Okta—access is managed via Single Sign-On (SSO). If an employee leaves the company, their access to the app is revoked immediately when their corporate credentials are disabled, preventing unauthorized lingering access to internal data.
From a compliance perspective, keeping an app private ensures that the software does not violate industry-specific regulations that might govern where data can reside or who can view it. For industries such as finance or healthcare, where data privacy is legally mandated, the ability to contain an application within a closed, audited environment is an essential feature of their compliance architecture.
Implementation Requirements and Prerequisites
Transitioning to a private app strategy requires more than just code; it requires a foundational IT framework. Organizations intending to distribute private software must fulfill several prerequisites:
- Identity Management: An established directory service to authenticate users.
- Device Management: Implementation of an MDM solution to ensure devices meet minimum security postures (e.g., encryption enabled, OS updated).
- App Signing: Proper digital certificates to verify the identity of the developer and ensure the integrity of the application.
- Distribution Portal Access: Administrative access to the respective enterprise developer programs (Apple Developer Enterprise Program, Google Play Console for Enterprise).
Failure to align these components often leads to installation errors, trust issues where the device refuses to run the code, or data leakage when permissions are not correctly enforced at the OS level.
Challenges and Common Pitfalls
While private apps offer immense control, they are not without complexity. The most common pitfall for organizations is the "maintenance overhead." Unlike public apps that auto-update via the store, private apps often require explicit action from the MDM administrator to push new versions. If the deployment process is not automated, the organization ends up with a fragmented user base where half the staff uses an outdated version, leading to bugs and security vulnerabilities.
Another challenge is the limitation of user devices. Because private apps are often tied to specific company policies, personal devices (BYOD—Bring Your Own Device) may not be compatible. Organizations must decide whether to provide corporate devices or implement a "work profile" on personal devices, which effectively walls off the private app and its data from the user’s personal photos, messages, and apps.
Troubleshooting Deployment Issues
If a private app fails to deploy or function correctly, the troubleshooting path typically involves three stages:
- Connectivity and Authentication: Is the device reaching the MDM server? Is the user’s SSO token active and valid?
- Certificate and Provisioning Profiles: Have the security certificates expired? Apple devices in particular are sensitive to expired provisioning profiles, which will cause the app to fail to launch immediately.
- Permissions and Privacy Settings: Does the app have the required OS-level permissions (e.g., location, camera, storage)? Often, the MDM profile needs to be updated to explicitly grant these permissions upon installation, otherwise the app may crash upon its first launch.
Frequently Asked Questions
What is the difference between a private app and a web app? A private app is installed natively on a mobile device, allowing for offline access and deeper hardware integration (e.g., Bluetooth, camera, sensors). A web app runs inside a browser; while it is easier to update, it requires an active internet connection and lacks access to the device’s underlying hardware features.
Can a private app be published to the public App Store? Generally, no. Private apps are built using specific distribution methods that are incompatible with public store policies. If a developer wants to make a private app public, they must reconfigure the app to remove internal-only authentication and comply with the public App Store Review Guidelines.
Do I need a developer account for private apps? Yes. Even for internal use, you must enroll in the Apple Developer Program or the Google Play Console. This is necessary to sign your binaries and obtain the distribution tools required to manage your internal app ecosystem.
Is it possible to track user activity within a private app? Yes. Because you own the distribution channel and the authentication layer, you can integrate analytics tools to monitor usage patterns, provided you remain compliant with your organization’s internal data privacy policies and any relevant employment laws.
How do I revoke access to a private app? Access is revoked via your MDM or UEM platform. By removing the application from the user’s assigned policy or by revoking their SSO credentials, the app will either be uninstalled from the device automatically or the user will be denied authentication upon opening the app.
Strategic Considerations for Scaling
As an organization grows, the management of private apps becomes a matter of lifecycle management. Organizations should treat their private app suite like a product portfolio. This includes documenting version history, managing deprecation timelines for older software, and conducting regular security audits of the code.
For long-term success, favor an "infrastructure as code" approach to your deployment. By automating the push of updates via your MDM, you reduce the manual labor associated with version control. Furthermore, invest in comprehensive internal documentation for users; because they cannot rely on public forums or FAQ pages to solve their problems, they must rely on the organization’s internal help desk.
The ultimate goal of deploying a private app is to streamline an internal process without introducing unnecessary risk. If the overhead of managing the distribution outweighs the efficiency gains of the app itself, reconsider whether a secure web portal might be a more sustainable solution.