Accessing GW Mail requires navigating George Washington University's Central Authentication Service (CAS) and Microsoft Office 365 infrastructure, utilizing a valid NetID and password while adhering to multi-factor authentication requirements.
Understanding GW Mail and the Microsoft 365 Ecosystem
George Washington University (GW) provides email, calendar, and collaboration tools to students, faculty, and staff through Microsoft Office 365. This enterprise environment integrates standard cloud utilities like Outlook, OneDrive, and SharePoint under a unified university identity. Because the system relies heavily on institutional credentials, attempting to sign in requires understanding how single sign-on (SSO) gateways interact with third-party software applications.
When users attempt a standard mail login, they are rarely authenticating directly against a local mail server. Instead, they interact with a federated identity management framework. This framework routes authentication requests through the university's custom login portal, which verifies credentials against institutional databases before issuing a secure token that grants access to the user's mailbox. Recognizing this architecture helps explain why a simple password change on a personal device might fail if it does not synchronize with university directory services.
Prerequisites for Successful Account Access
Before initiating a login session, users must ensure they meet specific foundational requirements. Failing to satisfy any of these conditions will result in authentication errors or restricted access.
1. Active NetID and Password
Every user requires an active George Washington University NetID. This unique username, paired with a regularly updated password managed through the GW IT Identity and Access Management portal, serves as the primary key for account entry. Accounts belonging to graduated students or former employees enter a grace period and eventual deactivation phase, after which login attempts will be permanently blocked.
2. Multi-Factor Authentication (MFA) Configuration
GW enforces mandatory multi-factor authentication using solutions like Duo Security to protect institutional data against unauthorized access. Users cannot bypass this step. A successful login requires not only the correct password but also access to an approved secondary verification method, such as:
- A registered smartphone running the Duo Mobile push notification application.
- Hardware security tokens or physical security keys.
- SMS text message codes or voice call verification (where permitted).
3. Supported Web Browsers and Device Hygiene
While modern web standards allow access from virtually any device, troubleshooting is minimized when using updated versions of mainstream browsers such as Google Chrome, Mozilla Firefox, Apple Safari, or Microsoft Edge. Clear cache and cookie data if persistent loops occur during the authentication redirection phase.
Step-by-Step Instructions for GW Mail Login
Navigating to your university inbox efficiently requires a clear, sequential approach. Whether you are using a desktop web browser or configuring a mobile application, the core steps remain consistent.
Method 1: Logging In via Web Browser
- Navigate to the Official Portal: Open your preferred web browser and go to the official George Washington University Information Technology portal or directly to the Microsoft 365 sign-in page.
- Enter Institutional Credentials: Input your full GW email address (typically
netid@gwu.edu) into the username field. - Handle the Redirection: Upon entering your email, the system will automatically recognize the domain and redirect your browser to the GW Central Authentication Service (CAS) login screen, identifiable by the university branding.
- Complete Password Verification: Type your NetID password into the secure input box and click submit.
- Approve Multi-Factor Authentication: Respond to the Duo prompt sent to your registered mobile device or select an alternative secondary verification method.
- Stay Signed In (Optional): Choose whether to remain signed in to reduce the frequency of authentication prompts on trusted, private computers. Do not select this option on public or shared laboratory terminals.
Method 2: Configuring Desktop and Mobile Mail Clients
To access GW Mail via native applications like Apple Mail, Microsoft Outlook for Desktop, or mobile mail apps on iOS and Android:
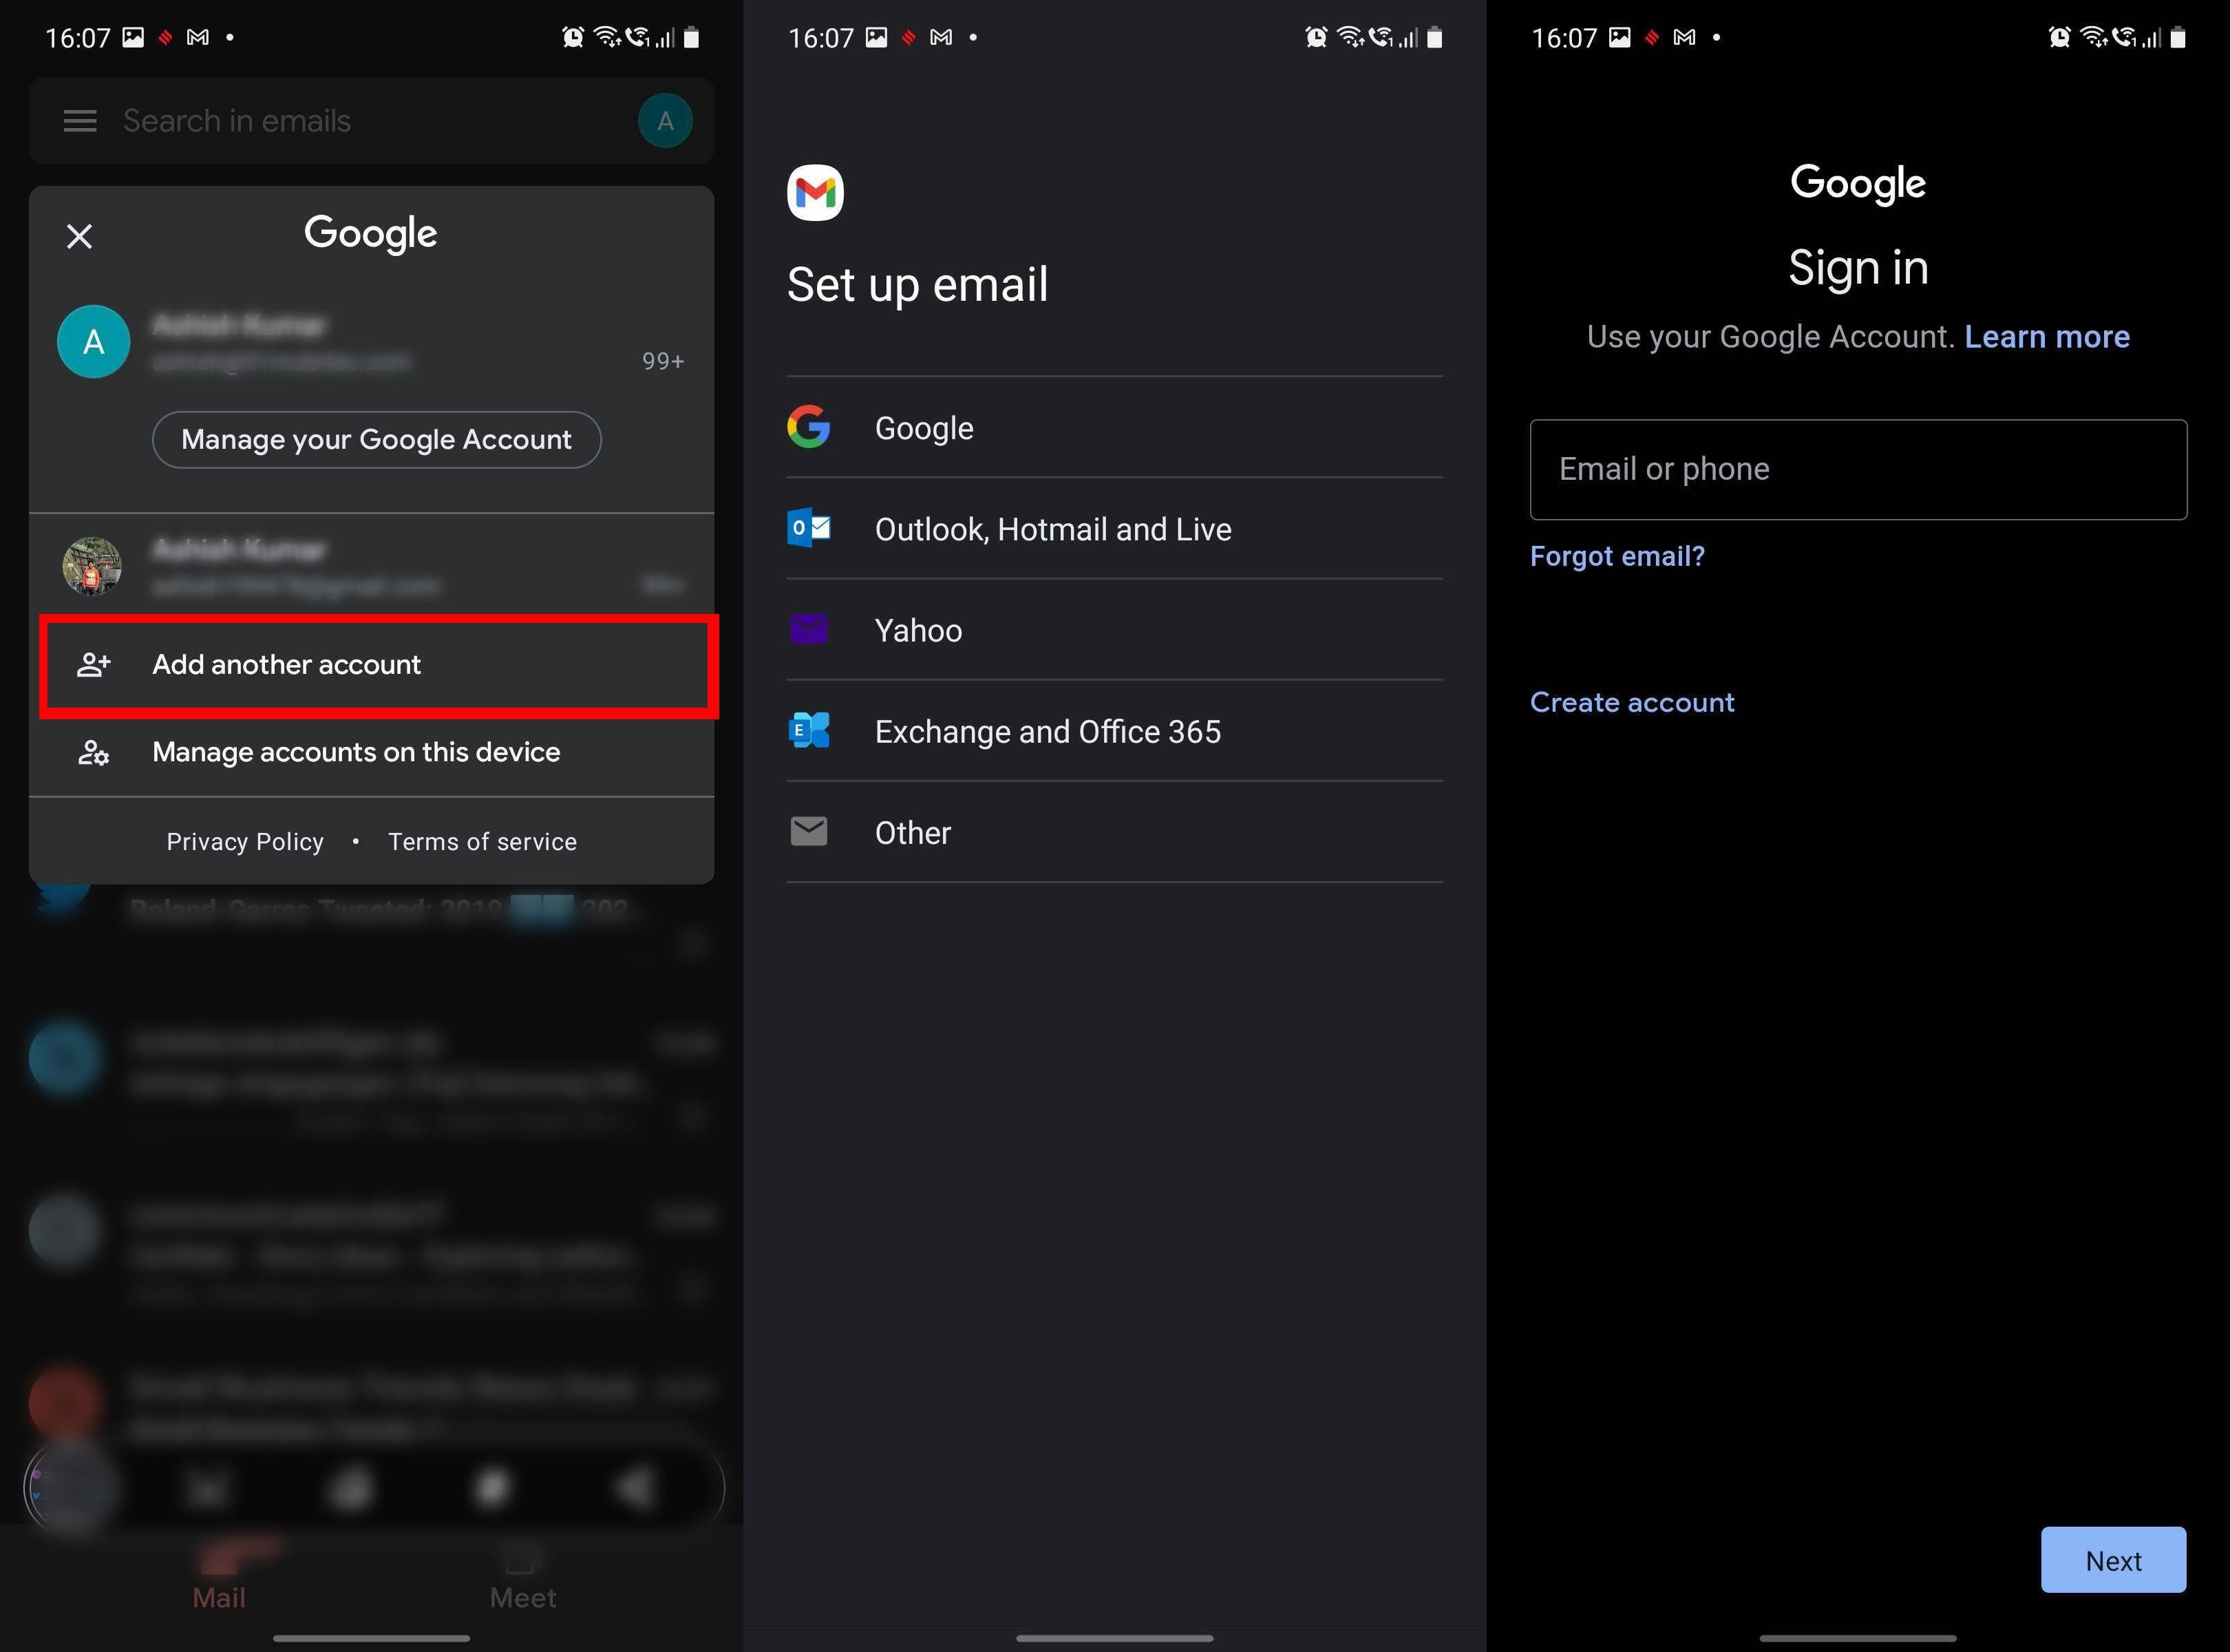
- Open the mail application settings and choose to add a new account.
- Select Work or School Account (Microsoft Exchange or Office 365) rather than a generic IMAP/POP configuration.
- Input your complete GW email address.
- The application will trigger an embedded browser window or redirect to the GW login gateway.
- Complete your NetID and Duo MFA verification. Once approved, the client synchronizes folders, contacts, and calendar items automatically.
| Access Method | Primary Advantage | Potential Limitation | Recommended Use Case |
|---|---|---|---|
| Web Browser (Outlook on the Web) | No software installation required; instant access from any public or shared computer. | Dependent on an active, stable internet connection; browser extensions may occasionally conflict. | Quick checks, travel, public terminals, and temporary workstation use. |
| Native Desktop App (Outlook / Apple Mail) | Offline access to downloaded messages; superior notification integration and calendar management. | Requires initial configuration and periodic credential re-authentication. | Daily office work, heavy email volume, and advanced calendar organization. |
| Mobile App (iOS / Android) | Real-time push notifications; portable access to contacts and schedules on the go. | Smaller screen space; battery consumption from background synchronization. | On-the-campus mobility, urgent communications, and calendar management. |
Troubleshooting Common Login Errors
Even with proper preparation, technical hurdles can disrupt access. Below are detailed solutions for the most frequent issues encountered during the authentication process.
Incorrect Password or Expired Credentials
If the system rejects your password, verify that caps lock is disabled. If you suspect your password has expired or you have forgotten it, do not guess repeatedly, as multiple failed attempts will temporarily lock your NetID. Instead, visit the central identity management portal to reset your password using security challenge questions or an alternative recovery email address.
Duo MFA Failures and Push Not Received
If push notifications fail to arrive on your smartphone:
- Ensure your device has an active cellular or Wi-Fi data connection.
- Open the Duo Mobile application manually to check for pending authentication requests.
- Generate a passcode directly inside the Duo app and type it into the login prompt.
- If you have replaced your phone or changed your phone number without updating your security profiles, contact the IT support desk to register your new device.
Browser Redirect Loops and Cache Corruption
Occasionally, authentication tokens become corrupted, causing the browser to bounce endlessly between Microsoft and GW login pages. To resolve this:
- Close all open browser windows related to the portal.
- Clear your browser's cache, cookies, and local storage for
gwu.eduandmicrosoftonline.com. - Open an incognito or private browsing window and attempt the login process again.
Frequently Asked Questions
What should I do if my NetID account is locked out?
NetID accounts typically lock automatically after a set number of consecutive failed password attempts to prevent brute-force attacks. To unlock your account, wait approximately 15 to 30 minutes for the lockout timer to expire, or immediately reset your password using the official self-service identity tools provided by GW IT.
Can I forward my GW Mail to a personal email address?
While university policy or technical settings may allow external forwarding under specific guidelines, doing so for official university correspondence is generally discouraged due to security and FERPA compliance regulations. Important academic and administrative notices must remain within the secure, encrypted university environment.
How do I update my mobile number for Duo multi-factor authentication?
You can manage your registered MFA devices by logging into the GW IT Account Management portal from a trusted computer using an active session, navigating to the security settings section, and adding or removing phone numbers and hardware tokens as needed.
Is it safe to stay signed in on a shared library computer?
No. Selecting the "Stay signed in" option on public, campus library, or shared laboratory computers allows subsequent users of that machine to access your inbox, personal files, and institutional data. Always use private browsing windows on public hardware and explicitly sign out and close the browser when finished.
Who should I contact if I cannot resolve a persistent login error?
If standard troubleshooting steps fail, reach out directly to the George Washington University Division of Information Technology (IT) Support Center via phone, online chat, or by visiting their physical help desks on campus for direct administrative assistance.
Next Actions
To maintain secure and uninterrupted access to your institutional inbox, verify that your Duo multi-factor authentication methods are up to date and bookmark the official GW IT Support Center for future reference. If you are setting up a new device, complete the Office 365 client configuration steps using an incognito browser window to prevent credential caching conflicts.