The Digital Operational Resilience Act (DORA) does not mandate a single "license" in the traditional sense of a permit to operate, but rather establishes a comprehensive regulatory framework for financial entities in the European Union to ensure they can withstand, respond to, and recover from ICT-related disruptions. Compliance requires demonstrating robust digital operational resilience through specific reporting, testing, and governance protocols.
The Regulatory Framework of DORA
The Digital Operational Resilience Act, formally Regulation (EU) 2022/2554, represents a paradigm shift in how the European financial sector manages information and communication technology (ICT) risk. Often mistakenly referred to as a "DORA license," the regulation is not a permission-based entry requirement but a mandatory standard that all financial entities operating within the EU must uphold. Its primary goal is to harmonize the rules relating to digital operational resilience, ensuring that banks, insurance companies, investment firms, and other financial institutions maintain a consistent level of protection across the single market.
For many organizations, the challenge lies in shifting from a siloed approach to IT risk management toward an integrated, board-level mandate. Under DORA, ICT risk is no longer considered a purely technical issue for the IT department; it is treated as a core component of overall operational risk. Organizations must ensure that their digital infrastructure is resilient enough to endure severe operational disruptions, thereby protecting both the institution and the broader financial stability of the EU.
Entities Subject to the Regulation
The scope of DORA is exceptionally broad, covering nearly every type of financial entity authorized to operate within the European Union. This includes, but is not limited to, credit institutions, payment institutions, electronic money institutions, investment firms, and crypto-asset service providers. Additionally, the regulation applies to ICT third-party service providers that supply essential services to these financial entities.
Because the regulation applies to the entire financial ecosystem, the "license to operate" concept is functionally represented by the institution’s ability to prove compliance during regulatory audits. Failure to meet these requirements can lead to significant financial penalties, mandatory remedial actions, and potential reputational damage that may threaten an entity's existing authorization to perform financial activities.
Key Financial Sectors Impacted
- Banking and Credit: Retail and investment banks.
- Payment Services: Payment and electronic money institutions.
- Investment and Securities: Central securities depositories, central counterparties, and trading venues.
- Insurance: Insurance and reinsurance undertakings.
- Crypto-Assets: Providers authorized under the Markets in Crypto-Assets (MiCA) regulation.
Core Pillars of Operational Resilience
To achieve compliance, financial entities must adhere to five primary pillars outlined by the regulation. These pillars represent the operational requirements that audit bodies use to verify that an entity has reached the necessary maturity level.
1. ICT Risk Management
Entities must have a comprehensive framework that includes strategies, policies, and internal controls for identifying, protecting against, detecting, and responding to ICT risks. This requires mapping all ICT assets and vulnerabilities, conducting continuous risk assessments, and ensuring that senior management is actively involved in risk governance.
2. ICT-Related Incident Reporting
DORA mandates a strict, standardized process for classifying and reporting ICT-related incidents to competent authorities. Entities must demonstrate the capability to detect threats in real-time and provide detailed updates on the impact, the nature of the breach, and the recovery steps being taken.
3. Digital Operational Resilience Testing
Static security audits are no longer sufficient. Organizations must conduct regular, intelligence-led penetration testing and threat-led penetration testing (TLPT). These tests must be performed by independent parties—either internal or external—to ensure an unbiased assessment of the entity’s ability to withstand actual cyber threats.
4. Management of ICT Third-Party Risk
Many financial entities rely on cloud providers, data centers, and software vendors. DORA requires institutions to manage these risks as if they were internal. This involves rigorous pre-contractual due diligence, clearly defined service level agreements (SLAs), and the right to audit these third-party providers.
5. Information Sharing
The regulation encourages the exchange of cyber threat intelligence among financial entities. By participating in communities that share information on tactics, techniques, and procedures (TTPs), institutions collectively raise the barrier to entry for malicious actors.
Technical Requirements and Implementation
The implementation process for DORA requires a deep integration between legal, risk, and technical teams. Unlike standard software compliance, DORA requires continuous monitoring. In 2026, the focus for many entities is on the refinement of the "ICT asset registry," a mandatory document that lists all components supporting the organization's business functions.
Comparative Overview of DORA Compliance Components
| Feature | Requirement Status | Objective |
|---|---|---|
| Asset Mapping | Mandatory | Maintain an exhaustive registry of all ICT assets. |
| Incident Reporting | Mandatory | Streamlined, time-sensitive notification to authorities. |
| Penetration Testing | Periodic | Regular stress tests under realistic attack scenarios. |
| Third-Party Risk | Contractual | Enforced security standards for all external vendors. |
| Board Oversight | Constant | Active accountability for ICT-related risk policies. |
Managing ICT Third-Party Risks
One of the most complex aspects of the DORA framework is the regulation of third-party service providers. Financial institutions often outsource critical functions, which can create a single point of failure if multiple banks rely on the same cloud provider. DORA mandates that contracts with these providers must include specific clauses regarding security standards, data localization, and the ability of the financial entity (or the regulator) to perform audits.
If you are currently evaluating your vendor contracts in 2026, you must ensure that every service-level agreement reflects the technical requirements of the Act. Vendors that fail to comply with these standards may effectively become "non-viable" partners for EU-based financial institutions, as the financial entity would be unable to meet its own regulatory obligations while maintaining that partnership.
Reporting and Oversight Cycles
DORA introduces a synchronized approach to oversight. Financial regulators at the national level, working alongside European Supervisory Authorities (ESAs), oversee compliance. These bodies have the power to demand access to documentation, require improvements to security protocols, and impose fines for non-compliance.
The reporting cycle is not a one-time event. Entities must maintain a continuous documentation trail. This includes:
- Annual reporting of ICT risks and incident statistics.
- Ad-hoc reporting during major incidents.
- Scheduled test results from resilience programs.
Common Challenges and Pitfalls
Many organizations struggle with the transition to DORA because they underestimate the necessity of board-level engagement. If the board of directors does not have a clear understanding of the ICT risk profile, the organization is inherently non-compliant regardless of how robust the IT infrastructure is.
Another common mistake is the "compliance-only" mindset. Organizations that treat DORA as a box-ticking exercise often find themselves overwhelmed by the technical requirements. Because DORA is risk-based, it expects the organization to adapt its security posture based on the actual threat landscape, not just a static set of rules.
Preparing for Regulatory Verification
To prepare for verification in 2026, firms should conduct a thorough gap analysis. This involves comparing current security documentation and incident response protocols against the specific mandates of the Regulation (EU) 2022/2554. If your organization is operating in multiple jurisdictions, it is vital to reconcile DORA requirements with local laws to ensure that security measures are consistent but locally compliant.
Steps for readiness:
- Inventory Assessment: Catalog all ICT assets and classify their criticality to business functions.
- Gap Analysis: Evaluate current security policies against the five pillars of DORA.
- Vendor Audit: Review contracts with all ICT service providers to verify compliance clauses.
- Operational Drills: Execute incident response simulations to test reporting speed and accuracy.
- Governance Update: Ensure the management board has designated responsibility for ICT risk management.
Frequently Asked Questions
Does DORA require a specific license to operate?
No, DORA is not a licensure system. It is a regulatory framework governing operational resilience. Compliance is a requirement for maintaining the existing authorization of any financial entity operating in the EU.
Who is responsible for DORA compliance within an organization?
The management body—typically the board of directors—holds the ultimate responsibility. They are required to define, approve, and oversee the execution of the organization's ICT risk management framework.
How are third-party ICT service providers held accountable?
Through "criticality assessments." If a provider is deemed critical, the regulatory authorities have direct oversight powers over them, and the financial entities utilizing them must strictly enforce compliance via contractual agreements.
What happens if an organization fails to meet DORA requirements?
Non-compliance can lead to significant administrative penalties, periodic penalty payments to compel compliance, and potential regulatory intervention that could restrict or suspend an entity's financial service operations.
Is DORA only applicable to the European Union?
Yes, it applies to financial entities established within the EU. However, it also impacts international organizations that provide services to these entities, effectively extending the influence of these security standards globally.
Does DORA change data privacy laws like GDPR?
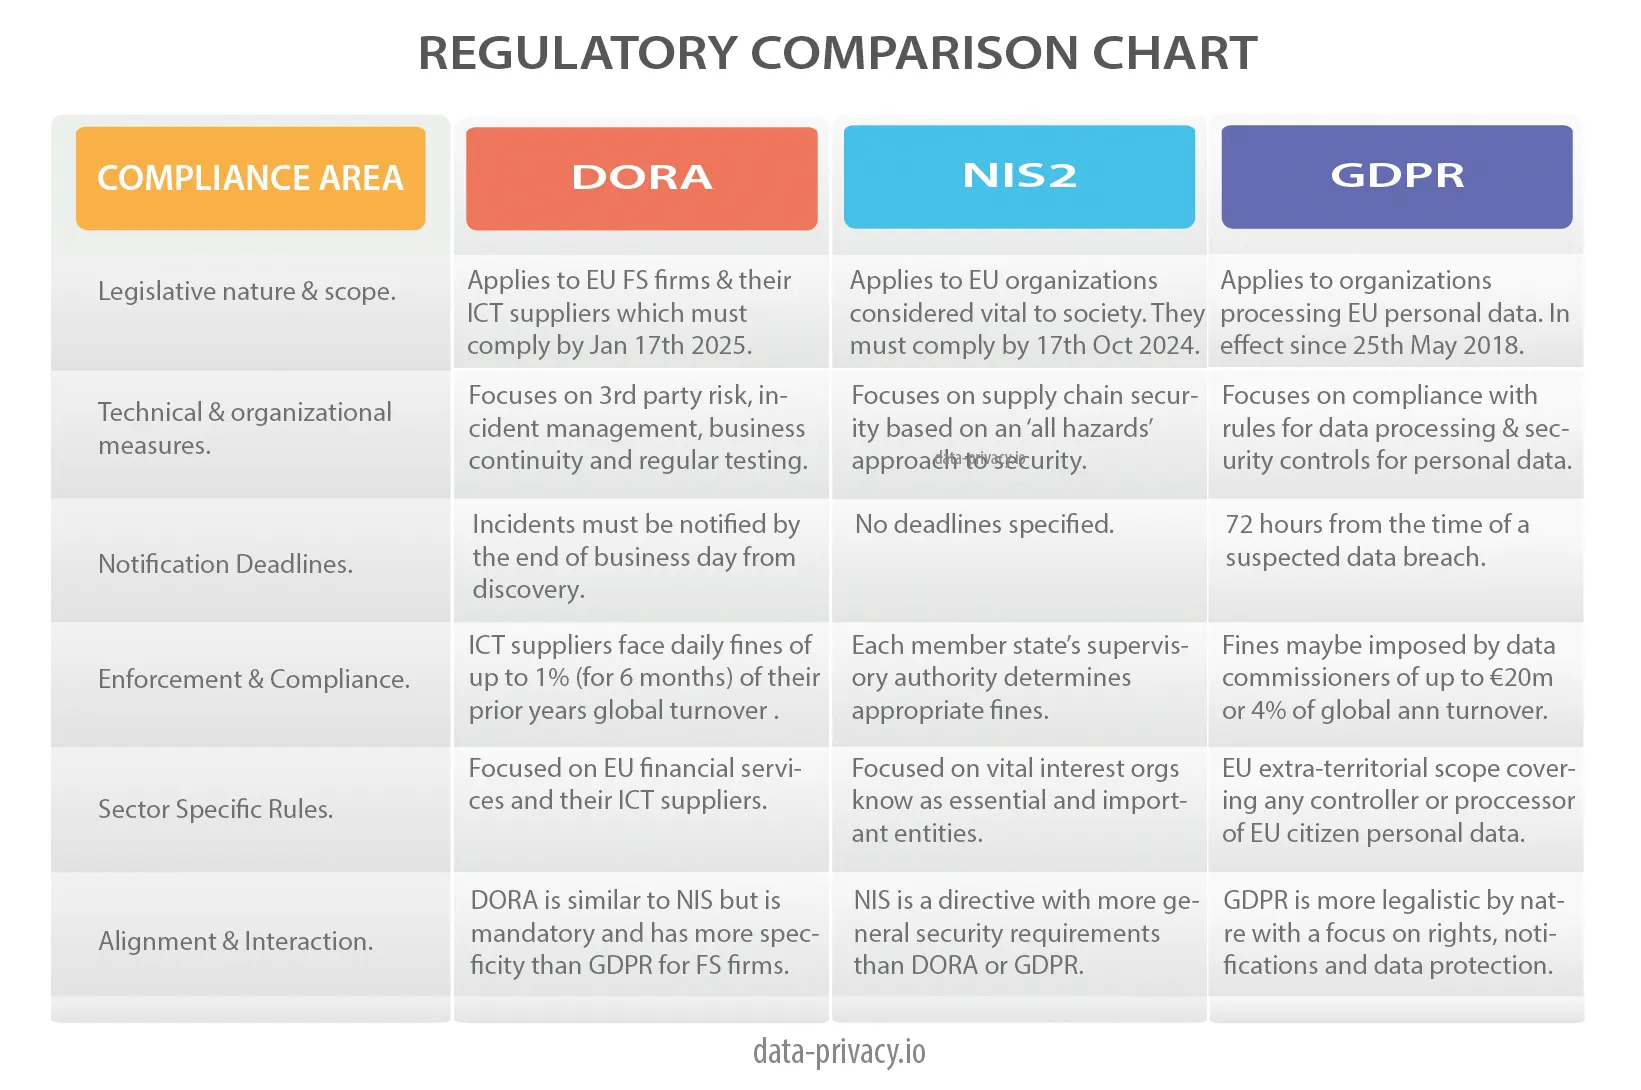
DORA complements GDPR. While GDPR focuses on the protection of personal data, DORA focuses on the operational availability and integrity of the ICT systems that process such data. Both must be managed in parallel.
Final Recommendation
For organizations navigating the regulatory landscape, the most effective next step is to initiate a cross-functional task force consisting of IT security, legal, and risk management departments. Focus your immediate efforts on the ICT asset registry and the review of third-party contracts, as these two areas are the most common points of failure during regulatory inspections. Do not wait for a formal audit notification to begin your gap analysis; the complexity of mapping third-party dependencies suggests that early, rigorous documentation is the primary defense against future regulatory friction.