iOS sideloading refers to the practice of installing applications on Apple mobile devices from sources other than the official Apple App Store, such as direct downloads of application archive files or third-party alternative marketplaces. Depending on geographic location, regulatory frameworks, and system configuration, users can execute sideloading through developer certificates, enterprise provisioning, or regulatory-mandated alternative app stores.
Understanding iOS Sideloading and Its Ecosystem
Sideloading on iOS has historically diverged significantly from the open-file installation models seen on desktop operating systems or Android. Apple designed iOS with a tightly controlled security architecture known as a "walled garden," which requires every application distributed to standard users to undergo manual and automated review through App Review, sign with an Apple-issued cryptographic certificate, and execute within a strict application sandbox.
When users bypass the App Store to install software, they circumvent these built-in verification pathways. This practice shifts the burden of trust from Apple’s centralized moderation team to the user, the developer, and any third-party signing services involved in the process. Understanding how this ecosystem operates requires analyzing the technical enforcement mechanisms, the regional variances driven by antitrust legislation, and the operational differences between standard user installations and developer provisioning.
The Walled Garden and Cryptographic Enforcement
At the heart of iOS security is code signing. iOS refuses to execute any binary file unless it carries a valid cryptographic signature issued by Apple or traced back to an authorized provisioning profile.
- Provisioning Profiles: These files dictate where and how an app can run. They contain a list of authorized device identifiers (UDIDs), explicit application entitlements (such as push notifications or iCloud access), and a digital signature from Apple.
- App Store Distribution: Standard applications receive a signature directly from Apple’s servers upon publication, allowing any consumer device to run them without additional configuration.
- Sideloading Mechanisms: Sideloading circumvents standard App Store deployment by generating alternative provisioning profiles, utilizing developer accounts, or leveraging legal mandates that force Apple to allow alternative app distribution marketplaces under specific regional laws.
Regional Legal Shifts: The European Union and the Digital Markets Act
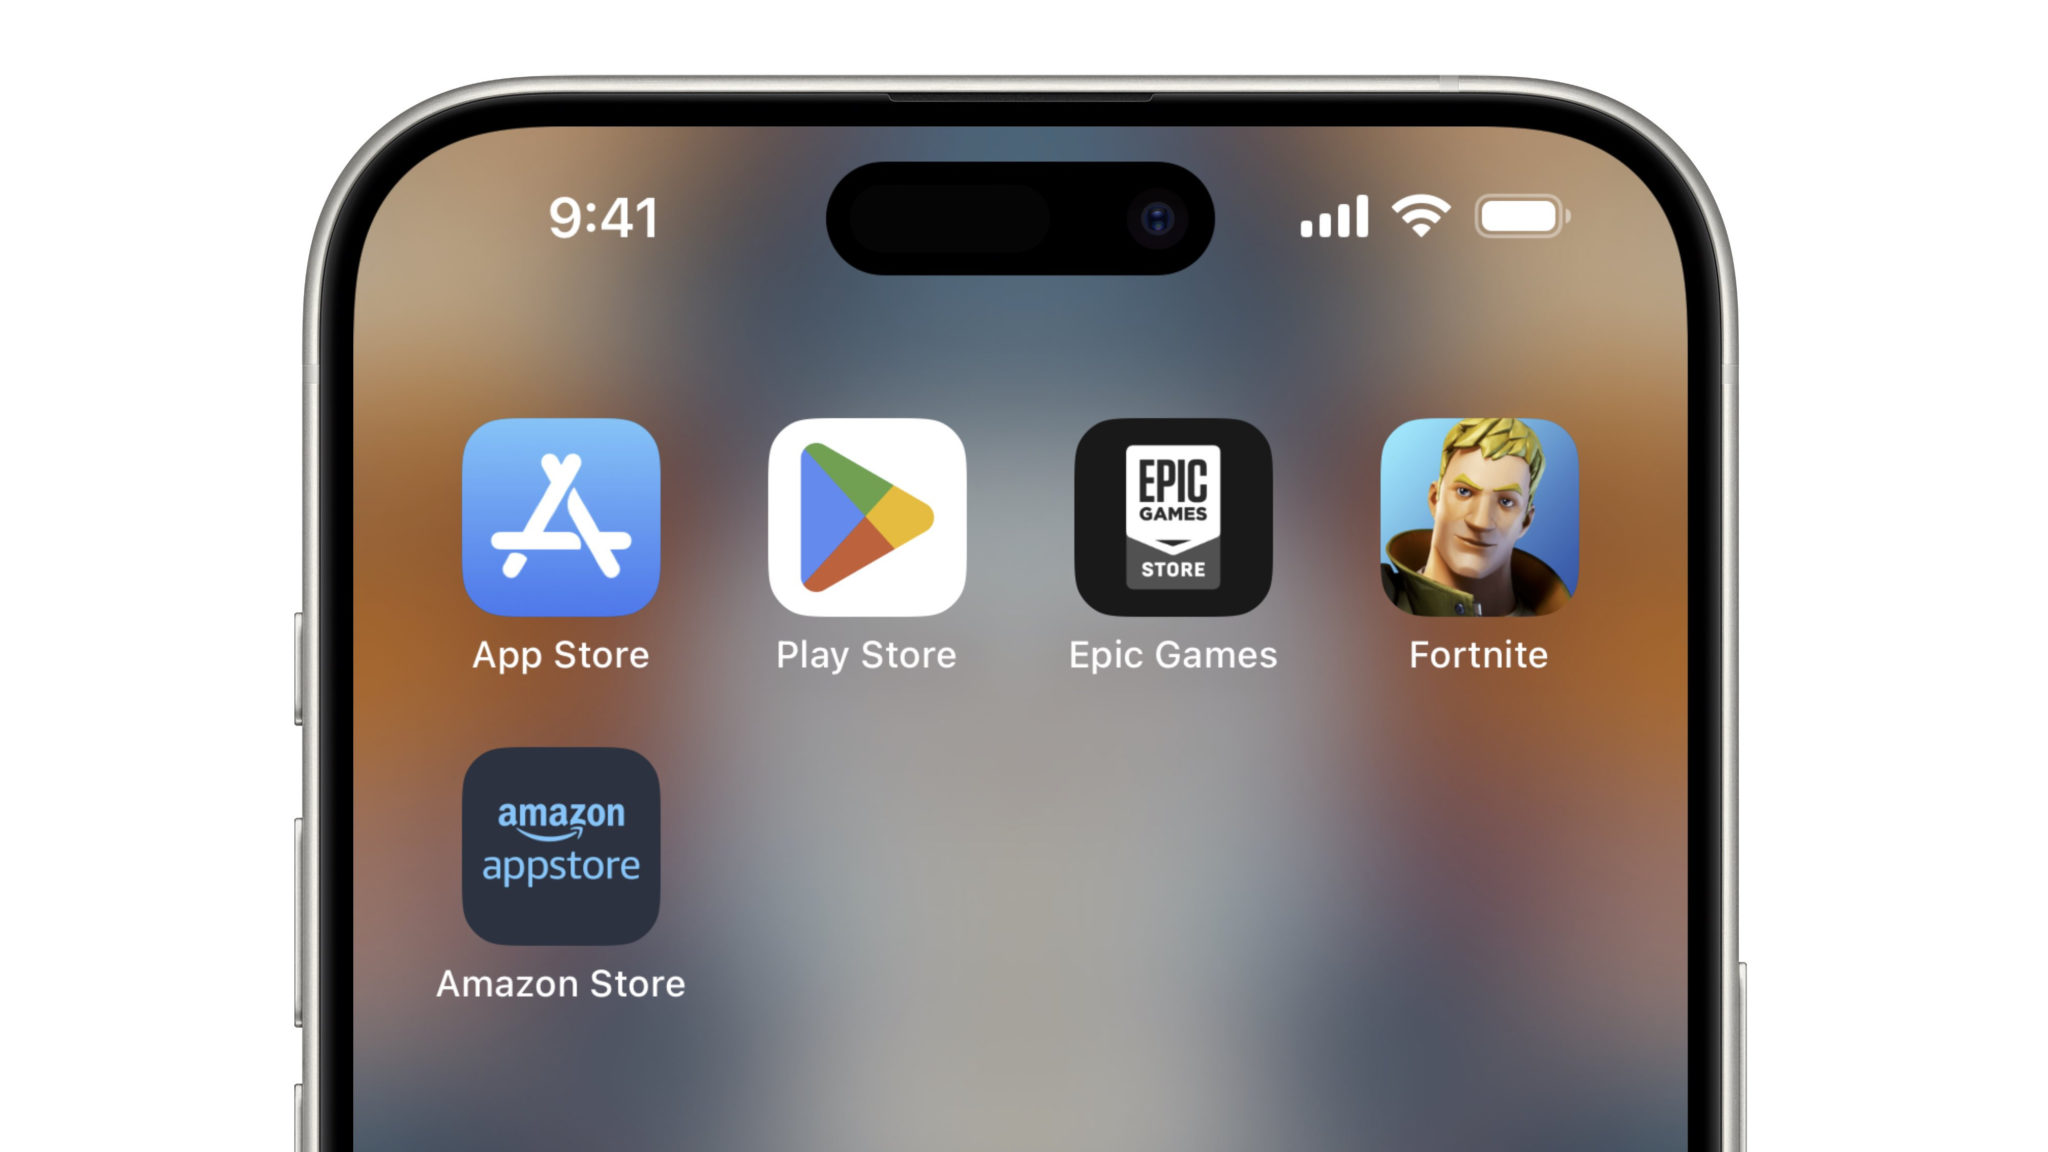
The regulatory landscape surrounding iOS sideloading shifted significantly with the implementation of the European Union's Digital Markets Act (DMA). Designated as a gatekeeper under the DMA, Apple was required to introduce alternative ways for developers to distribute iOS apps to users located within the European Union.
For users residing in the EU, iOS supports alternative app marketplaces, provided those marketplaces and the apps they host meet specific Apple authorization criteria regarding malware scanning, transparency, and developer accountability. Users outside the EU, however, remain bound by the traditional global iOS application delivery framework, where the official App Store is the sole officially supported mechanism for software installation.
Methods and Technical Approaches to iOS Sideloading
Users and developers employ several distinct methods to sideload applications onto iOS devices, each carrying specific requirements, maintenance overheads, and functional limitations.
| Method | Core Requirement & Limitation |
|---|---|
| Free Apple ID Signing | Requires re-signing every 7 days; max 3 active side-loaded apps per device. |
| Paid Developer Account | Valid Apple Developer Program ($99/yr); apps last up to a year; no 3-app limit. |
| Enterprise Certificates | Designed for internal business use; prone to rapid Apple revocation. |
| EU Alternative Stores | Restricted to users physically in the EU; governed by regional compliance. |
Free Developer Account Sideloading
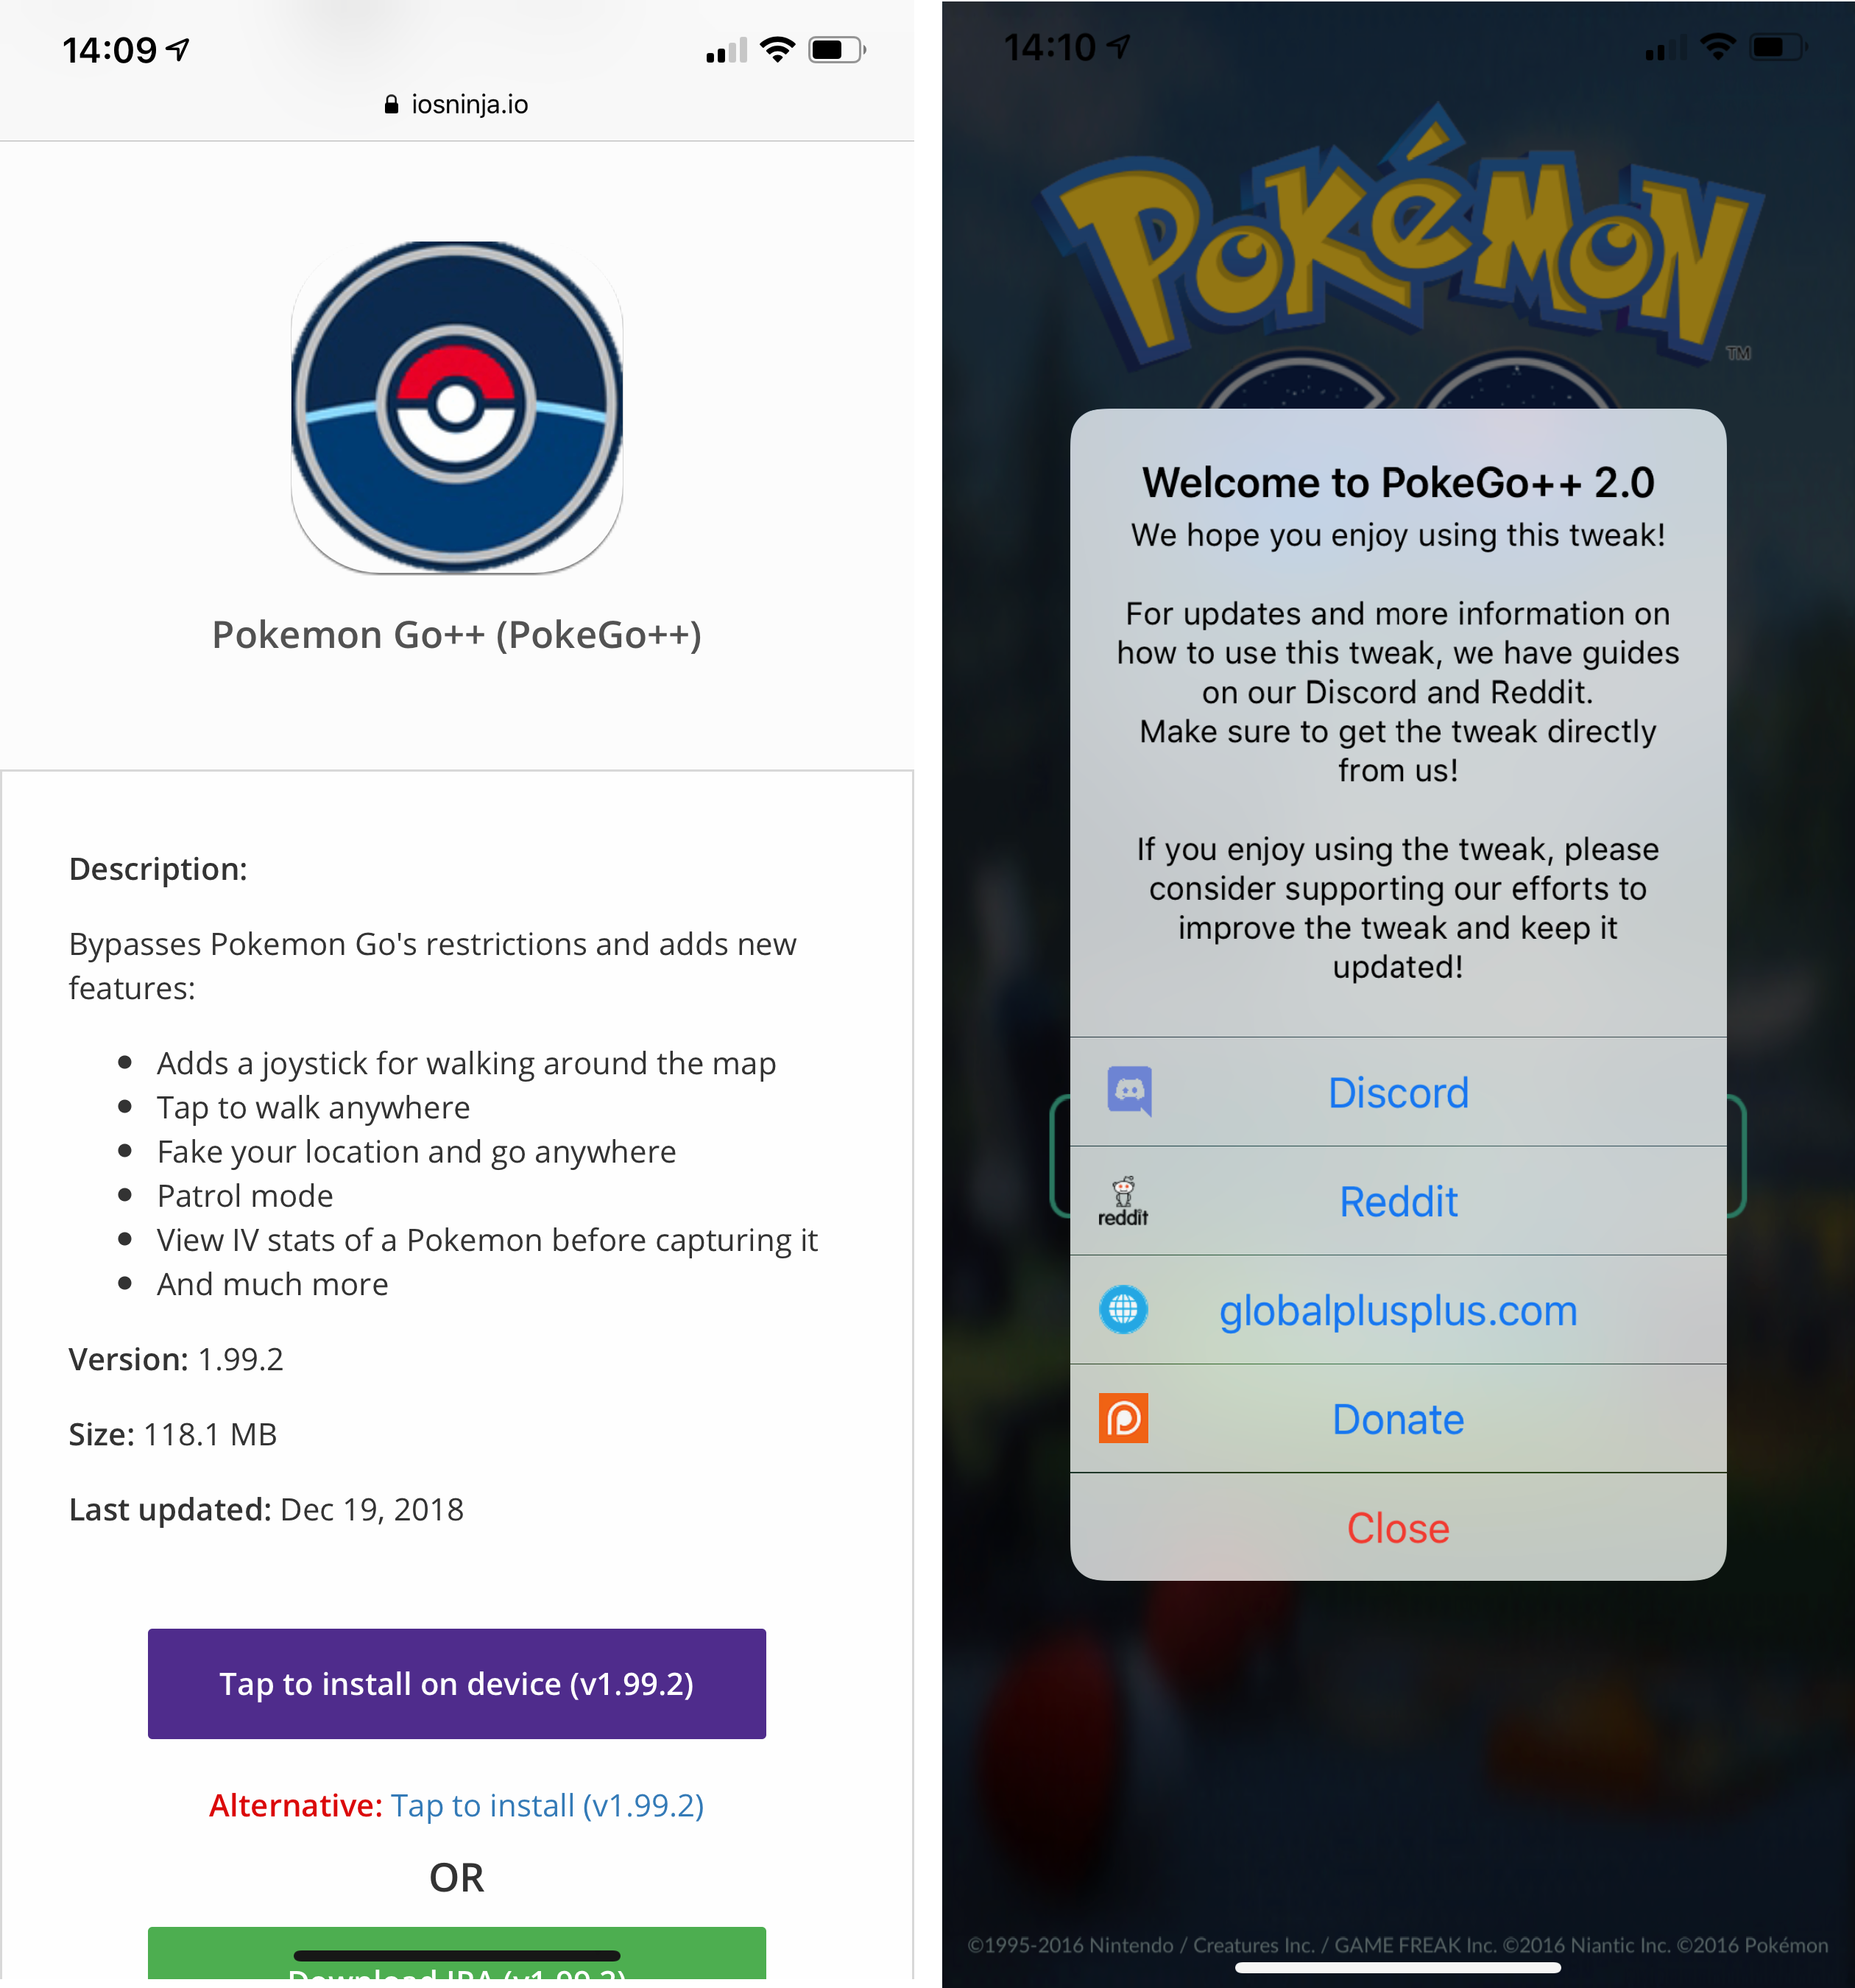
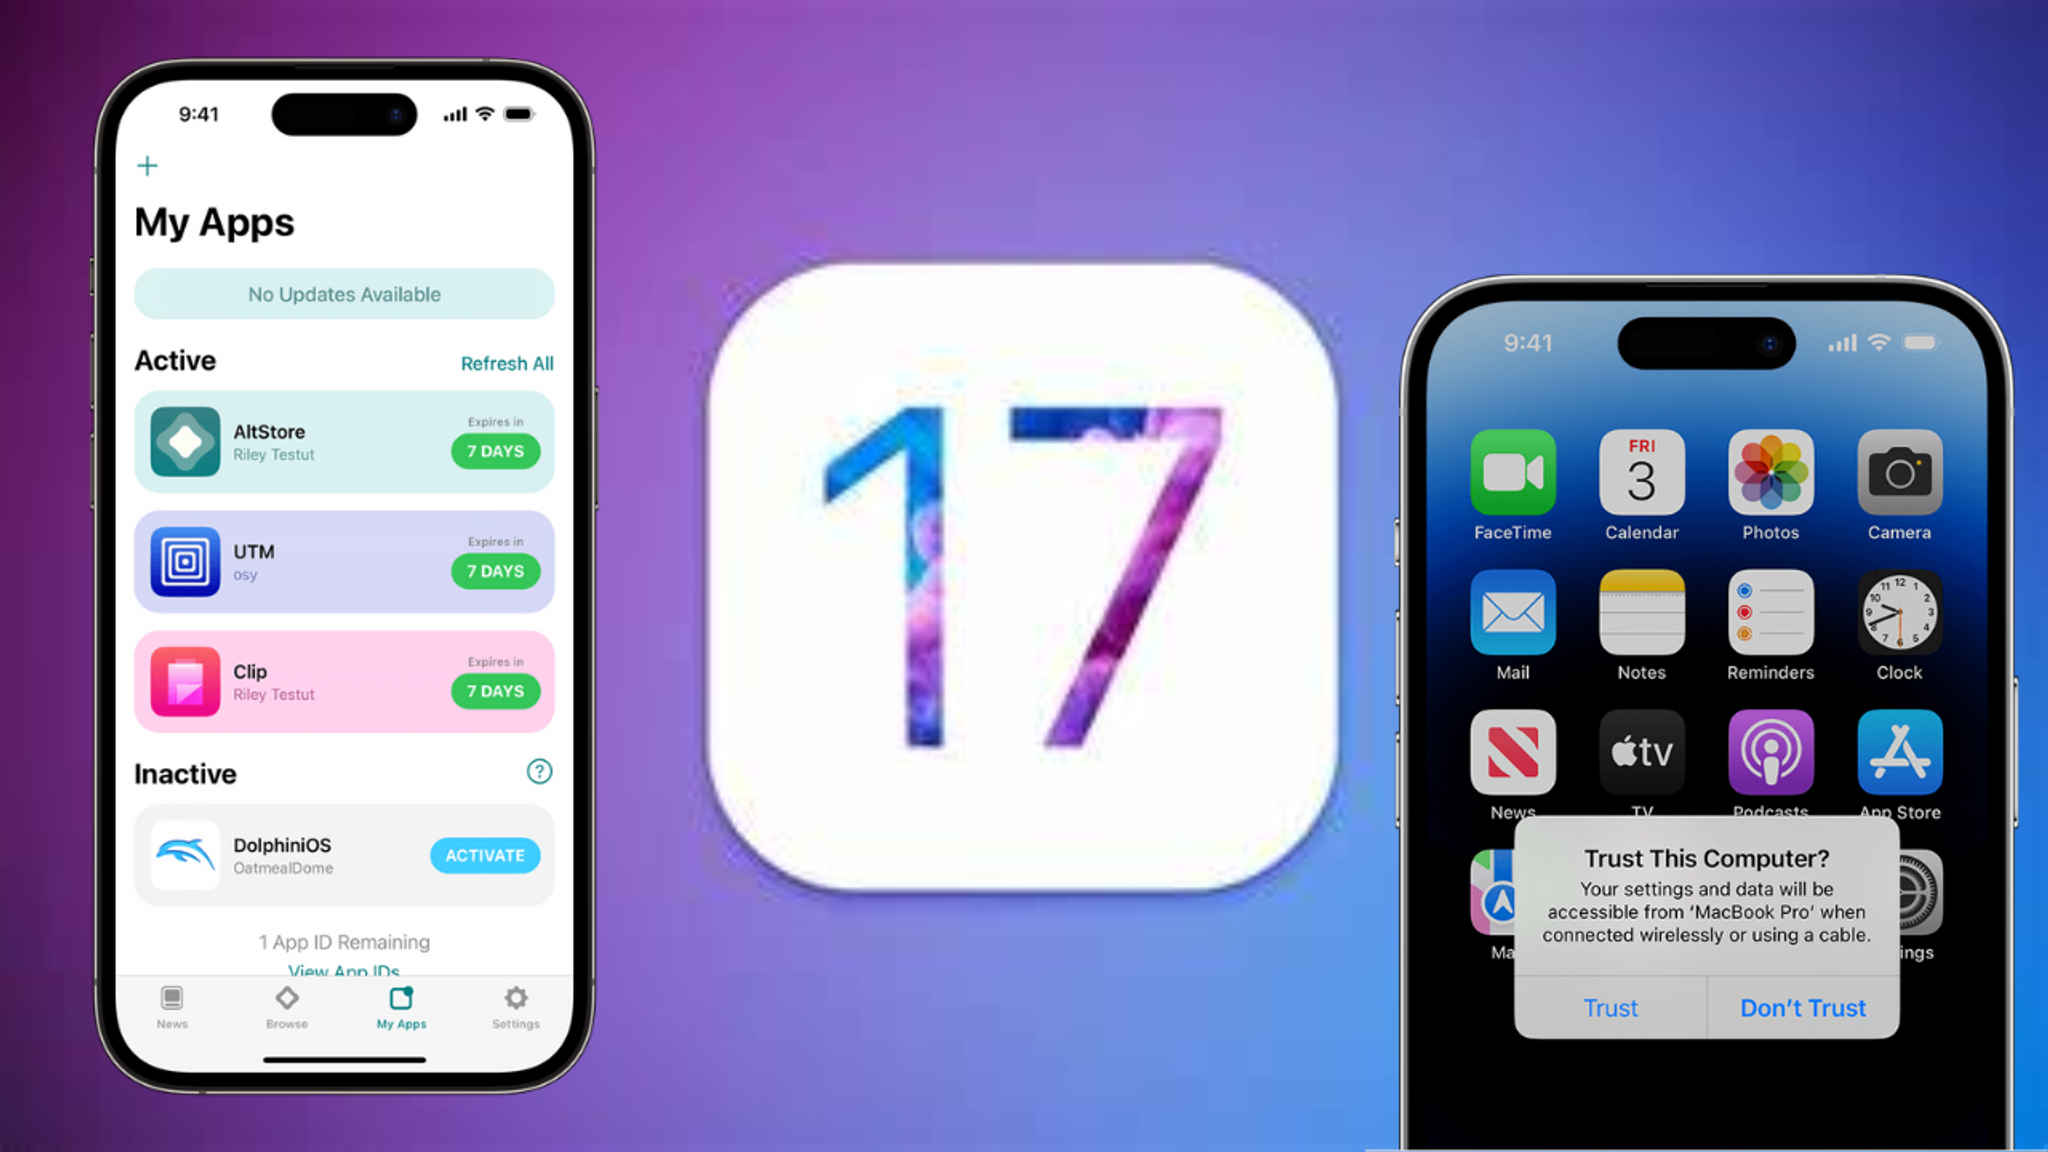
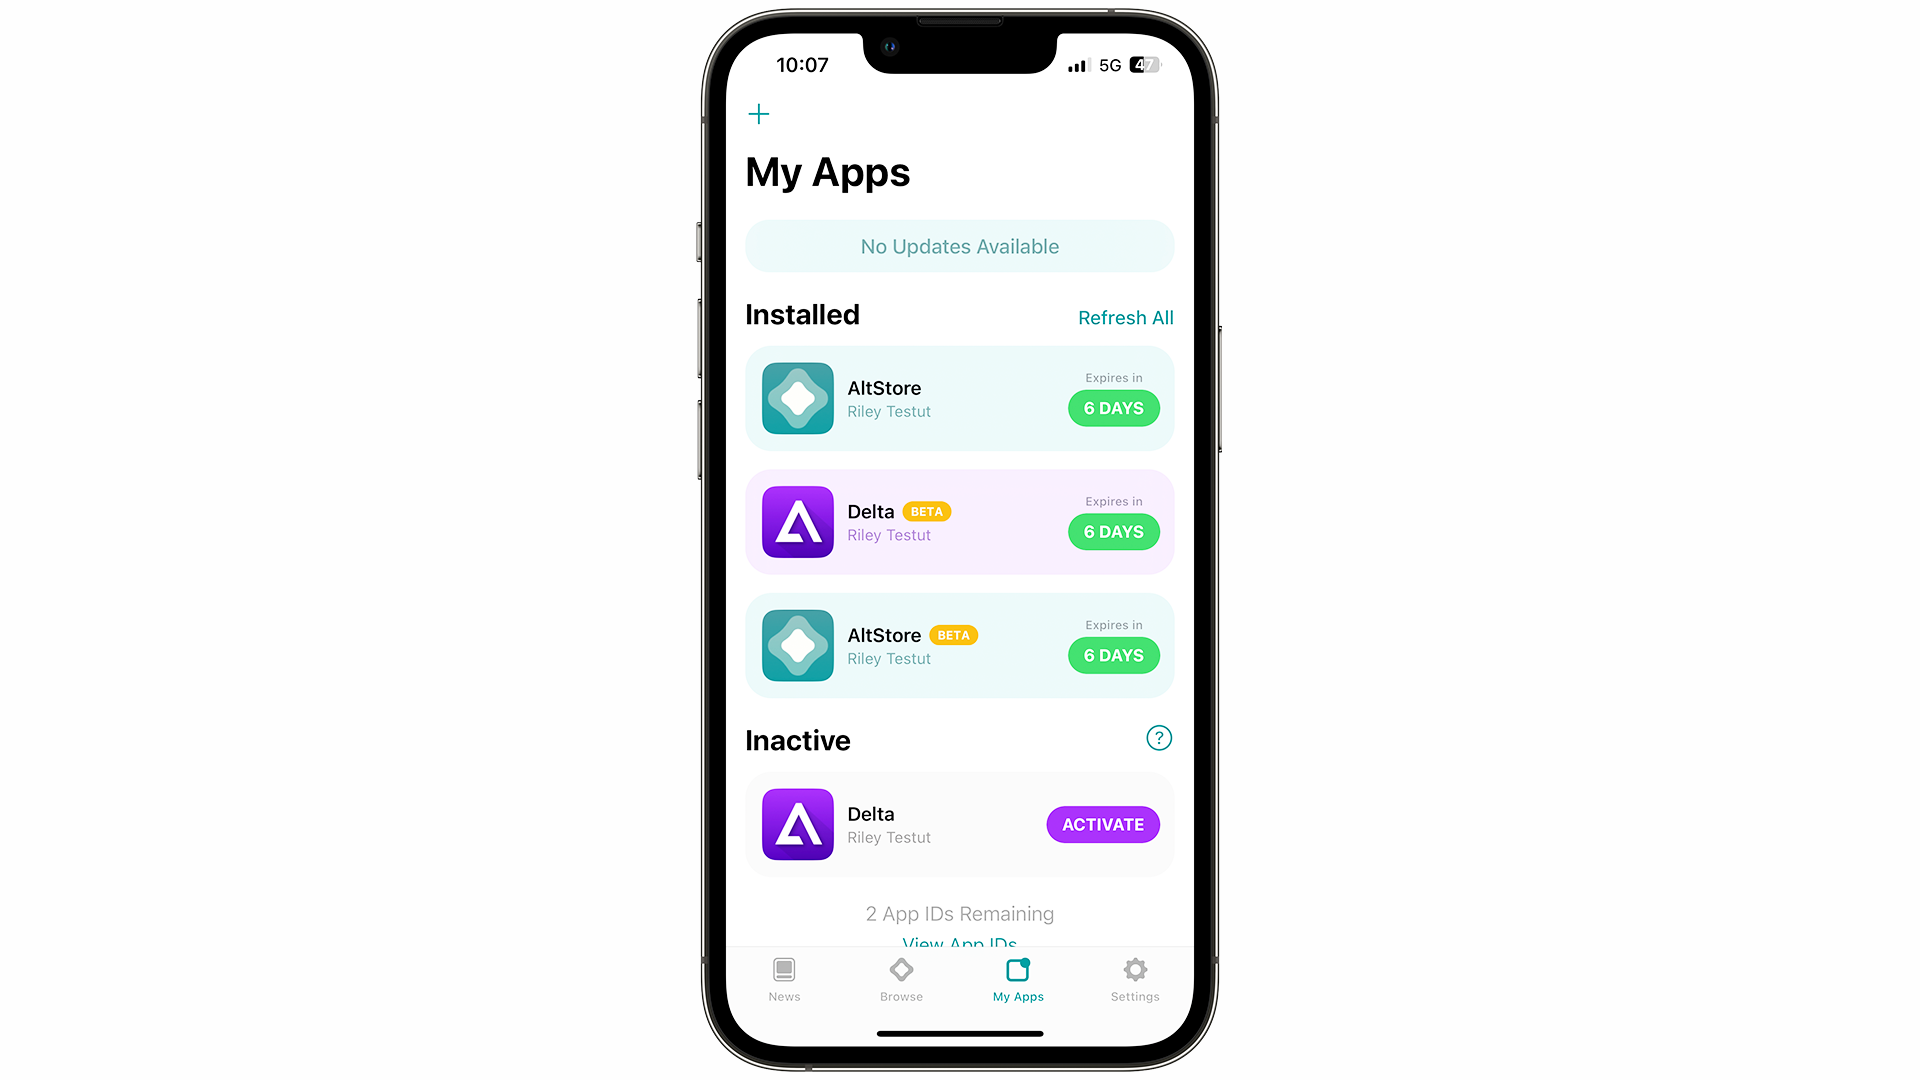
Individual users can utilize standard desktop utility software, such as AltStore or Sideloadly, combined with a free Apple ID to sign and install application files (IPA format) directly to their devices.
- The 7-Day Expiration Rule: Free Apple ID provisioning profiles expire automatically after seven days. To keep sideloaded apps operational, users must periodically refresh the apps using a companion desktop application connected via local Wi-Fi or USB.
- App Limits: Free accounts are generally restricted to a maximum of three active sideloaded applications per device simultaneously.
Paid Apple Developer Program Sideloading
Enrolling in the paid Apple Developer Program (costing $99 USD annually) removes many restrictions associated with free-tier sideloading.
- Extended Validity: Provisioning profiles generated via a paid developer account remain valid for up to one year before requiring renewal.
- Expanded Capacity: Paid accounts allow developers to install a larger number of test builds and custom applications across registered test devices without the strict three-app cap imposed on free accounts.
Enterprise Provisioning and Third-Party Signing Services
Enterprise certificates are intended for large organizations to distribute proprietary internal apps to employees without passing through the public App Store.
- Public Abuse: Third-party signing services often misuse enterprise certificates to distribute modified, cracked, or pirated applications to retail consumers.
- Revocation Risk: Apple actively monitors and revokes enterprise certificates used for public distribution. When a certificate is revoked, all apps signed with it instantly crash upon launch across all connected devices until reinstalled with a valid signature.
Comparing iOS Sideloading Options
Evaluating the right approach to iOS software installation requires weighing convenience, longevity, safety, and regulatory compliance.
| Sideloading Method | Cost | Certificate Lifespan | Geographic Restriction | Primary Use Case |
|---|---|---|---|---|
| Official App Store | Free | Managed by Apple | Global | Standard consumers seeking verified apps |
| Free Developer ID | Free | 7 Days | Global | Personal testing, open-source utilities |
| Paid Developer Account | $99/Year | 1 Year | Global | App development, private distribution |
| EU Alternative Marketplaces | Varies | Managed by Marketplaces | European Union Only | Regional users accessing alternative app stores |
| Enterprise Provisioning | $299/Year | 1 Year (Subject to Revocation) | Global | Corporate internal app deployment |
Security, Privacy, and Operational Risks
While sideloading provides freedom to run customized software, emulators, or alternative utilities not permitted in the official App Store, it introduces substantial security trade-offs.
Malware and Unauthorized Data Access
The official App Store uses strict automated and human code reviews to screen for malicious behavior, hidden APIs, and privacy violations. Sideloaded IPAs downloaded from unverified internet repositories may contain malicious payloads capable of intercepting keystrokes, recording audio, or siphoning personal data. Because iOS sandboxing limits inter-process communication, a poorly written or malicious sideloaded app still poses risks to user files stored within its container or synced to cloud accounts if explicit permissions are granted.
System Stability and Battery Drain
Applications compiled outside standard developer tooling or forced onto devices via unstable signing methods can experience unexpected memory leaks, background processing loops, and elevated battery consumption. Furthermore, system updates issued by Apple can alter private APIs or security enforcement protocols, causing previously stable sideloaded applications to break entirely.
Step-by-Step Guide: Sideloading via Desktop Companion Tools
For users utilizing free or paid developer accounts via desktop utility software (such as AltStore or Sideloadly), the following sequence outlines the standard operational procedure.
- Prepare Your Environment: Download an authorized desktop client and install the matching companion daemon on your macOS or Windows computer. Connect your iOS device via a trusted USB cable.
- Authenticate with Apple ID: Enter your Apple ID credentials into the desktop utility. (Users often utilize a secondary burner Apple ID for security purposes).
- Install the Companion App: Follow the on-screen prompts to install the initial management app onto your iOS device through the local provisioning profile.
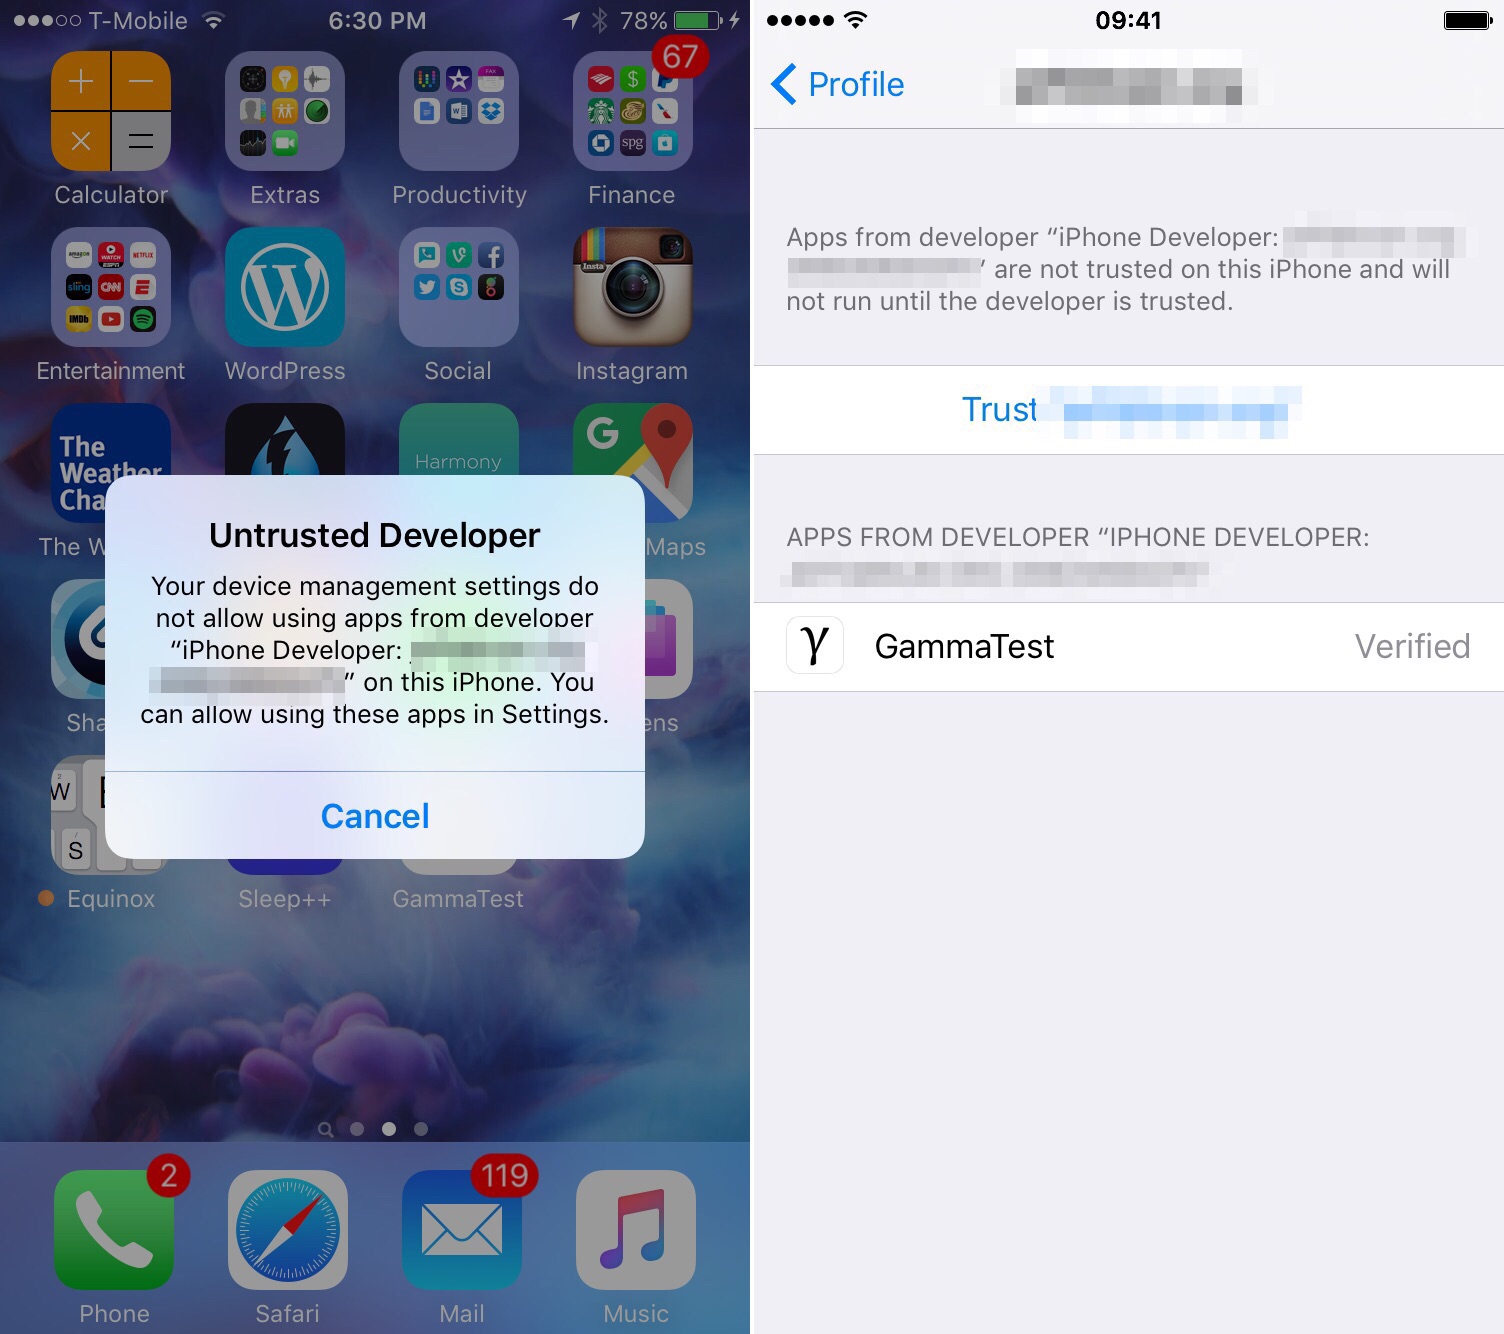
- Trust the Certificate: On your iOS device, navigate to Settings > General > VPN & Device Management, locate your developer profile, and tap Trust.
- Import and Sign IPAs: Download the desired application package (IPA file), send it to your device management app, and input your Apple ID credentials to complete the code-signing process.
- Maintain App Refresh: If using a free Apple ID, ensure your computer and device connect to the same local network at least once every seven days to refresh the app certificates before they expire.
Frequently Asked Questions
Is iOS sideloading legal?
Yes, sideloading software onto personal computing hardware is legal in many jurisdictions, though the legal status varies globally regarding copyright circumvention and terms-of-service violations. In the European Union, the Digital Markets Act explicitly requires Apple to permit alternative app distribution for regional users. However, sideloading does not exempt users or developers from intellectual property laws or copyright infringement regulations.
Will sideloading void my iPhone warranty?
Sideloading software does not inherently void standard hardware warranties provided by Apple. However, if a software modification, custom bootloader, or malicious sideloaded application causes permanent hardware failure, logic board damage, or unrecoverable bricking, repair services under standard warranty or AppleCare may be denied.
Why do sideloaded apps expire every 7 days?
Applications signed using a free, non-paid personal Apple ID rely on Apple's free developer provisioning profile limits, which intentionally expire after seven days to prevent commercial distribution of unreviewed apps. Paid developer accounts bypass this limitation by issuing certificates that remain valid for 365 days.
Can I sideload apps without a computer?
Certain web-based signing services and enterprise certificate distributors attempt to install apps directly through mobile Safari without a computer. However, these methods rely on enterprise certificates that are frequently detected and revoked by Apple, leading to sudden app crashes. Stable sideloading typically requires a local computer for initial setup and regular certificate refreshing.
Does sideloading work on all iOS versions?
No. Sideloading capabilities, available exploits, and system permissions depend heavily on the installed iOS version and device hardware. Apple frequently patches vulnerabilities used for advanced installations or kernel exploits in point releases, meaning newer iOS versions often have fewer sideloading avenues available compared to older, jailbroken or exploit-compatible firmware.
Conclusion and Recommendations
iOS sideloading serves as a powerful utility for developers, power users, and residents of regions covered by digital competition regulations. However, it demands careful management of cryptographic certificates, vigilance against malicious software repositories, and acceptance of ongoing maintenance overhead. Users should weigh the utility of customized applications against the security guarantees of the official App Store before modifying their device workflows.