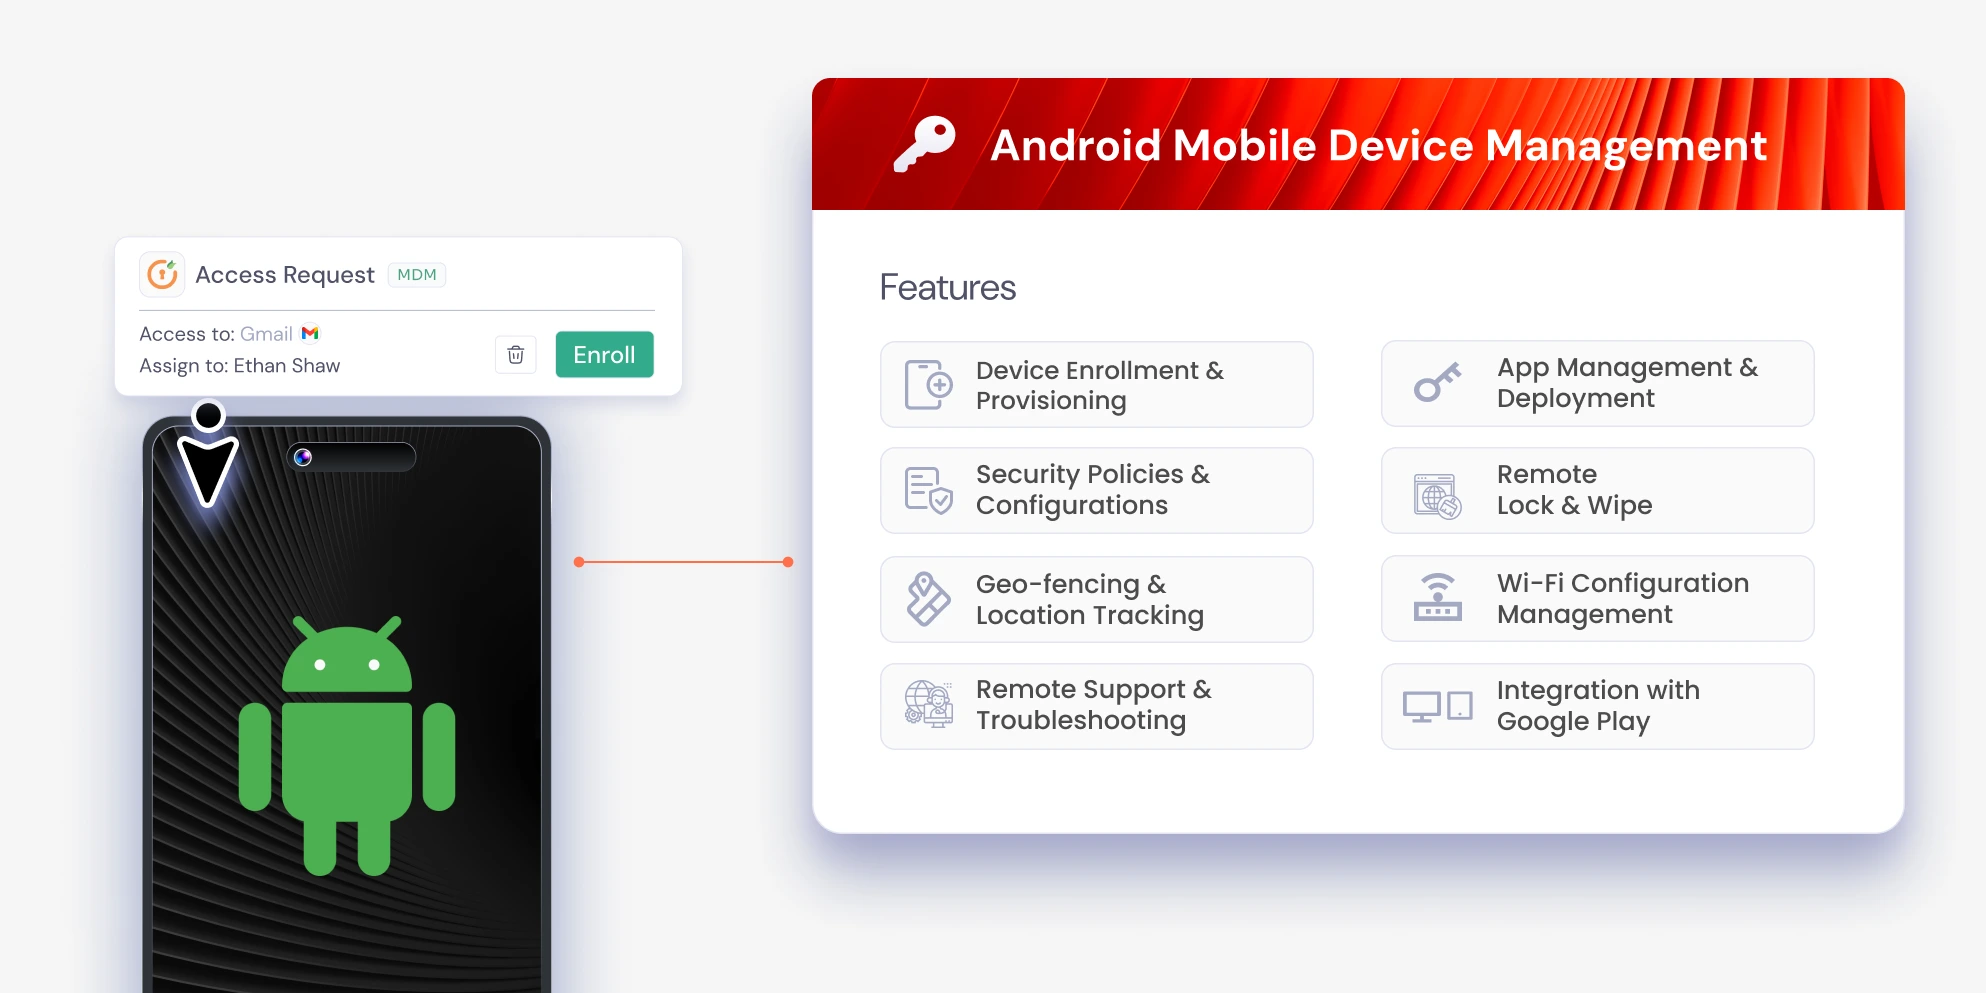
Mobile Device Management (MDM) for Android encompasses the software, protocols, and administrative frameworks organizations use to secure, monitor, and manage corporate-owned or employee-owned Android devices. By leveraging the management APIs provided by Google, MDM platforms enable IT administrators to enforce security compliance, push enterprise applications, configure network settings, and remotely wipe sensitive corporate data from a centralized console without compromising personal user privacy on dual-use devices.
Understanding MDM Android Architecture and the Evolution of Android Enterprise
The management of Android devices within enterprise environments has undergone a profound structural shift over the past decade. In the early days of mobile management, third-party vendors relied heavily on custom device firmware or root-level privileges to control settings. This approach introduced significant security vulnerabilities, stability issues, and fragmentation problems as hardware manufacturers updated their operating systems at varying cadences.
To resolve these challenges, Google introduced Android Enterprise (formerly known as Android for Work), a unified set of APIs built directly into the Android operating system framework. Modern MDM Android solutions interface directly with these native APIs, ensuring a standardized, highly secure management experience across heterogeneous device fleets from manufacturers such as Samsung, Google, Motorola, and Zebra.
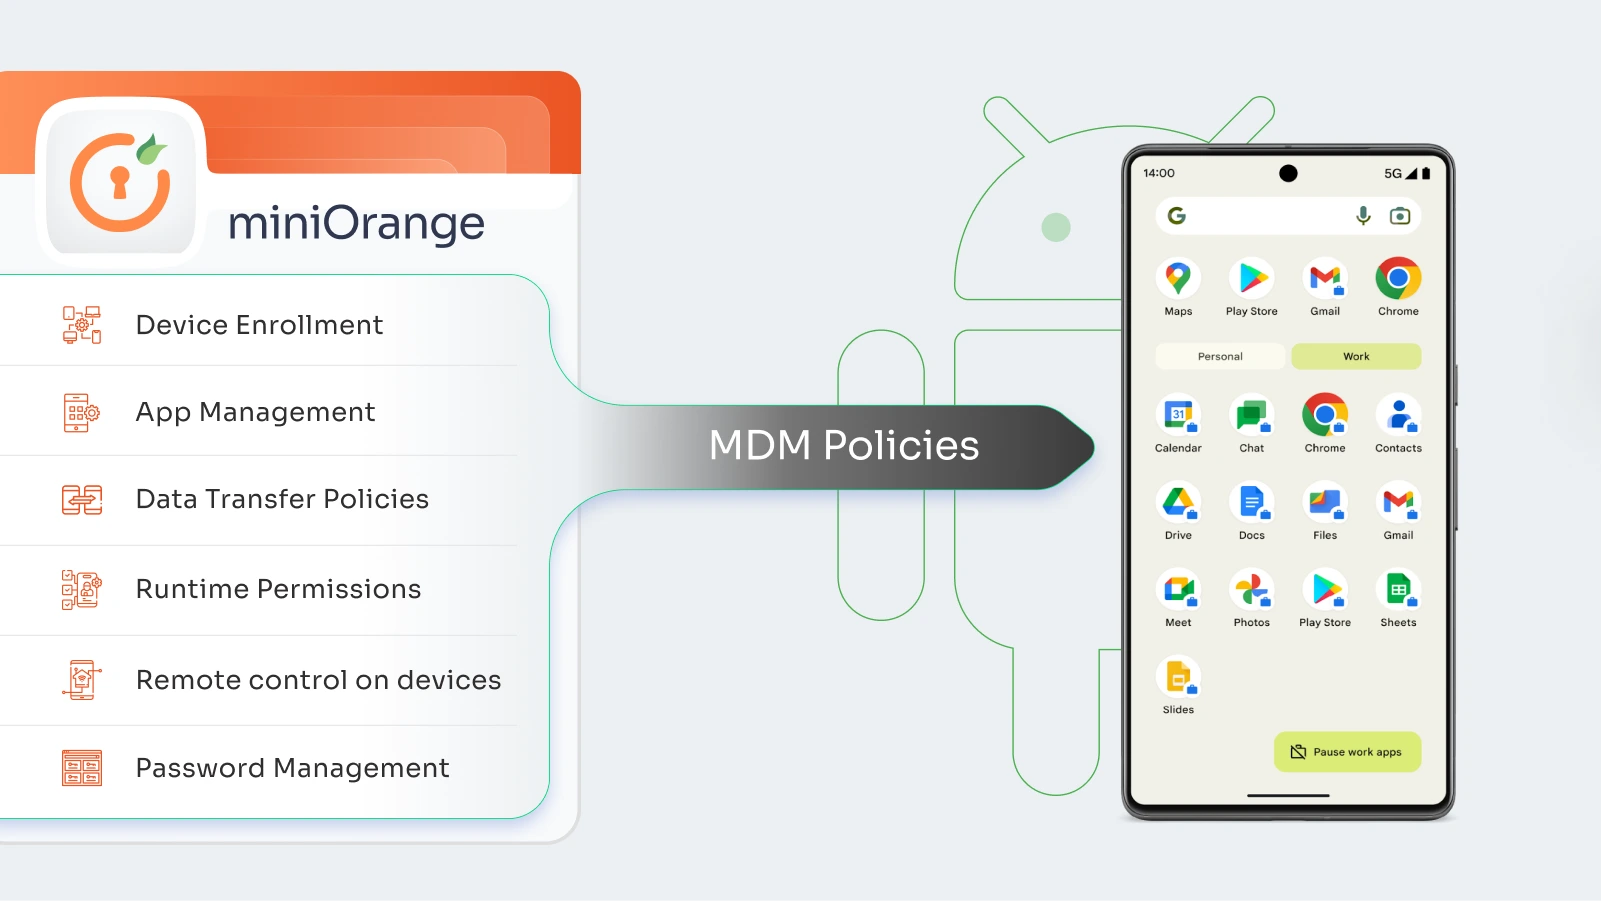
At the core of this architecture is the separation of management layers. Android Enterprise allows IT administrators to establish a dedicated work profile on a device, cleanly separating corporate data, applications, and policies from personal data. This containerization ensures that corporate documents cannot be shared via personal messaging apps or extracted without authorization, while simultaneously protecting employee privacy by preventing administrators from viewing personal photos, web browsing history, or personal emails.
Core Management Modes for Android Devices
When deploying an MDM solution for Android, organizations must select the appropriate management mode based on device ownership, use case, and security requirements. Google defines several distinct deployment scenarios within Android Enterprise:
1. Fully Managed Devices (Device Owner)
In this mode, the organization owns the hardware, and the MDM solution acts as the "Device Owner." This grants the administrator complete control over the device settings, security policies, and application lifecycle.
- Use Cases: Dedicated corporate smartphones, ruggedized warehouse scanners, and frontline worker devices.
- Key Capabilities: Silent application installation, restriction of factory resets, blocking untrusted app sources, and enforcement of strict network configurations.
2. Work Profile (Profile Owner)
Designed for Bring Your Own Device (BYOD) scenarios, the Work Profile mode creates a secure, encrypted container for corporate apps and data alongside the personal side of the device.
- Use Cases: Corporate email access on personal smartphones and flexible remote-work environments.
- Key Capabilities: Remote wipe of only the work profile, prevention of data leakage via copy-paste restrictions between profiles, and selective enforcement of enterprise password complexity.
3. Dedicated Devices (Kiosk Mode)
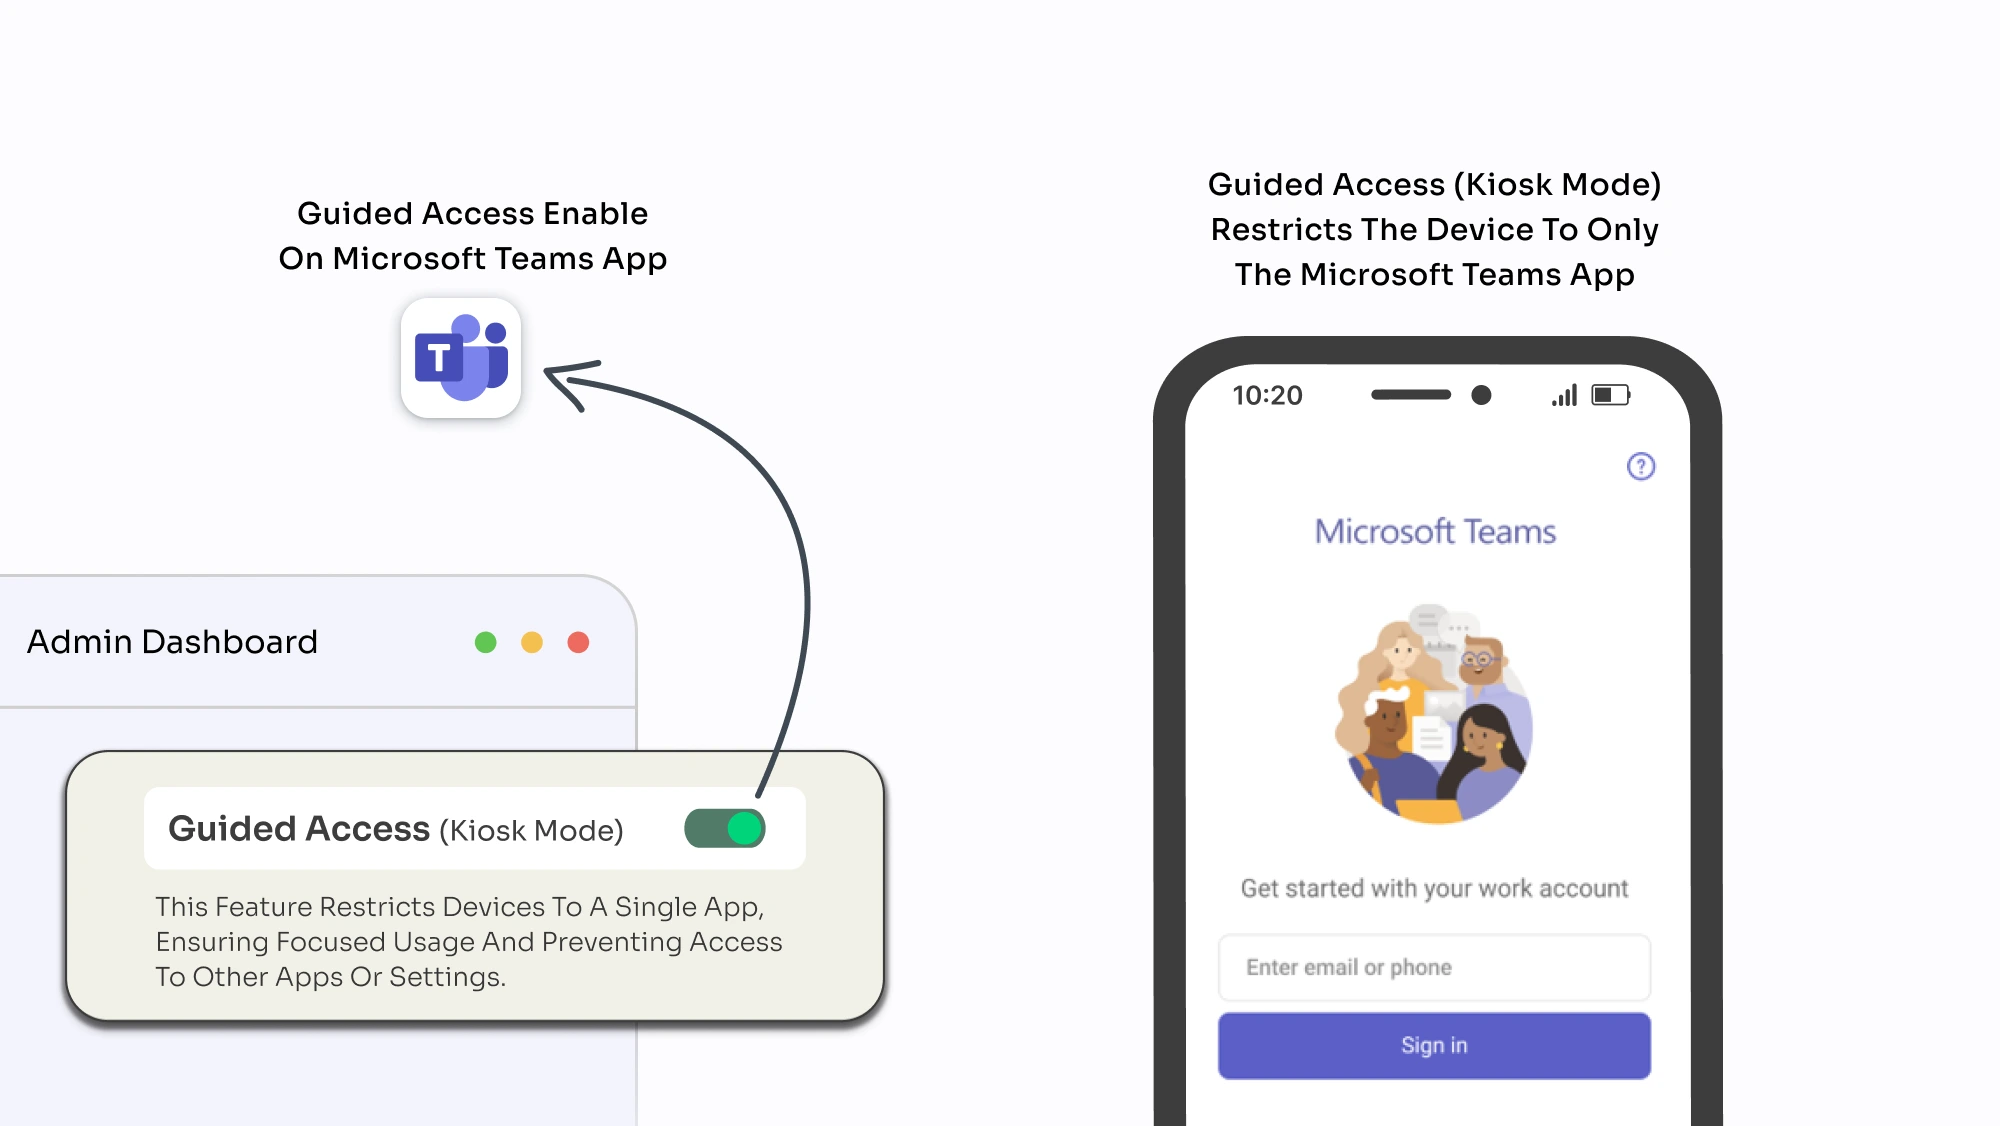
Previously known as COSU (Corporate-Owned, Single-Use), dedicated devices are locked down to run one or a specific set of pre-approved applications.
- Use Cases: Retail point-of-sale (POS) terminals, digital signage, self-service check-in kiosks, and hospitality tablets.
- Key Capabilities: Disabling the status bar, preventing access to device settings, locking the screen to a single application loop, and automated rebooting schedules.
4. Corporate-Owned, Personally Enabled (COPE)
A hybrid model where the organization owns the device, but the user is permitted to use it for personal tasks during off-hours, typically via a dedicated personal profile coexisting with managed policies.
Essential Features of Enterprise Android MDM Platforms
A robust MDM Android platform provides a comprehensive toolkit designed to streamline IT operations, reduce support overhead, and mitigate security risks. The following table compares the primary administrative features across different deployment modes:
| Feature / Capability | Fully Managed (COBO) | Work Profile (BYOD) | Dedicated Devices (Kiosk) |
|---|---|---|---|
| Primary Owner | Organization | Employee | Organization |
| Data Separation | Single management scope | Dual containerized profile | Single locked-down scope |
| Remote Factory Reset | Supported | Not allowed (Work wipe only) | Supported |
| Silent App Deployment | Supported | Supported (Work profile only) | Supported |
| Personal Privacy | Minimal (Organization owned) | Absolute (Personal side hidden) | N/A (Single-use hardware) |
| OS Update Control | Full administrative control | Deferred/Not controlled | Full administrative control |
Application Management and Distribution
Administrators can integrate their MDM console with Google Play Custom App Publishing or Managed Google Play. This integration allows IT teams to approve, purchase, and silently push internal or public applications to targeted device groups without requiring end-users to sign in with a personal Google account. Furthermore, administrators can configure managed app configurations, pre-setting server URLs, account credentials, or security parameters upon installation.
Security and Compliance Policies
Security enforcement forms the backbone of any mobile device management strategy. MDM platforms allow organizations to enforce policies including:
- Minimum PIN or password complexity requirements (length, alphanumeric composition, expiration intervals).
- Encryption enforcement for internal storage and external SD cards.
- Geofencing capabilities that restrict device functionality or trigger alerts when a device leaves a designated geographic perimeter.
- Disabling hardware peripherals such as cameras, Bluetooth, USB file transfers, or microphone access in high-security environments.
Step-by-Step Enrollment Methods for Android Devices
Deploying an MDM solution requires registering devices with the management server. Google and hardware vendors provide several streamlined enrollment methods to minimize user friction during onboarding.
1. Zero-Touch Enrollment
For corporate-purchased devices bought through authorized resellers, Google Zero-Touch Enrollment automates the provisioning process. When the device is unboxed and connected to the internet, it automatically contacts Google's servers, recognizes the corporate association, and downloads the designated MDM agent without manual configuration by the end-user.
2. QR Code Provisioning
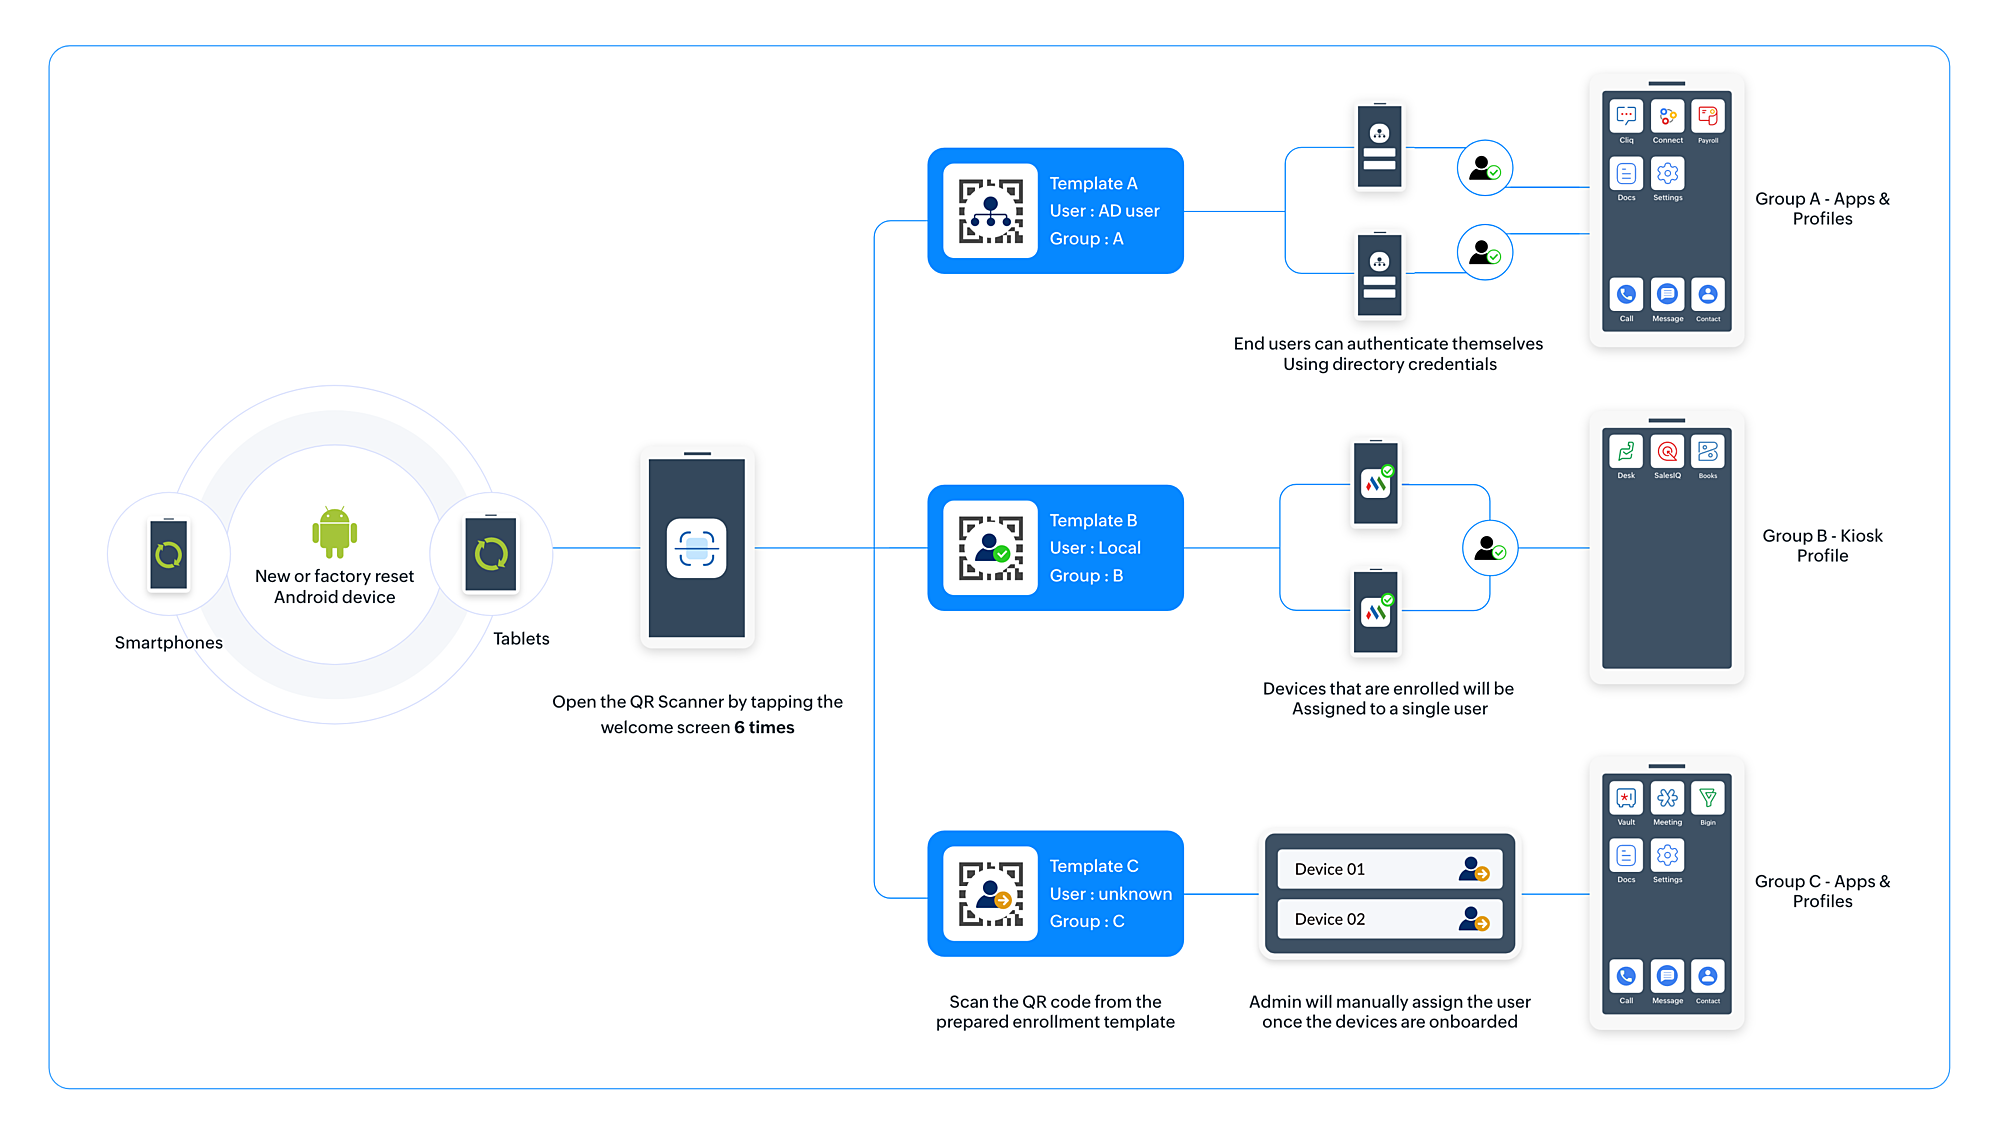
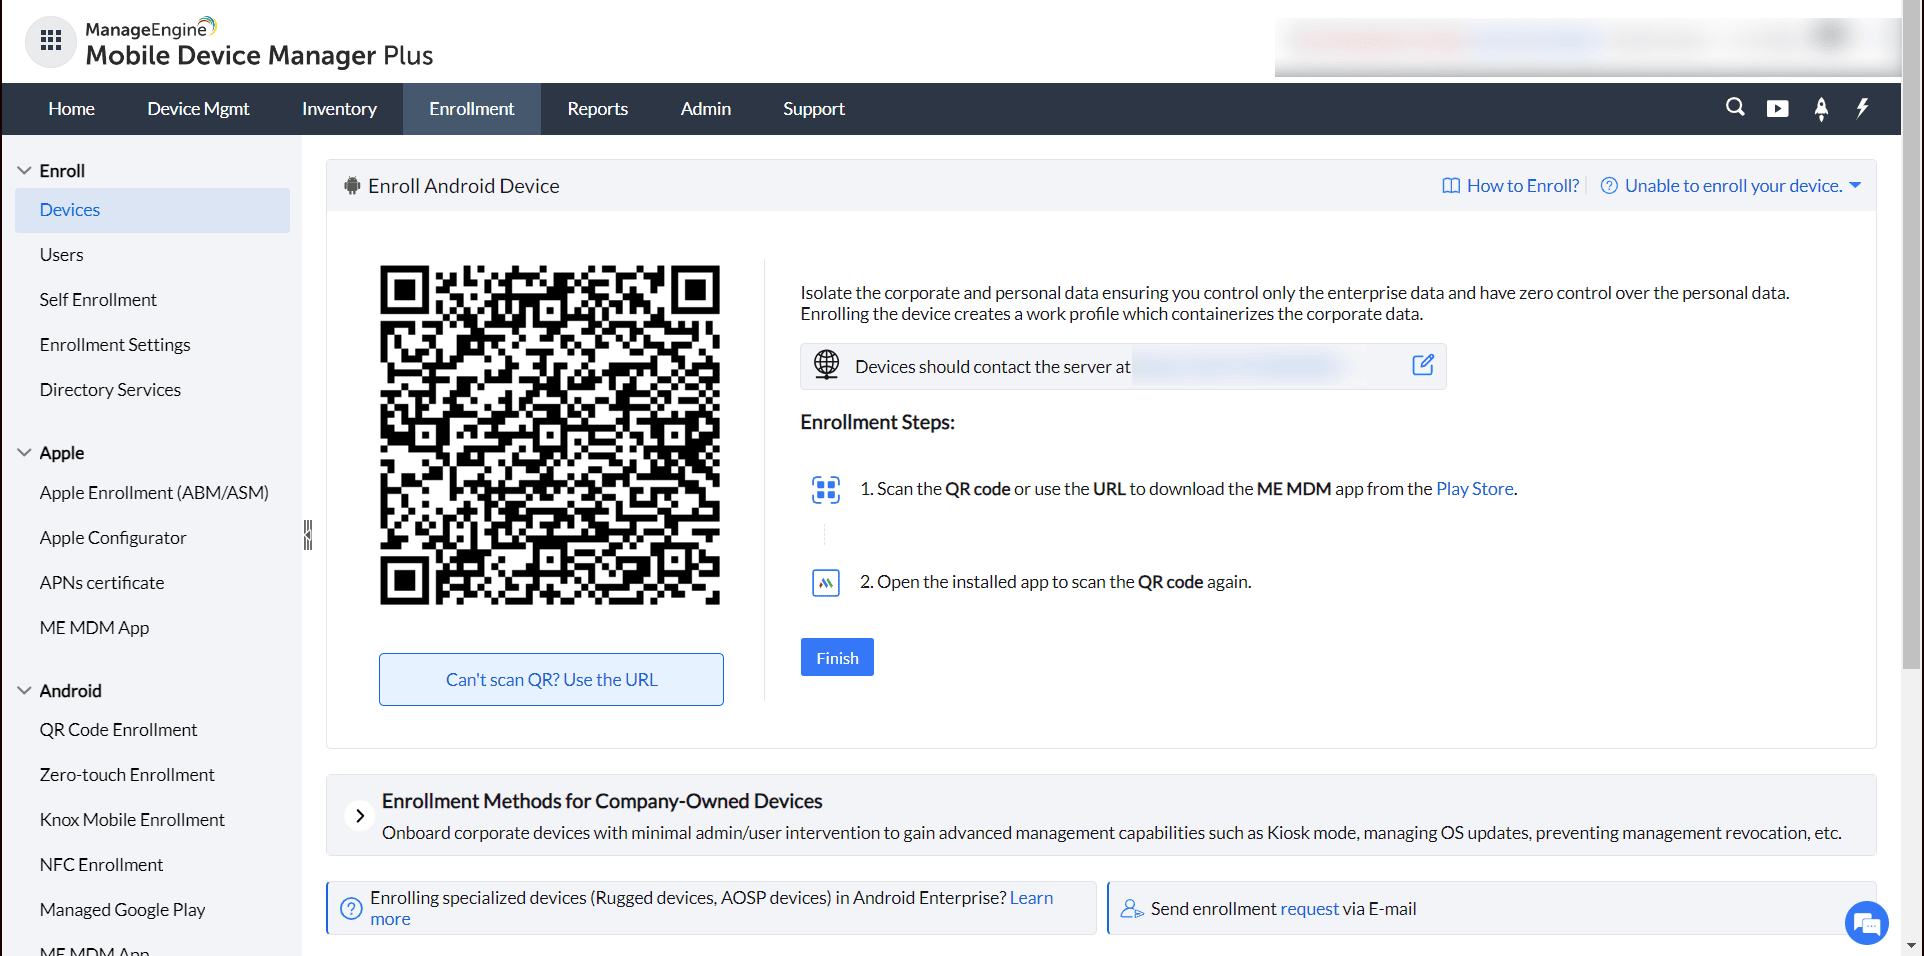
During the initial device setup wizard (the "Welcome" screen), tapping the screen six times launches the device camera to scan a QR code generated by the MDM console. This code contains the configuration JSON payload, Wi-Fi credentials, and enrollment token, instantly configuring the device as a fully managed asset.
3. NFC Bump Provisioning
Administrators can configure a master provisioning device to beam configuration settings via Near Field Communication (NFC) to a new or factory-reset target device placed back-to-back during initial startup.
4. End-User Self-Enrollment
Commonly used in BYOD environments, employees download the MDM client application (such as Intune, MobileIron/Ivanti, or Workspace ONE) from the public Google Play Store and sign in with corporate credentials. The application guides the user through the creation of the Managed Google Play account and work profile.
Troubleshooting Common MDM Android Issues
Despite streamlined provisioning tools, administrators frequently encounter specific technical challenges during deployment and ongoing management. Understanding these common friction points helps maintain high uptime and user compliance.
Enrollment Failures and Factory Reset Protection (FRP)
If a corporate-owned device has previously been associated with a personal Google account before being wiped and re-enrolled, Factory Reset Protection (FRP) may block setup until the original user credentials are entered.
- Resolution: Ensure devices are properly enrolled using zero-touch or staged provisioning workflows before handing them to end-users. If FRP is triggered, administrators must release the device from the enterprise Google domain console or use OEM-specific unlock tokens.
Compliance Policy Conflicts
Devices may occasionally fall out of compliance due to failing password complexity checks, outdated operating system versions, or unauthorized root detection.
- Resolution: Review the compliance report within the MDM console to identify the exact failing parameter. Configure grace periods for remediation before conditional access policies block access to corporate email and cloud storage.
Application Deployment Stalls
Silently pushed applications may occasionally remain stuck in a "Pending" state due to connectivity timeouts, insufficient storage space, or Managed Google Play synchronization errors.
- Resolution: Verify that the device has an active internet connection, check that the application is explicitly approved in the Managed Google Play console, and force an explicit policy synchronization from the MDM dashboard.
Frequently Asked Questions About MDM Android
Can an administrator read my personal text messages or view my photos on a managed Android device?
No. In a Work Profile (BYOD) setup, administrators have zero visibility into personal applications, photos, browser histories, text messages, or personal emails. The privacy boundary is strictly enforced by the Android operating system architecture. On fully managed corporate devices, while administrators have broader control over security and app installation, standard MDM frameworks do not provide built-in tools for monitoring personal communications or media unless specific third-party monitoring agents are explicitly deployed.
What happens to corporate data if a managed device is lost or stolen?
Administrators can execute a remote wipe command directly from the MDM console. In a BYOD work profile environment, this command deletes only the work profile container and associated corporate data, leaving personal files intact. On fully managed corporate devices, a remote wipe executes a complete factory reset, restoring the device to its original unconfigured state and neutralizing data theft risks.
Does Android MDM require a Google account on every managed device?
No. Android Enterprise utilizes Managed Google Play accounts, which are generated silently in the background by the MDM server. End-users do not need to input or create a personal Gmail account to receive enterprise applications and security updates on fully managed devices.
How do Android Enterprise updates affect existing MDM configurations?
Google updates the Android Enterprise framework alongside major operating system releases. Modern MDM vendors update their cloud-based consoles concurrently to support new API features. However, organizations should test critical line-of-business applications against beta OS releases before enforcing enterprise-wide upgrades using the MDM's OS update management policies.
Can MDM track the real-time GPS location of an Android device?
Location tracking capabilities depend on the device ownership mode and privacy policies configured by the organization. While MDM platforms possess the technical capability to query device GPS coordinates, most enterprise deployments restrict location polling to specific compliance auditing or asset recovery scenarios, and many platforms provide user-facing transparency notifications when location tracking is active.
Strategic Next Actions for Enterprise Deployment
Implementing an MDM Android strategy requires a structured evaluation of your organization's specific operational requirements. Begin by auditing your existing device inventory to classify assets into BYOD, fully managed corporate, or dedicated kiosk use cases. Next, conduct a proof-of-concept (PoC) pilot with a small user group to validate application compatibility, enrollment workflows, and helpdesk support procedures. Finally, draft clear corporate mobile usage policies that transparently communicate privacy boundaries to employees before rolling out the solution across the broader enterprise infrastructure.