Navigating the complexities of modern security requires implementing established "security do's" that address both digital cybersecurity threats and physical safety protocols. Adopting these proactive measures minimizes vulnerabilities, protects critical assets against unauthorized access, and ensures operational resilience across diverse environments.
Understanding Security Do's: Core Principles and Scope
Security do's represent the proactive, recommended actions that individuals and organizations must take to maintain robust defensive postures. In an era where security threats range from sophisticated social engineering attacks to physical perimeter breaches, relying on ad-hoc safety measures is insufficient. A structured framework of security do's bridges the gap between theoretical policies and daily operational reality.
The scope of security practices extends across multiple domains, including digital infrastructure, physical environments, personal data privacy, and organizational compliance. Establishing clear do's helps stakeholders internalize habits that naturally repel common threats. Rather than focusing solely on what to avoid—the traditional "security don'ts"—focusing on positive actions empowers users to take control of their security posture.
To build an effective security routine, one must understand the foundational principles of confidentiality, integrity, and availability (the CIA triad). Every security do maps back to one or more of these pillars. By enforcing strict access controls, maintaining up-to-date systems, and fostering a culture of vigilance, security do's serve as the first line of defense against evolving threat landscapes.
Digital Security Do's: Protecting Information and Networks
Digital security demands continuous attention to software updates, credential management, and network configurations. Failing to follow fundamental digital security do's often leads to unauthorized data access, malware infections, and costly system compromises.
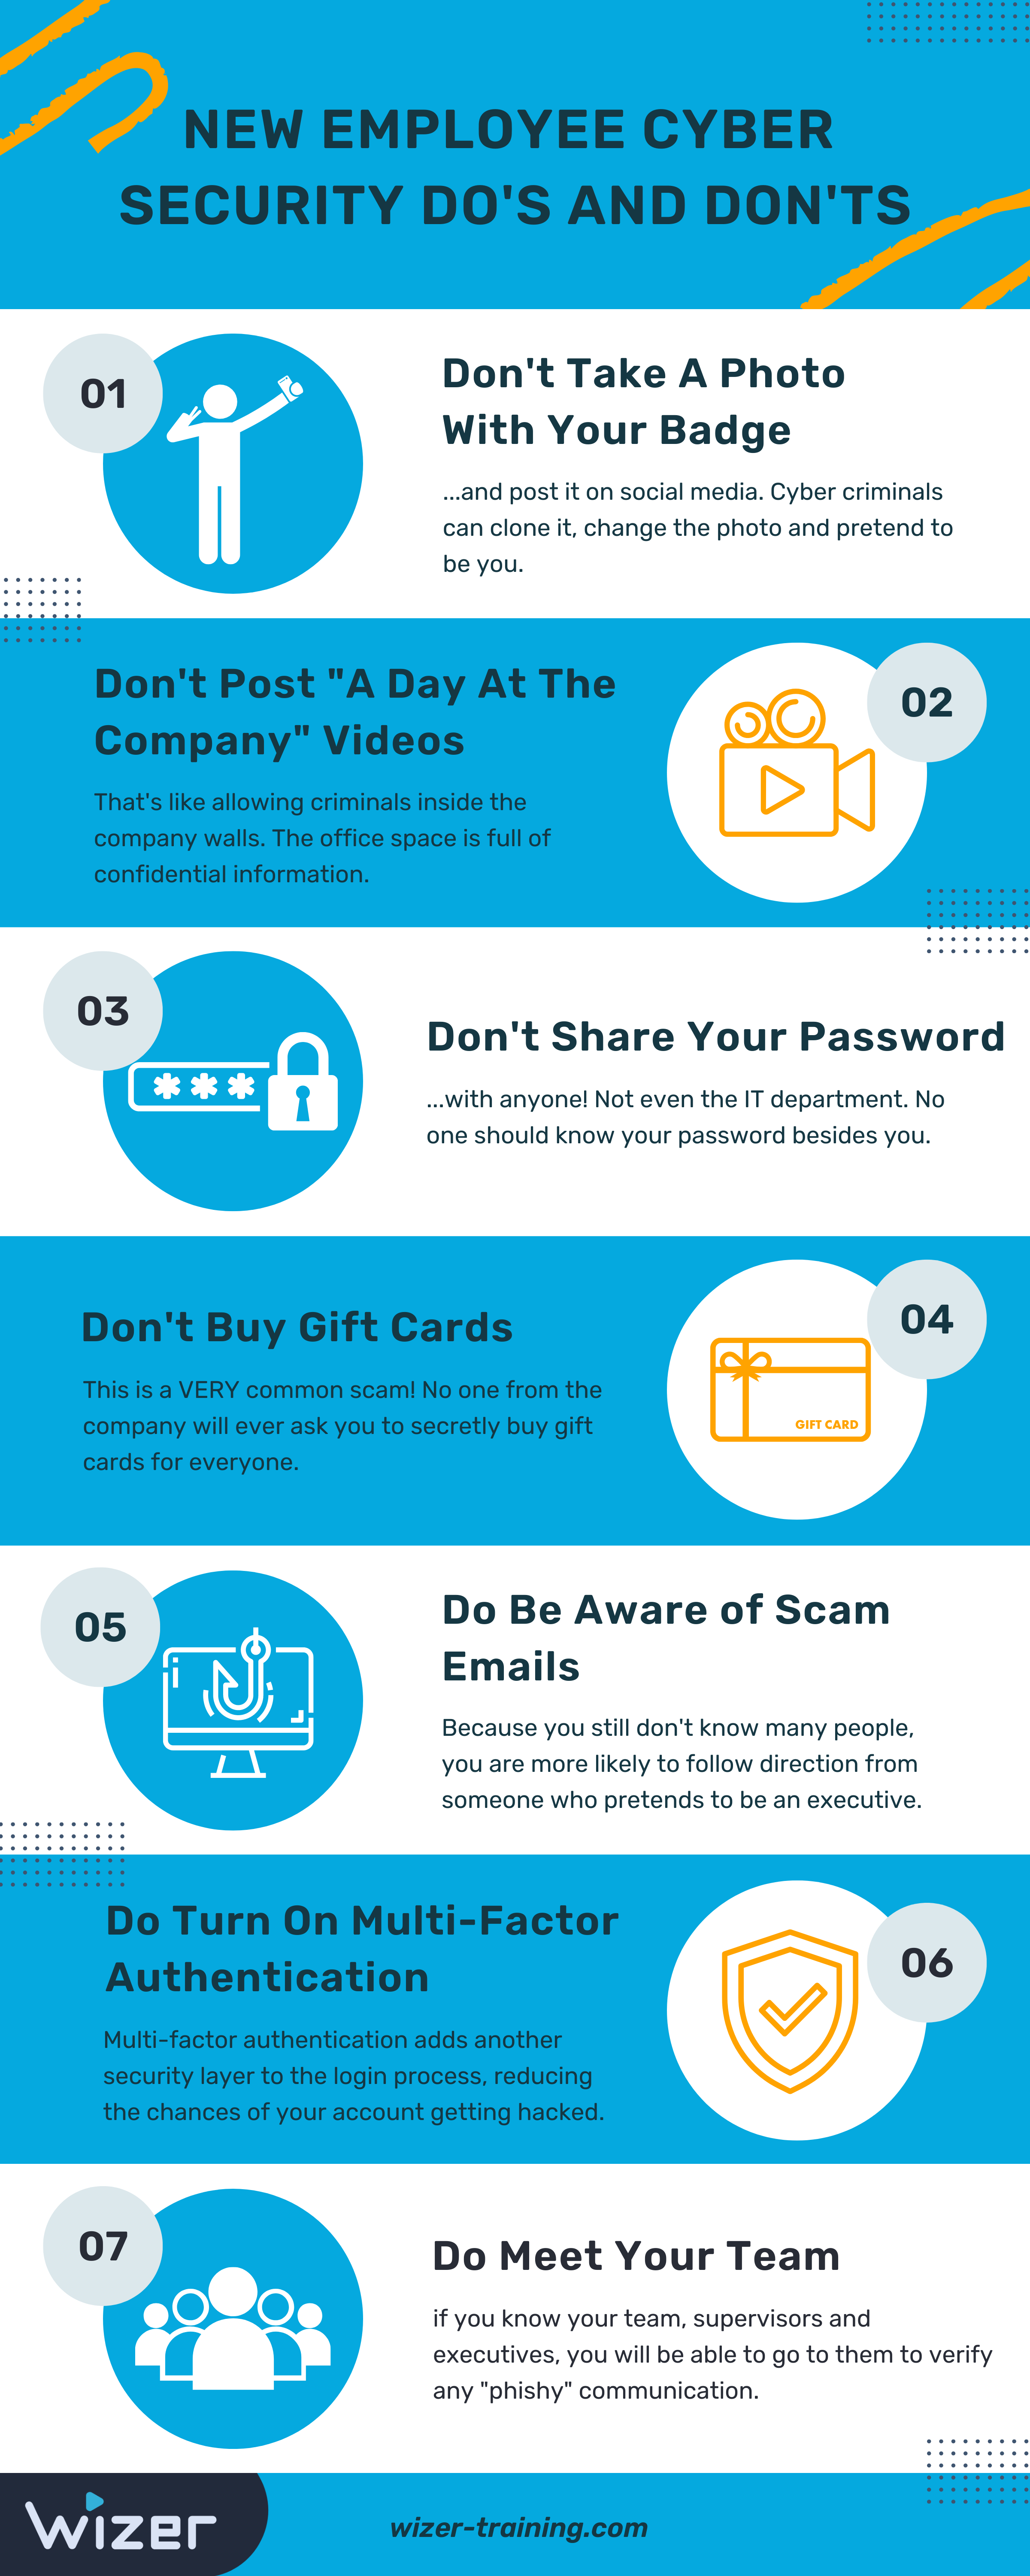
1. Implement Multi-Factor Authentication Everywhere
Multi-factor authentication (MFA) requires users to provide two or more verification factors to gain access to an account or system. This typically combines something you know (a password), something you have (a smartphone or hardware token), or something you are (biometrics).
- Enable MFA on all personal and professional accounts, prioritizing email, financial services, and cloud storage.
- Prefer app-based authenticators or hardware security keys over SMS-based verification codes, which remain vulnerable to SIM-swapping attacks.
2. Maintain Rigorous Password Hygiene
Passwords remain a primary gatekeeper for digital assets. Weak or reused credentials provide attackers with an easy entry point through credential-stuffing attacks.
- Use a reputable password manager to generate and store complex, unique passwords for every service.
- Update critical administrative passwords immediately if a breach or unauthorized login attempt is suspected.
3. Apply Software Updates and Patches Promptly
Software vendors regularly release updates to patch newly discovered vulnerabilities. Ignoring these updates leaves systems exposed to known exploits.
- Enable automatic updates for operating systems, web browsers, and productivity applications whenever possible.
- Establish a routine patching schedule for enterprise servers and specialized software to minimize downtime while maintaining security integrity.
Physical Security Do's: Safeguarding Facilities and Hardware
Physical security is often overlooked in favor of digital defenses, yet a physical breach can completely bypass advanced software controls. Protecting hardware, facilities, and physical documents is just as critical as securing network perimeters.
- Enforce Strict Access Control: Utilize keycards, biometric scanners, or security personnel to restrict entry to sensitive areas such as server rooms and executive offices.
- Secure Workstations When Unattended: Always lock computer screens using keyboard shortcuts (such as Windows Key + L or Command + Control + Q) whenever stepping away from a desk.
- Maintain Visitor Logs: Require all external visitors to sign in, wear temporary identification badges, and be escorted while inside secure facilities.
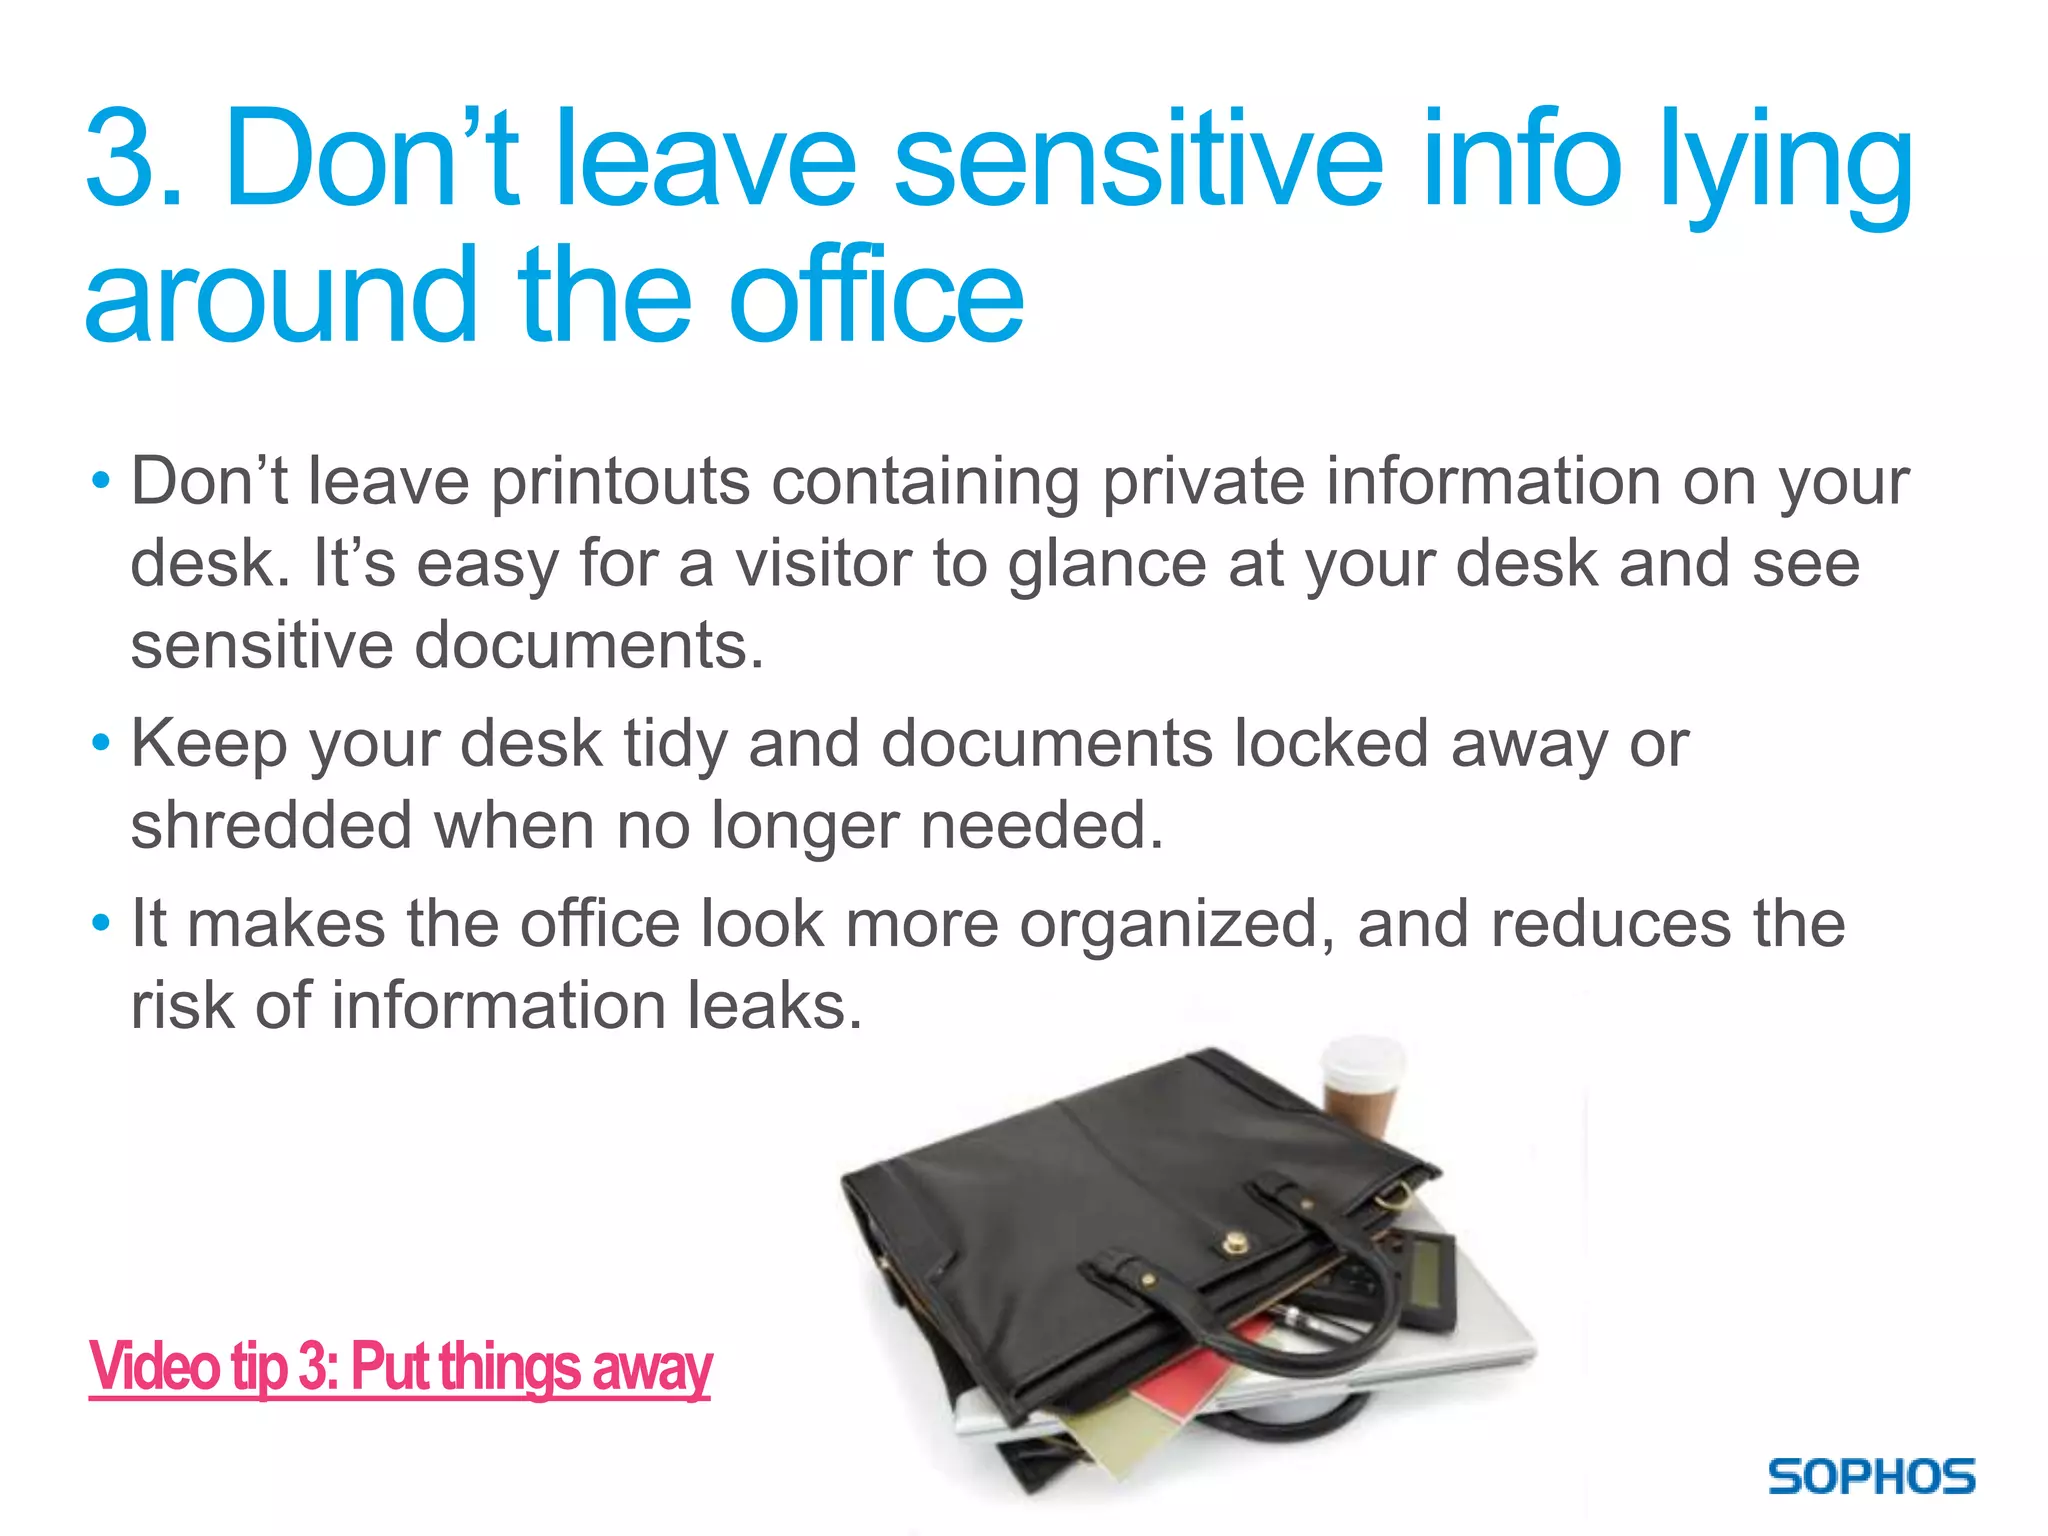
- Properly Dispose of Sensitive Media: Shred physical documents containing confidential information and securely wipe or physically destroy hard drives before discarding old hardware.
Comparative Overview of Security Frameworks
Implementing security do's varies depending on the operational environment. The table below outlines key focus areas, common vulnerabilities, and recommended proactive actions for different sectors.
| Security Domain | Primary Risk | Recommended Security Do's | Potential Impact of Inaction |
|---|---|---|---|
| Digital / Enterprise | Phishing & Ransomware | Enforce MFA, train employees regularly, back up data offsite. | Data loss, financial extortion, regulatory penalties. |
| Physical Facilities | Unauthorized Entry | Use access control systems, enforce visitor logging, secure perimeters. | Theft of hardware, corporate espionage, physical harm. |
| Data Privacy | Regulatory Non-Compliance | Encrypt sensitive data at rest and in transit, limit data collection. | Legal liabilities, loss of customer trust, hefty fines. |
| Personal Security | Identity Theft | Monitor financial statements, shred documents, use secure networks. | Financial loss, compromised personal reputation. |
Operational and Procedural Security Do's
Beyond technical controls and physical barriers, human behavior remains the most significant variable in security outcomes. Developing robust operational procedures ensures that teams respond effectively to incidents and maintain consistent standards.
Conduct Regular Security Awareness Training
Human error is a contributing factor in the vast majority of security breaches. Organizations must move beyond one-time orientation briefings and implement ongoing education.
- Train staff to recognize phishing emails, social engineering tactics, and suspicious physical tailgating attempts.
- Perform controlled phishing simulations to measure awareness and provide targeted refresher training for vulnerable departments.
Establish and Test Incident Response Plans
Having a security policy is insufficient without a clear, practiced plan for handling breaches or emergencies.
- Document step-by-step procedures for containing threats, notifying stakeholders, and preserving forensic evidence.
- Conduct regular tabletop exercises to test team readiness and identify bottlenecks in communication or technical response capabilities.
Common Mistakes and Troubleshooting Security Gaps
Even well-intentioned security programs can falter due to common pitfalls. Recognizing these missteps helps organizations and individuals course-correct before a security incident occurs.
- Over-Reliance on Technology: Believing that installing a firewall or purchasing security software eliminates the need for user vigilance and physical security controls.
- Neglecting Third-Party Risk: Failing to vet vendors, contractors, and software dependencies that have access to your network or facilities.
- Ignoring Shadow IT: Allowing employees to use unauthorized applications or personal cloud storage services for work tasks without security oversight.
- Failing to Verify Backups: Regularly creating backups is essential, but failing to test data restoration processes renders the backup strategy unreliable during a crisis.
When a security gap or minor incident is identified, immediate troubleshooting involves isolating the affected asset, revoking compromised credentials, reviewing access logs, and applying necessary patches or policy adjustments to prevent recurrence.
Frequently Asked Questions
What is the single most important security do for everyday users?
Enabling multi-factor authentication across all accounts is widely considered the single most effective step everyday users can take. MFA blocks a significant percentage of automated credential-based attacks, even if a password is compromised.
How often should security passwords and access credentials be updated?
Modern security guidance moves away from mandatory periodic password changes unless a breach is suspected, as forced changes often lead users to choose weaker, predictable passwords. Instead, focus on using unique, complex passwords managed via a password manager and updating them only when compromise occurs.
What differentiates physical security from digital security?
Physical security focuses on protecting tangible assets, facilities, hardware, and personnel from physical threats and unauthorized entry. Digital security focuses on protecting electronic data, software, and networks from cyber threats, malware, and remote intrusions. Both are essential components of a comprehensive security strategy.
How can small businesses implement effective security do's on a budget?
Small businesses can achieve strong security without excessive spending by leveraging built-in platform security features, enforcing strict password and MFA policies, training employees on phishing awareness, and utilizing reputable, low-cost cloud security services.
What should be done immediately following a suspected security breach?
Immediately isolate affected systems from the network to prevent lateral movement by attackers, preserve system logs for forensic analysis, revoke compromised access credentials, and notify relevant internal stakeholders or regulatory bodies as required by law.
Conclusion and Next Actions
Adopting comprehensive security do's requires a shift from reactive problem-solving to proactive vigilance. Start by conducting a thorough audit of your current digital credentials and physical access points. Implement multi-factor authentication, update your software systems, and establish clear operational protocols. By making security an ongoing habit rather than a one-time checklist, you significantly reduce vulnerabilities and protect valuable assets against emerging threats.